

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
13
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
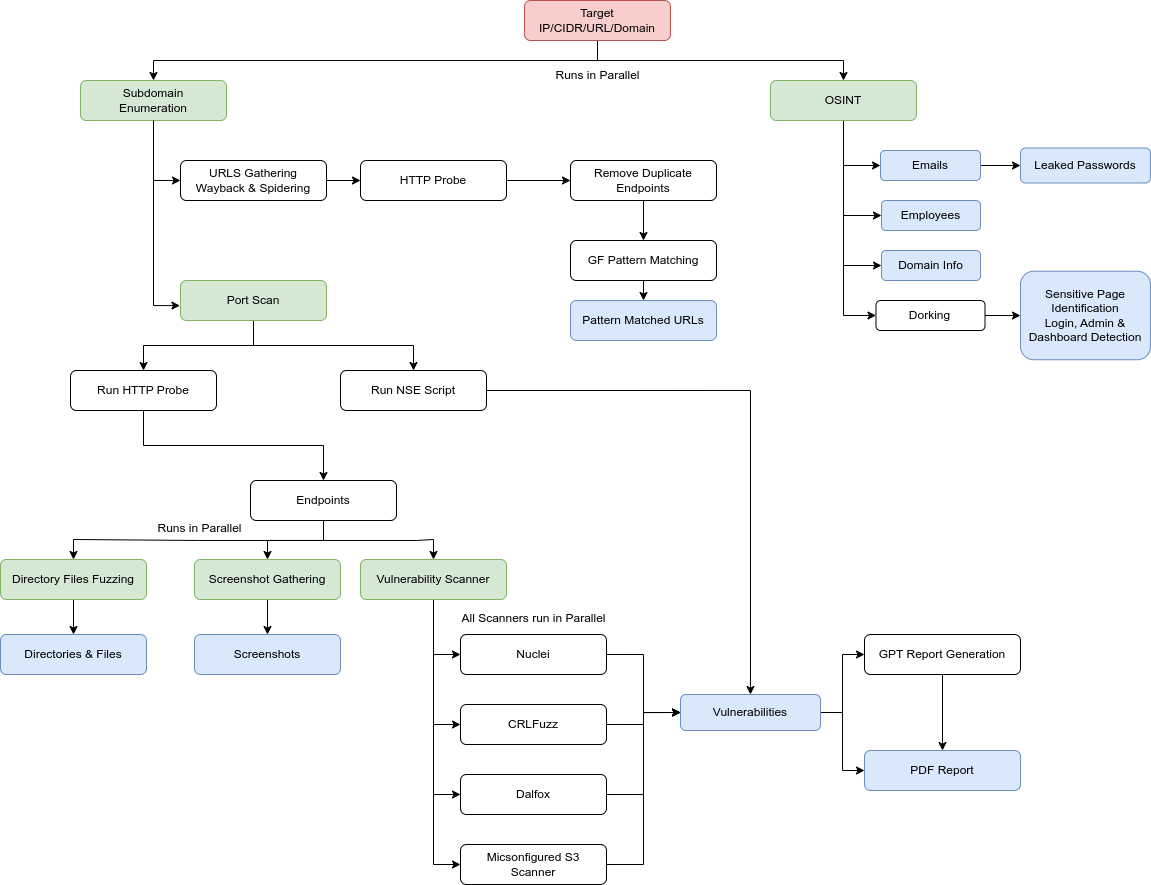 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 d3ckx1/omniscan
Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
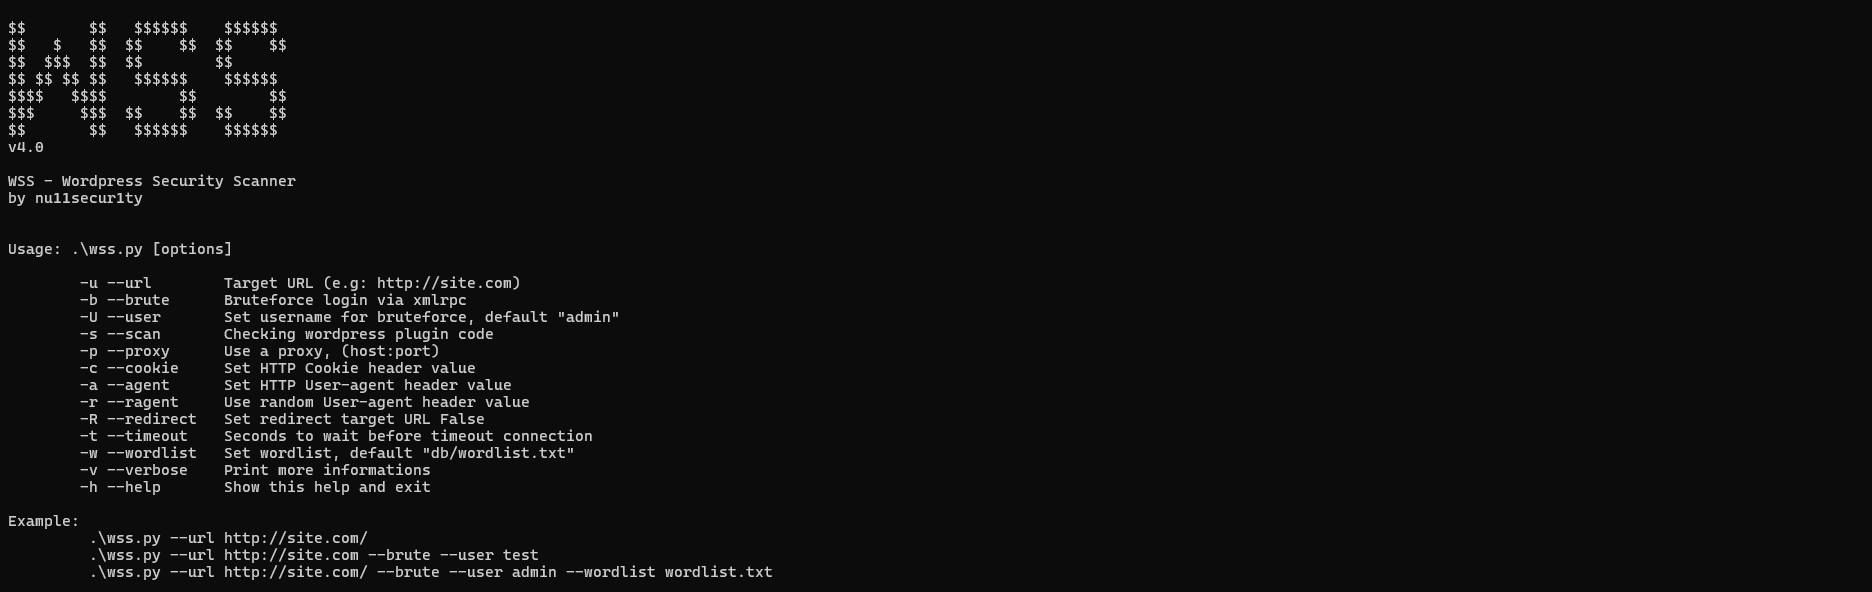 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 flenz00/cve-2026-18110-poc
Python PoC and Nuclei template exploiting CVE-2026-18110, an unauthenticated user enumeration flaw in Concrete CMS 9.0.0-9.5.2 via the user…
 cappricio-securities/laravel-ignition-rxss
Laravel Ignition contains a cross-site scripting vulnerability when debug mode is enabled.