

EasY_HaCk
 sabri-zaki/easy_hack
Hack the World using Termux
exploit-frameworksinformation-gatheringnetwork-mapping+4
sabri-zaki/easy_hackHack the World using Termux
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
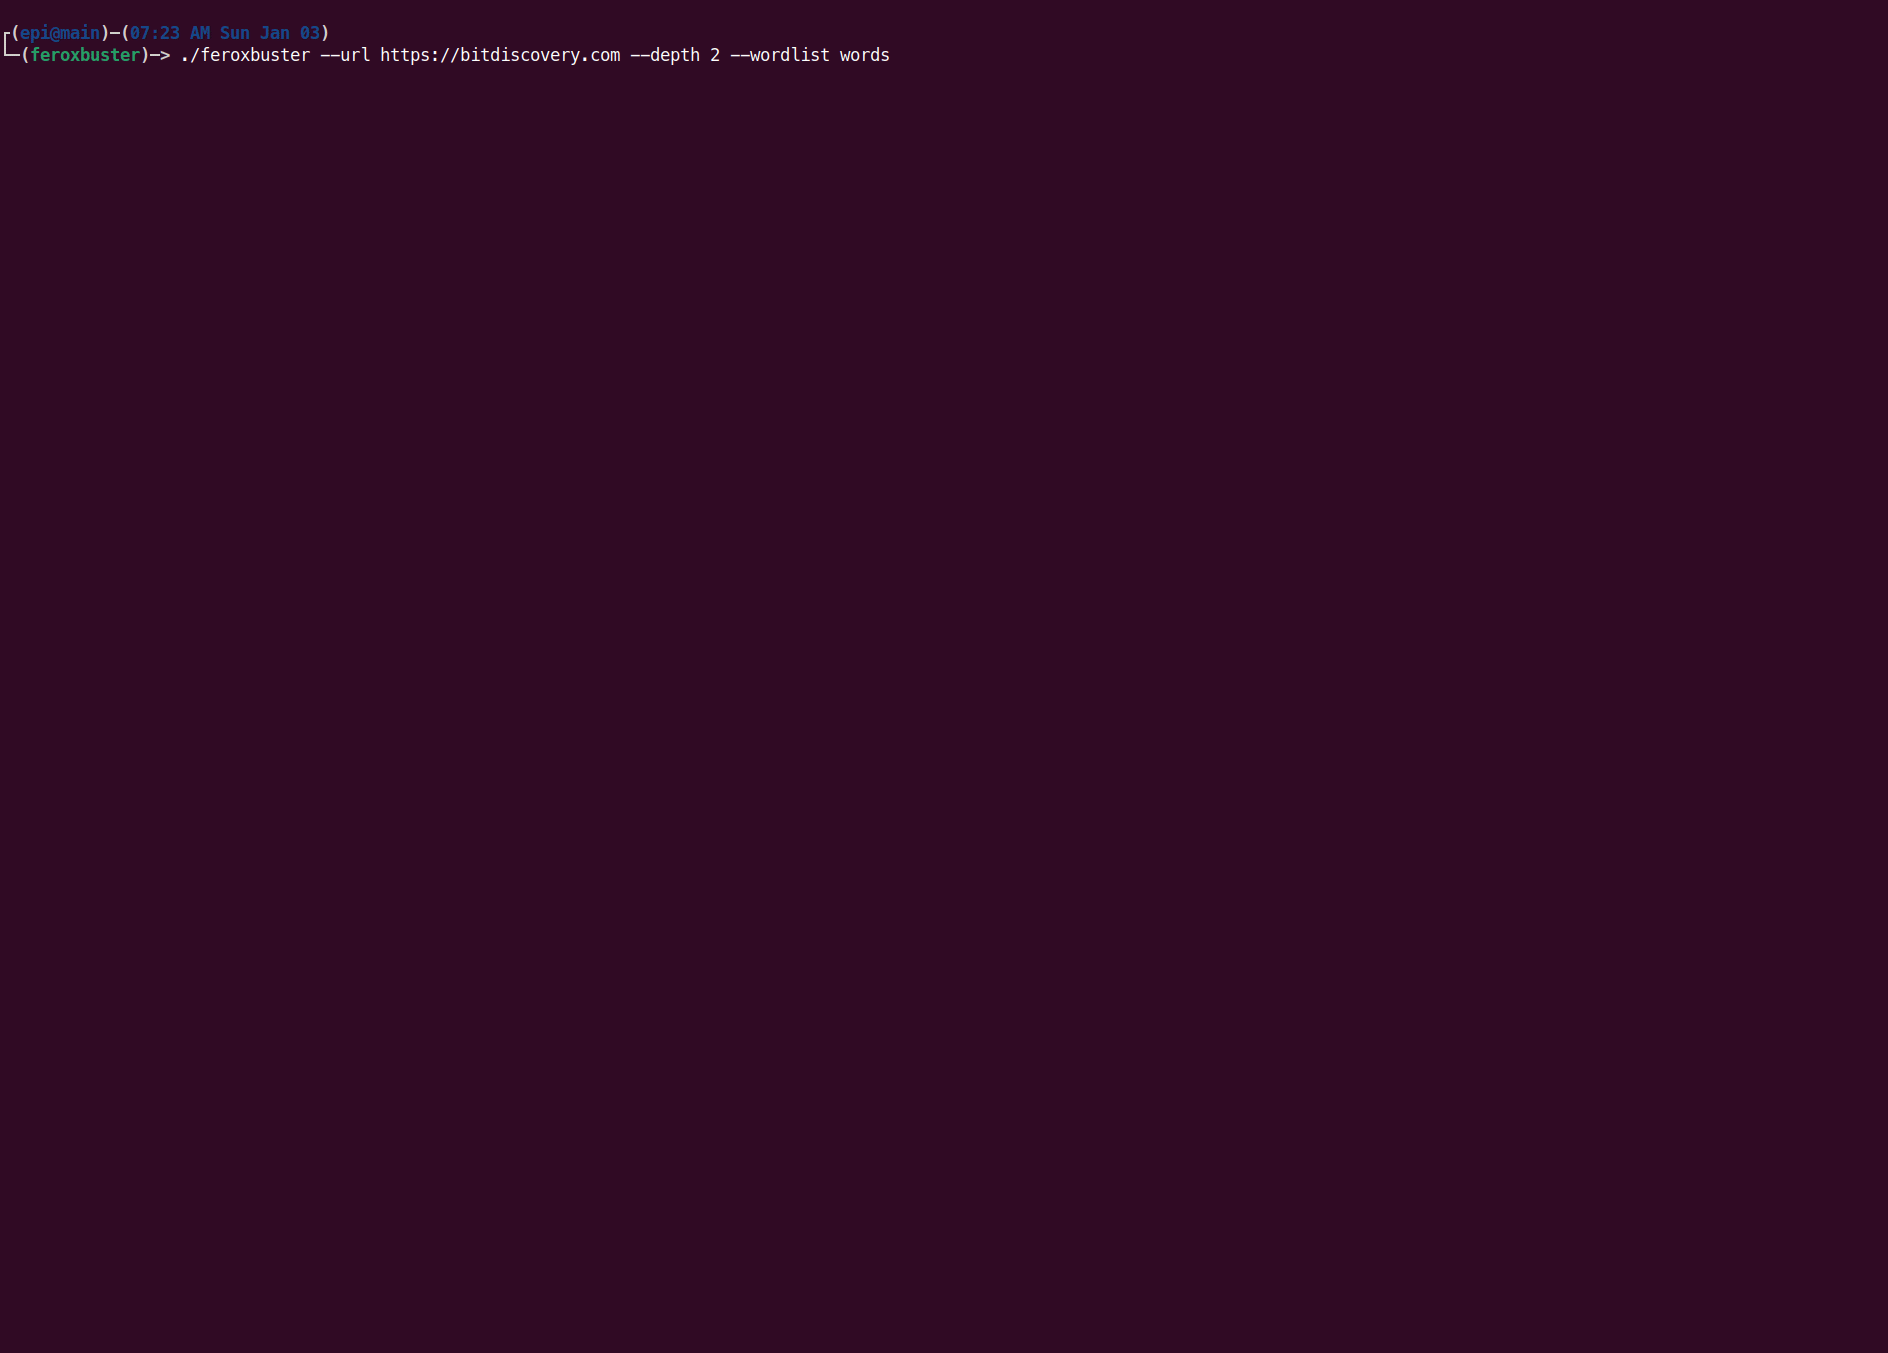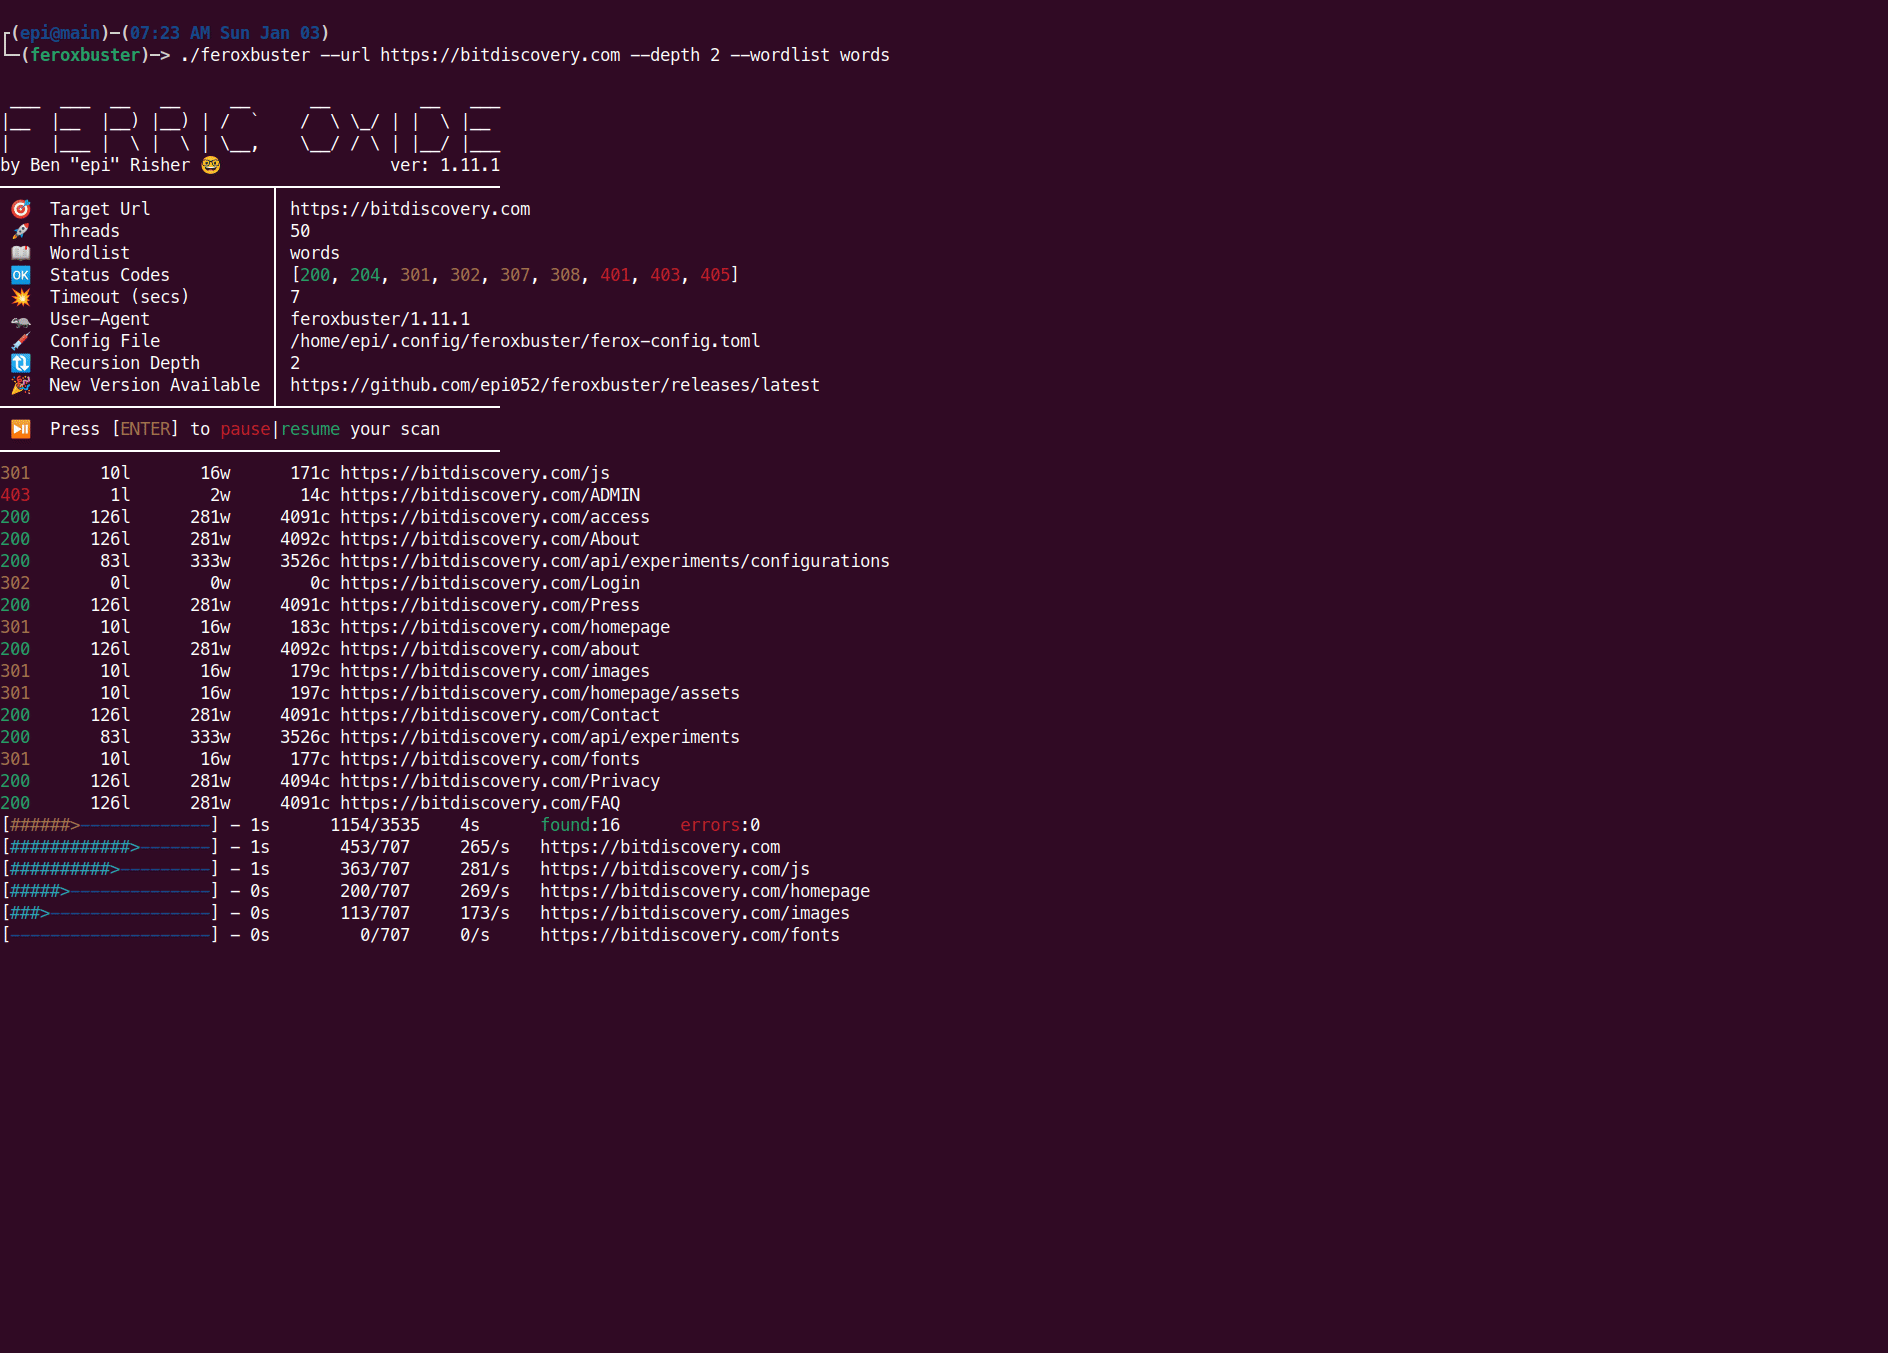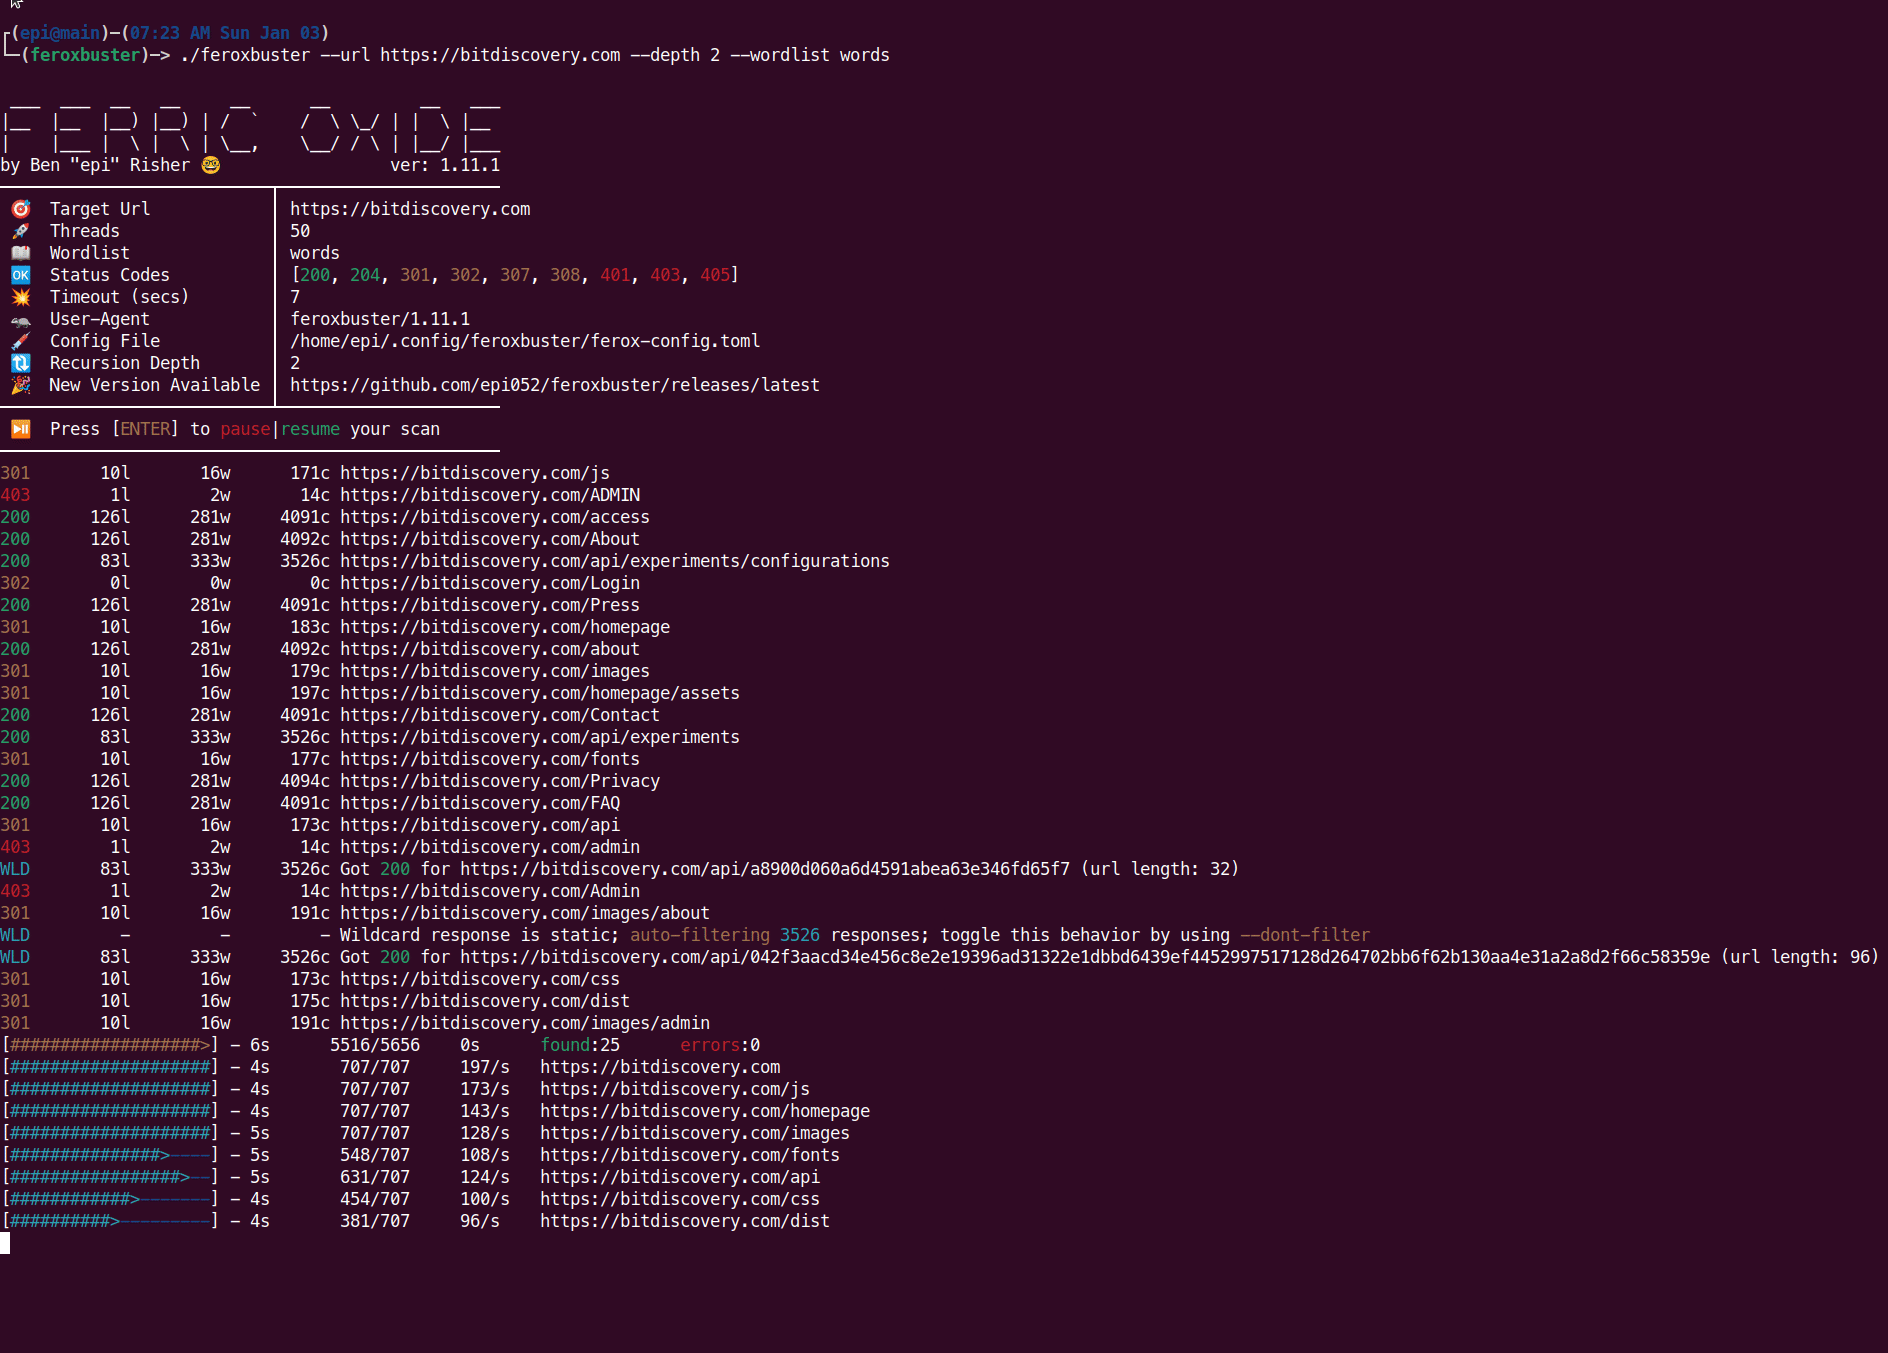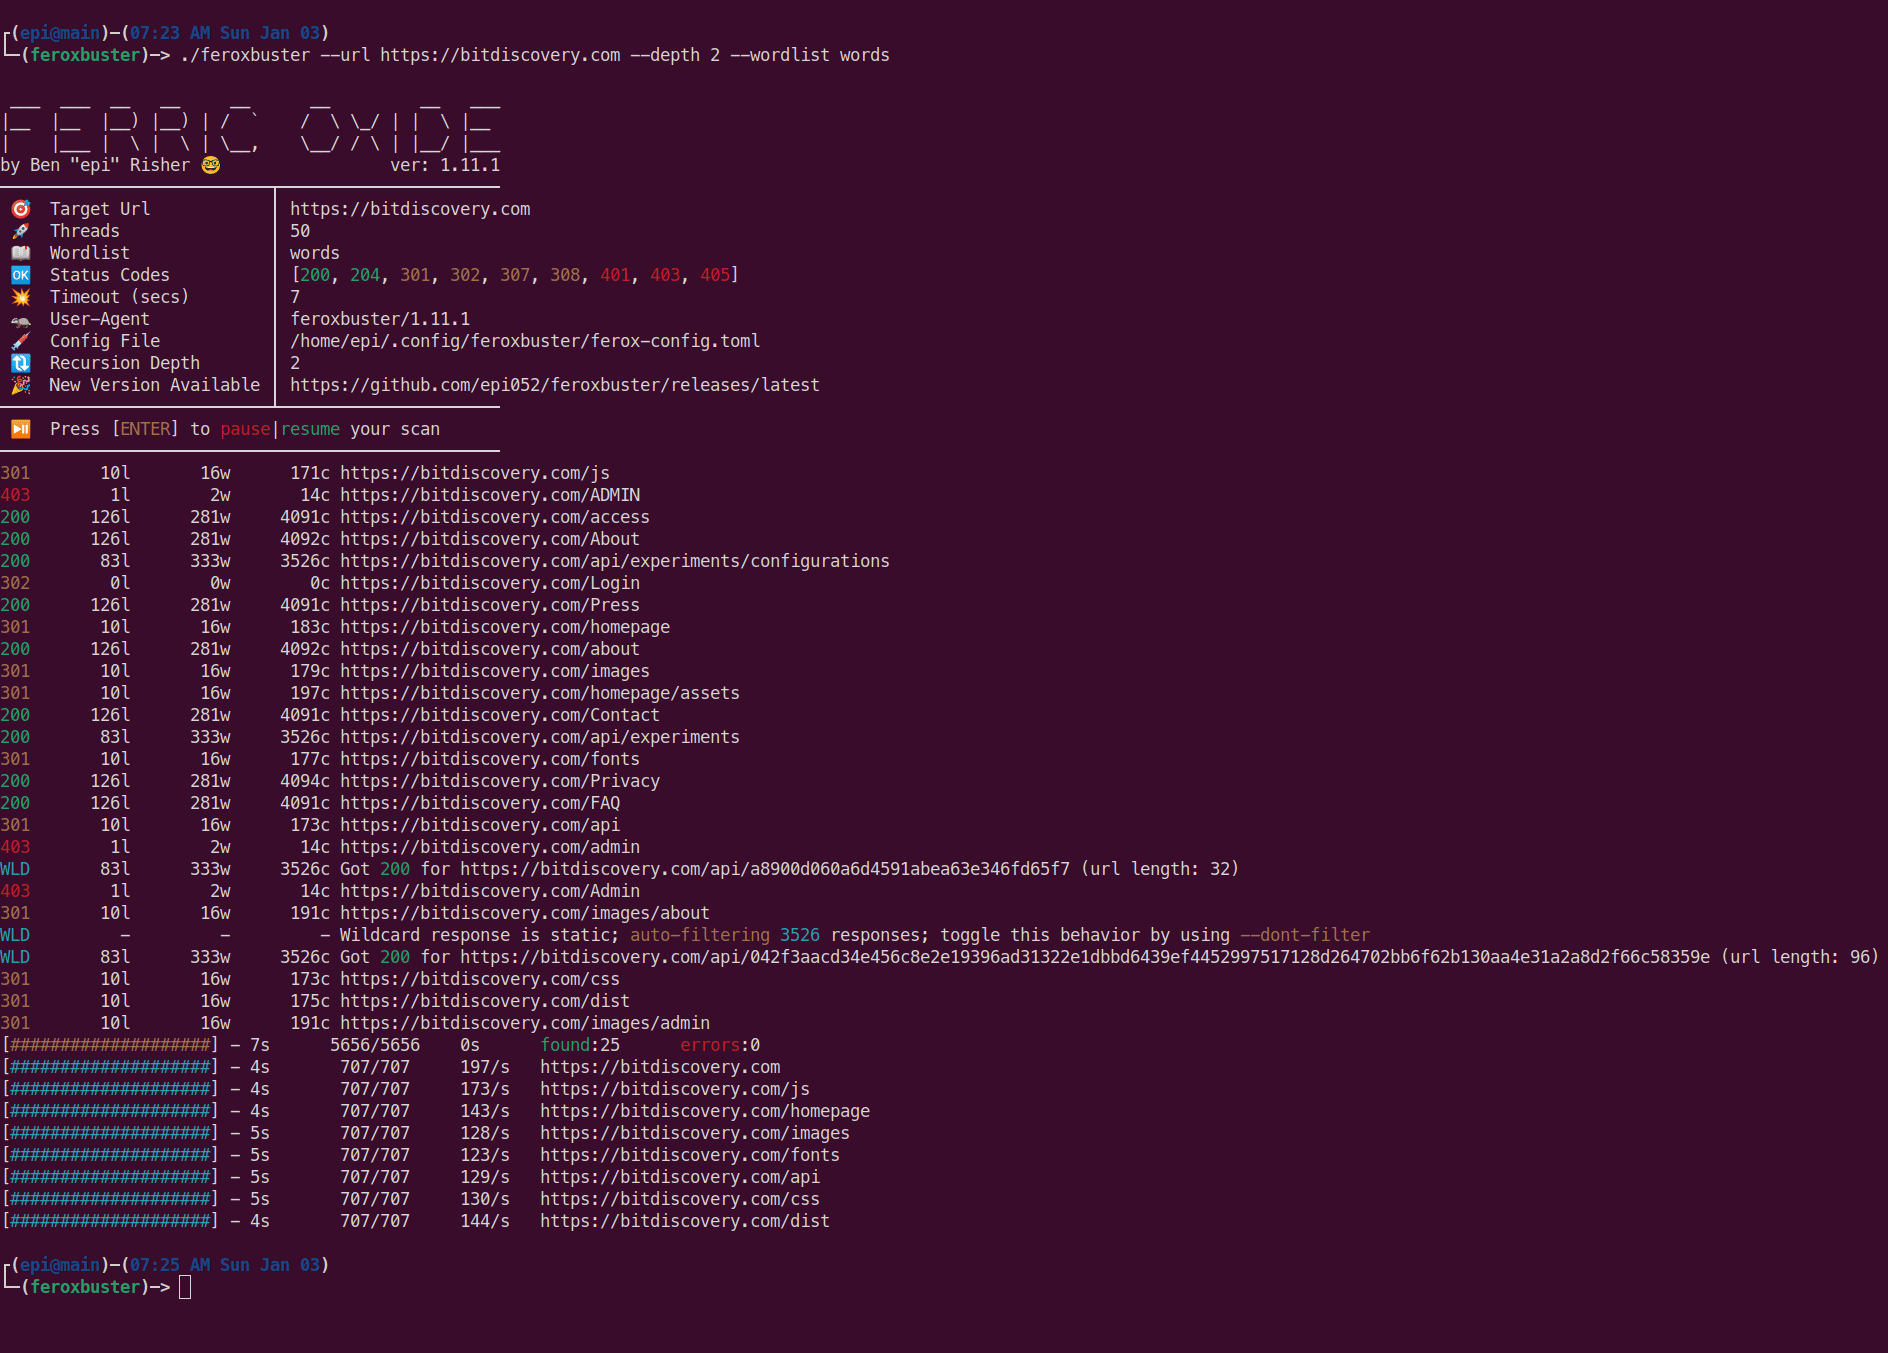 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 hahwul/xspear
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
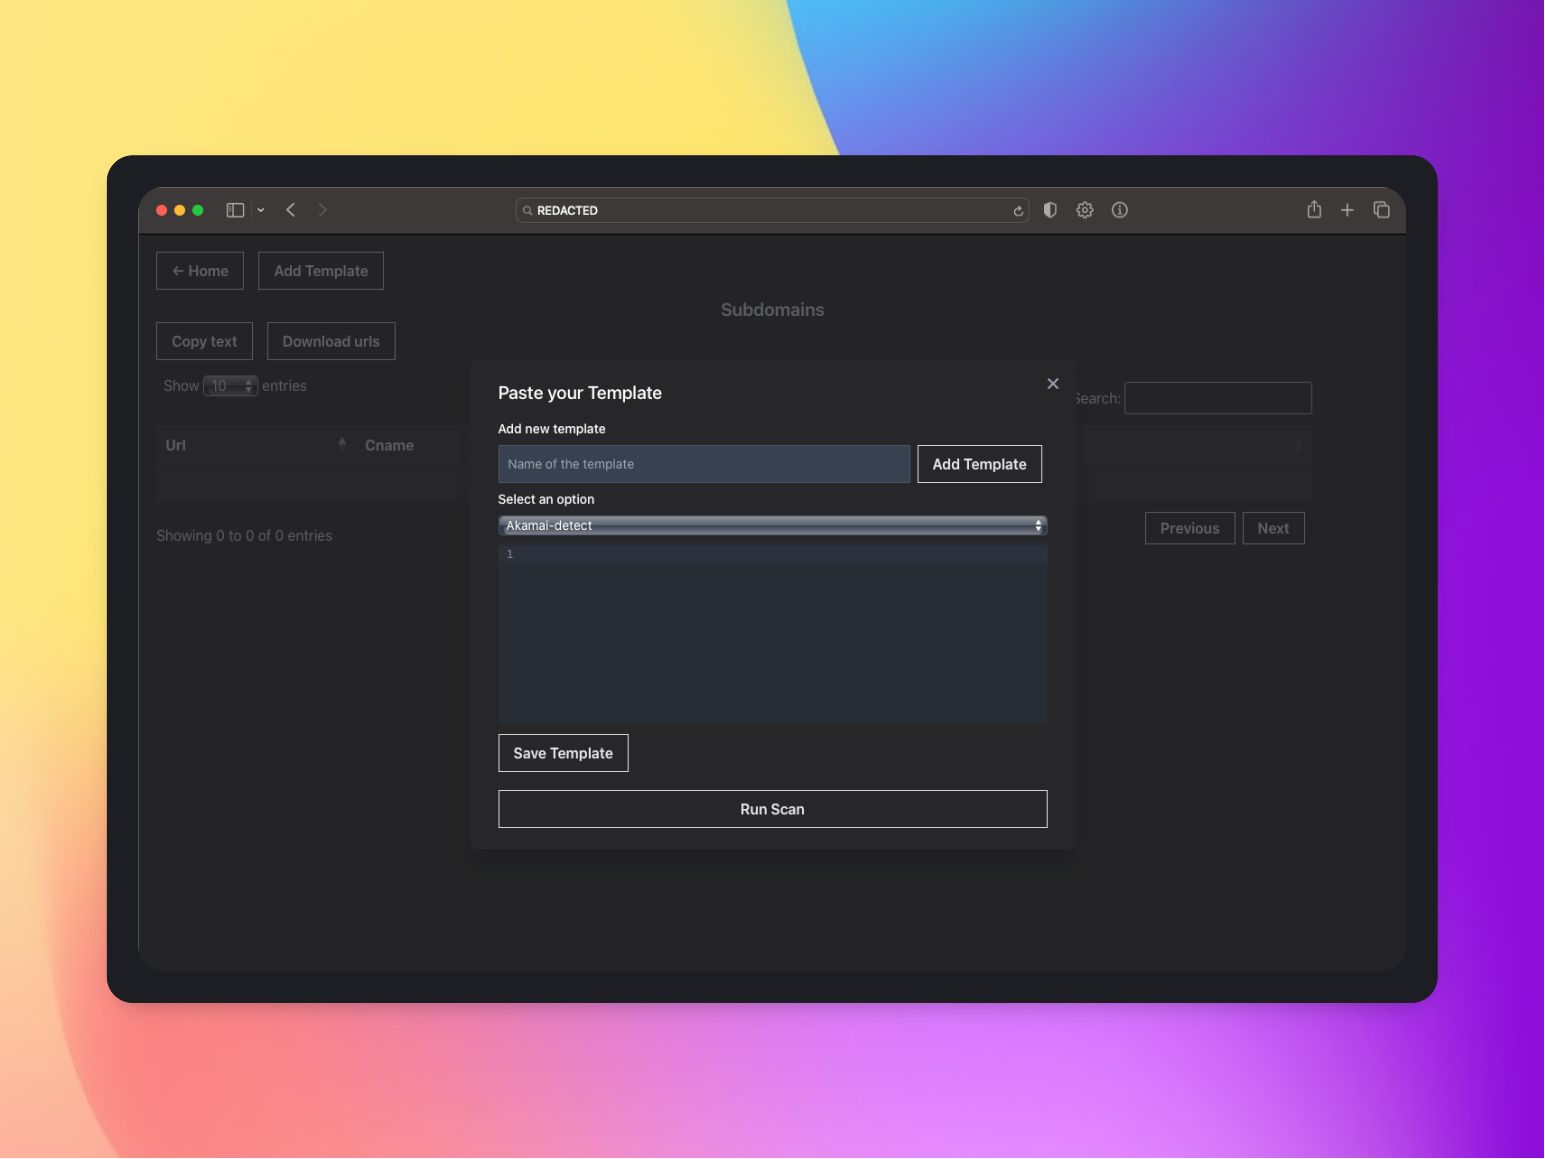
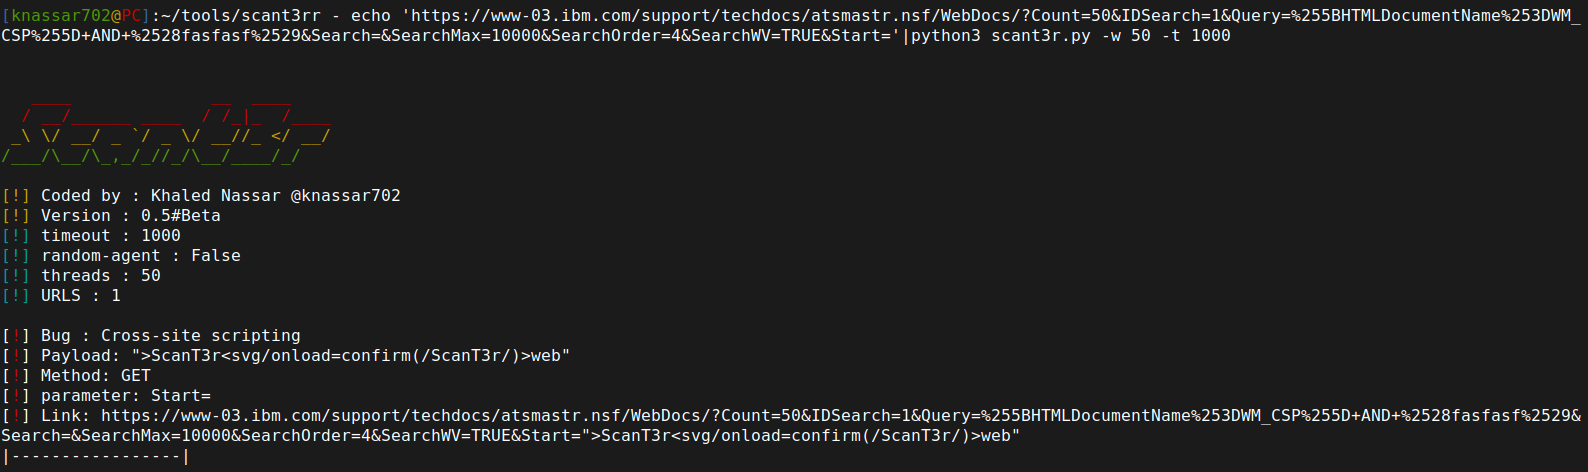 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
 hood3drob1n/bingoo
BinGoo! A Linux bash based Bing and Google Dorking Tool