

CVE-2023-34965
 agenty0/cve-2023-34965
SSPanel UIM is a multi-purpose agency service sales management system specially designed for Shadowsocks / V2Ray / Trojan protocols. SSPanel-Uim…
information-gatheringmisconfigurationpenetration-testing+2
3
agenty0/cve-2023-34965SSPanel UIM is a multi-purpose agency service sales management system specially designed for Shadowsocks / V2Ray / Trojan protocols. SSPanel-Uim…
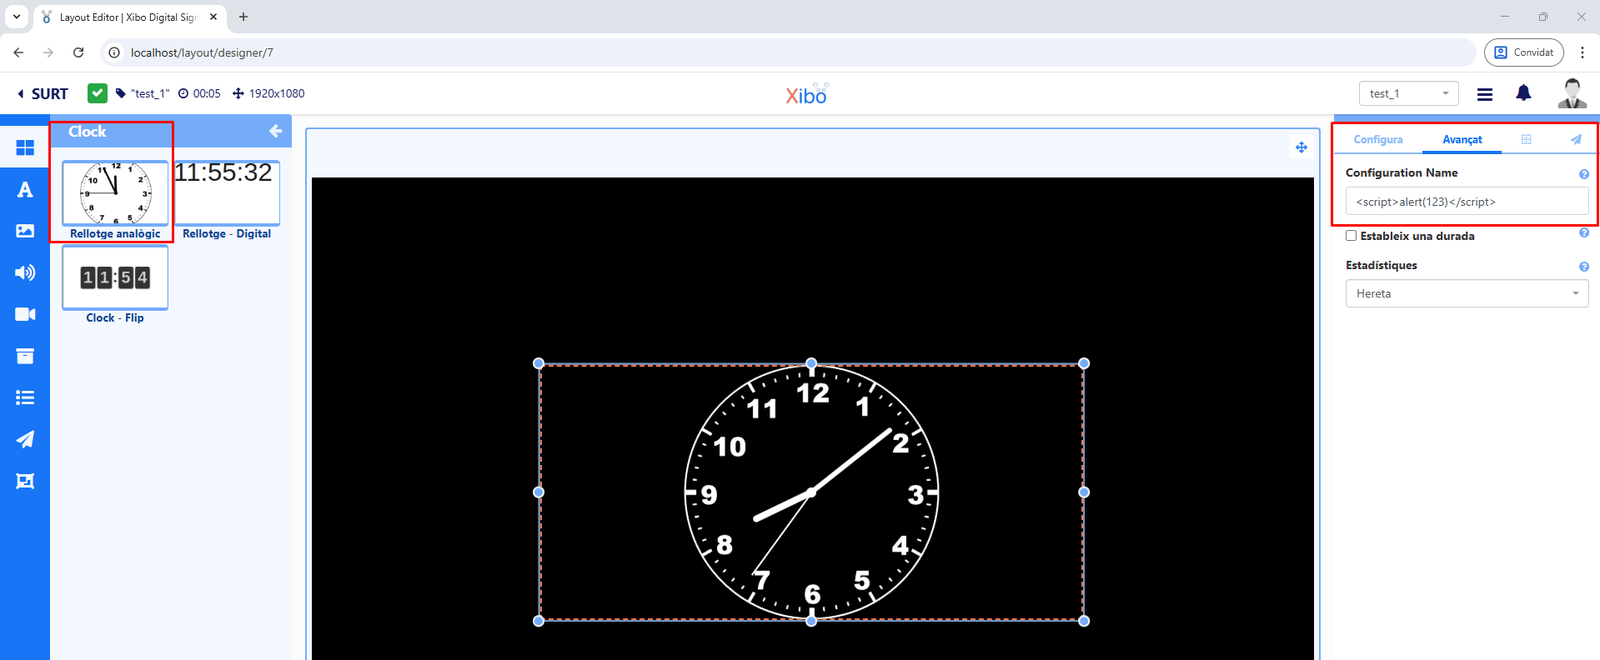 marinafabregat/cve-2025-41089
Reflected Cross-Site Scripting (XSS) in Xibo CMS v4.1.2 from Xibo Signage, due to a lack of proper validation of user input.
 tansique-17/cve-2025-26199
Public Disclosure
 dievus/cve-2022-27665
Reflected XSS via AngularJS Sandbox Escape Expressions in IPSwitch WS_FTP Server 8.6.0
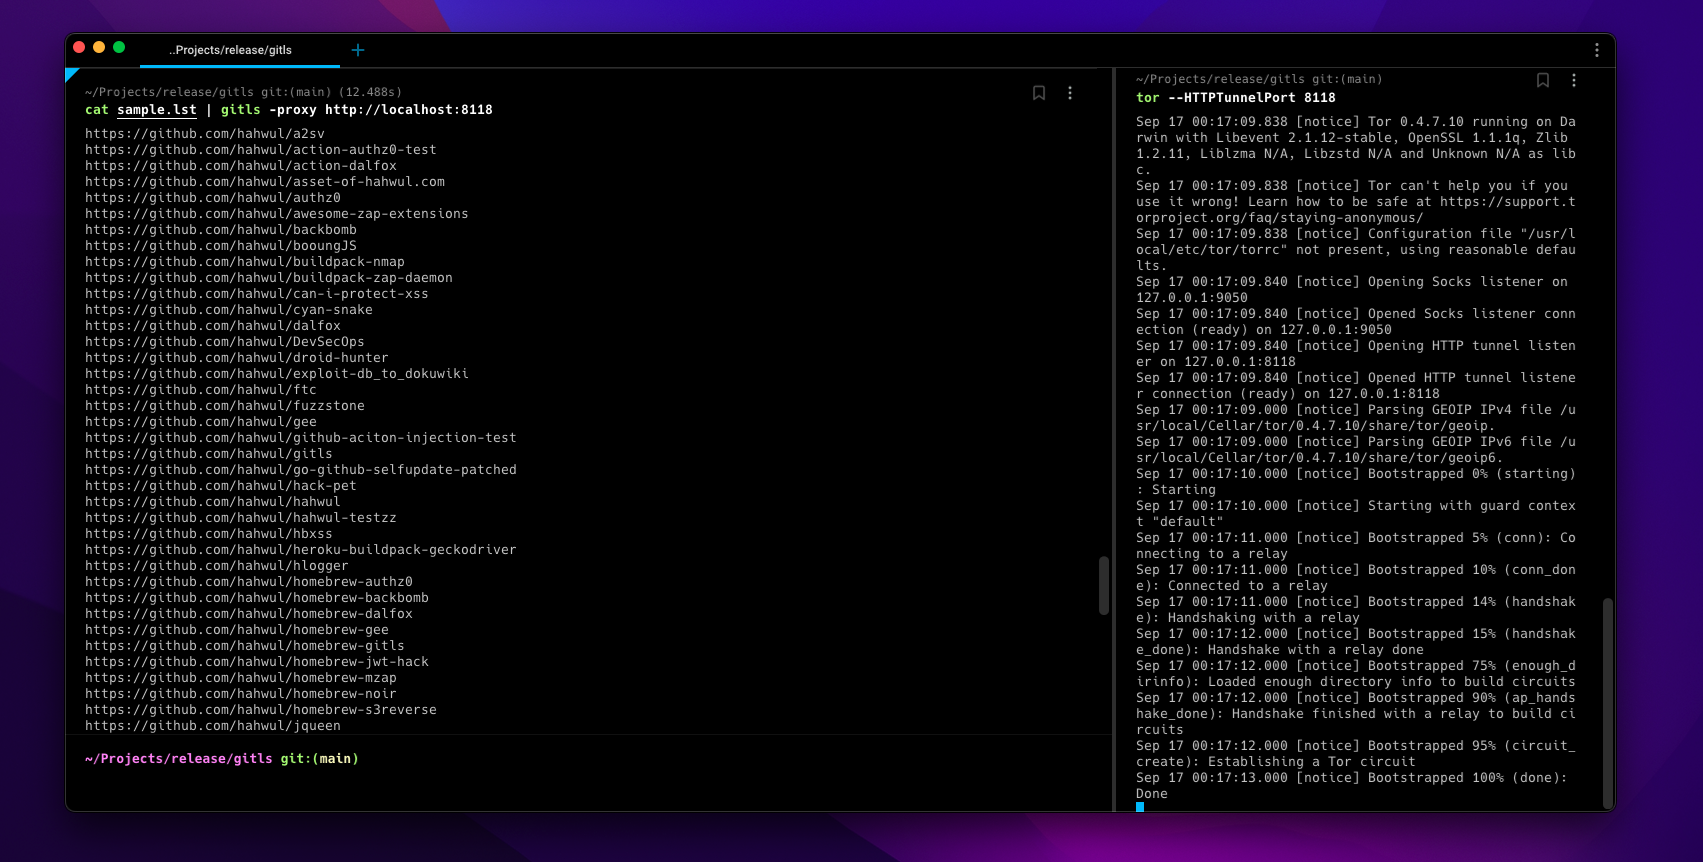 hahwul/gitls
🖇 Enumerate git repository URL from list of URL / User / Org. Friendly to pipeline
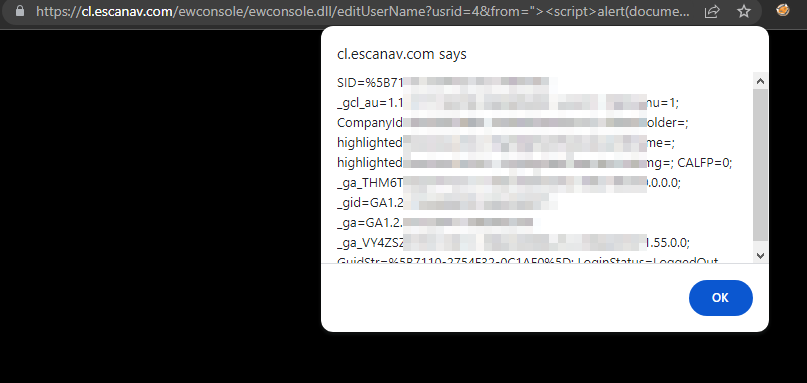 sahiloj/cve-2023-31703
A reflected Cross-Site Scripting (XSS) vulnerability exists in the Edit User functionality of the Microworld Technologies eScan Management Console…
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…
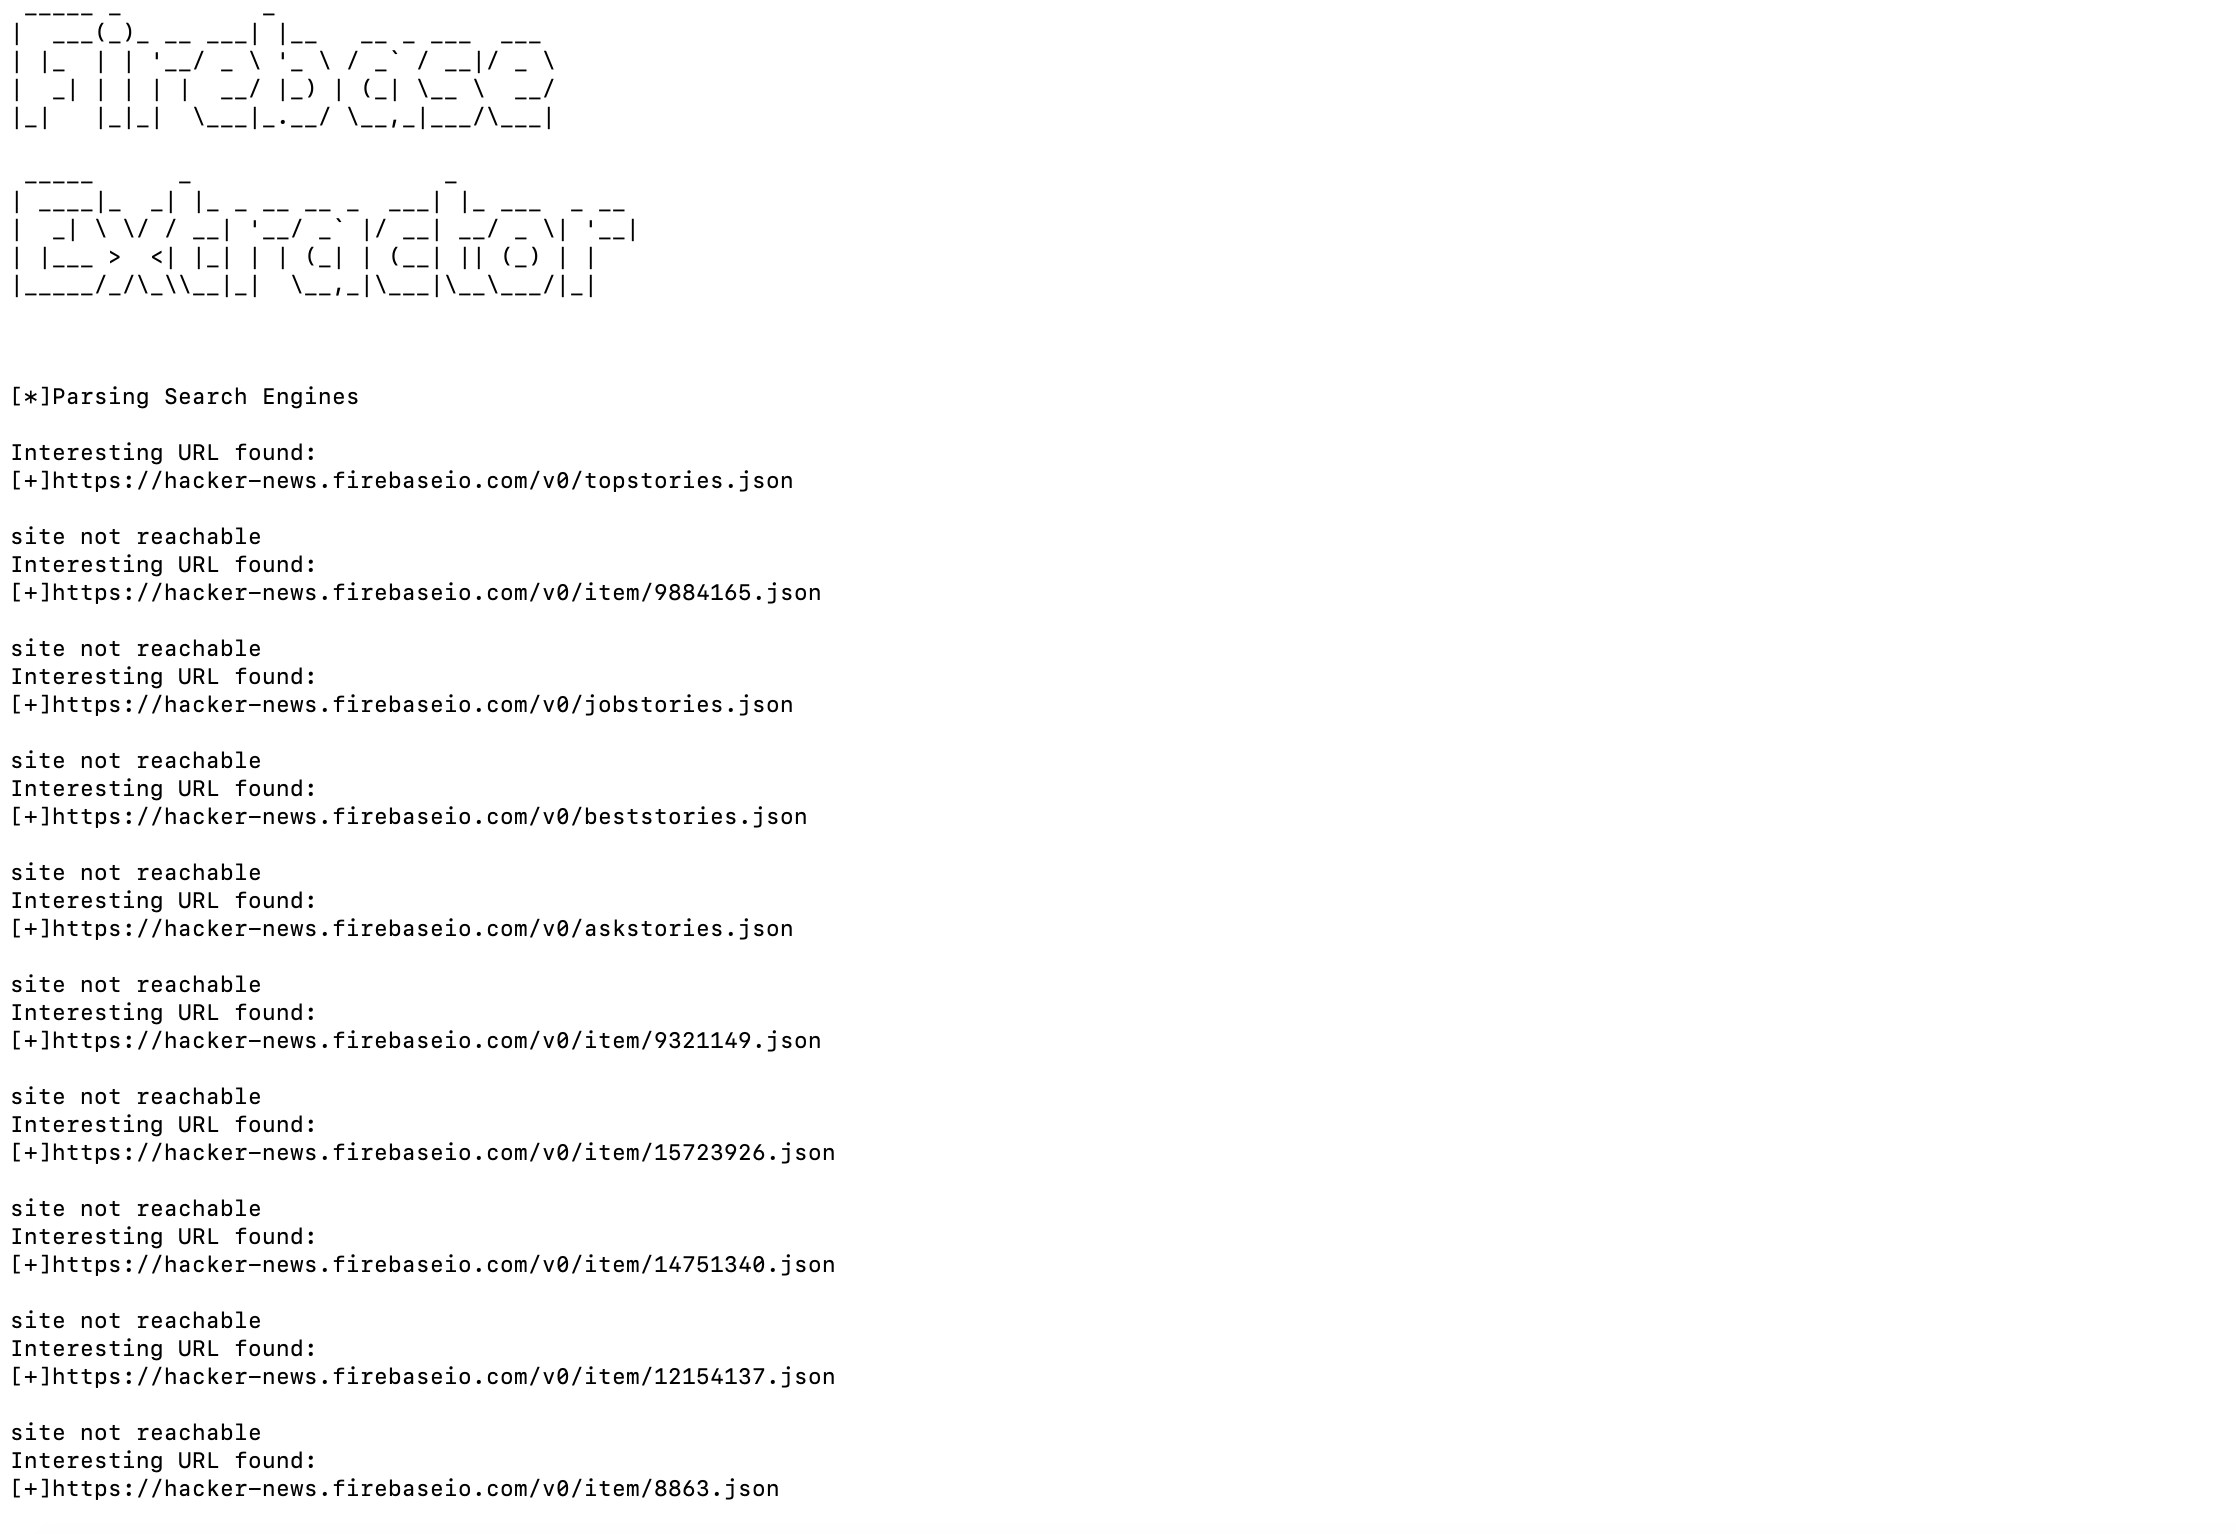 viperbluff/firebase-extractor
A tool written in python for scraping firebase data
 bevennyamande/cve-2024-10557
A CSRF POC for Updating the Profile of a Hospital leading to Account Takeover
 r0lh/cve-2019-8449
User Enumeration Proof Of Concept Exploit for CVE-2019-8449
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 ahrixia/cve-2023-43325
mooSocial v3.1.8 is vulnerable to cross-site scripting on user login function.
 maikroservice/cve-2022-3949
XSS in Simple Cashiering System
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 saykino/cve-2025-56221
Advisory detailing CVE-2025-56221, an authentication rate-limiting flaw in Ascertia SigningHub allowing brute-force attacks, with affected versions…
 nagisayumaa/cve-2025-10377
CVE-2025-10377