
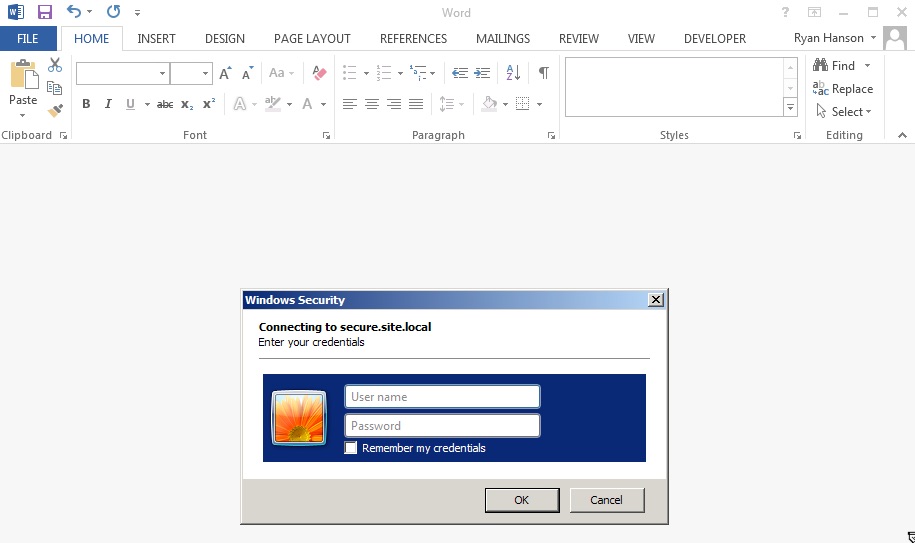
phishery
 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
phishingphishing-toolssocial-engineering+1
ryhanson/phisheryAn SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.