
Archived
socialhunter
 utkusen/socialhunter
crawls the website and finds broken social media links that can be hijacked
crawlerosintphishing-tools+3
779
utkusen/socialhuntercrawls the website and finds broken social media links that can be hijacked
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 hannob/snallygaster
Tool to scan for secret files on HTTP servers
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 randomrobbiebf/csp-log4j
Finds CSP report urls and tests to see if they are vulnerable to log4j
 devploit/debughunter
Chrome extension that passively finds debug parameters, sensitive headers and exposed paths (.env, .git, actuator) while you browse. Built for bug…
 danmcinerney/elite-proxy-finder
Finds public elite anonymity proxies and concurrently tests them
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 devploit/nomore403
403/401 bypass tool: finds HTTP access-control bypasses via path, method, header and raw-request mutations. Baseline diff, auto-calibration,…
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
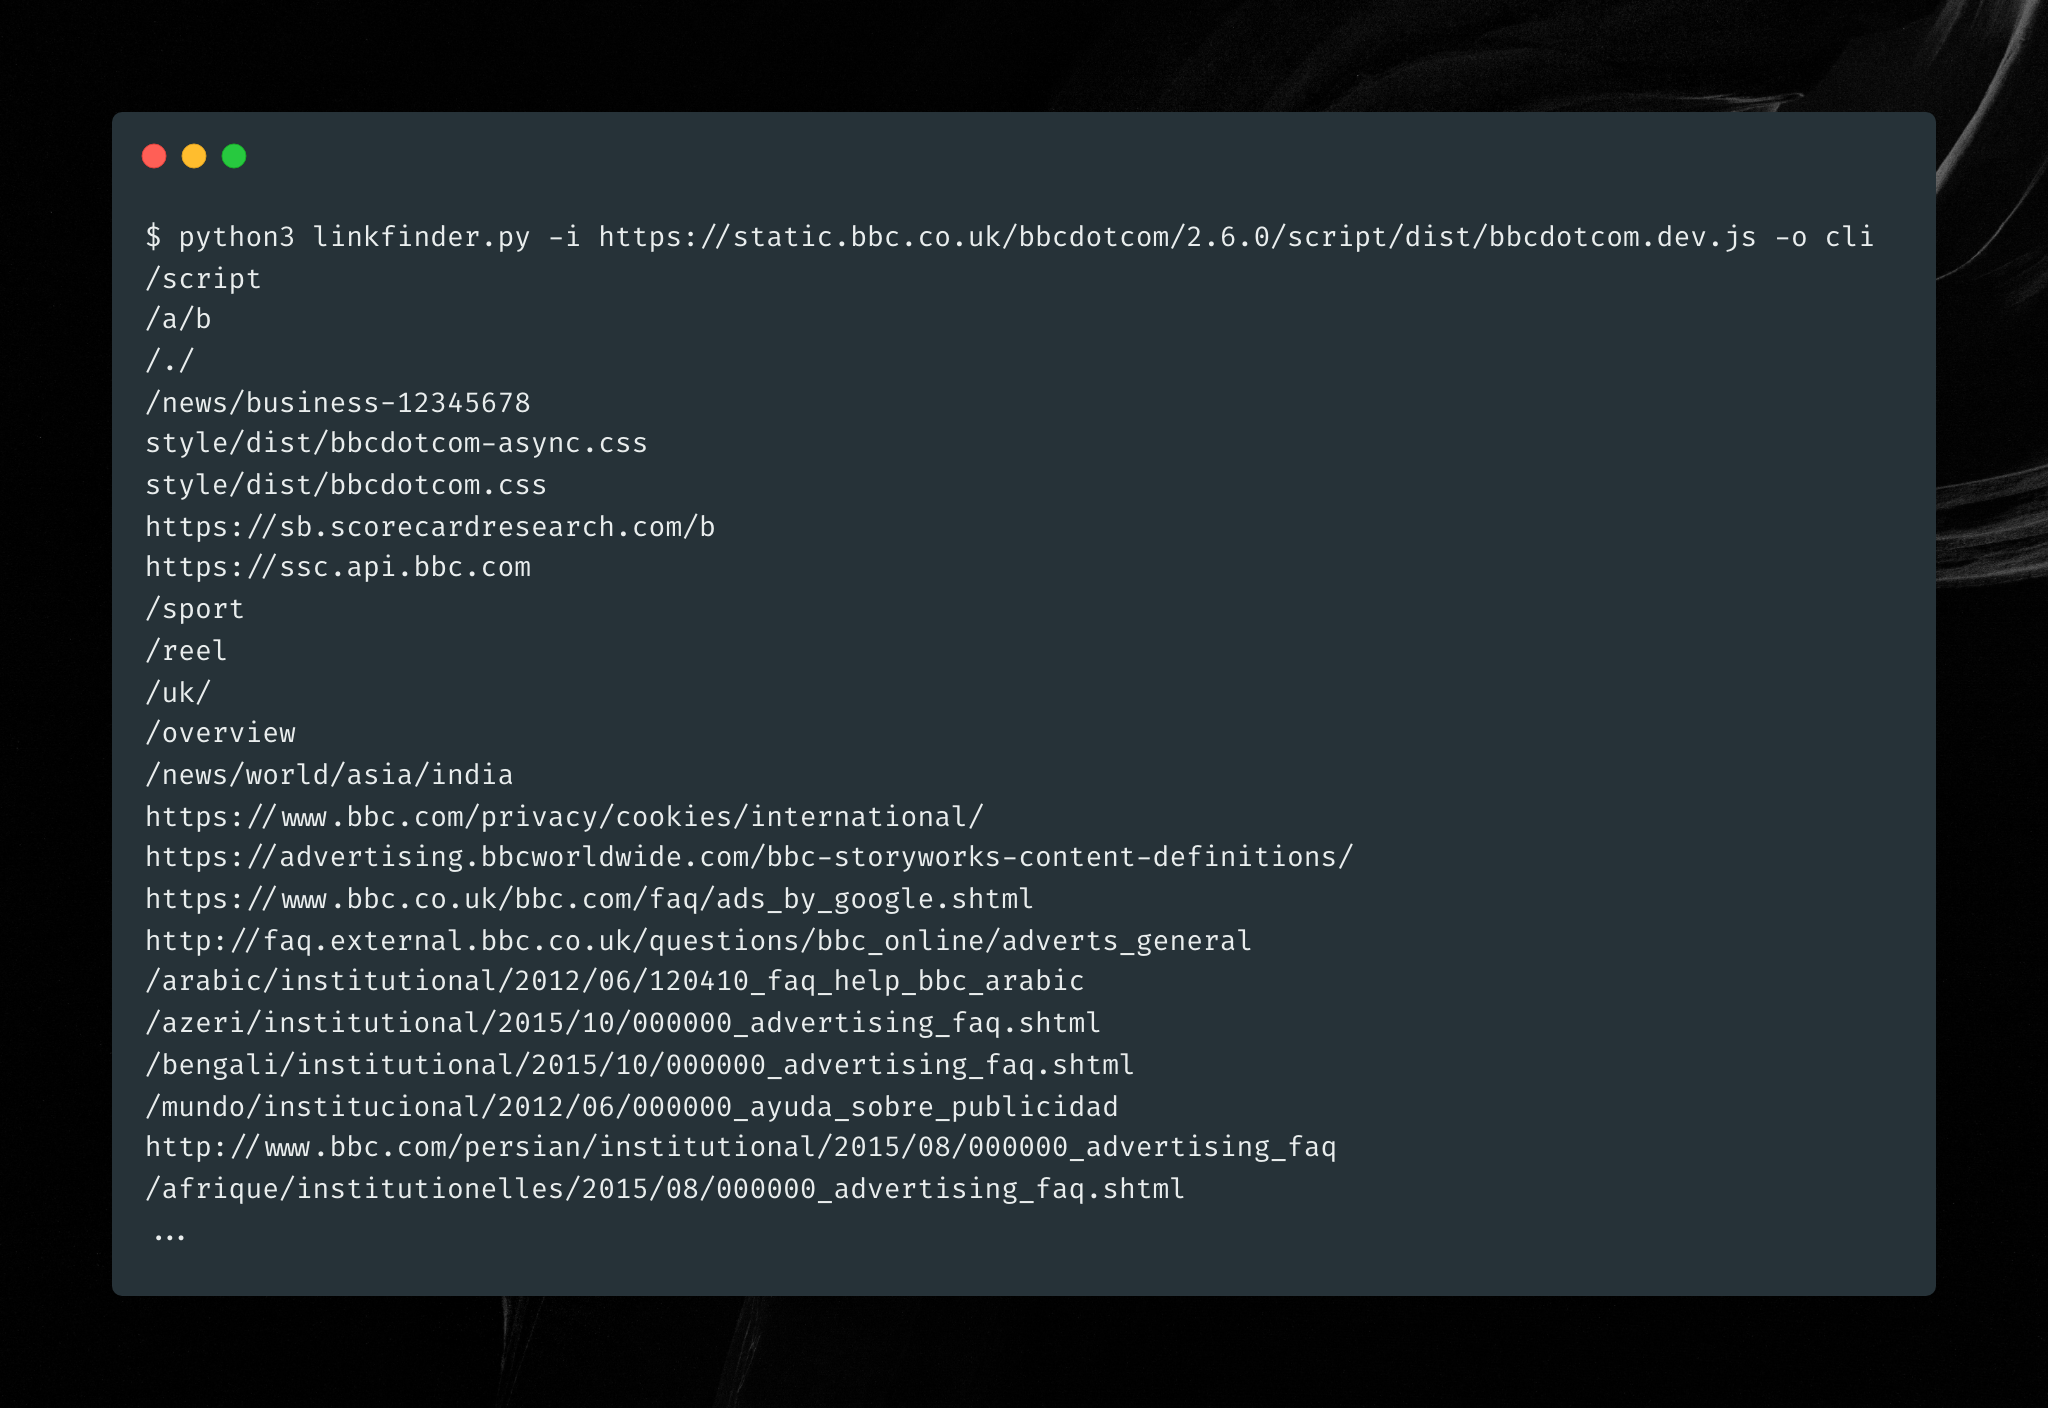 gerbenjavado/linkfinder
A python script that finds endpoints in JavaScript files
 graph-x/davscan
Fingerprints servers, finds exploits, scans WebDAV. May or may not also make coffee.
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 retirejs/retire.js
scanner detecting the use of JavaScript libraries with known vulnerabilities. Can also generate an SBOM of the libraries it finds.
 robre/scripthunter
Tool to find JavaScript files on Websites