apache__jspwiki_CVE-2022-46907_2-11-3

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…

Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…

Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…

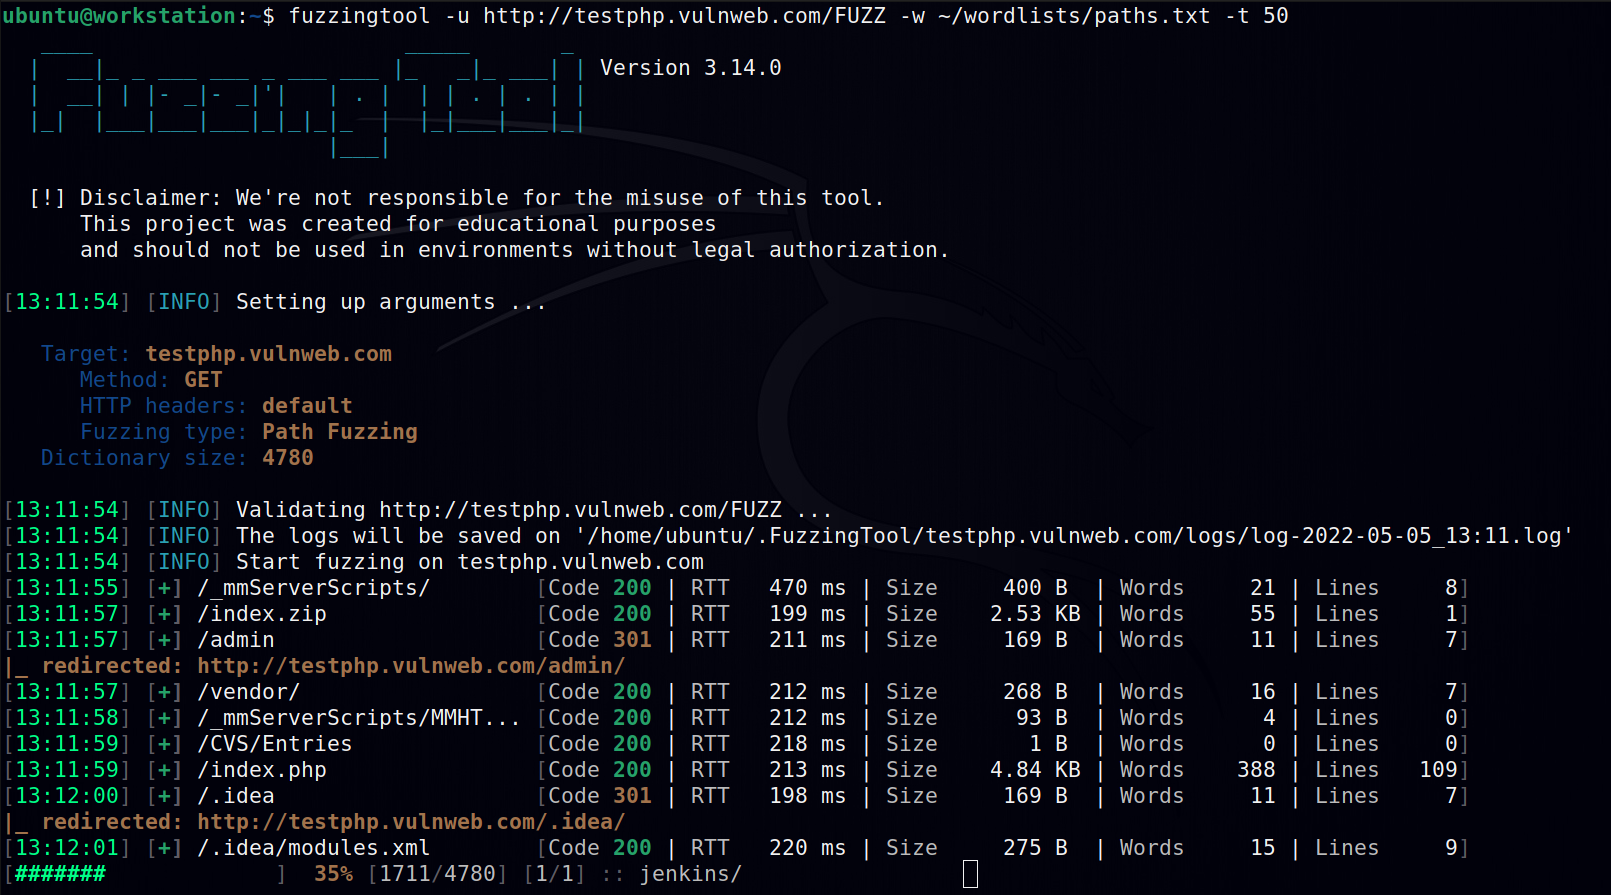
Software for fuzzing, used on web application pentestings.

Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…

Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…

WordPress security scanner that enumerates vulnerable plugins, themes, and users to identify misconfigurations and known vulnerabilities for…

CVE-2022-23779 is a security vulnerability in Zoho ManageEngine Desktop Central ,Testing for CVE-2022-23779 using curl

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.

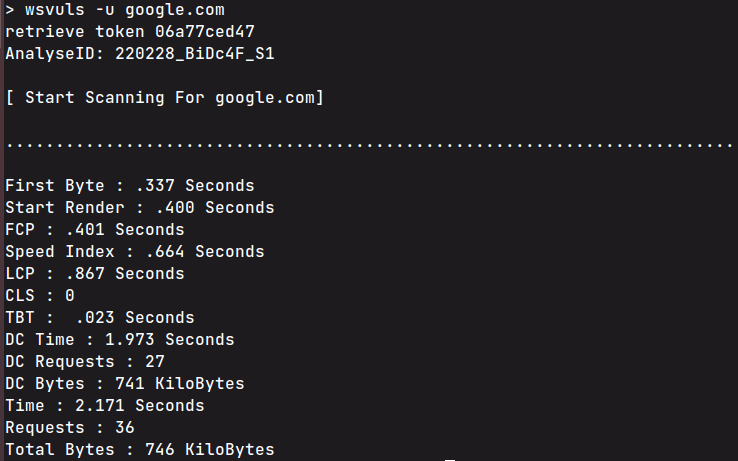
CLI website vulnerability scanner that detects outdated server software, insecure HTTP headers, and extracts Cloudflare IP/port data with performance…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

Nuclei template to detect OpenSSH servers vulnerable to CVE-2024-6387 (regreSSHion) by checking software version.

Detection for CVE-2025-24016 - Deserialization of Untrusted Data Vulnerability in the Wazuh software

Proof of concept for exploitation of the vulnerability described in CVE-2025-11554, which concerns the possibility of a privilege escalation through…