
Bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.

Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.

HTTP(S)/WS(S)/TCP Tunnels to localhost using only SSH.

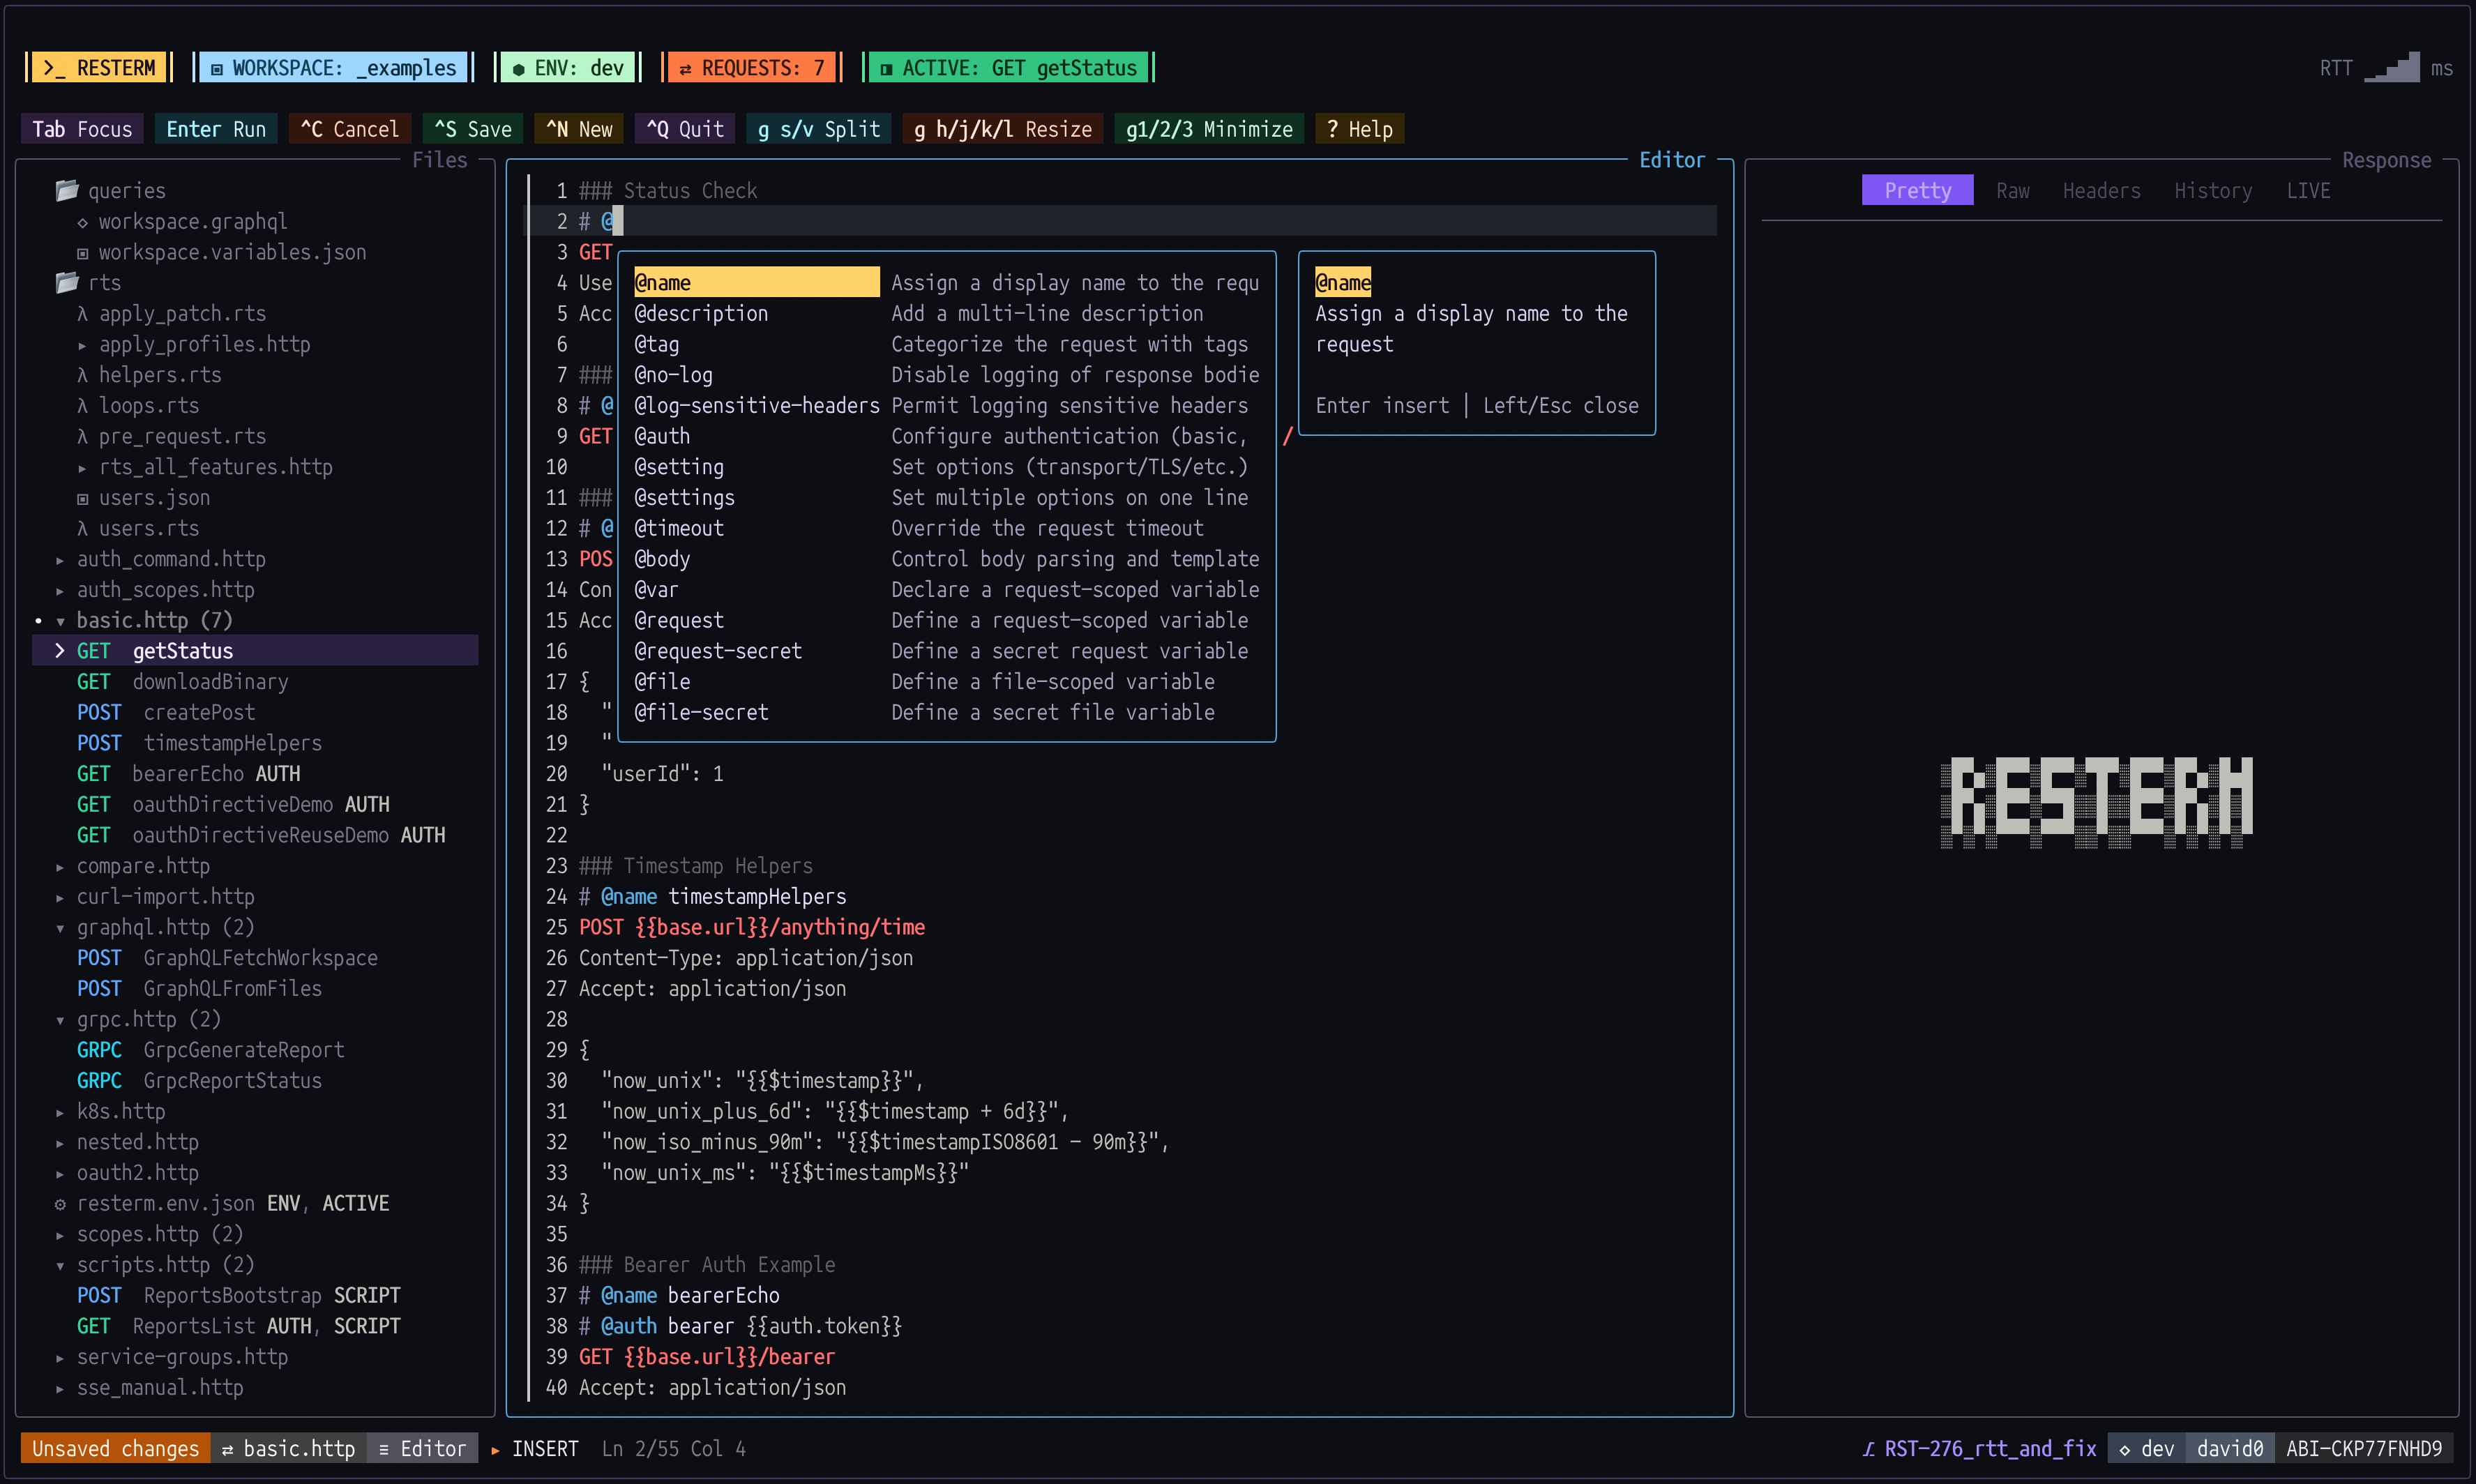
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Proof-of-concept demonstrating a newline injection vulnerability in OpenSSH ProxyCommand (CVE-2025-61984), allowing command injection via crafted SSH…

Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…

POC for the CVE-2026-1459 which payload changes root SSH password.

Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…

Gogs Under Attack: Unpacking the Critical SSH Vulnerability (CVE-2024–39930)

Authentication bypass exploit for CVE-2022-40684 targeting FortiOS, FortiProxy, and FortiSwitchManager. Checks vulnerability and overwrites admin SSH…

Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager, enabling SSH key injection…

Automated Exploit Tool for Grafana CVE-2021-43798: Scanning common files that contain juicy informations and extracting SSH keys from compromised…

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…

Project with sublist3r, massan, CVE-2018-15473, ssh bruteforce, ftp bruteforce and nikto.

A secure low code deception runtime framework, leveraging AI for System Virtualization.

A collection of scripts which may come in handy during your freedom fighting activities.

Graphical Web interface developed to facilitate the use of security information tools.

MitM attack allowing a malicious interloper to impersonate a legitimate server when a client attempts to connect to it

CVE-2024-41817 POC ImageMagick <= 7.1.1-35 Arbitrary Code Execution