
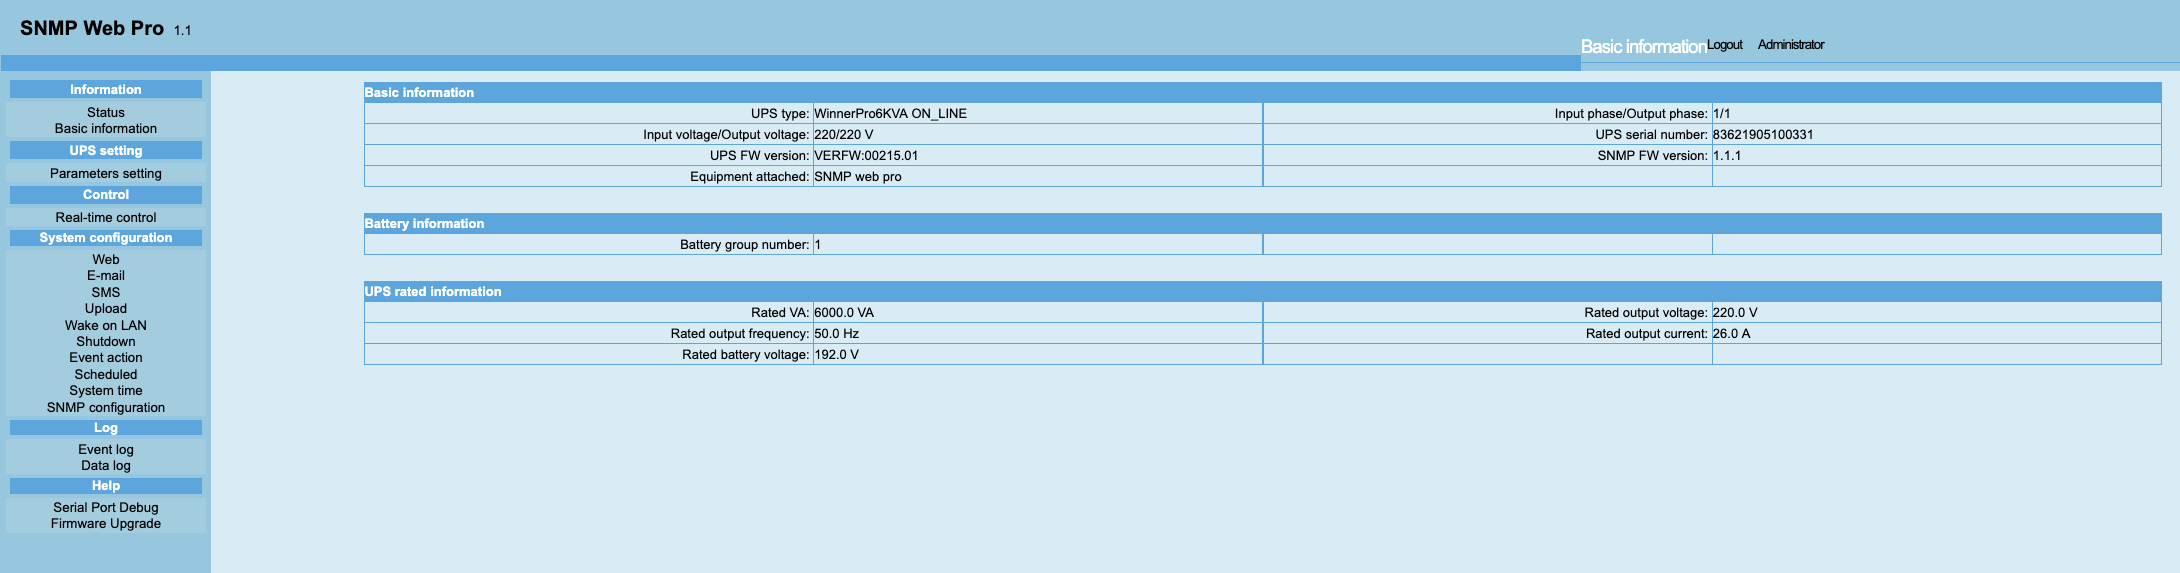
CVE-2026-44402
 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
embedded-systems-securityexploitationiot-security+5
1
virgula0/cve-2026-44402Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 mc-17/cve-2023-38609
SIP bypass using package scripts
 jet-pentest/cve-2021-3130
Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…