
CVE-2006-2842
CLI scanner for CVE-2006-2842 (PHP include() path truncation) vulnerability. Scans single or multiple URLs to detect this specific web application…

CLI scanner for CVE-2006-2842 (PHP include() path truncation) vulnerability. Scans single or multiple URLs to detect this specific web application…

CLI scanner for CVE-2020-17453 that tests single or multiple URLs for the vulnerability, designed for bug bounty hunters and penetration testers.

jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

Enumeration tool for CVE-2024-45440

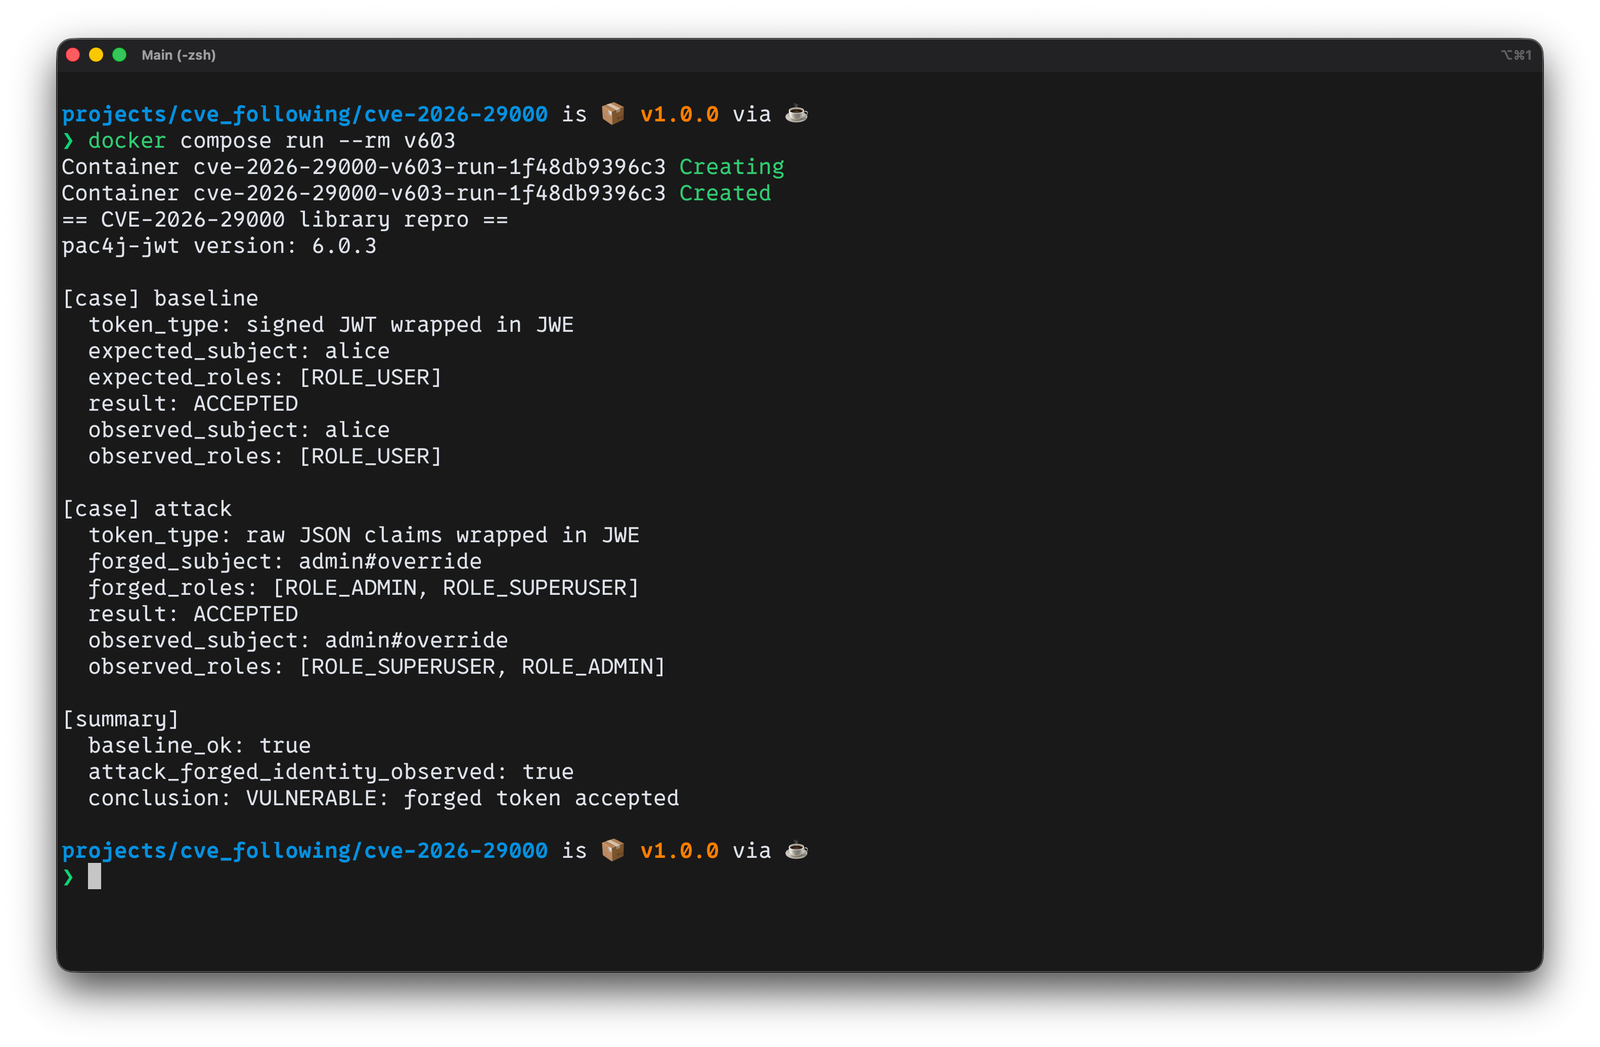
Library-level proof-of-concept lab demonstrating CVE-2026-29000 in pac4j-jwt, comparing vulnerable and patched versions with Docker to show forged…

Demonstrates CVE-2023-41080, an open redirect in Apache Tomcat, comparing vulnerable and patched endpoints to show arbitrary site redirection.

A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…

Burp plugin that clusters responses to show an overview of received responses

The goal of this project is to demonstrate the log4j cve-2021-44228 exploit vulnerability in a spring-boot setup, and to show how to fix it.

Single-threaded PowerShell PoC scanner for CVE-2023-20198 targeting Cisco IOS XE devices. Quick proof-of-concept for vulnerability detection and…

Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…

Lightweight CLI scanner for CVE-2021-31589 that checks single or multiple URLs for the vulnerability, outputting results to a file for bug bounty and…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

Hands-on lab for CVE-2026-40072 — SSRF vulnerability in web3.py via CCIP Read (EIP-3668)

POC to test/exploit drupal vulnerability SA-CORE-2018-004 / CVE-2018-7602

A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…

JSM Show Post Metadata < 4.9.1 - Contributor+ Stored XSS via Custom Field Meta Key

WordPress JSmol2WP Plugin 1.07版本中存在安全漏洞。攻击者可利用该漏洞读取任意文件。