

dalfox
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
devsecopsdynamic-code-analysispenetration-testing+5
5.3k
hahwul/dalfoxFast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 kiraly07/demo_cve-2025-3248
Educational lab simulating CVE-2025-3248 with a vulnerable Docker service and PoC exploit for hands-on security training and mitigation practice.
 rootdirective-sec/cve-2026-39987-lab
Local Docker lab reproducing CVE-2026-39987, a pre-auth RCE in marimo's terminal WebSocket. Compares vulnerable and patched versions with least-harm…
 edgecases-purplehax/cve-images
Intentionally-vulnerable nginx 1.30.0 CVE lab images (CVE-2026-40701/42934/42945/42946) for isolated security research. Lab use only.
 rootdirective-sec/cve-2026-23744-lab
Docker lab to compare vulnerable and patched builds of MCPJam Inspector for CVE-2026-23744, demonstrating network binding differences and API…
 cved-sources/cve-2017-7529
Docker-based reproduction of CVE-2017-7529 (Nginx integer overflow) for security testing and education. Part of the Cved vulnerable container…
 jasalurah/creating-a-vulnerable-docker-environment-cve-2023-30212-
Docker-based vulnerable environment for practicing CVE-2023-30212 exploitation, featuring an OURPHP web app with a reflected XSS vulnerability for…
 layarkacasiber/cve-2021-42013
Docker-based lab environment for exploiting CVE-2021-42013 (Apache HTTP Server path traversal and RCE) with step-by-step setup instructions for…
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
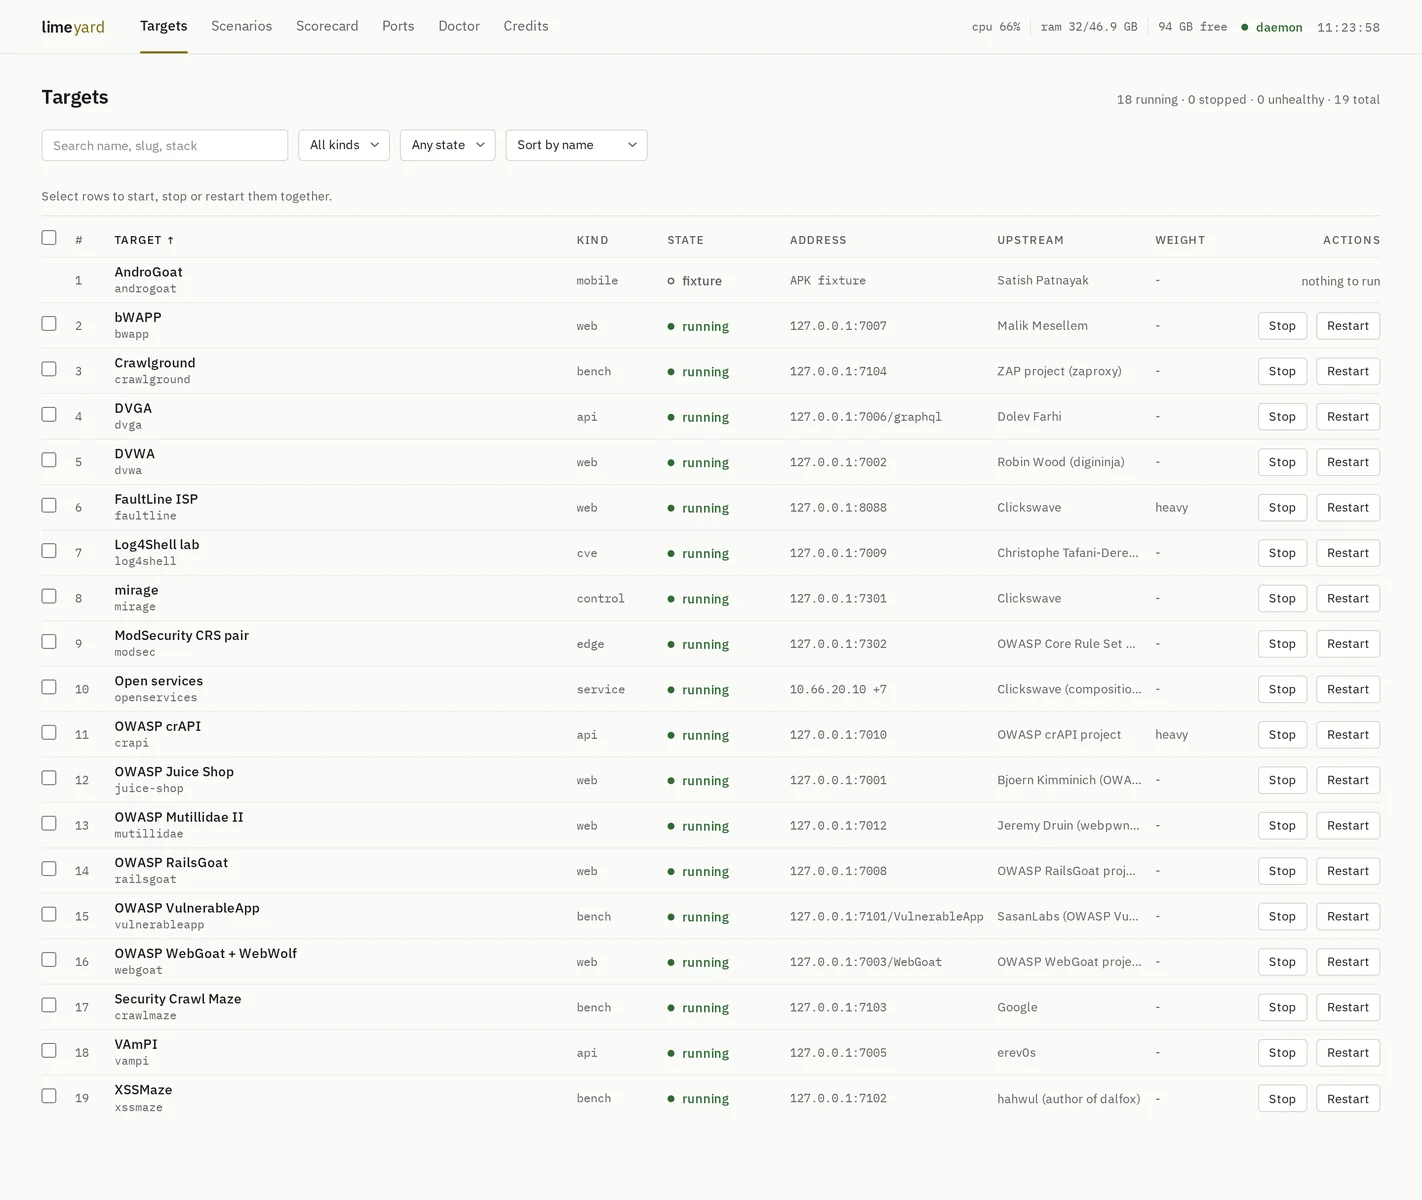 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
 m1k1o/neko
A self hosted virtual browser that runs in docker and uses WebRTC.
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
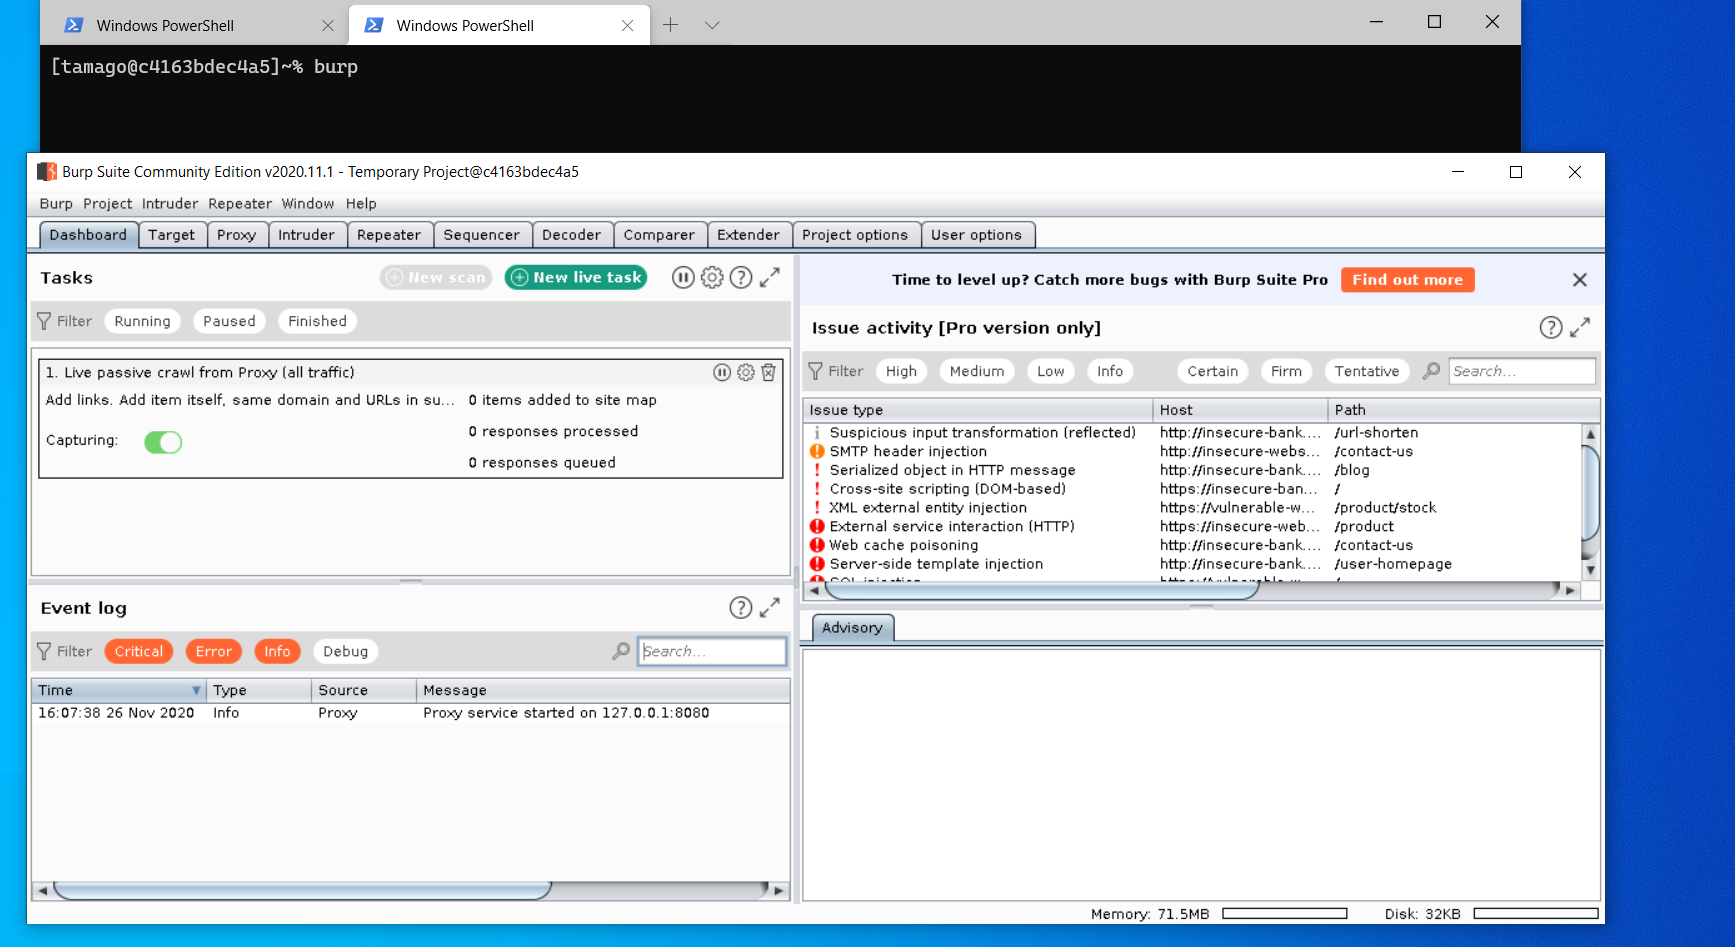 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
 obscuritylabs/log4shell-poc-lab
A lab demonstration of the log4shell vulnerability: CVE-2021-44228