Network-Detection-Engine

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…

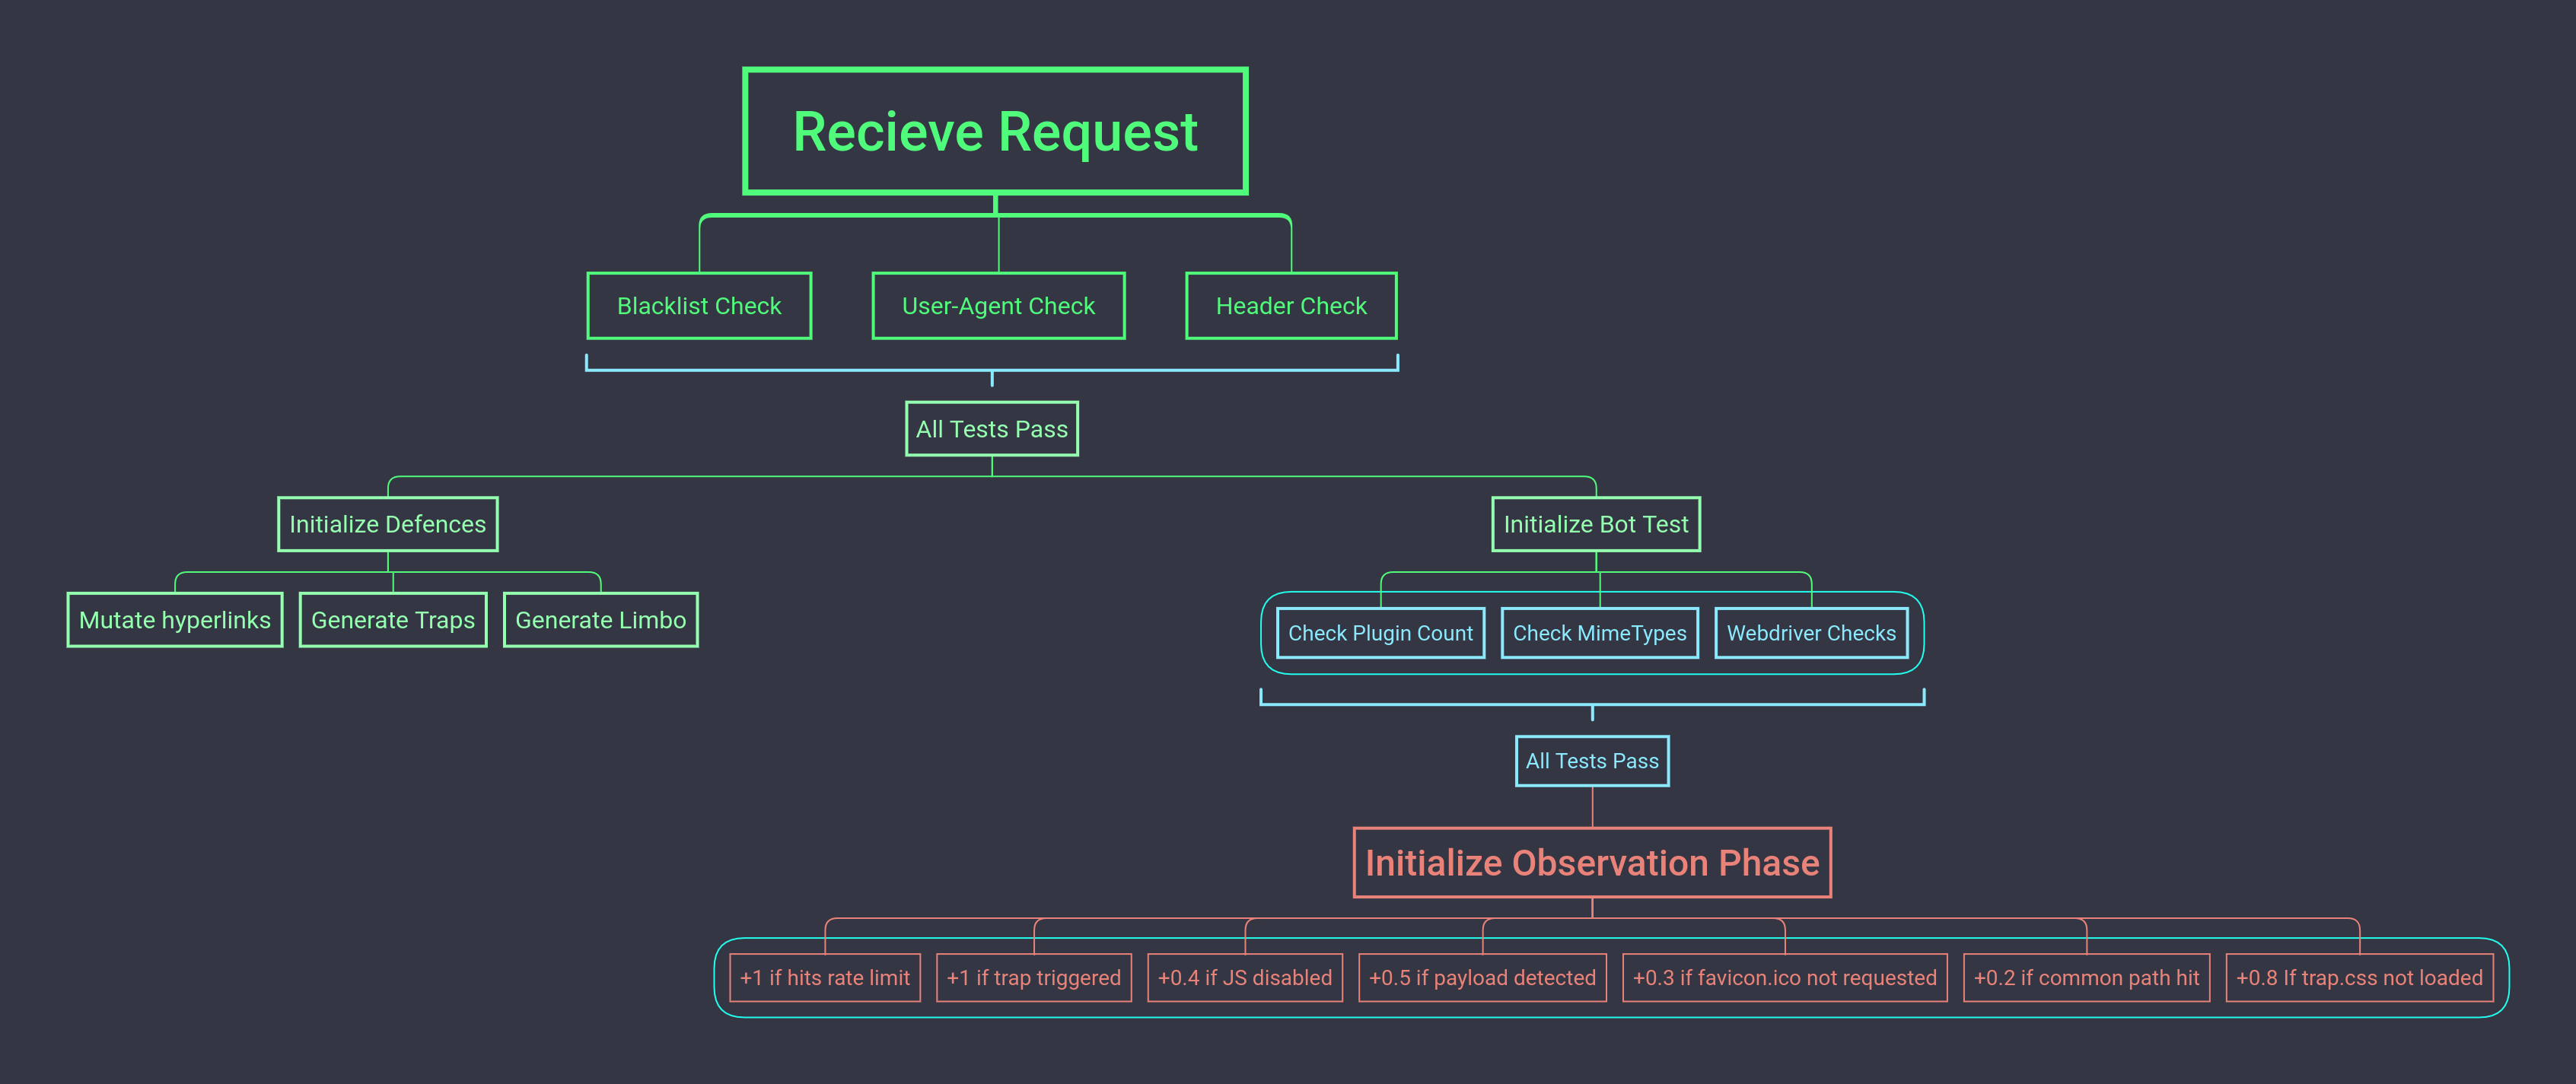
Playwright that anti-bots cannot see, so no captchas: same API, anti-detect stealth headless Firefox, undetected fingerprint, bypass bot detection,…

CVE‑2025‑55182 Detection

Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.

Detection rules for CVE-2025-53770

Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl

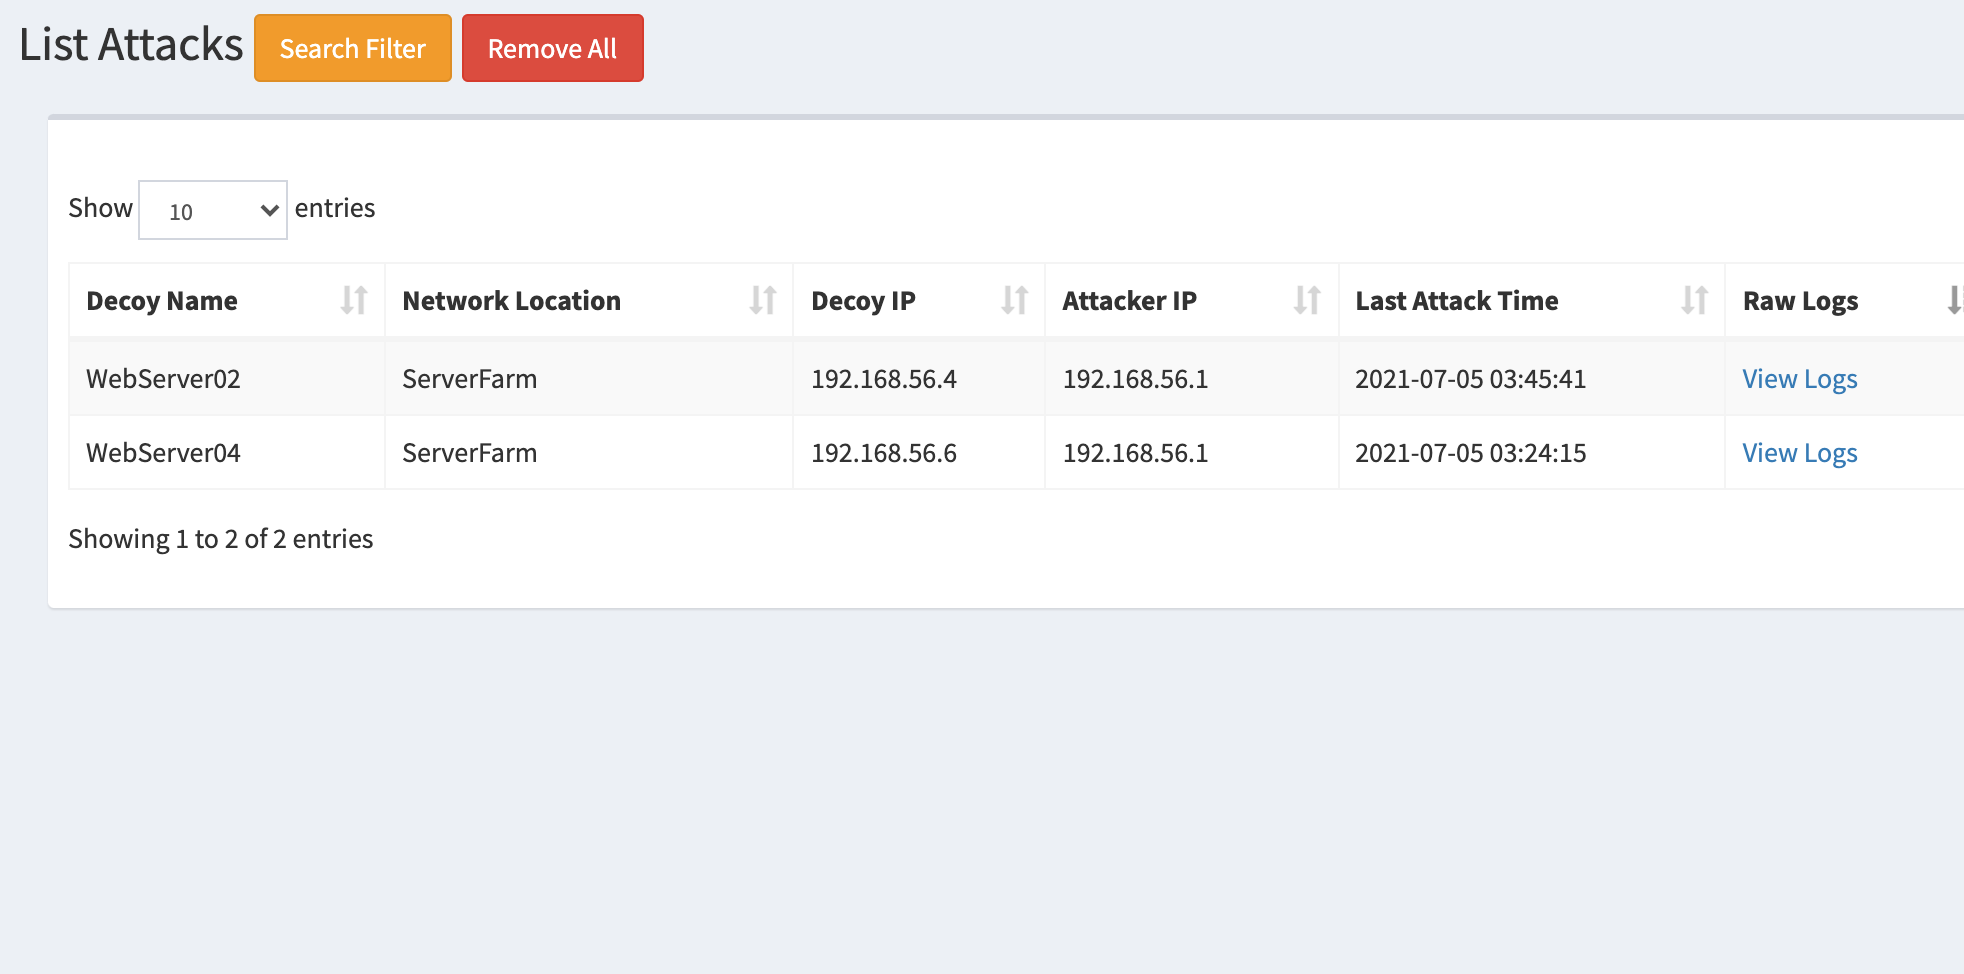
DejaVU - Open Source Deception Framework

This repo exists as a quick and dirty arsenal of methods and scripts to subvert .NET SSL/TLS certificate validation in PowerShell and press on with…

CVE-2025-55182-scanner with 2 different method

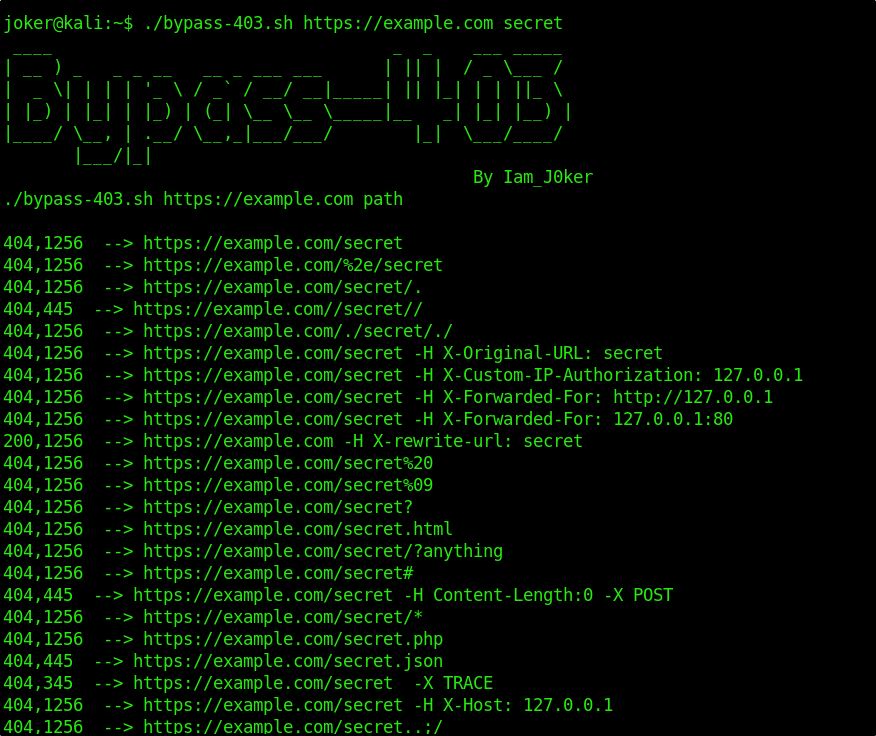
A simple script just made for self use for bypassing 403

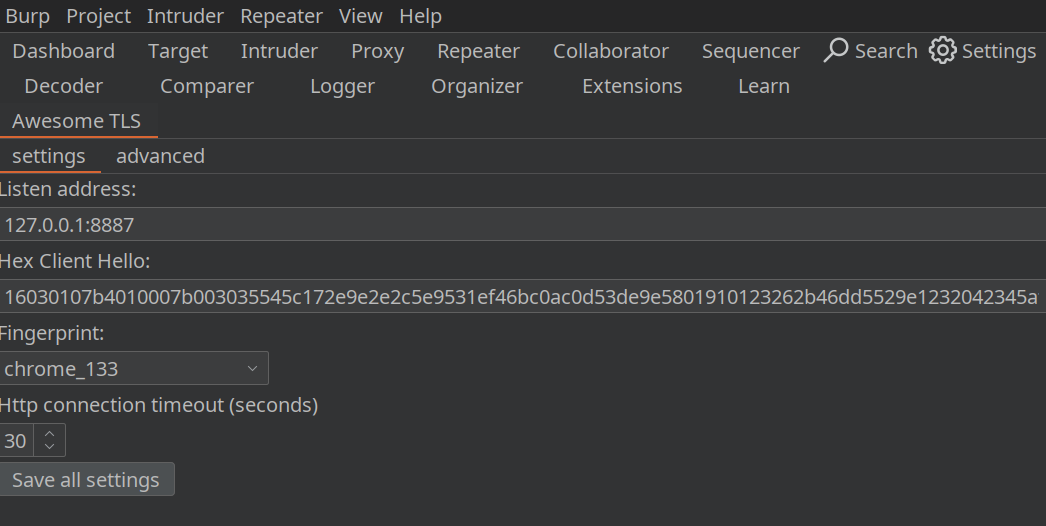
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.

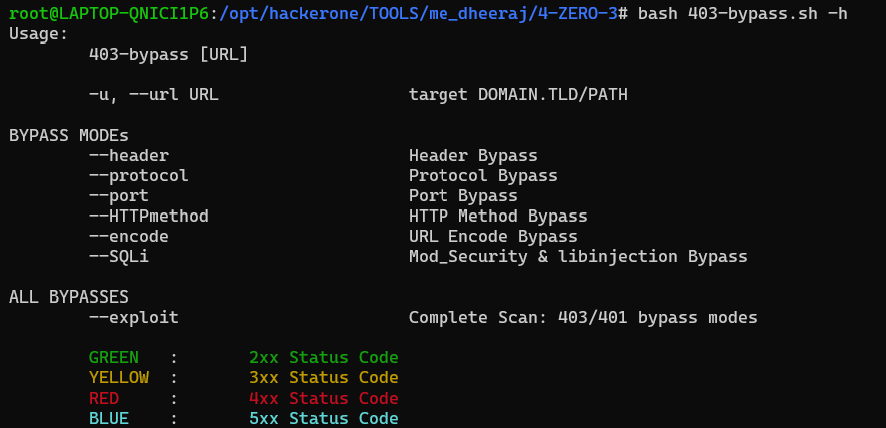
403/401 Bypass Methods + Bash Automation + Your Support ;)

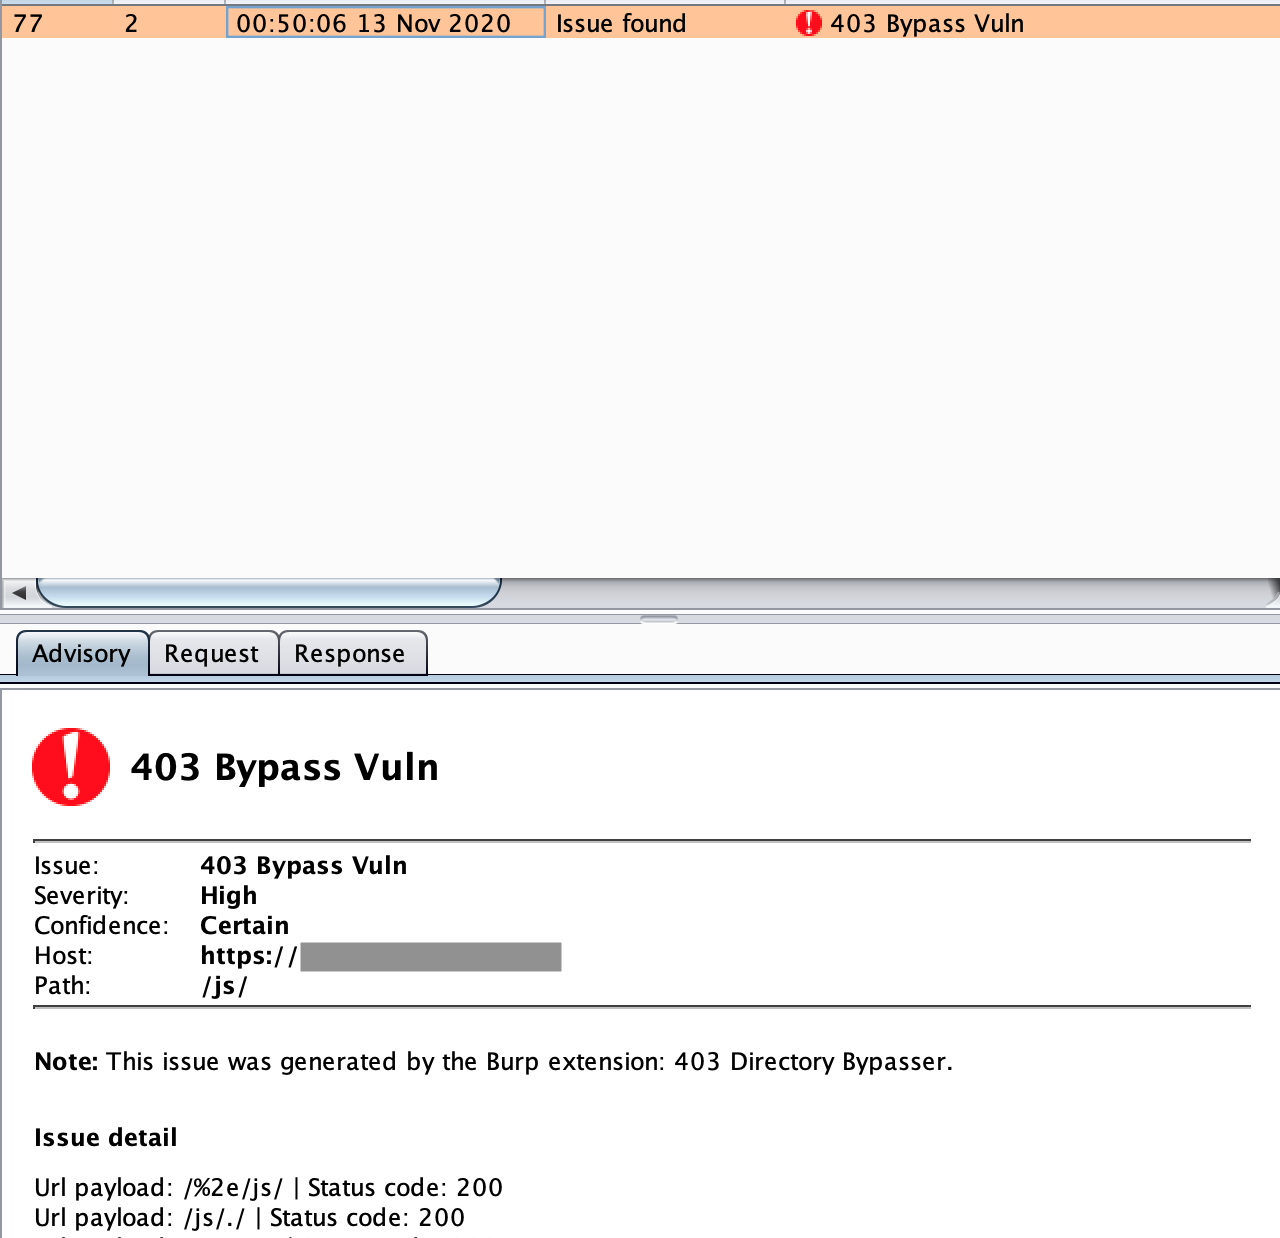
Burpsuite Extension to bypass 403 restricted directory

🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…

Burp Plugin to Bypass WAFs through the insertion of Junk Data

A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.