

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
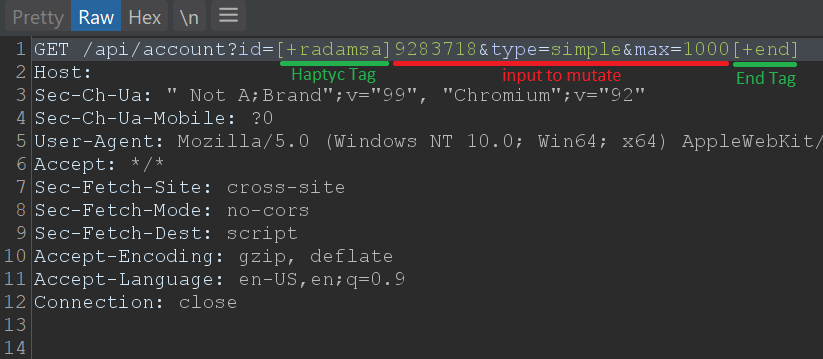 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
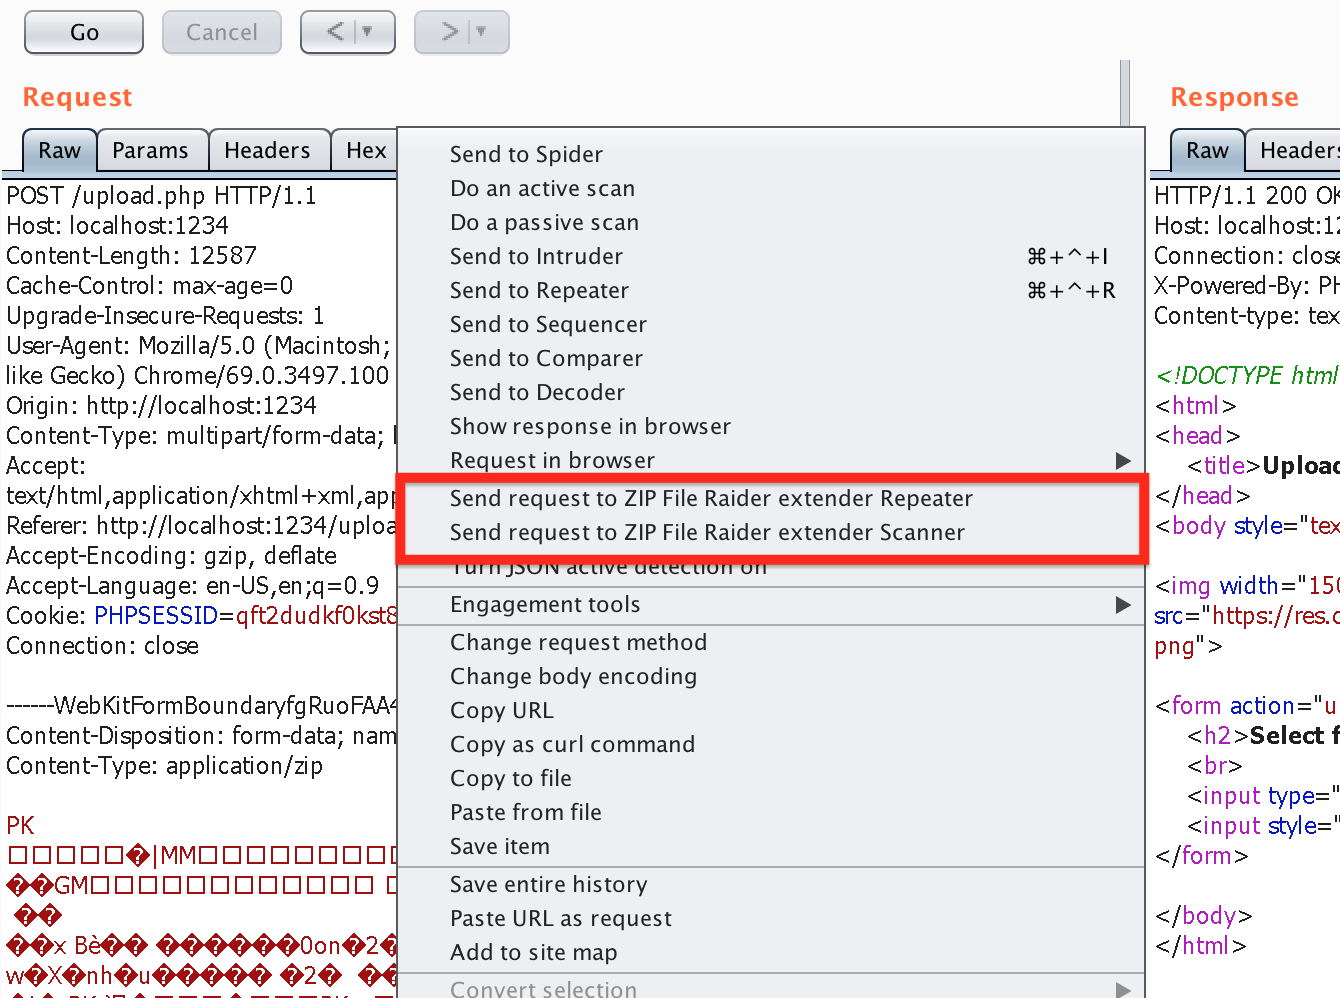 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 malwaretech/exifsmugglingpoc
A Proof-of-Concept using Cache Smuggling + Exif data to passively download a second stage payload
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 jptr218/ghostcat
Exploit tool for Apache Tomcat CVE-2020-1938 LFI vulnerability, enabling sensitive file reading and remote JSP payload execution via AJP connector.
 0xricksanchez/cve-2021-29447
A XXE payload generator
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
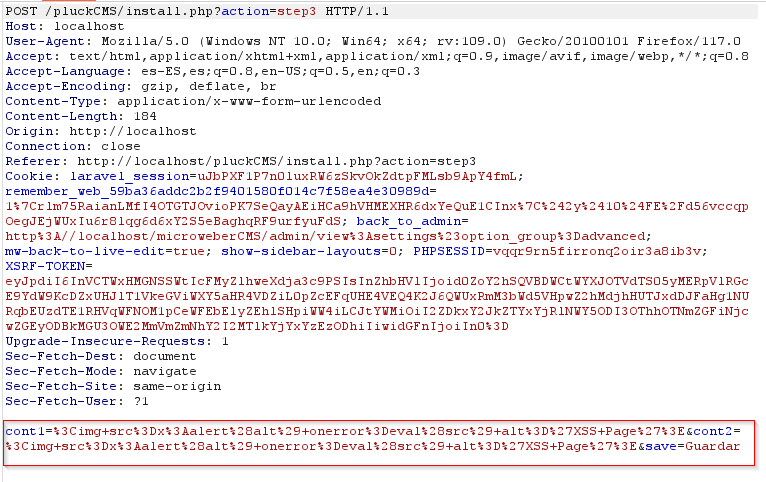 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
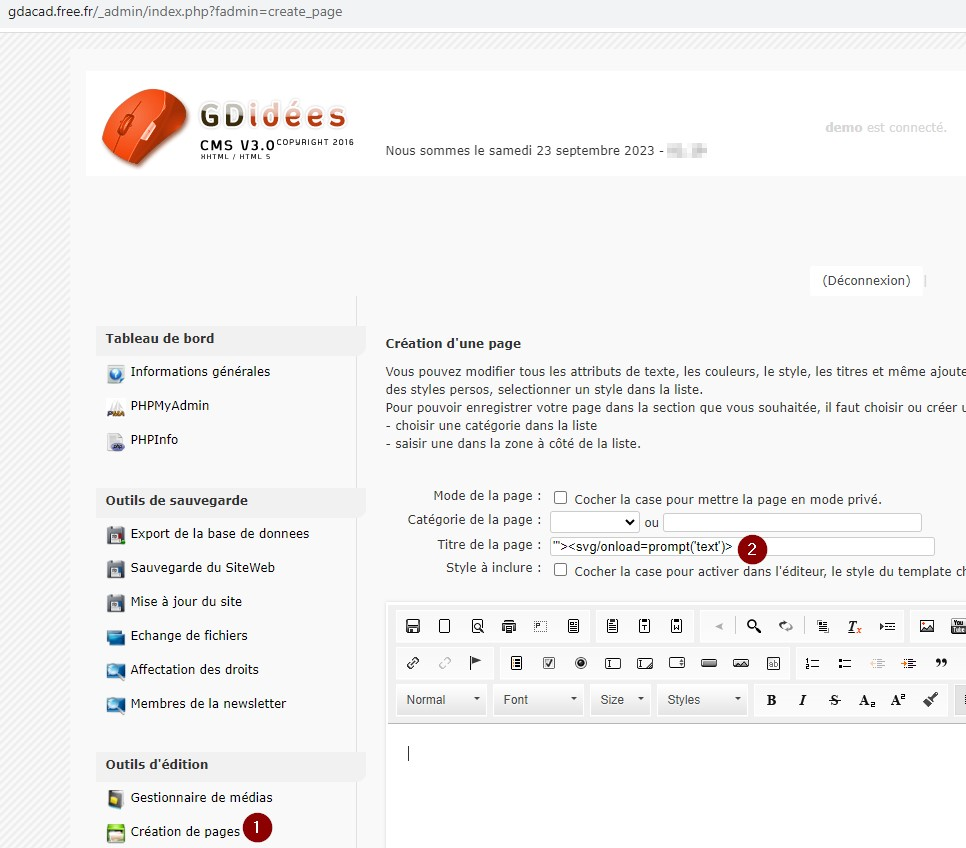 sromanhu/cve-2023-44758_gdidees-cms-stored-xss---title
GDidees CMS 3.9.2 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to…