Search-log4Jvuln-AppScanSTD

This Pwsh script run AppScan Standard scans against a list of web sites (URLs.txt) checking for Log4J (CVE-2021-44228) vulnerability

This Pwsh script run AppScan Standard scans against a list of web sites (URLs.txt) checking for Log4J (CVE-2021-44228) vulnerability

Proof-of-concept exploit for CVE-2025-54309, demonstrating an authentication bypass via race condition in CrushFTP WebInterface to enumerate users.

Time-based blind SQL injection detection tool for recon and bug bounty. Accepts single URLs or lists, supports custom headers, proxy, and POST data…

SimplCommerce is affected by a Broken Access Control vulnerability in the review system, allowing unauthorized users to post reviews for products…

Proof-of-concept for CVE-2024-43416 demonstrating GLPI user enumeration via crafted login requests to expose valid usernames.

Proof-of-concept exploit script for CVE-2024-24919 that scans target URLs via HTTP POST requests, analyzes responses for unauthorized access or data…

Proof-of-concept exploit for CVE-2022-39841 demonstrating plaintext credential leakage via unauthenticated WebSocket in Medusa. Includes blog post…

Brute-force tool for discovering hidden GET and POST parameters in web applications, supporting custom wordlists and concurrent requests.

Proof of concept for CVE-2022-22629, a heap buffer overflow in Safari's WebGL multi-draw extension, with vulnerability analysis and crash…

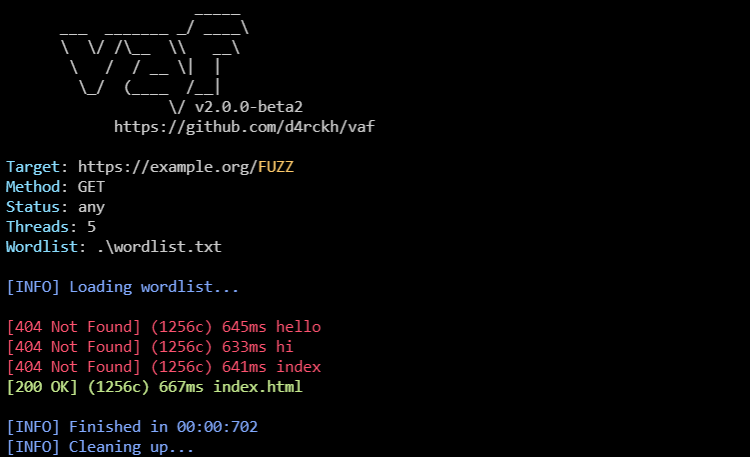
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…

Smart ssrf scanner using different methods like parameter brute forcing in post and get...

Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…

Cross-site Scripting (XSS) in blog-post creation functionality in Amasty Blog Pro for Magento 2

Stored Cross-site Scripting (XSS) in blog-post creation functionality in Amasty Blog Pro for Magento 2

Proof-of-concept for CVE-2026-40864: JupyterHub XSRF bypass via cross-origin form POST exploiting Sec-Fetch-Mode: no-cors. Includes PoC HTML, root…

A Powerful Sensor Tool to discover login panels, and POST Form SQLi Scanning

Time-based SQL injection detection template for SMM Panel targeting the service_detail parameter via crafted POST requests to /ajax_data, using…

a PoC for CVE-2024-0509/WP Plugin - WP 404 Auto Redirect to Similar Post (<= 5.4.14)