
CVE-2020-8248
 mbadanoiu/cve-2020-8248
CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client
exploitationpenetration-testingprivilege-escalation+3
mbadanoiu/cve-2020-8248CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
 al1ex/cve-2020-9470
Wing FTP Server 6.2.5 - Privilege Escalation
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 sasqwatch/cve-2019-11477-poc
Proof-of-concept exploit for CVE-2019-11477, demonstrating a denial-of-service attack against Linux kernel TCP SACK panic via crafted netfilter…
 mahfuzreham/cpanel-cve-2026-41940
cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 homjxi0e/cve-2017-3078
Proof-of-concept exploit for CVE-2017-3078, a memory corruption vulnerability in Adobe Flash Player ATF module enabling arbitrary code execution on…
 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
 dinosn/cve-2026-42945-nginx32-lab
CVE-2026-42945 nginx 32-bit exploit lab ASLR enabled
 theexploiters/cve-2024-39123-exploit
Exploit For: CVE-2024-39123: Stored XSS in Calibre-web 0.6.21
 cyberqueenmeg/cve-2022-33082-exploit
Proof-of-concept exploit for CVE-2022-33082 causing denial of service in Open Policy Agent versions ≤0.41.0 via crafted input. Intended for…
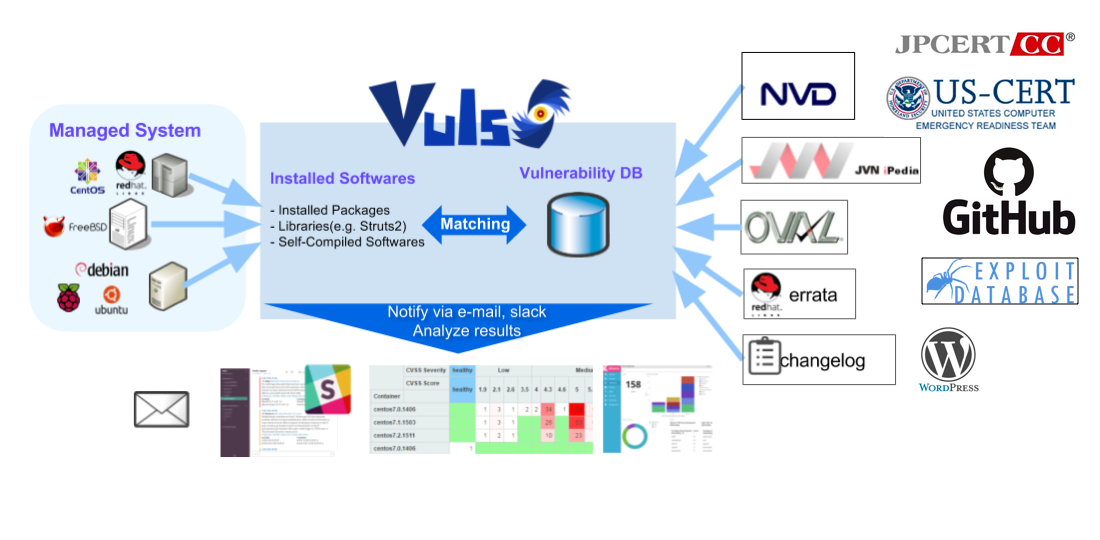 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
 rkx1209/cve-2014-1303
CVE-2014-1303 (WebKit Heap based BOF) proof of concept for Linux