
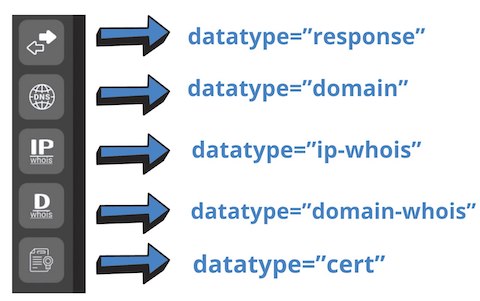
netlas-cookbook
 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
curated-resourcesdigital-forensicseducation+9
890
netlas-io/netlas-cookbookThe goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 dariusztytko/vhosts-sieve
Searching for virtual hosts among non-resolvable domains
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
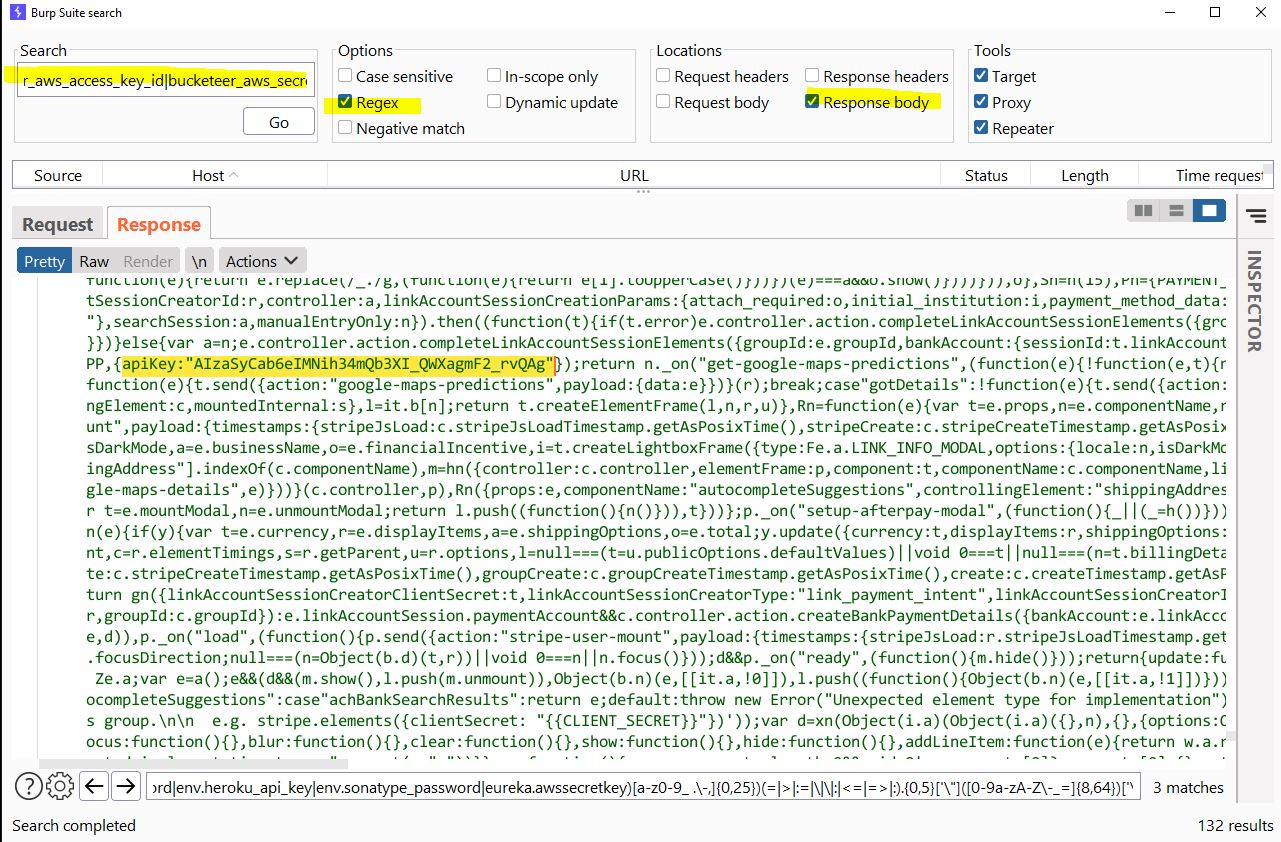 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
 janhalendk/react
A OSINT project that explores how to dump data from React
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 adityabhatt3010/cve-2025-10585-the-chrome-v8-zero-day
Google patched CVE-2025-10585, a Chrome V8 zero-day under active exploitation — here’s what it is, why it matters, and how to stay safe.
 becodoexploit-mrcat/sapgatebreaker-exploit
SAPGateBreaker is a PoC exploit for CVE-2022-22536, a critical HTTP Request Smuggling vulnerability in SAP NetWeaver. It demonstrates how to bypass…
 fourcube/nextjs-middleware-bypass-demo
Demonstrates a middleware bypass vulnerability (CVE-2025-29927) in Next.js, showing how to exploit the x-middleware-subrequest header to access…
 shaunmclernon/ghostcat-verification
Learnings on how to verify if vulnerable to Ghostcat (aka CVE-2020-1938)
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 chilit-nl/log4shell-example
The goal of this project is to demonstrate the log4j cve-2021-44228 exploit vulnerability in a spring-boot setup, and to show how to fix it.
 v1n1v131r4/csrf-to-rce-on-backdrop-cms
Proof-of-concept exploit for CSRF to RCE in Backdrop CMS 1.20 (CVE-2021-45268) using malicious plugin upload.
 itsshotgun/chrome_v8_cve_checker
Checks if your Chrome version is vulnerable to CVE-2025-5419, from the browser
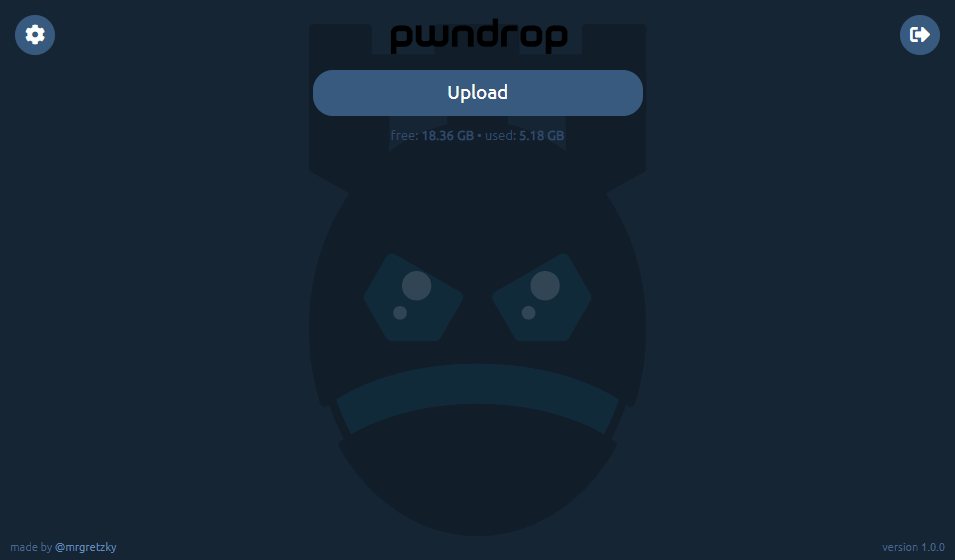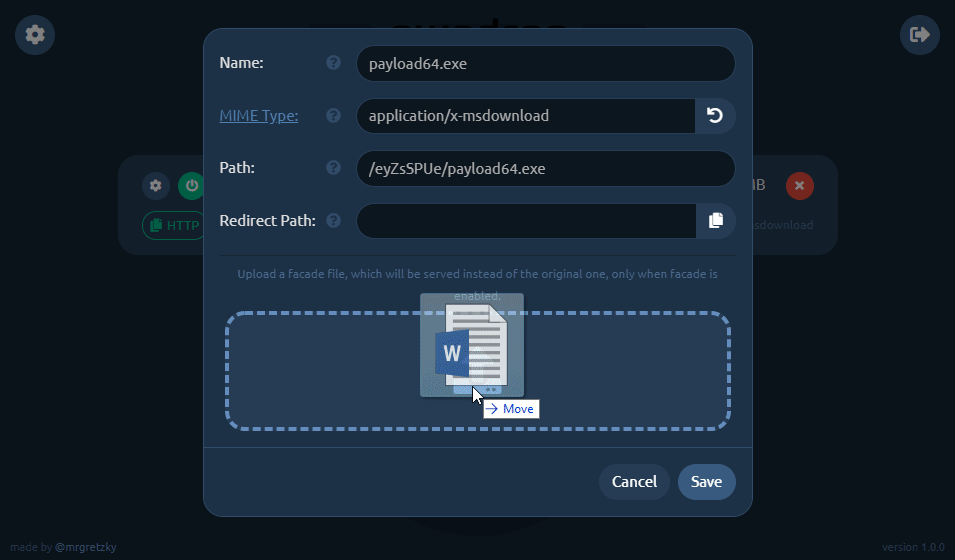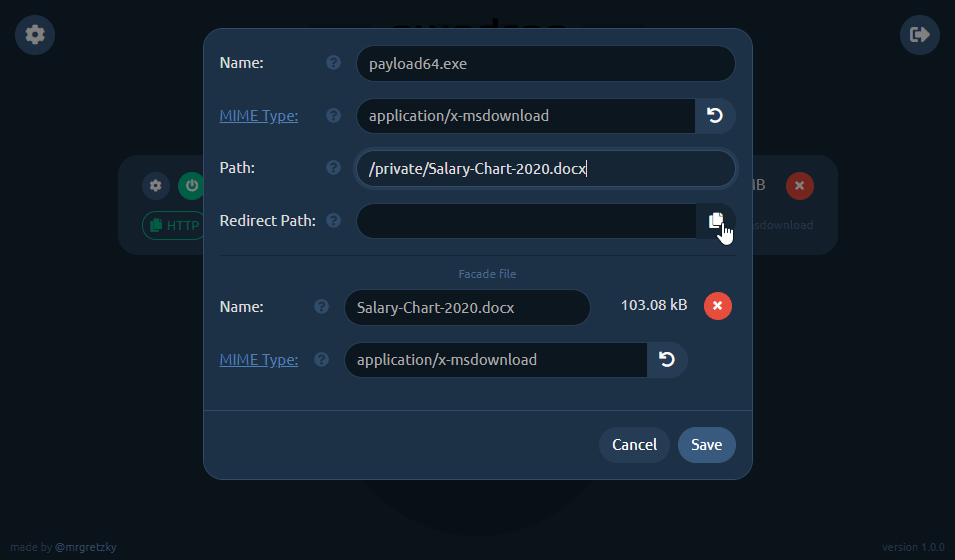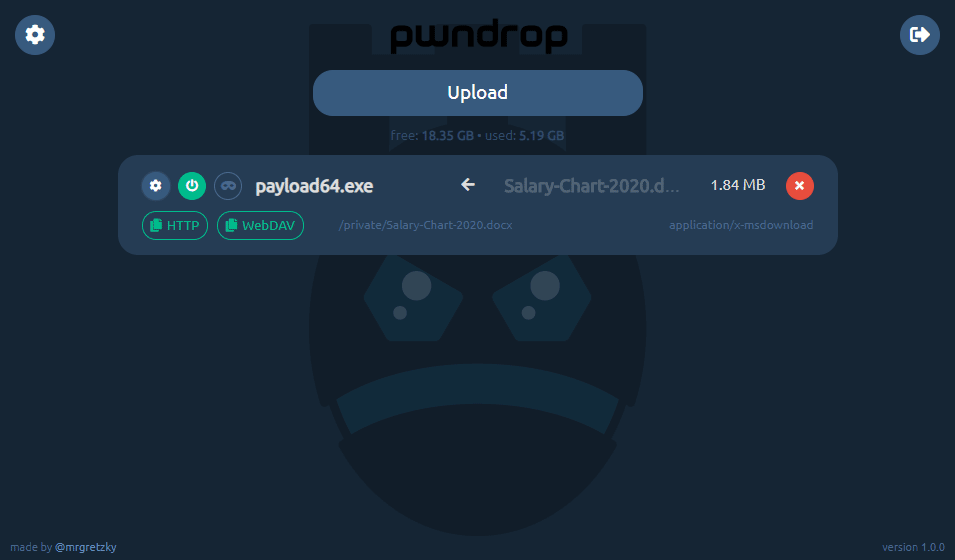 kgretzky/pwndrop
Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter