

git-dump
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
information-gatheringmisconfigurationpenetration-testing+3
1
jenderal92/git-dumpThis script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
 hashview/hashview
A web front-end for password cracking and analytics
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 tw1sm/spraycharles
Low and slow password spraying tool, designed to spray on an interval over a long period of time
 rosemary1337/cve-2025-24799
Exploits GLPI CVE-2025-24799 via unauthenticated time-based blind SQL injection to extract usernames and password hashes from glpi_users for…
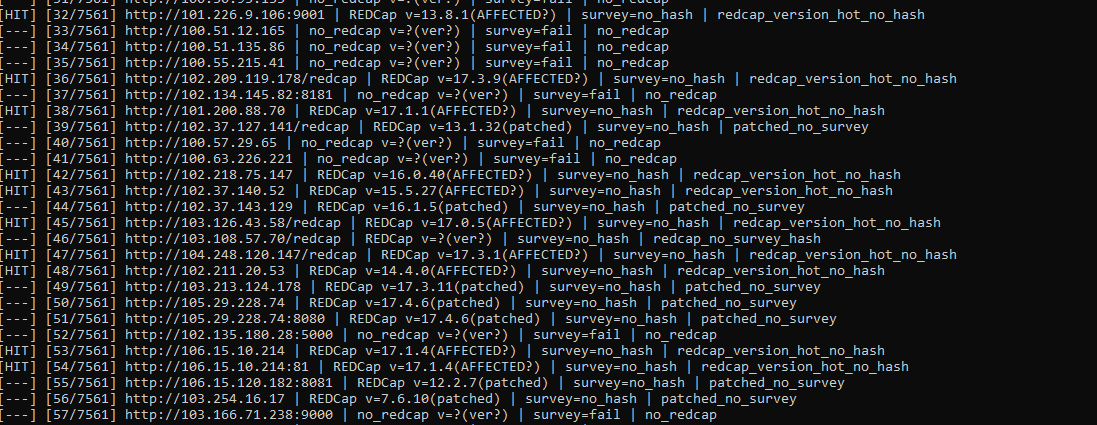 yulisec/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…
 farih123/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
 nbs-system/php-malware-finder
YARA-based scanner that detects obfuscated PHP malware and webshells using semantic pattern matching instead of file hashes, with a whitelist system…
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.