gitlab-cve-2026-85706-ioc

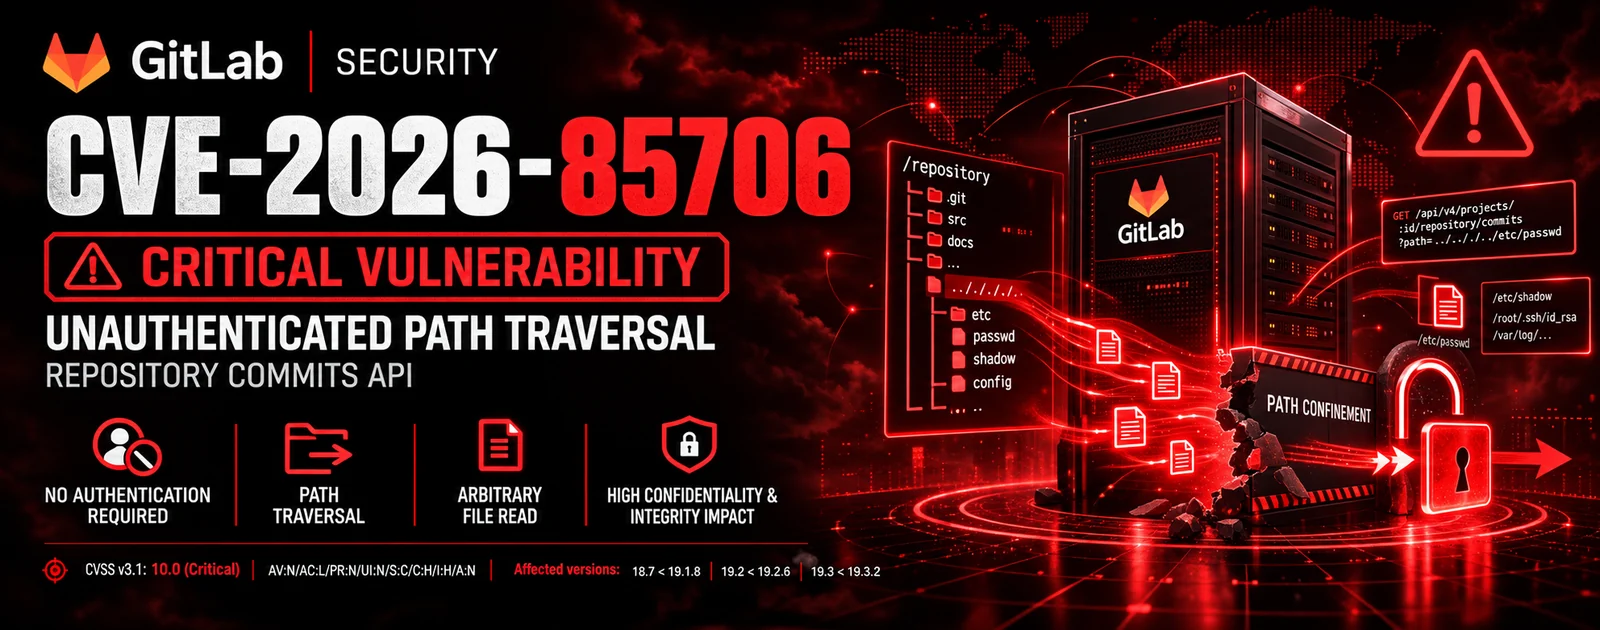
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

Find open databases - Powered by Binaryedge.io

Reproducible A/B lab + safe PoC for GitLab CVE-2026-19478 / CVE-2026-19650 (GraphQL @gl_introduced)

Proof-of-concept exploit for GitLab stored XSS (CVE-2022-1175) enabling personal access token theft and account takeover via malicious issue comments.

Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…

Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…

PoC for CVE-2026-85706: GitLab CE/EE unauthenticated arbitrary local file read

Reproducible lab for CVE-2026-10053 (GitLab npm package-registry path traversal -> arbitrary file write as git). Vulnerable 19.2.1 vs patched 19.2.2,…

NSE script to fingerprint if GitLab is vulnerable to cve-2021-22205-nse

Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.

Nmap NSE to check for CVE-2023-5612

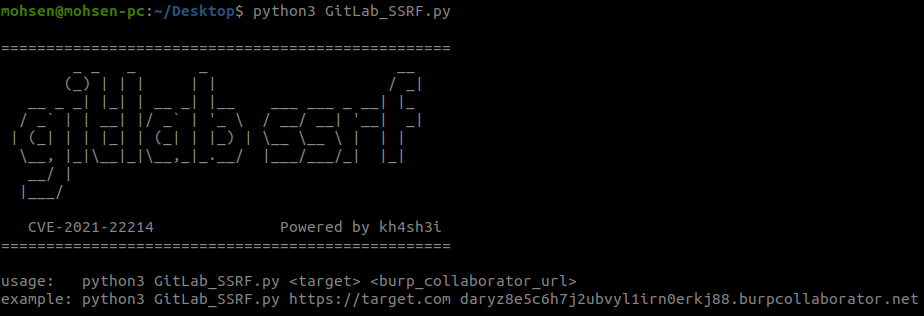
Proof-of-concept exploit for CVE-2021-22214, a server-side request forgery in GitLab webhooks, allowing unauthenticated attackers to make internal…

Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…

Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…

Go exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE Workhorse via URL-encoding bypass, with concurrent requests and…

Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…

Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…