
CVE-2022-21907
 zz-socmap/cve-2022-21907
HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907
exploitationpayload-developmentpenetration-testing+3
360
zz-socmap/cve-2022-21907HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907
 malwareman007/cve-2022-21907
POC for CVE-2022-21907: HTTP Protocol Stack Remote Code Execution Vulnerability.
 michelep/cve-2022-21907-vulnerability-poc
CVE-2022-21907 Vulnerability PoC
 vonahisec/cve-2022-47966-scan
Python scanner for CVE-2022-47966. Supports ~10 of the 24 affected products.
 becrevex/cve-2022-24706
Apache CouchDB 3.2.1 - Remote Code Execution (RCE) Checker
 gpiechnik2/nmap-cve-2022-21907
Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…
 irgoncalves/irule-cve-2022-22965
F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…
 p0dalirius/cve-2022-30780-lighttpd-denial-of-service
CVE-2022-30780 - lighttpd remote denial of service
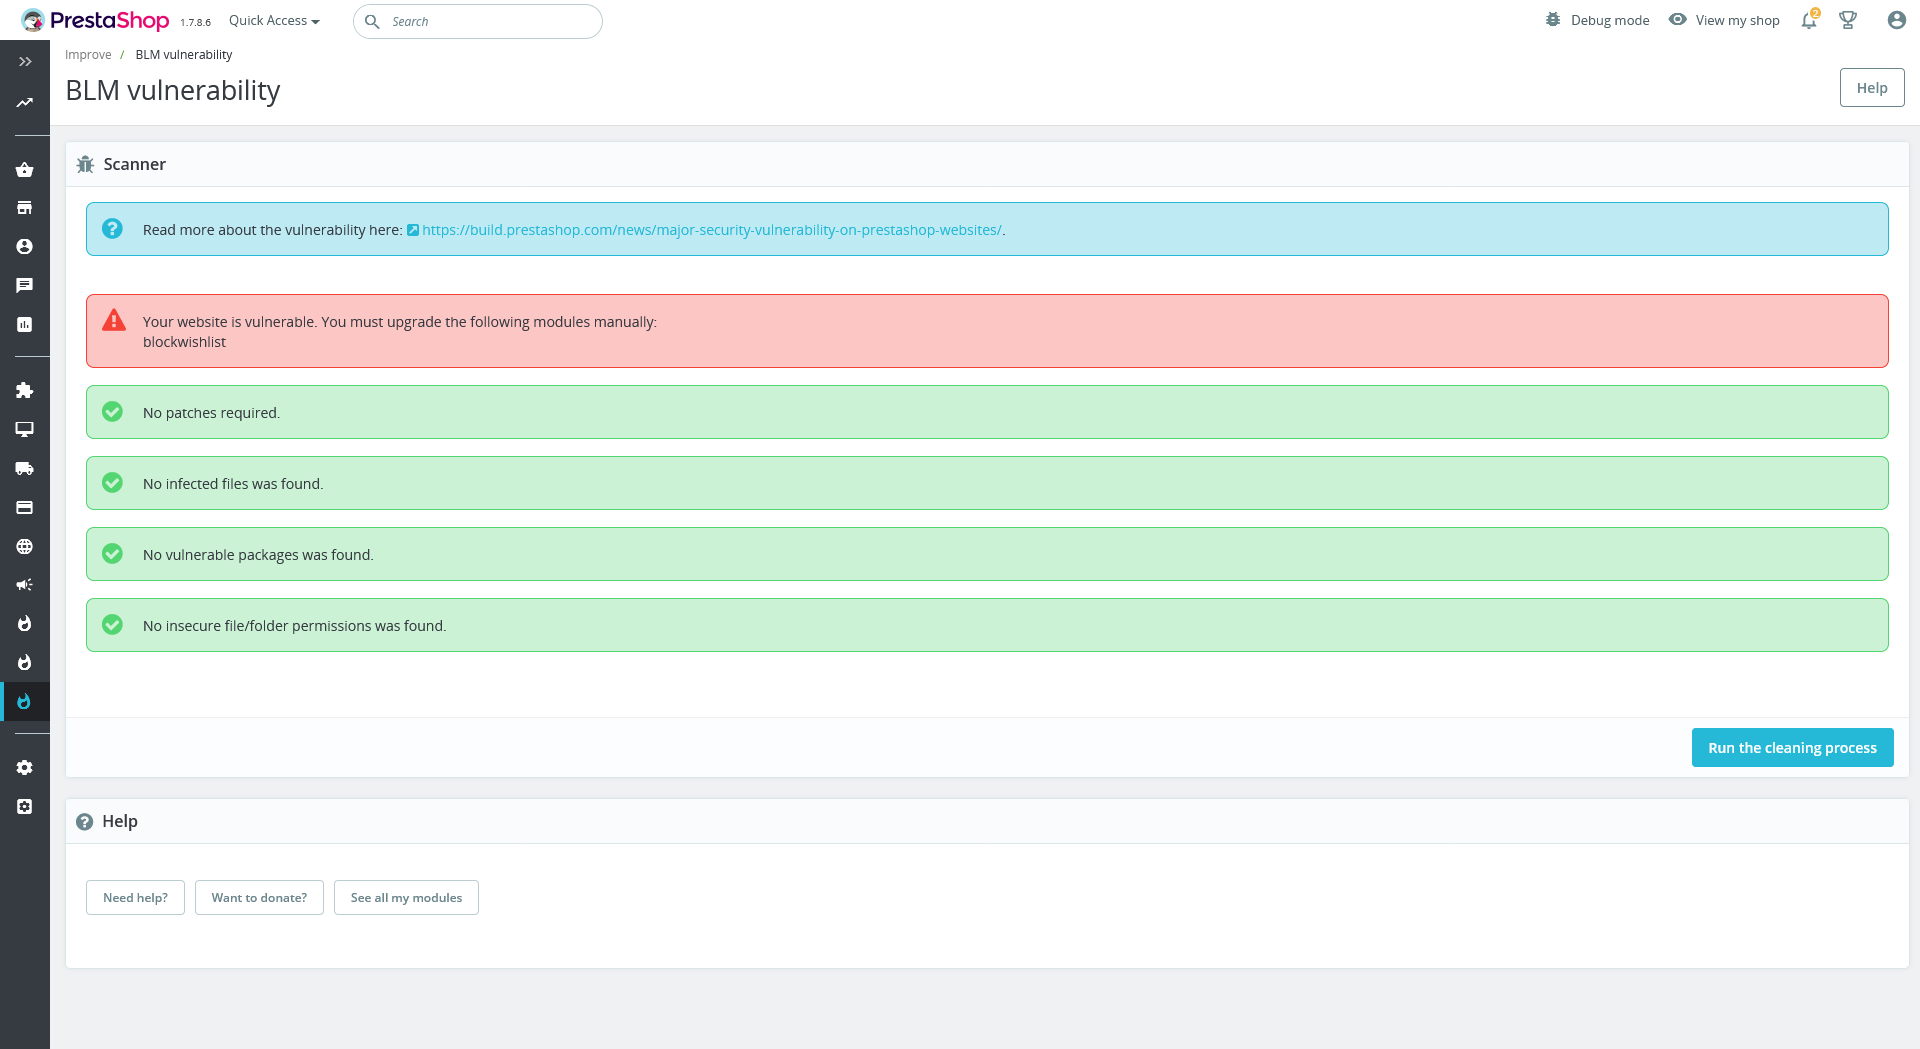 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
 meng-security/spring4shell-local-verification-lab
Spring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
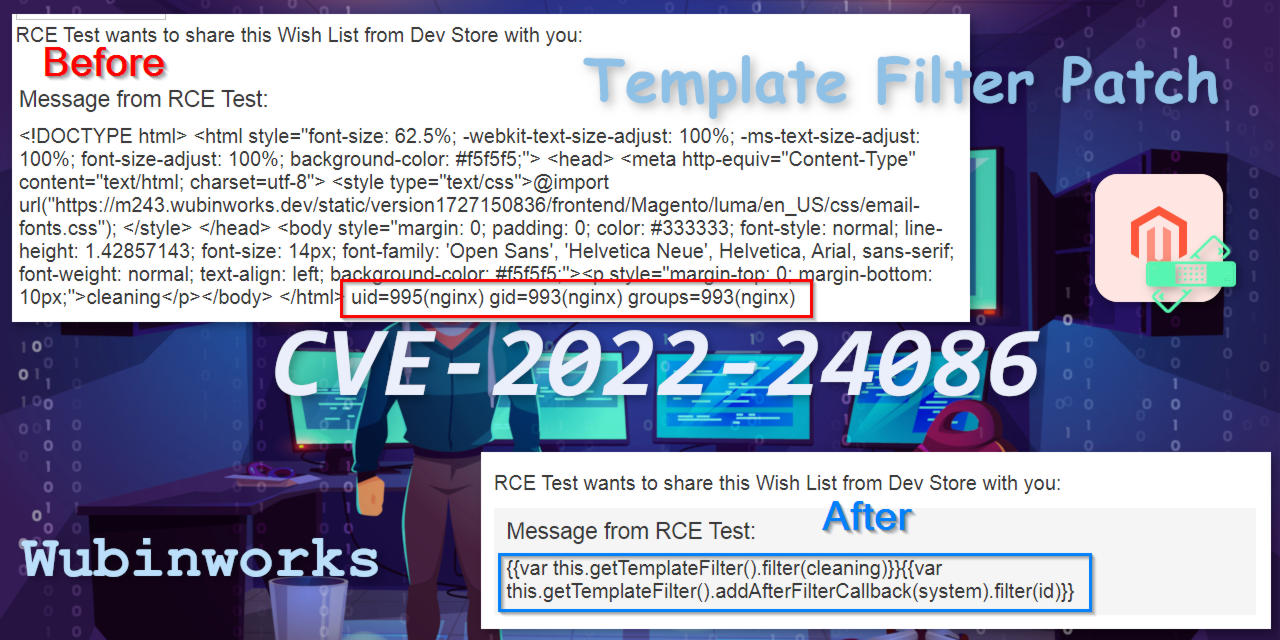 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 coana-tech/cve-2022-0155-poc
Proof-of-concept demonstrating CVE-2022-0155 cookie theft via HTTP redirect in follow-redirects npm package, including Express server and client…
 simonepetruzzi/websecurityproject
Analysis and replication of CVE-2022-23988 and CVE-2022-34265
 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 user0x1337/cve-2022-39227
CVE-2022-39227 : Proof of Concept
 neverendingsupport/angularjs-poc-cve-2022-25869
A minimal reproduction of an AngularJS <textarea> XSS vulnerability on IE (tracked as CVE-2022-25869).