
CVE-2019-9053
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
11
4nner/cve-2019-9053Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 halencarjunior/dlkploit600
Simple Python script for D-Link vulnerability scan and test [CVE-2019-13101]
 brianwrf/cve-2019-6690
It is a simple PoC of Improper Input Validation in python-gnupg 0.4.3 (CVE-2019-6690).
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 jyothsna-git007/cms-made-simple-2.2.10---sql-injection
Google Dork-based scanner for detecting CVE-2019-9053 SQL injection in CMS Made Simple < 2.2.10. Designed for security auditing and patch…
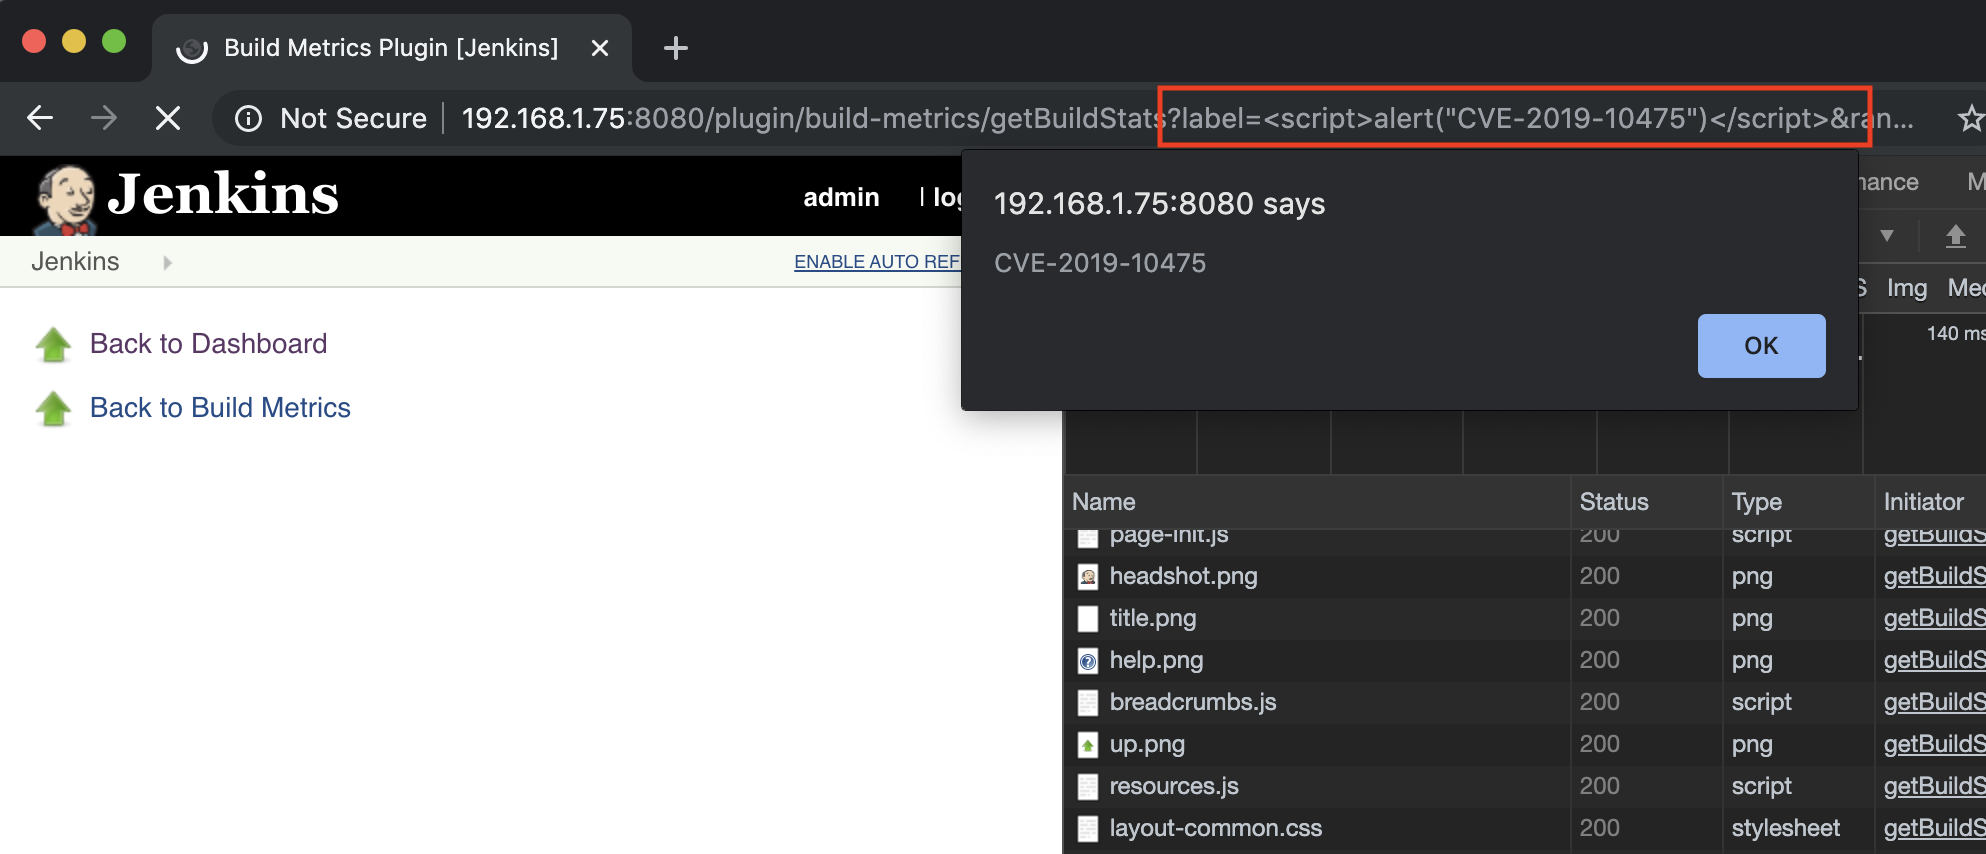 vesche/cve-2019-10475
Reflected XSS proof-of-concept exploit for Jenkins build-metrics plugin CVE-2019-10475, with a Python weaponization script for generating malicious…
 davidfortytwo/bluekeep
Python-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…
 0xsharz/telerik-scanner-cve-2019-18935
Telerik CVE-2019-18935 Vulnerability Scanner
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 cisagov/check-cve-2019-19781
Test a host for susceptibility to CVE-2019-19781
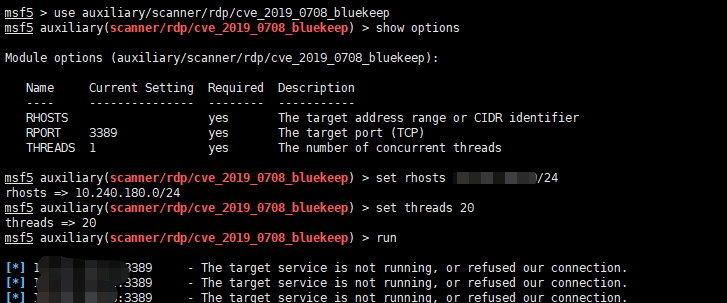 pa55w0rd/cve-2019-0708
CVE-2019-0708批量检测
 autocode07/cisagov__check-cve-2019-19781.4142e02b
Command-line utility to check if a host is vulnerable to CVE-2019-19781 (Citrix ADC/NetScaler). Scans a single host and reports vulnerability status…
 r0lh/cve-2019-8449
User Enumeration Proof Of Concept Exploit for CVE-2019-8449
 mufeedvh/cve-2019-8449
CVE-2019-8449 Exploit for Jira v2.1 - v8.3.4
 ianxtianxt/cve-2019-16279
Shell script exploit for CVE-2019-16279 that triggers a denial-of-service via memory corruption by sending excessive CRLF sequences to an HTTP server.
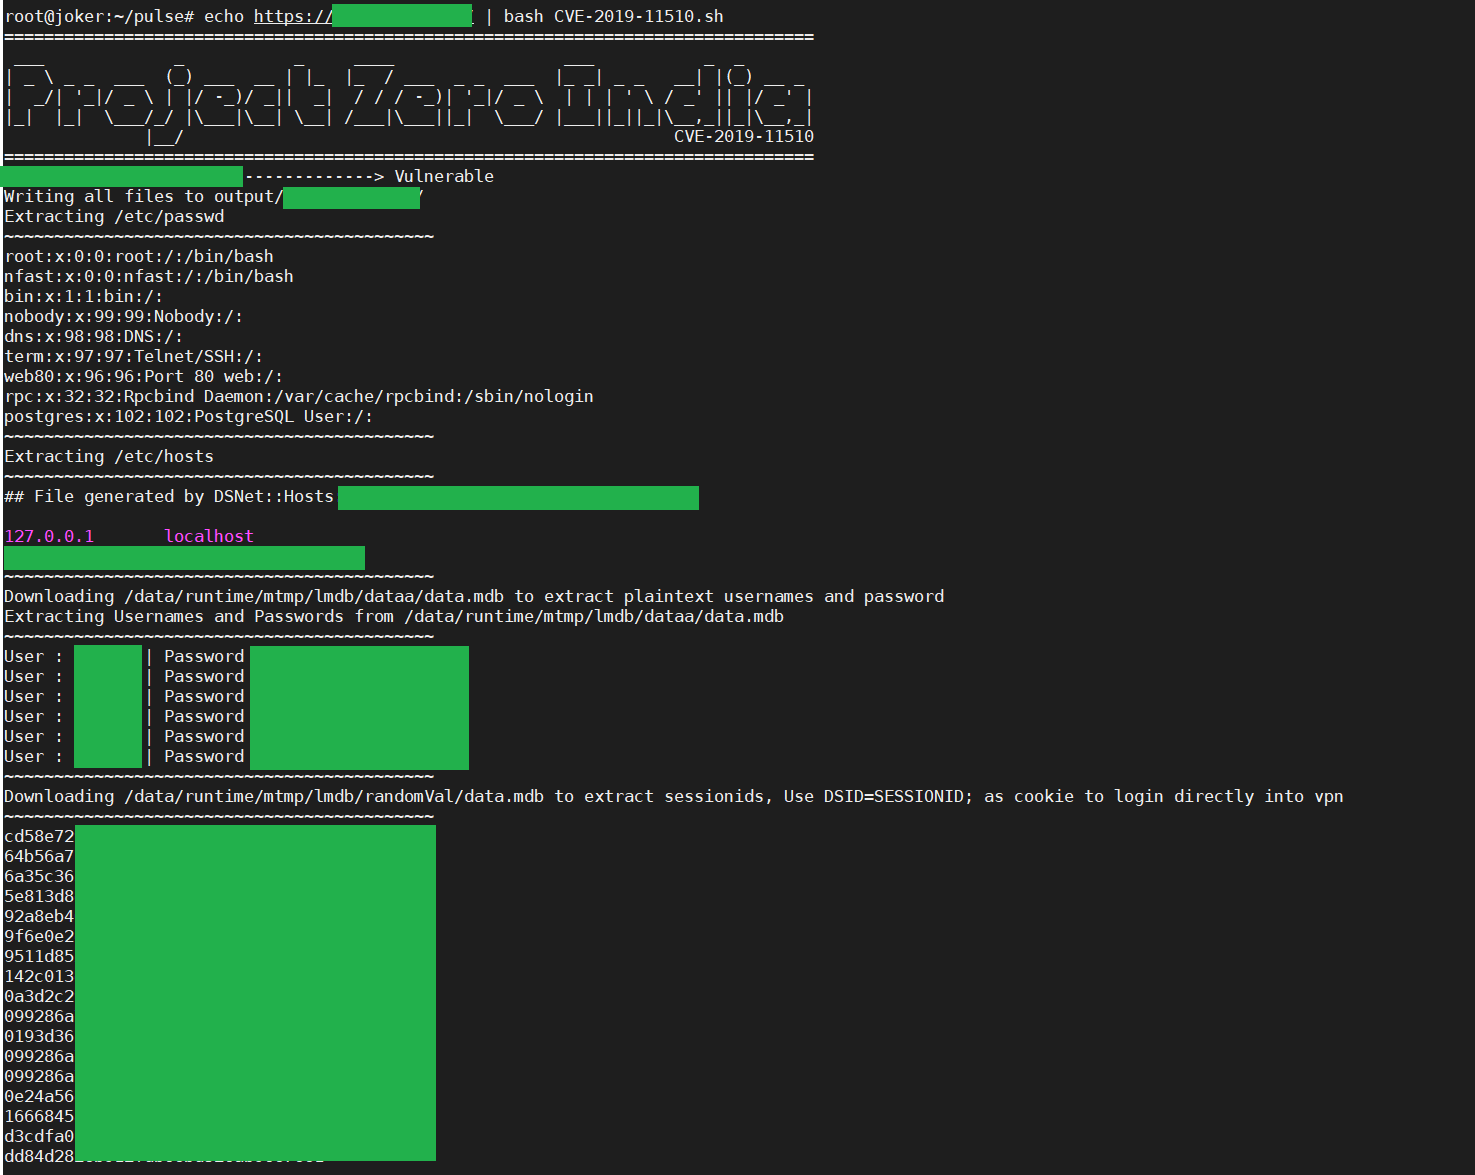 projectzeroindia/cve-2019-11510
Exploit for Arbitrary File Read on Pulse Secure SSL VPN (CVE-2019-11510)
 random-robbie/cve-2019-7616
POC for CVE-2019-7616 / ESA-2019-09
 eliushhimel/citrix-honeypot
Citrix ADC (NetScaler) Honeypot. Supports detection for CVE-2019-19781 and login attempts