PAN-OS-CVE-2024-3400-Command-Injection-Investigation

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…

Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…

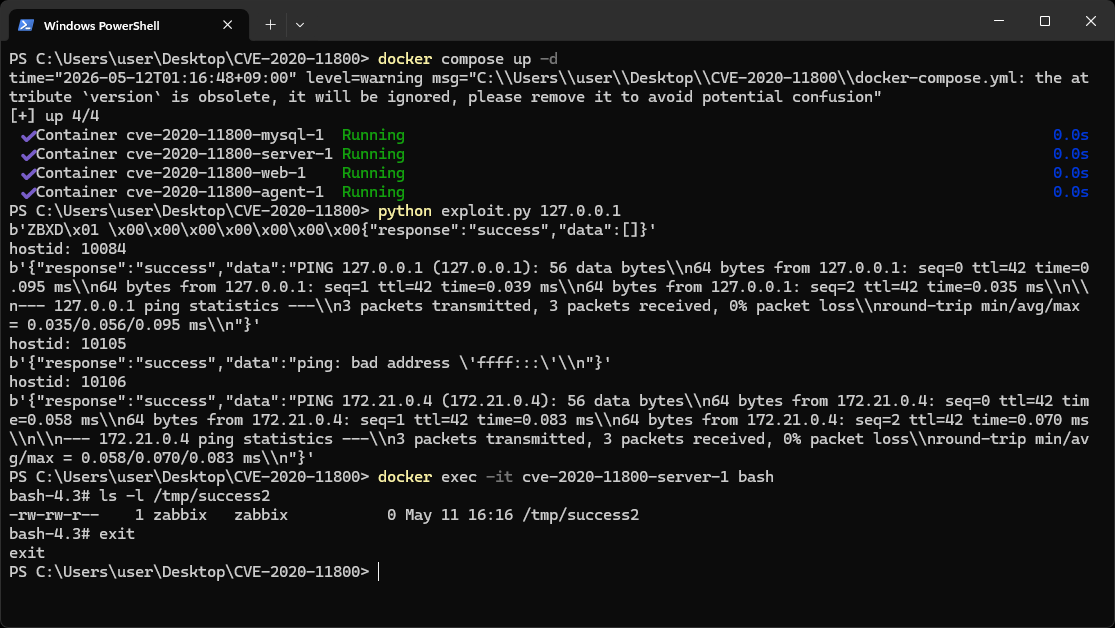
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…

Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…

Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…

Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…

Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…