
CVE-2025-63848
 codermohammed1/cve-2025-63848
CVE disclosure for stored cross-site scripting (XSS) in SWISH Prolog up to v2.2.0, enabling arbitrary code execution and account takeover via crafted…
curated-resourceseducationexploitation+2
codermohammed1/cve-2025-63848CVE disclosure for stored cross-site scripting (XSS) in SWISH Prolog up to v2.2.0, enabling arbitrary code execution and account takeover via crafted…
 aksalsalimi/cve-2026-26416
Detailed write-up of CVE-2026-26416, an authorization bypass vulnerability in TCS Cognix Recon Client v3.0 allowing privilege escalation via crafted…
 muthaiyanmani/react2shell-checker
A security vulnerability scanner for detecting the React2Shell vulnerability (CVE-2025-55182) in Next.js and React applications.
 olimpiofreitas/cve-2025-5349-scanner
Python-based scanner for CVE-2025-5349 that probes IP ranges and hosts on HTTP/HTTPS ports to detect vulnerable Citrix NetScaler instances.
 autocode07/cisagov__check-cve-2019-19781.4142e02b
Command-line utility to check if a host is vulnerable to CVE-2019-19781 (Citrix ADC/NetScaler). Scans a single host and reports vulnerability status…
 anilpatel199n/cve-2024-40898
This Python script checks for the presence of CVE-2024-40898, a critical vulnerability in Apache HTTP Server that may allow SSL/TLS certificate…
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
 tlekrean/cve-2025-65345
An authenticated Directory Traversal vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file manager…
 thegenetic/cve-2026-2964-lab
Educational lab demonstrating CVE-2026-2964, a prototype pollution vulnerability in web-audio-recorder-js leading to RCE. Includes vulnerable and…
 cves-labs/cve-2026-21876
Docker-based lab environment for reproducing and exploiting CVE-2026-1357, with step-by-step setup and Burp Suite exploitation guidance.
 abanop22333/apache-authentication-flaw-research-cve-2024-38476-
Technical research paper analyzing CVE-2024-38476, a critical Apache HTTP Server vulnerability enabling SSRF, information disclosure, and potential…
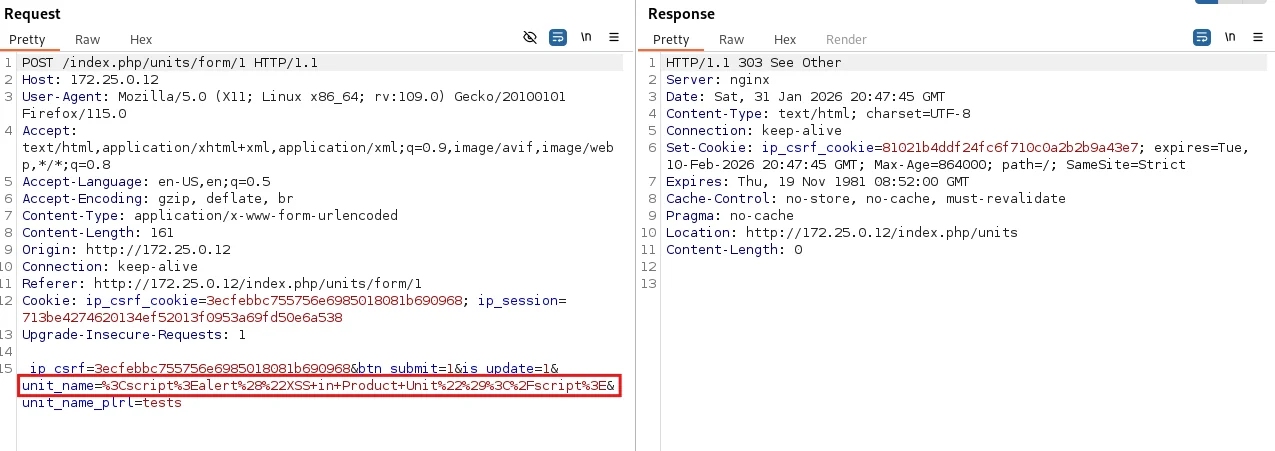 lagathos/cve-2026-25596
Proof-of-concept for a stored XSS vulnerability in InvoicePlane 1.7.0 via the product unit name field, including vulnerable code locations and…
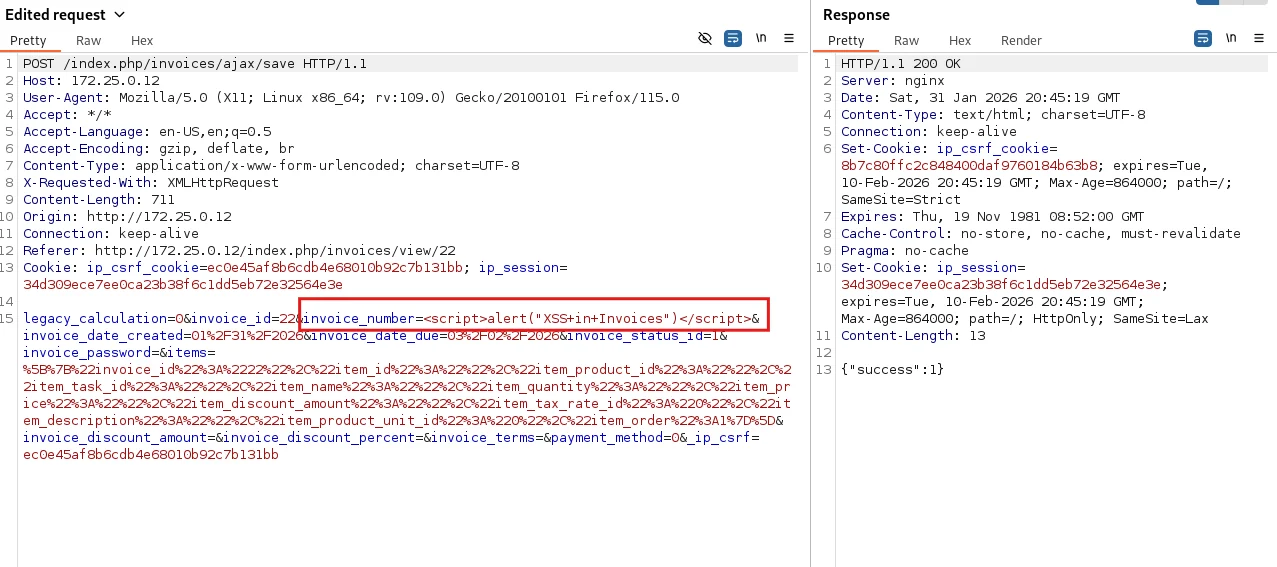 lagathos/cve-2026-25595
Stored XSS vulnerability in InvoicePlane 1.7.0 via unsanitized invoice number field, with proof-of-concept and remediation details.
 p3nt3st3r-star/majordomo-cve-2026-27179
Proof-of-concept and scanner for CVE-2026-27179, demonstrating vulnerability behavior in controlled environments for academic research and defensive…
 pierfrancescoconti/leaflet-cve-2025-69993
Proof-of-concept for CVE-2025-69993: Cross-Site Scripting in Leaflet's bindPopup() method. Includes advisory, impact analysis, and a demo Angular…
 m0d0ri205/wargame_re-ls
CTF challenge exploiting CVE-2025-0184 DOCX SSRF vulnerability to access internal admin service and retrieve a flag. Includes exploit generator and…
 kai-one001/react-router-cve-2025-61686-
Detailed analysis of CVE-2025-61686, a path traversal vulnerability in React Router's file session storage, including root cause, attack scenarios,…
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478