
CVE-2025-31651-o
 gregk4sec/cve-2025-31651-o
Proof-of-concept exploit for CVE-2025-31651, demonstrating bypass of security-enforcing rewrite rules via specially crafted requests in affected…
exploitationmisconfigurationpenetration-testing+3
2
gregk4sec/cve-2025-31651-oProof-of-concept exploit for CVE-2025-31651, demonstrating bypass of security-enforcing rewrite rules via specially crafted requests in affected…
 tahaxafous/cve-2023-44487-dos
PoC for CVE-2023-44487 ( HTTP/2 Rapid Reset Attack ) Concept
 amnsecurity/helm-plugin-path-traversal-security-assessment
Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…
 0xsojalsec/nuclei-templatesnuclei-templates-cve-2017-17736
Nuclei template for detecting CVE-2017-17736, a command injection vulnerability in ntopng, by sending crafted HTTP requests and matching response…
 faizzaidi/typo3-v7.6.15-unencrypted-login-request
Proof-of-concept exploit for TYPO3 v7.6.15 unencrypted login request vulnerability (CVE-2017-6370), demonstrating plaintext credential exposure over…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
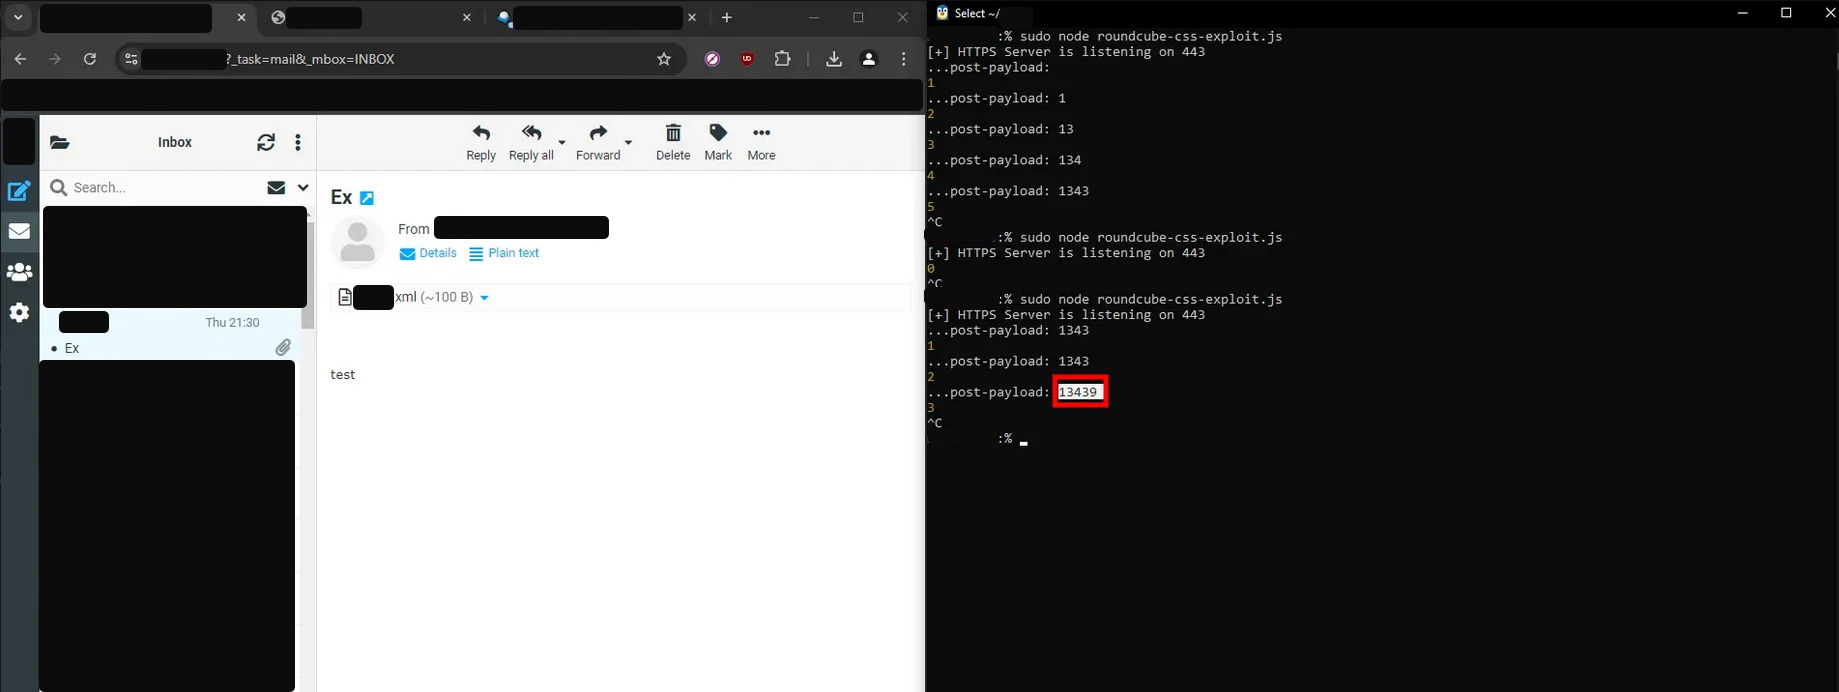 victoni/roundcube-cve-2024-42008-and-cve-2024-42010-poc
POC for Roundcube vulnerabilities CVE-2024-42008 and CVE-2024-42010
 dewankpant/cve-2017-16568
Proof-of-concept exploit for a persistent XSS vulnerability in Logitech Media Server 7.9.0, demonstrating HTML code injection via the Radio URL field.
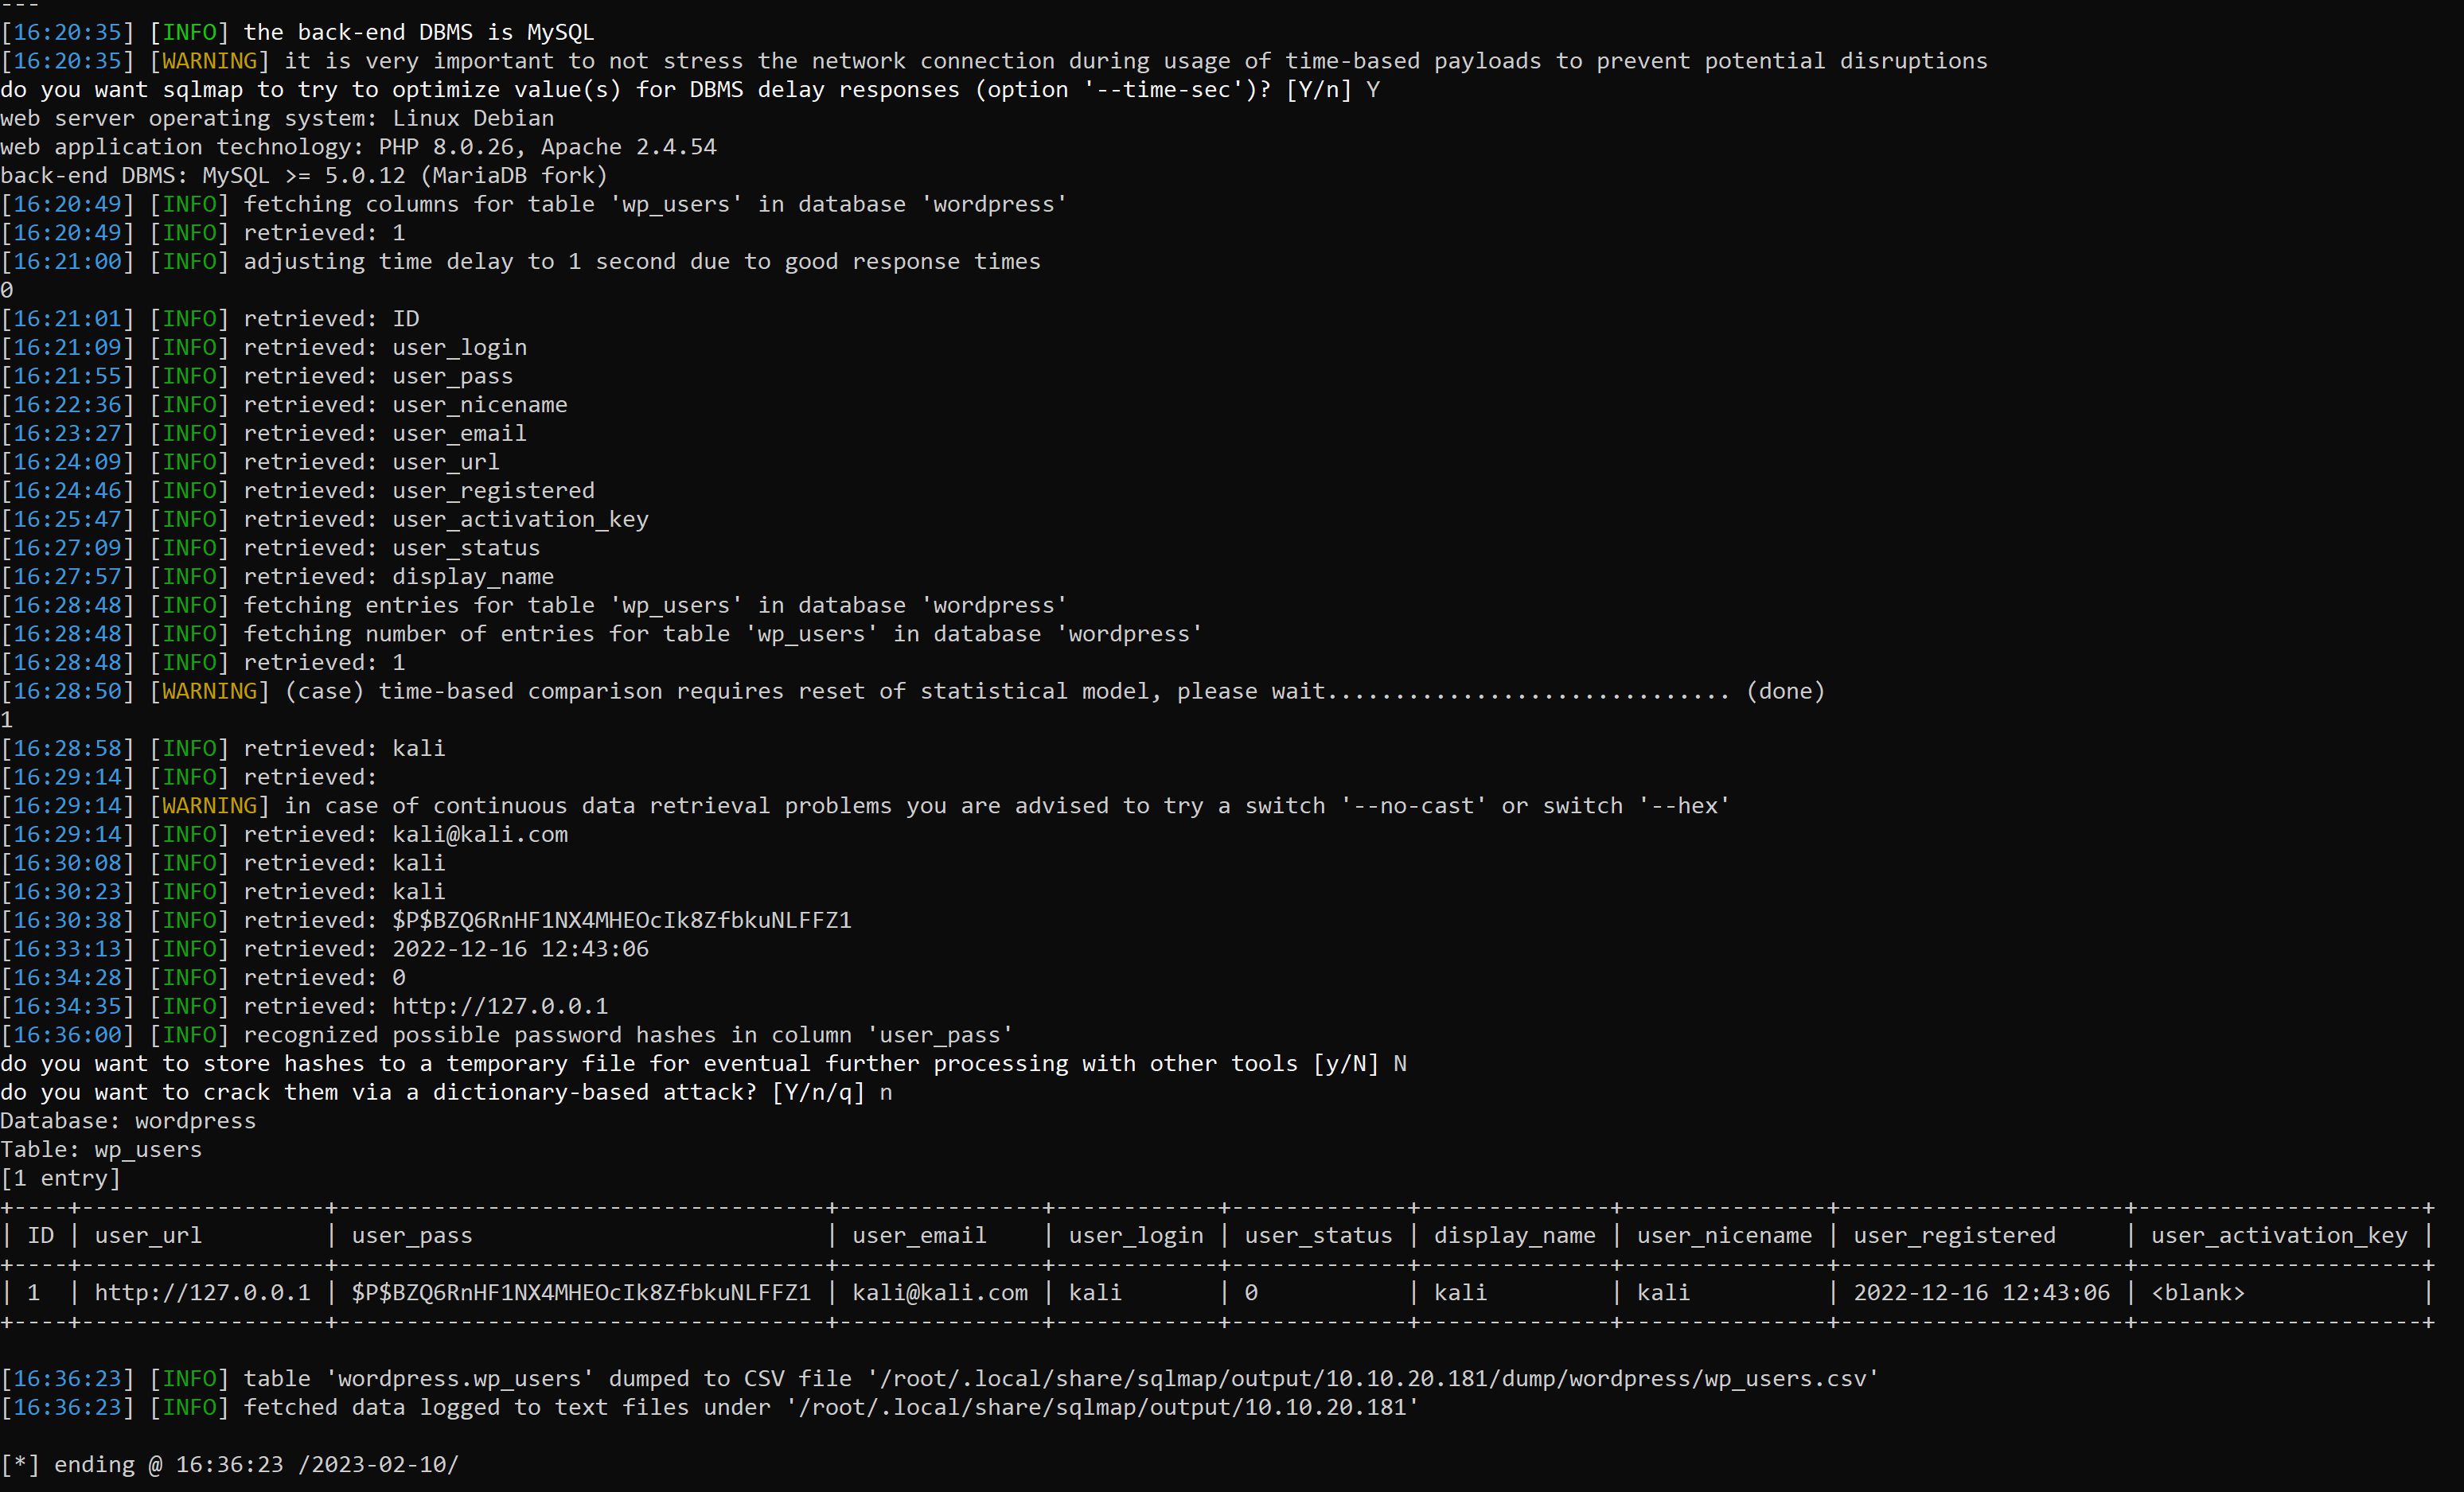 schmidalex/nex-forms_sql-injection-cve-2023-2114
Quick Review about the SQL-Injection in the NEX-Forms Plugin for WordPress
 iamdremig/cve-2026-14802
Compact CVE reference: OS command injection in create-react-app before 5.0.2 on macOS via react-dev-utils openBrowser.js, including affected versions…
 drone789/cve-2012-1823
Automated exploit for CVE-2012-1823, a PHP CGI remote code execution vulnerability. Provides a quick check script for vulnerable servers.
 becrevex/cve-2025-0108
NSE script that checks for CVE-2025-0108 vulnerability in Palo Alto Networks PAN-OS
 cmaruti/reports
Curated vulnerability disclosure reports with CVE mappings, covering SQLi, XSS, authentication bypass, and DoS in web applications and network…
 drackyjr/cve-2025-9784
Bash script to test for CVE-2025-9784 HTTP/2 DoS vulnerability in Undertow servers. Measures baseline response times, simulates rapid stream resets,…
 mister-joe/cve-2021-44593
Public disclosure and writeup of CVE-2021-44593, an unauthenticated SQL injection in Simple College Website leading to arbitrary file upload and…
 abian2/cve-2024-23652
Proof-of-concept exploit for CVE-2024-23652, demonstrating the vulnerability and its impact.
 drugeddon/drupal-exploit
Python exploit script for CVE-2018-7600 (Drupalgeddon2) targeting Drupal 7 <= 7.57 via password reset form poisoning and file upload trigger.
 imbas007/cve-2025-49844-vulnerability-scanner
Scans Redis instances for CVE-2025-49844 (RediShell) critical RCE vulnerability, detecting vulnerable versions and Lua scripting status with…