
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
6080 results
drupal-check preview

drupal-check

GitHubhestat/drupal-check

Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
forensicsincident-responselog-analysis+2
28 years ago
motionEye-RCE-through-config-parameter preview

motionEye-RCE-through-config-parameter

GitHubprabhatverma47/motioneye-rce-through-config-parameter

PoC steps for this vulnerability
exploitationpenetration-testingred-teaming+3
21 year ago
nginx-cve-2026-42945 preview

nginx-cve-2026-42945

GitHubtal7aouy/nginx-cve-2026-42945

🛡️ Script to test for NGINX CVE-2026-42945
configuration-auditingdefensive-toolsdevsecops+3
24 months ago
CVE-2026-5027 preview

CVE-2026-5027

GitHubyym8538/cve-2026-5027

Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…
exploitationpenetration-testingremote-access-tool+3
11 month ago
CVE-2026-15718-who-put-ptrs-in-my-wasm preview

CVE-2026-15718-who-put-ptrs-in-my-wasm

GitHubsneakynachos/cve-2026-15718-who-put-ptrs-in-my-wasm

PoC exploit chain for CVE-2026-15718: SpiderMonkey wasm baseline compiler array.fill missing-sync -> invalid pointer -> addrOf/fakeobj -> arbitrary…
binary-exploitationexploitationpayload-development+3
11 month ago
CVE-2026-49975 preview

CVE-2026-49975

GitHubyym8538/cve-2026-49975

Proof-of-concept HTTP/2 Bomb exploit for CVE-2026-49975, a cookie-header memory exhaustion DoS in Apache HTTP Server 2.4.17-2.4.67, with Docker lab…
exploitationnetwork-securityred-teaming+2
11 month ago
check-cve-2026-3055-netscaler preview

check-cve-2026-3055-netscaler

GitHubl0lsec/check-cve-2026-3055-netscaler

Low-impact probe for Citrix NetScaler CVE-2026-3055 (SAML IdP memory overread)
exploitationnetwork-securityvulnerability-scanners+1
11 month ago
Wordpress_cve-2019-9787_defense preview

Wordpress_cve-2019-9787_defense

GitHubsijiahi/wordpress_cve-2019-9787_defense

This is a recurrence of cve-2019-9787 on Wordpress and a hash-based defense.
exploitationpenetration-testingvulnerability-analysis+2
35 years ago
POC-CVE-2026-19295 preview

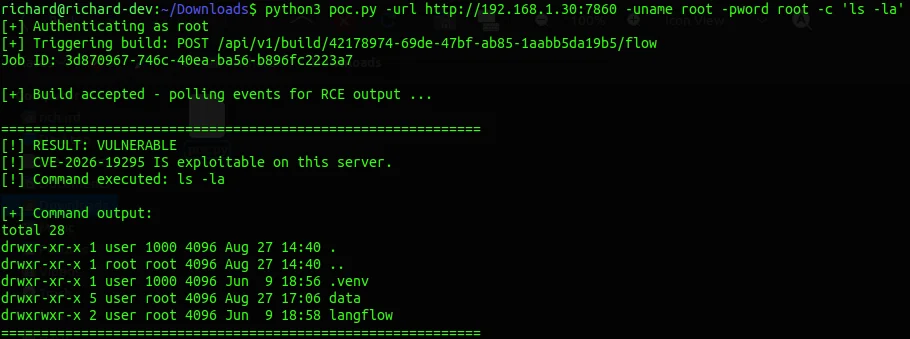
POC-CVE-2026-19295

GitHubrmhowe425/poc-cve-2026-19295

Proof-of-concept exploit for CVE-2026-19295 targeting Langflow, allowing authenticated exploitation via command-line interface.
exploitationpenetration-testingvulnerability-analysis+2
11 month ago
CVE-2026-20896 preview

CVE-2026-20896

GitHubyym8538/cve-2026-20896

Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
authenticationcontainer-securityexploitation+5
11 month ago
CVE-2021-45007 preview

CVE-2021-45007

GitHubas4mir/cve-2021-45007

Proof-of-concept for CVE-2021-45007, a CSRF vulnerability in Plesk Obsidian 18.0.37, demonstrating request submission without CSRF token protection.
exploitationvulnerability-analysisweb-application-exploitation+1
24 years ago
CVE-2026-15598 preview

CVE-2026-15598

GitHubiamdremig/cve-2026-15598

Proof-of-concept for CVE-2026-15598, a prototype-pollution weakness in AntV Layout 2.0.0's setNestedValue that lets attackers remotely alter object…
exploitationvulnerability-analysisweb-application-exploitation+1
12 months ago
CVE-2025-46817 preview

CVE-2025-46817

GitHubdwisiswant0/cve-2025-46817

Proof-of-concept for Redis Lua unpack integer overflow (CVE-2025-46817) demonstrating stack blow-up and potential RCE on Redis 8.2.1.
binary-exploitationdatabase-securityexploitation+2
31 year ago
CVE-2025-46818 preview

CVE-2025-46818

GitHubdwisiswant0/cve-2025-46818

Exploit for Redis 8.2.1 Lua sandbox escape via deprecated APIs and mutable metatables, enabling cross-user command execution.
exploitationpenetration-testingred-teaming+2
31 year ago
CVE-2021-41773 preview

CVE-2021-41773

GitHubcorelight/cve-2021-41773

Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…
exploitationincident-responseintrusion-detection+3
14 years ago
CVE-2026-8452-check preview

CVE-2026-8452-check

GitHubbishopfox/cve-2026-8452-check

Behavioral patch-state detector for Citrix NetScaler CVE-2026-8452. Sends crafted SAML requests to determine whether the PrefixList size check is…
network-securityvulnerability-analysisvulnerability-scanners+1
11 month ago
Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation preview

Incident-Analysis-Response-Check-Point-Security-Gateway-CVE-2024-24919-LFI-Exploitation

GitHubzedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
digital-forensicseducationincident-response+7
12 months ago
PAN-OS_CVE-2024-9474 preview

PAN-OS_CVE-2024-9474

GitHubcoskper-papa/pan-os_cve-2024-9474

Proof-of-concept exploit for CVE-2024-9474 in Palo Alto Networks PAN-OS. Executes Python-based exploitation against vulnerable firewalls.

exploitationnetwork-securitypenetration-testing+2
21 year ago
Previous1…969798…100Next