
CVE-2026-14840
 nullwhisper/cve-2026-14840
Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
exploitationlabs-practicepenetration-testing+3
nullwhisper/cve-2026-14840Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
 blinky-keys/cve-2026-48060
Proof-of-concept exploit and vulnerable application demonstrating an HTML injection vulnerability in Litestar 2.21.0 via CSRF token, with Docker…
 e4zyy/project-cve-2026-65351
Browser resource exhaustion payload that crashes target systems via memory, GPU, audio, and rendering overload. Designed for authorized security…
 ozozuz/magnolia-cms-6.2.19-stored-cross-site-scripting-cve-2022-33098
Proof-of-concept exploit for stored cross-site scripting (XSS) in Magnolia CMS 6.2.19 via crafted SVG upload, with detailed vulnerability analysis…
 ridhinva/beyondtrust-rce-scanner
Scanner: CVE-2026-1731 BeyondTrust Remote Support Pre-auth RCE — Python checker for actively exploited vulnerability (CISA KEV)
 nvicloud/cve-2026-12948
Proof of concept for stored XSS in Digi PortServer TS 4 H MEI web interface, demonstrating persistent payload execution and providing remediation…
 k0ns0l/cve-2024-10400
Proof-of-concept exploit for CVE-2024-10400, a time-based blind SQL injection in Tutor LMS WordPress plugin, allowing unauthenticated attackers to…
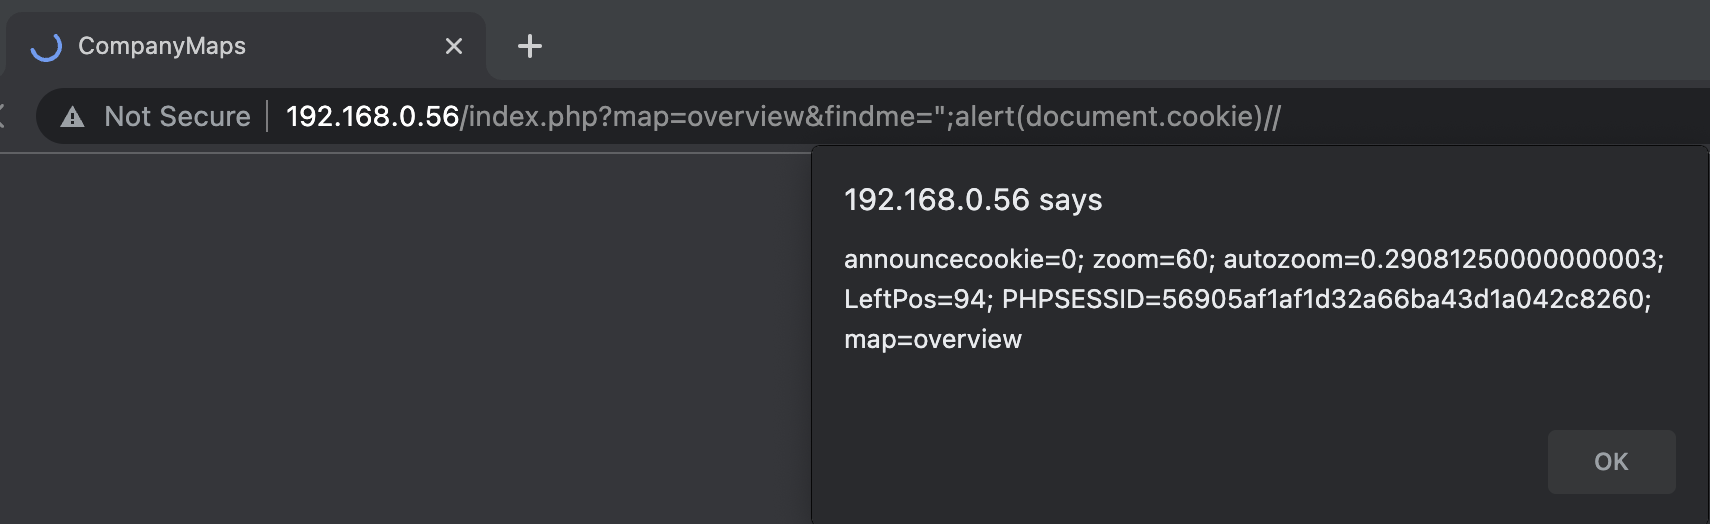 zprototype/cve-2023-29808
Reflected cross-site scripting (XSS) proof-of-concept exploit for CVE-2023-29808 targeting the /index.php?map=overview&findme= endpoint in cmaps…
 knight0x07/cve-2023-43770-poc
PoC for Stored XSS (CVE-2023-43770) Vulnerability
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 alfredooe/cve-2026-31431
Go implementation of CopyFail CVE-2026-31431, providing a proof-of-concept exploit for the vulnerability.
 venablee/cve-2026-30251
Reflected XSS vulnerability disclosure for ZenShare Suite login_newpwd.php, allowing arbitrary JavaScript execution via crafted URL in codice_azienda…
 gduma-phdata/patch-cve-2026-10520
Patch for Apache Struts OGNL injection vulnerability (CVE-2026-10520), currently in review and deployed to production.
 h3x0v3rl0rd/cve-2019-9053
Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…
 mrrawbit/sonicwall-sma1000-zero-day-ioc-check
Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…