
CVE-2026-47117-openmed-rce
 saiteja-erukude/cve-2026-47117-openmed-rce
OpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True
ai-securityexploitationpenetration-testing+3
saiteja-erukude/cve-2026-47117-openmed-rceOpenMed < 1.5.2 unauthenticated RCE via PII privacy-filter model loading and trust_remote_code=True
 gagaltotal/cve-2026-34910-unifi-poc
Proof-of-concept exploit for UniFi OS CVE-2026-34910 auth bypass enabling command injection/RCE, and CVE-2026-34909 path traversal for arbitrary file…
 oscerd/cve-2026-55993
PoC reproducer for CVE-2026-55993 (Apache Camel camel-atmosphere-websocket): the WebSocket consumer copies connection query parameters onto the…
 chpratik/cve-2026-9830
Threat intelligence report repository for CVE-2026-9830, an authentication bypass vulnerability in BookingPress Pro WordPress plugin, with detailed…
 fevar54/cve-2026-60004
Detects and exploits a critical pre-auth remote code execution vulnerability in Gitea via the diffpatch endpoint, with a non-intrusive detector and…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
 gustanini/cve-2022-42889-text4shell-poc
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell), demonstrating remote code execution via Apache Commons Text string substitution.
 oscerd/cve-2026-46726
Reproducer for CVE-2026-46726: Apache Camel camel-vertx-websocket unfiltered inbound header injection enabling SSRF and secret disclosure via…
 george0papasotiriou/cve-2026-11118-http-2-rapid-reset-ddos
Python PoC for CVE-2026-11118 demonstrating HTTP/2 Rapid Reset DDoS via RST_STREAM resource exhaustion; includes vulnerable server simulator and…
 s0ck37/cve-2025-22131-poc
POC for the vuln CVE-2025-22131
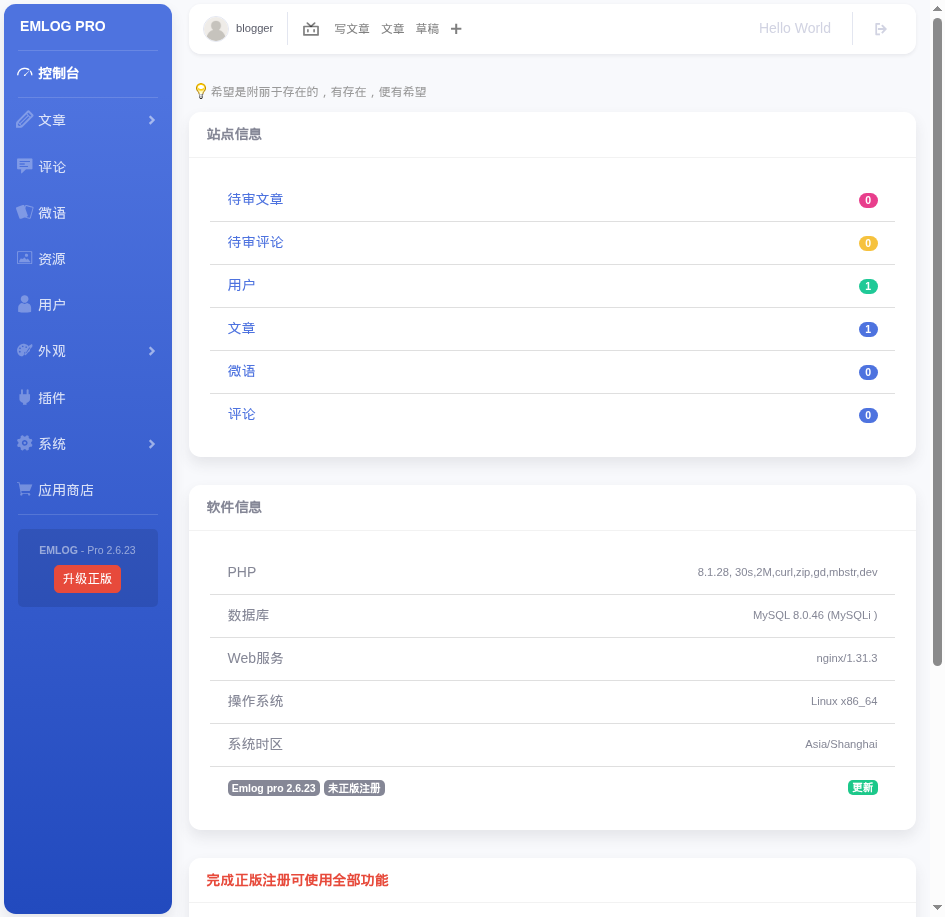 squeeze440/cve-2026-73847-emlog-poc
PoC for CVE-2026-73847 - emlog AI Assistant CSRF to SQL execution to admin takeover (CVSS 6.8)
 george0papasotiriou/cve-2026-22006-xslt-server-side-injection-via-xsl-script-
Proof-of-concept for CVE-2026-22006, demonstrating XSLT server-side injection via xsl:script in an lxml Flask endpoint to achieve remote code…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 0xdak/cve-2026-14483_exploit
Unauthenticated arbitrary file upload exploit for Realtyna WPL/Organic IDX WordPress plugin, chains PHP webshell upload to RCE, with command…
 daehyuh/cve-2026-47883
Minimal proof-of-concept for Spring Framework UrlHandlerFilter open redirect (CVE-2026-47883), demonstrating crafted double-slash requests produce…
 murrez/cve-j2store-2026
PoC for J2Store CVE-2026-67358–67362 (J2Commerce security advisory Aug 2026)
 dodgenefoli/cve-2025-64512
Automated proof-of-concept exploit for CVE-2025-64512 that accepts Target and Upload_dir parameters to test vulnerable file-upload functionality in…