
CVE-2014-0160.
 tungduongnt/cve-2014-0160.
Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
educationexploitationintrusion-detection+3
tungduongnt/cve-2014-0160.Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
 cuteecat/cve-2026-73633
Proof-of-concept exploit for Apache Struts S2-072 (CVE-2026-73633), demonstrating CPU and memory exhaustion by sending crafted JSON requests to the…
 fevar54/cve-2026-3055---citrix-netscaler-memory-overread-poc
PoC de CVE-2026-3055: memory overread en Citrix NetScaler ADC/Gateway para filtrar session IDs.
 bishopfox/cve-2026-8452-check
Behavioral patch-state detector for Citrix NetScaler CVE-2026-8452. Sends crafted SAML requests to determine whether the PrefixList size check is…
 renzi25031469/cve-2026-49975-http-2-bomb
Disclosed on June 3, 2026, the "HTTP/2 Bomb" is an unauthenticated remote DoS that combines an HPACK compression bomb with a Slowloris-style hold to…
 chaitanyagarware/cve-2026-54519
Public advisory landing page for CVE-2026-54519: missing ownership checks in ai-agent-automation memory APIs enabling cross-user memory read and…
 mehranturk/cve-2023-45802
CVE-2023-45802 - Apache HTTP/2 Memory Exhaustion DoS Apache versions: 2.4.17 through 2.4.57 Target: Apache/2.4.52 (Ubuntu) - VULNERABLE MehranTurk…
 netvanguard-cmd/cve-2026-3055
Proof-of-concept exploit for CVE-2026-3055, a memory overread in NetScaler ADC and Gateway when configured as SAML IDP, with detection and mitigation…
 mbanyamer/cve-2026-24514-kubernetes-dos
Proof-of-concept exploit for CVE-2026-24514, a memory exhaustion denial-of-service in ingress-nginx validating admission webhook, allowing…
 there-was-a-bird/triton-cve-2025-23320
Docker-based proof-of-concept demonstrating CVE-2025-23320 in NVIDIA Triton inference server, exploiting shared memory key leakage to trigger an…
 b1gn0se/tomcat-cve-2025-31650
Proof-of-concept exploit for Apache Tomcat HTTP/2 DoS vulnerability (CVE-2025-31650). Sends malformed priority headers to trigger memory exhaustion.…
 22imer/cve-2014-0160
Dockerized training lab for exploiting Heartbleed (CVE-2014-0160) via TLS heartbeat to leak nginx memory, plus Snort rule to detect attacks.
 ianxtianxt/cve-2019-16279
Shell script exploit for CVE-2019-16279 that triggers a denial-of-service via memory corruption by sending excessive CRLF sequences to an HTTP server.
 r1az4r/cve-2006-20001
A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…
 0xgh057r3c0n/cve-2025-5777
Citrix NetScaler Memory Leak PoC
 0xkayala/cve-2023-4966
CVE-2023-4966 - NetScaler ADC and NetScaler Gateway Memory Leak Exploit
 pierceoneill/bleeding-heart
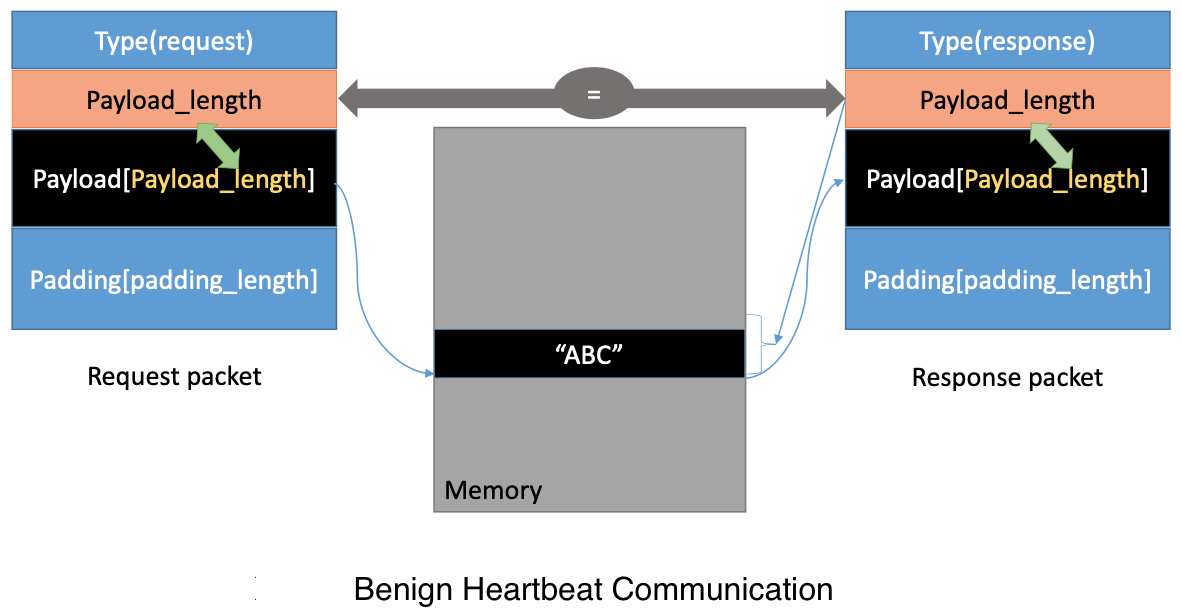
The Heartbleed bug `CVE-2014-0160` is a severe implementation flaw in the OpenSSL library, which enables attackers to steal data from the memory of…
 yashfren/cve-2014-0160-heartbleed
Python exploit for CVE-2014-0160 (Heartbleed) that extracts memory contents from vulnerable OpenSSL servers, adapted for Python 3 compatibility.