
CVE-2026-34220
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
database-securityexploitationpenetration-testing+4
1
yym8538/cve-2026-34220Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 twseptian/cve-2021-38314
cve-2021-38314 - Unauthenticated Sensitive Information Disclosure
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 nyakki-labs-0x420/myesve
CVE-2024-38475 exploitation & scanning tool with Mullvad VPN rotation
 shaheryar773/mitigate-cve-2026-23869-react-server-component-loops
Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.
 th-secforge/cve-2025-29972
CVE-2025-29927 - Critical Security Vulnerability in Next.js
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
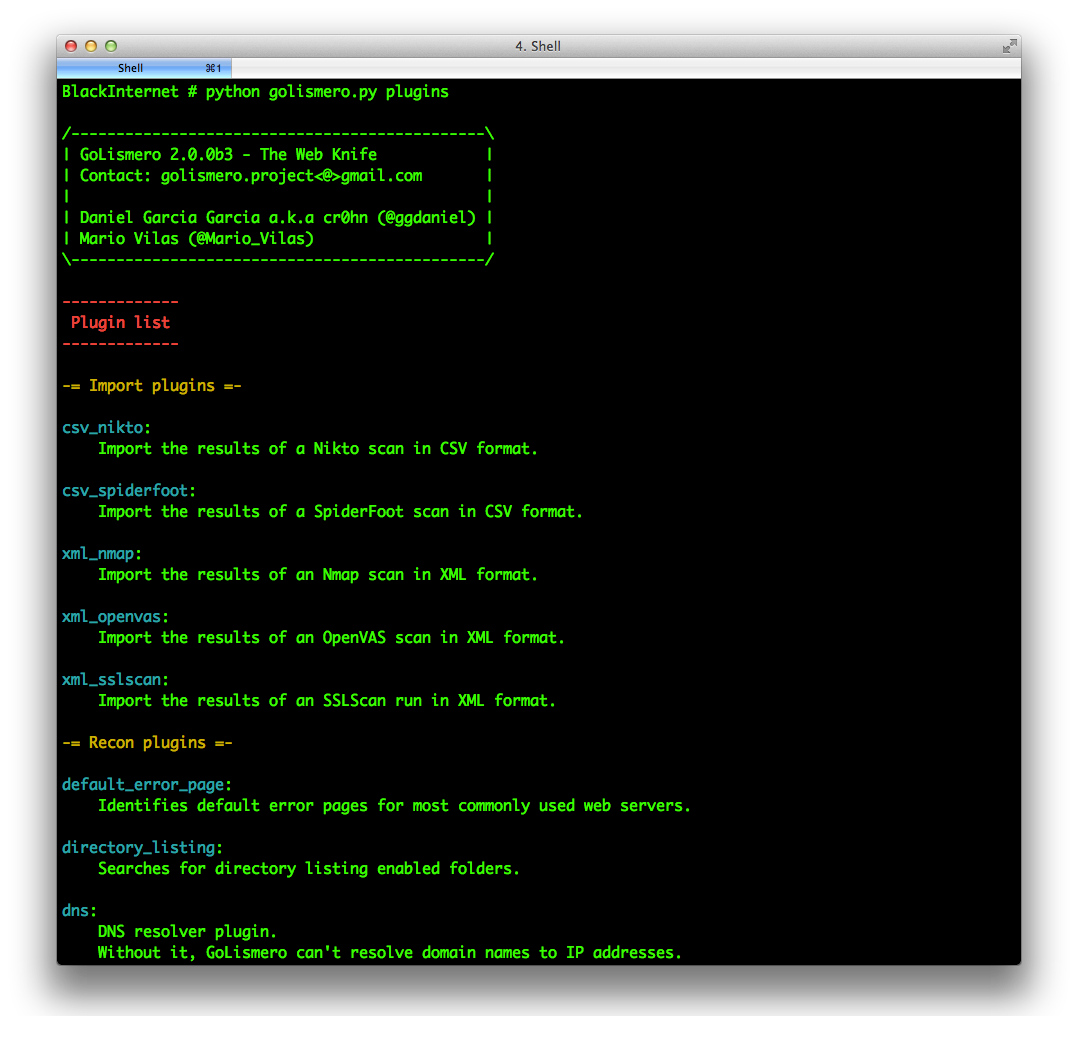 golismero/golismero
GoLismero - The Web Knife
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
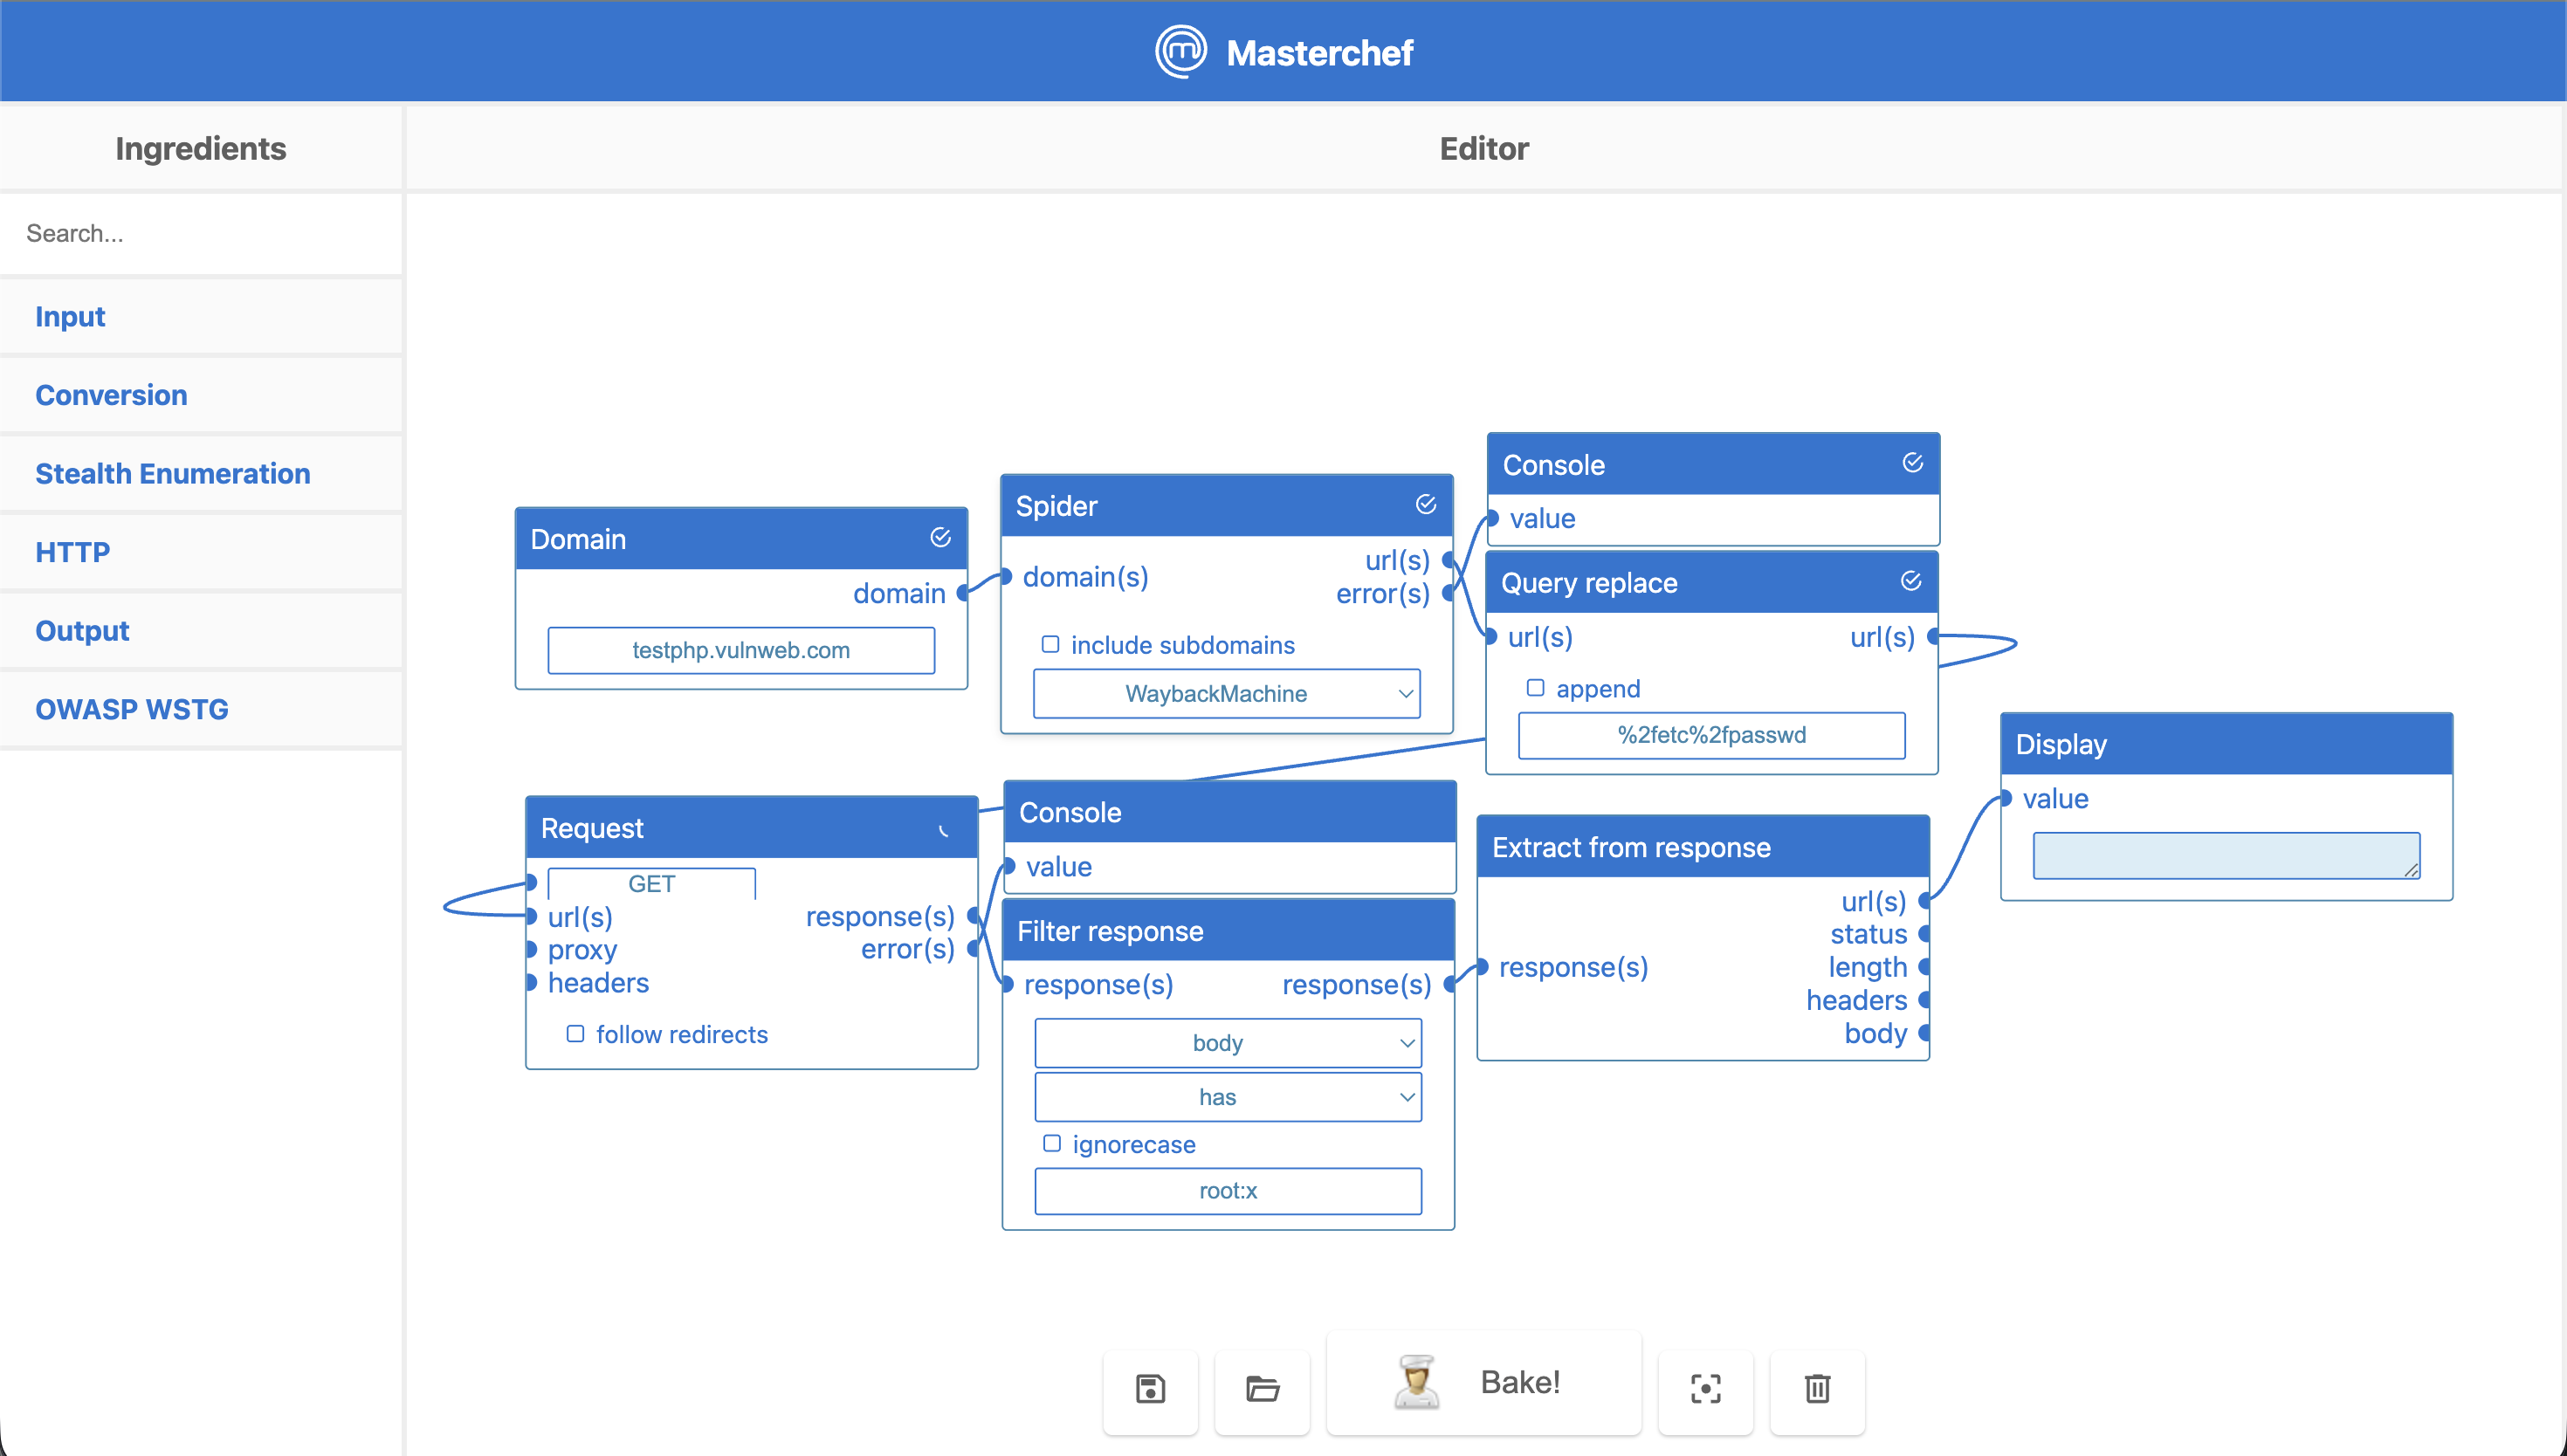 cosasdepuma/masterchef
🍳 The most delicious pentesting tool