
ReconHound
 s_r_e_e_r_a_j/reconhound
ReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
fuzzinginformation-gatheringpenetration-testing+3
1
s_r_e_e_r_a_j/reconhoundReconHound is a Python-based web reconnaissance tool designed for penetration testers, bug bounty hunters, and ethical hackers. It supports directory…
 tjoulel/wordpress-6.9.1-blind-ssrf
Based on CVE-2022-3590, WordPress <= 6.9.1 - Unauthenticated Blind SSRF via XML-RPC Pingback Discovery proof of concept (PoC)
 lorenzobruno7/cve-2026-26744
Demonstrates user enumeration in FormaLMS via response discrepancy on the /lostpwd endpoint, enabling unauthenticated username discovery for targeted…
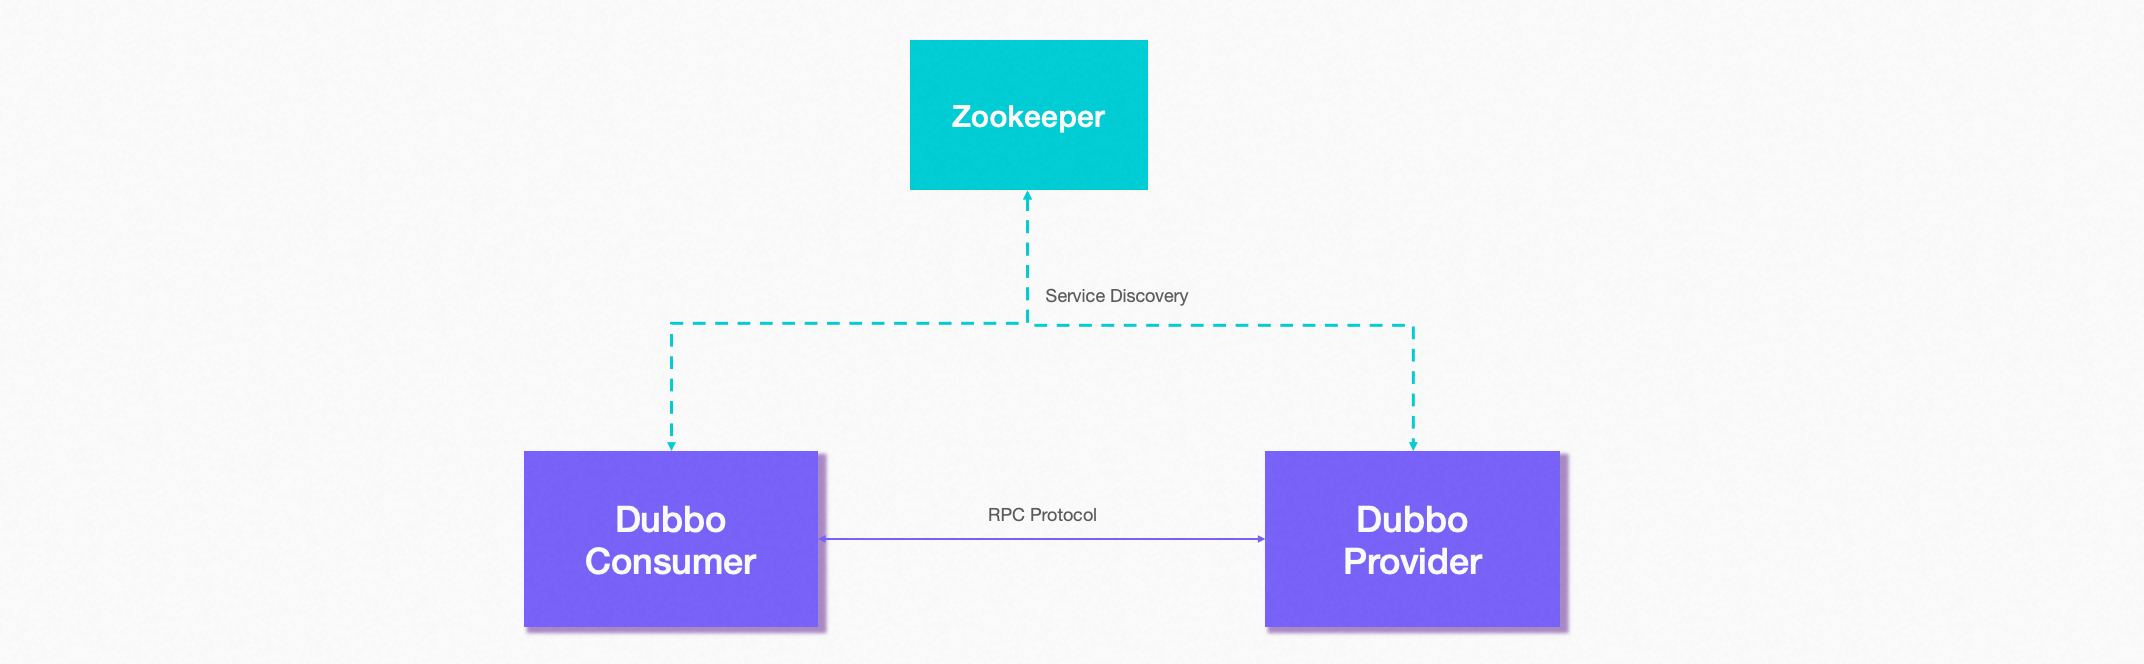 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 sattarbug/analysis-of-tomcatkiller---cve-2025-31650-exploit-tool
Detects CVE-2025-31650 in Apache Tomcat servers with Shodan-based target discovery and CSV/JSON reporting for vulnerability assessment.
 becrevex/cve-2023-41425
WonderCMS v3.4.2 NSE Discovery Script
 becrevex/citrix_cve-2019-19781
Took at stab at an NSE discovery script for CVE-2019-19781.
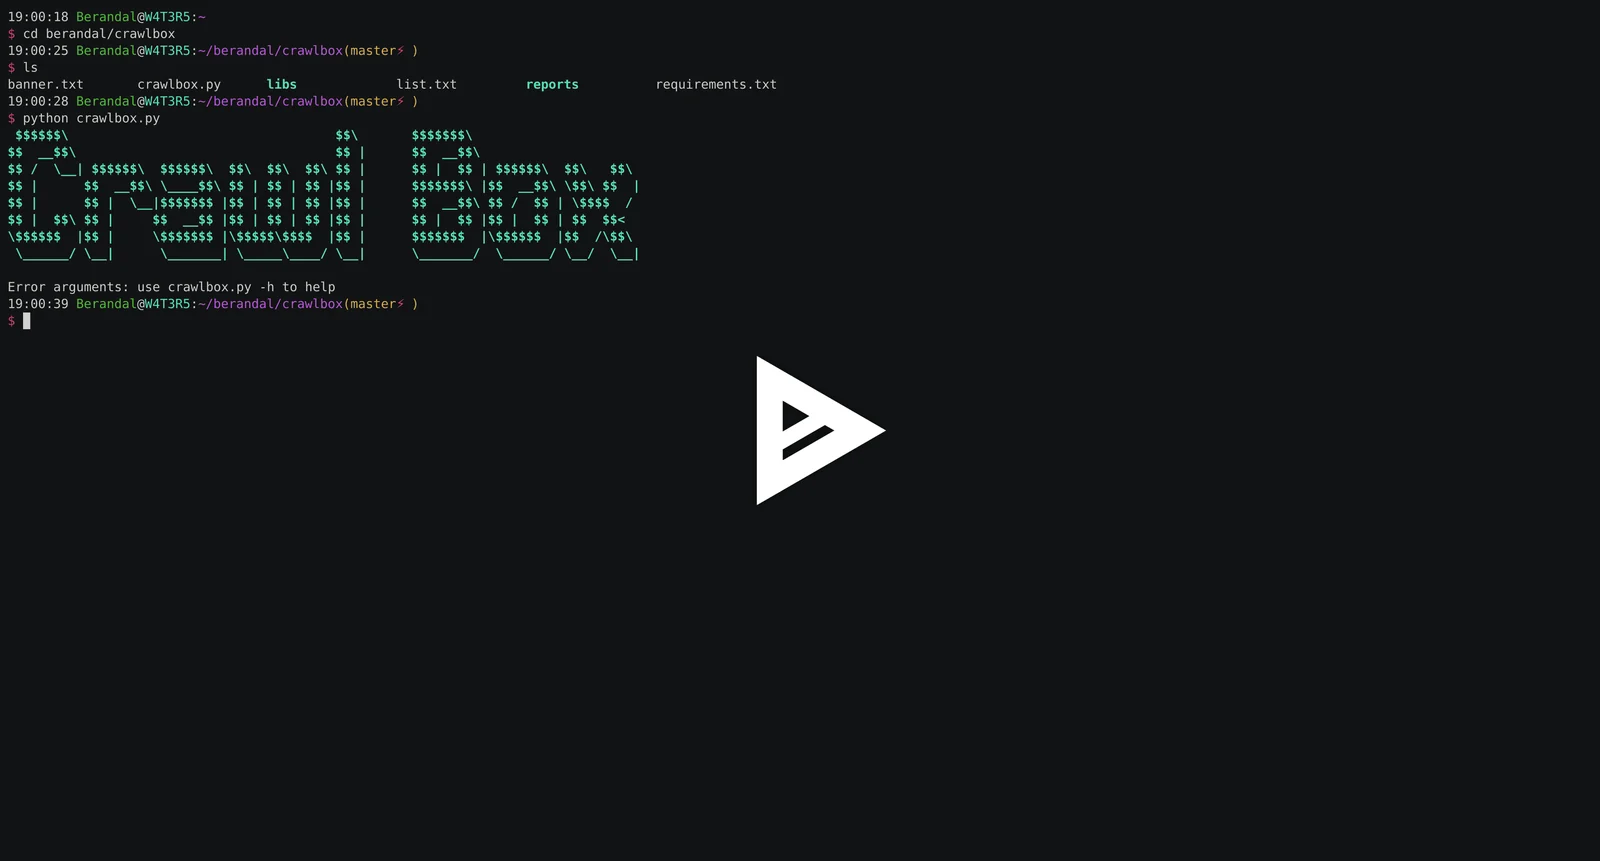 opiniondealer/crawlbox
Python script that brute-forces web directories and admin paths using built-in or custom wordlists, with configurable request delays for directory…

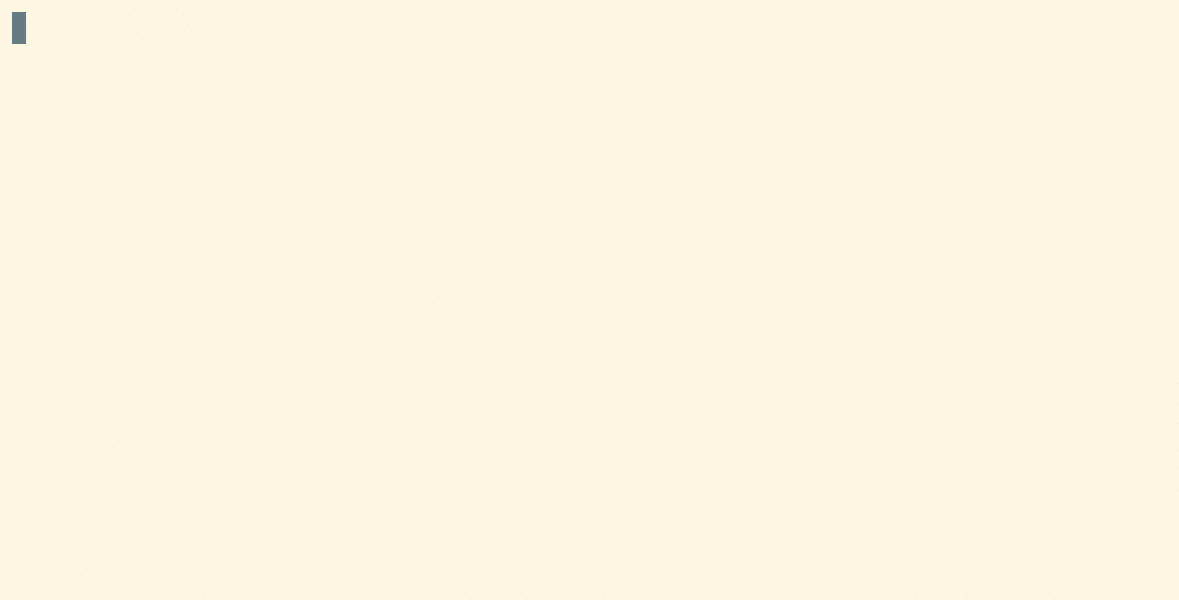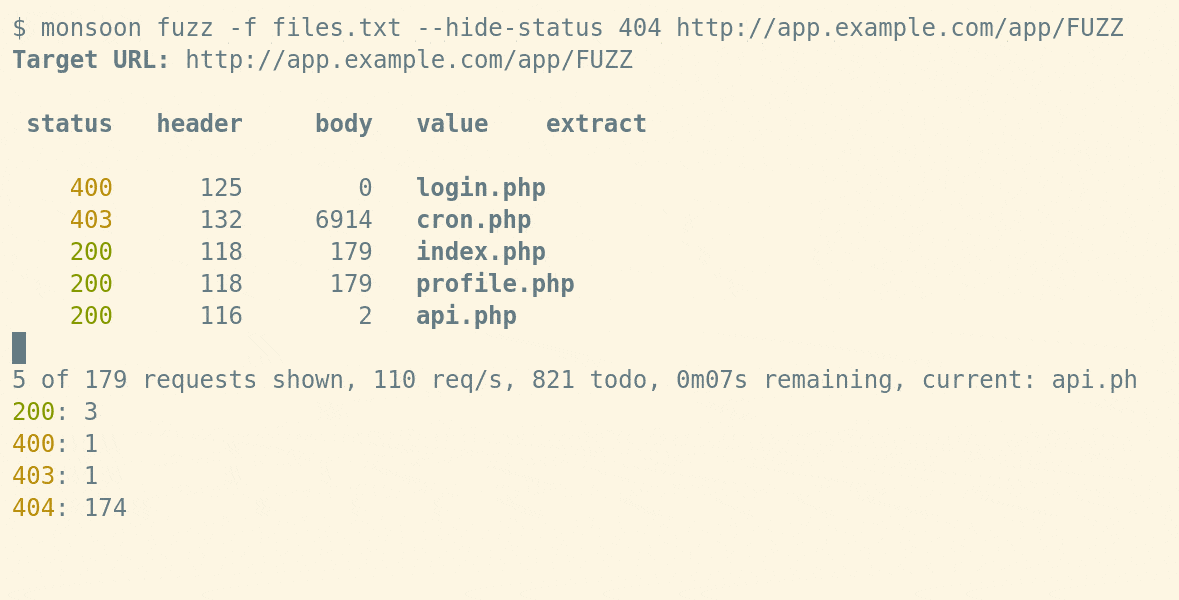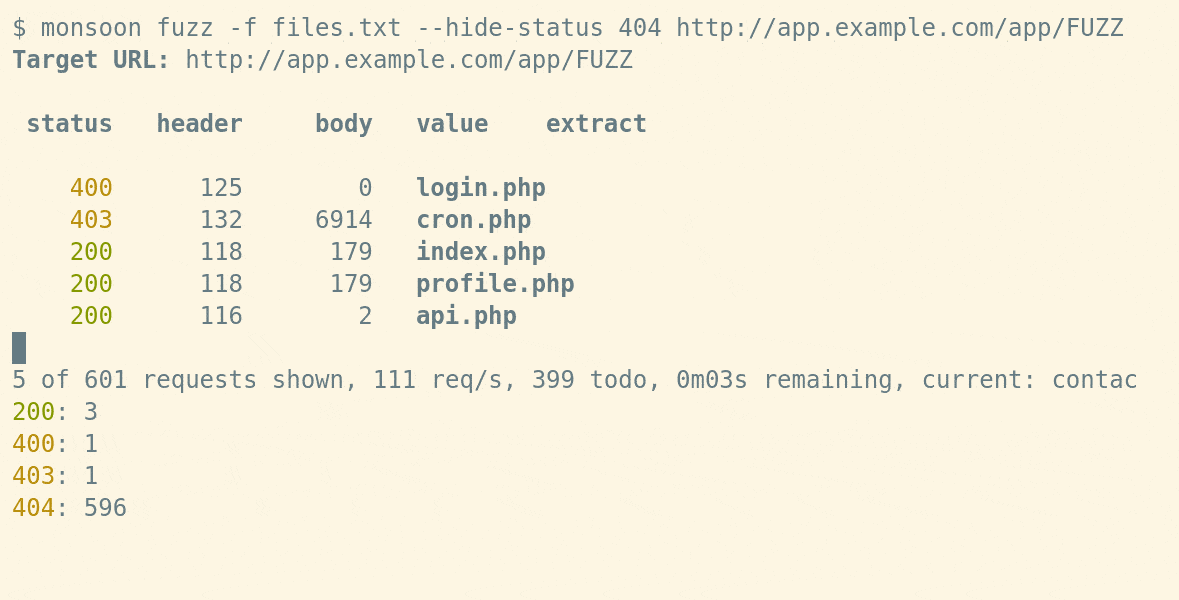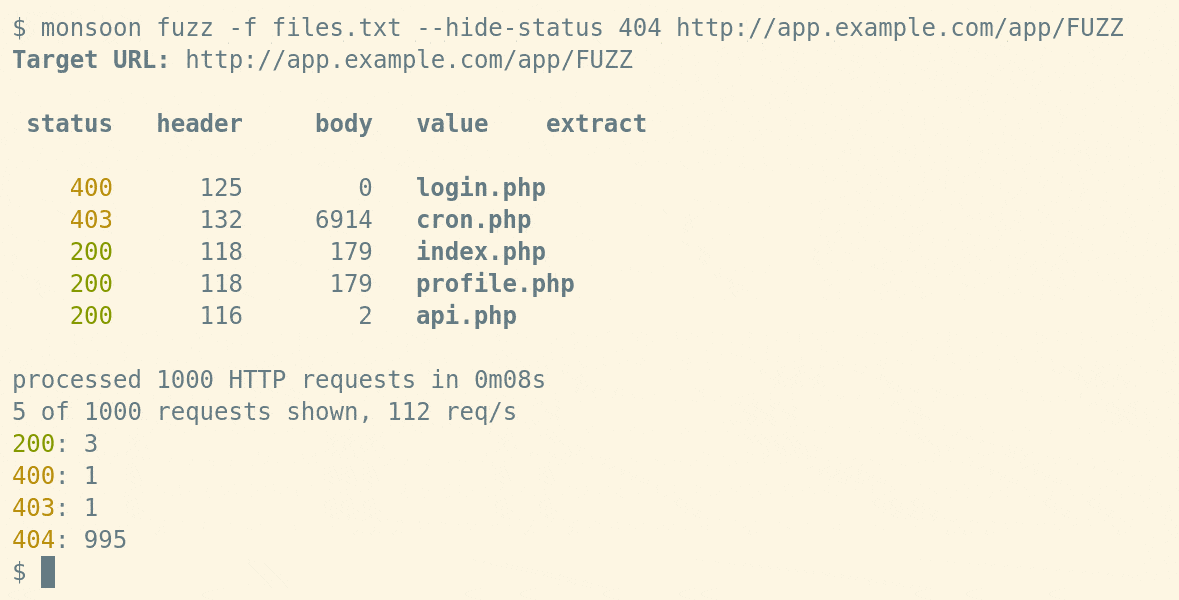 redteampentesting/monsoon
Fast HTTP enumerator
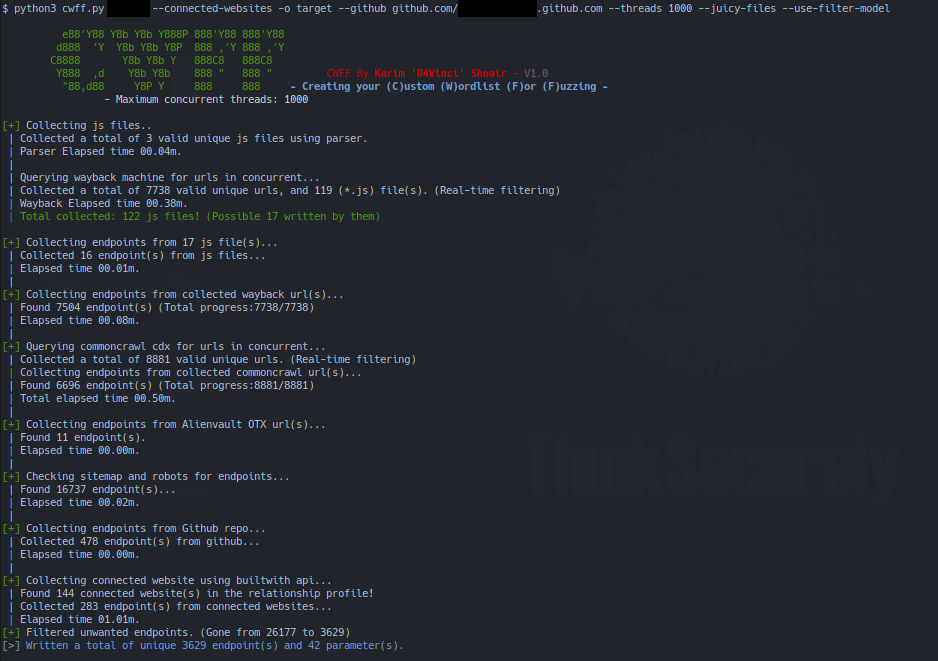 d4vinci/cwff
Create your Custom Wordlist For Fuzzing
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 chaudharyarjun/jwtxposer
An advanced JWT extraction & decoding tool for bug bounty hunters! 🏴☠️
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.