

zappzarapp-php-security
 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
api-securityauthentication-authorizationcode-analysis+6
marcstraube/zappzarapp-php-securityPHP 8.4+ security library (mirror)

 bishopfox/cve-2026-0265-check
Safely detect whether a PAN-OS target is vulnerable to CVE-2026-0265.
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 oguz-kagan-akar/cve-2026-41940-analysis
Technical analysis of the cPanel/WHM auth bypass
 nel-droid/cve-2026-71206-poc
PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)
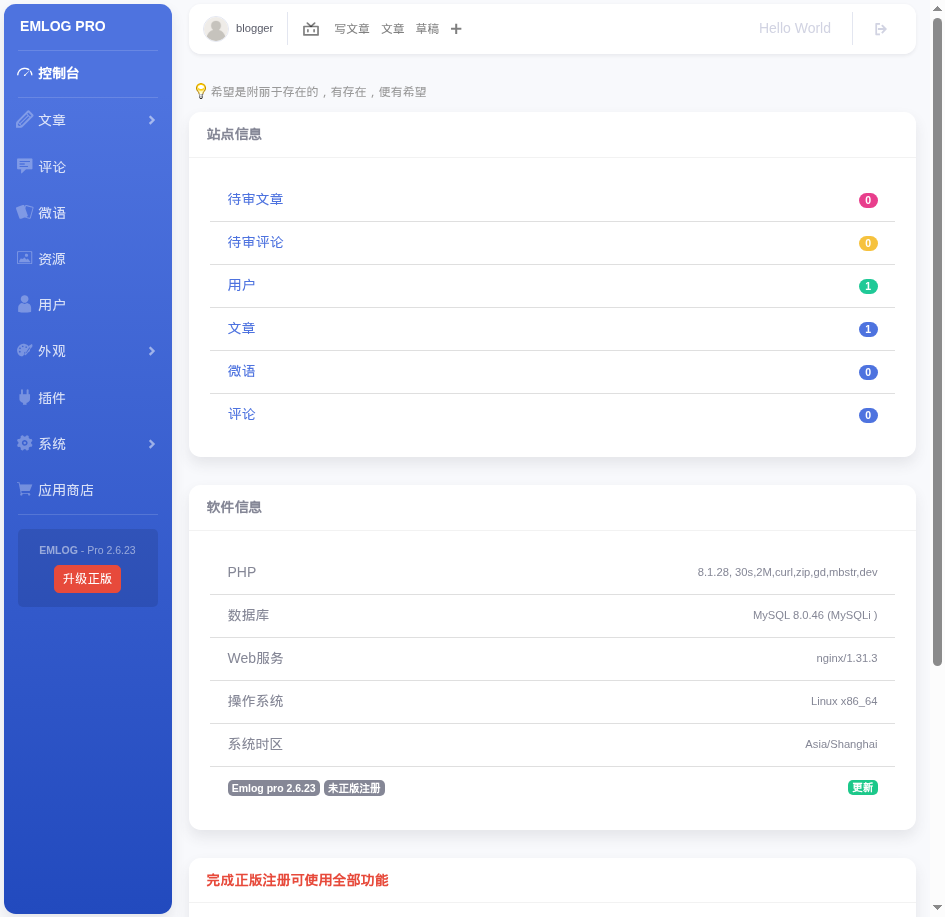 squeeze440/cve-2026-73847-emlog-poc
PoC for CVE-2026-73847 - emlog AI Assistant CSRF to SQL execution to admin takeover (CVSS 6.8)
 pn-tester/cve-2022-35497
TM4WEB Vulnerability - CVE-2022-35497
 bishopfox/cve-2026-11374-check
Detection script for CVE-2026-11374
 7own/cve-2021-26690---apache-mod_session
CVE-2021-26690 patch diffing - Apache HTTP mod_session NULL pointer dereference

 harley-ghostie/safe-check-cve-2025-23419
Script em python scanner safe-check da CVE-2025-23419
 jfriedli/cve-2025-12028
Proof-of-concept exploit for CVE-2025-12028 demonstrating CSRF-based OAuth token theft in WordPress IndieAuth plugin, enabling unauthorized API…
 ahrixia/cve-2023-43326
mooSocial v3.1.8 is vulnerable to cross-site scripting on Multiple URLs.
 ahrixia/cve-2023-43325
mooSocial v3.1.8 is vulnerable to cross-site scripting on user login function.
 ahrixia/cve-2023-44813
mooSocial v3.1.8 is vulnerable to cross-site scripting on Invite Friend function.
 ahrixia/cve-2023-45542
mooSocial v3.1.8 is vulnerable to cross-site scripting on search function.
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)