

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
390 results
atomicvulns preview

atomicvulns

GitHubdoretox/atomicvulns

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
ctfeducationlabs-practice+5
22
7 days ago
docker-cve-2022-39253-poc preview

docker-cve-2022-39253-poc

GitHubssst0n3/docker-cve-2022-39253-poc

Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…
container-escapecontainer-securityexploitation+2
101 year ago
CVE-2026-87902 preview

CVE-2026-87902

GitHubhassham1/cve-2026-87902

WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
educationexploitationlabs-practice+7
16 days ago
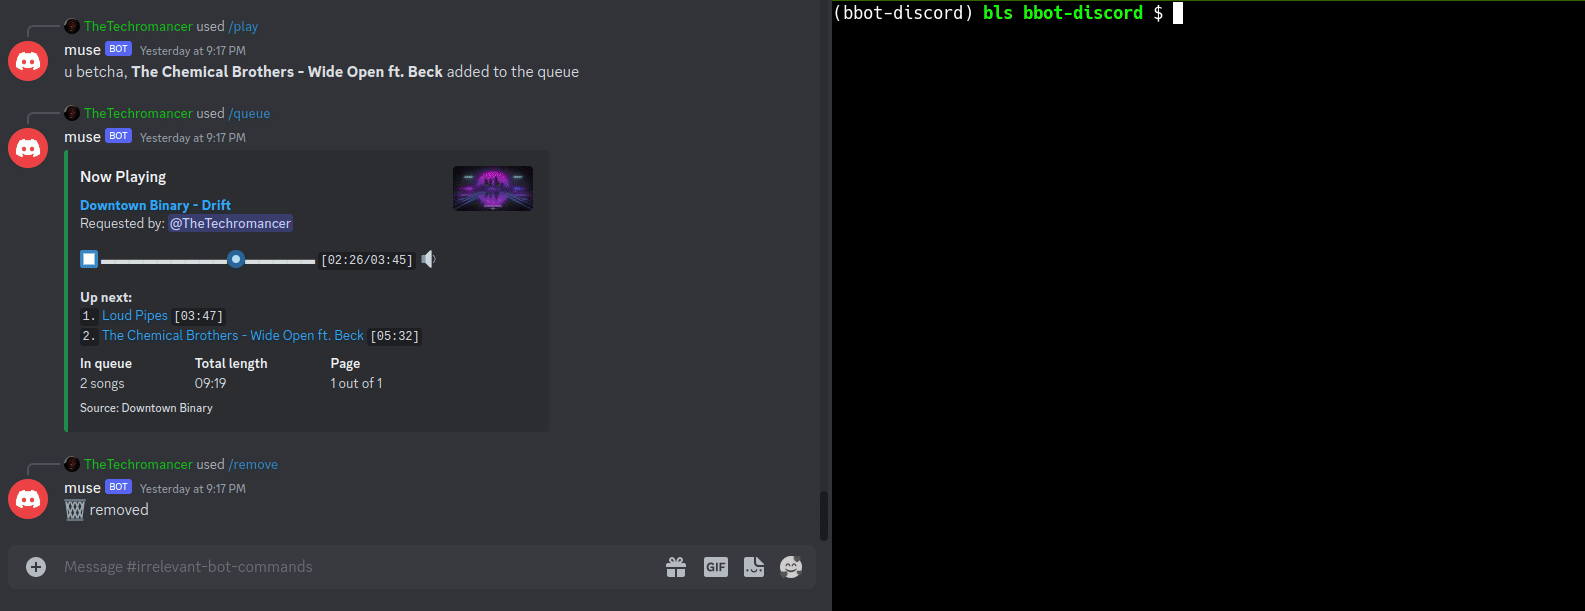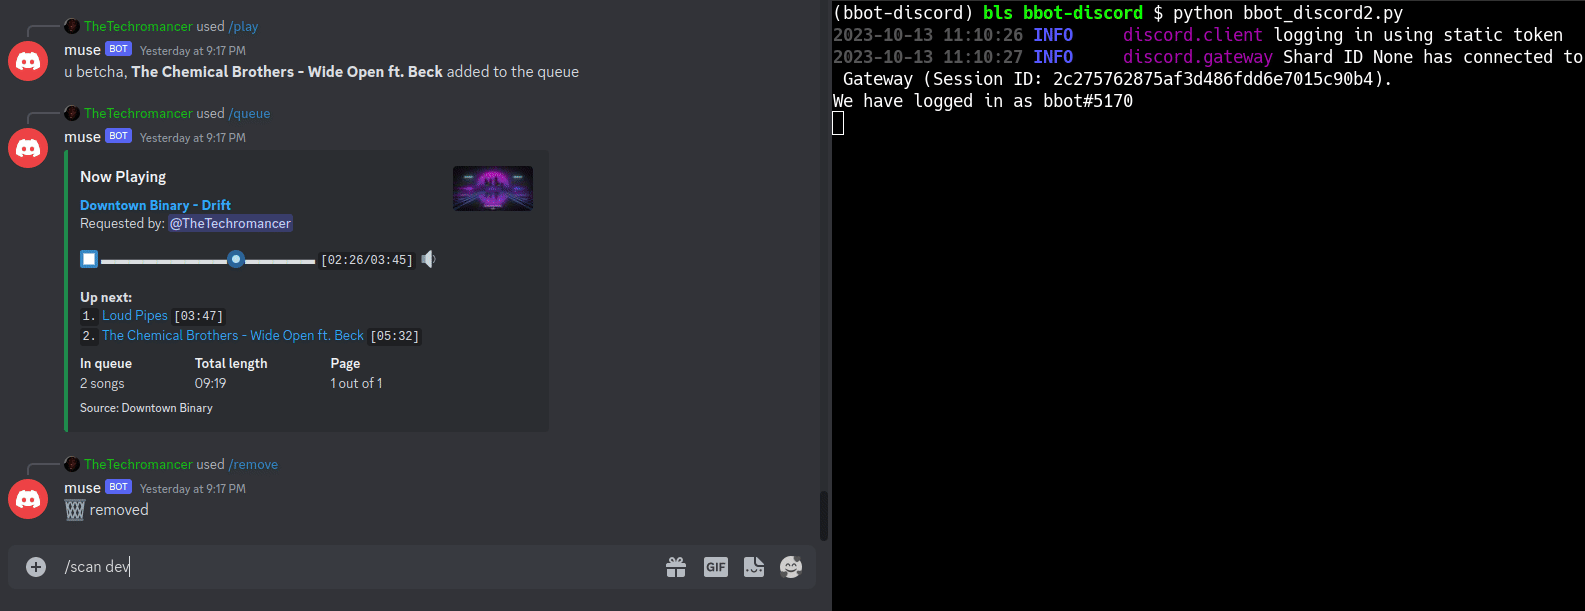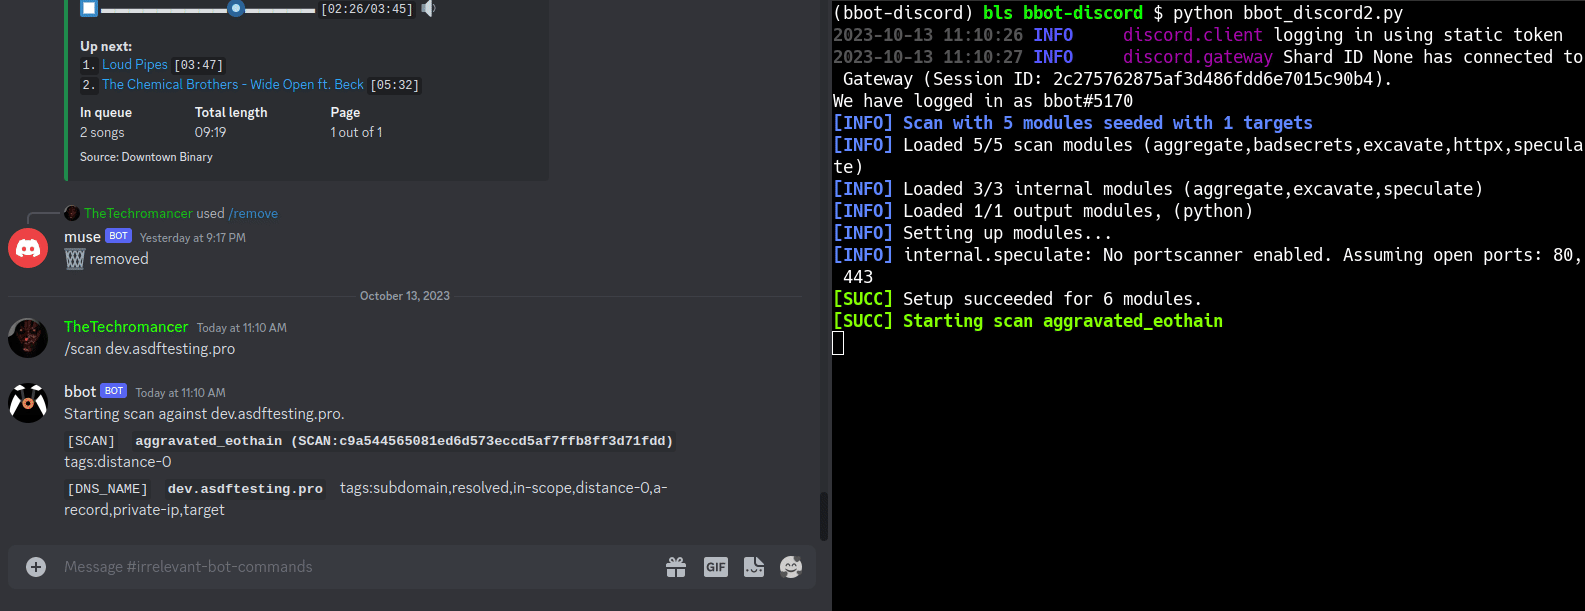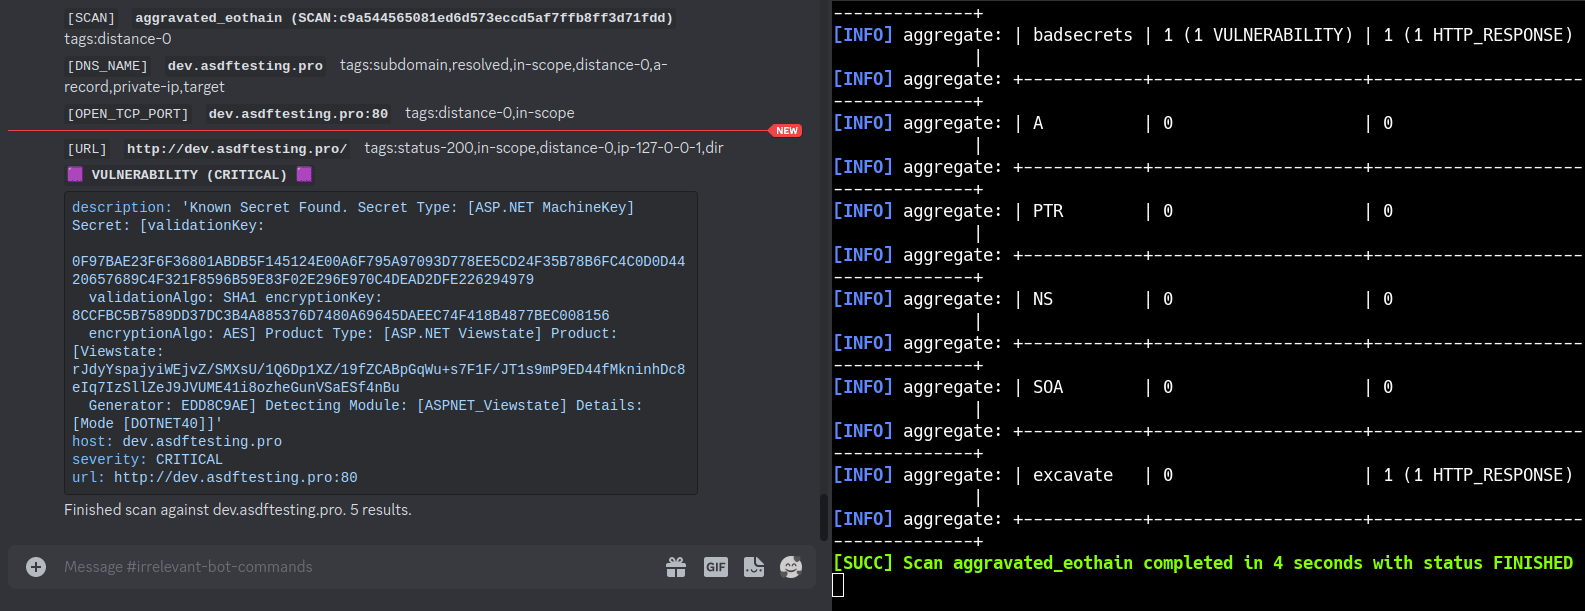
bbot preview

bbot

GitHubblacklanternsecurity/bbot

The recursive internet scanner for hackers. 🧡
crawlerdns-analysisemail-harvesting+8
10.6k1 month ago
heartbleed-lab preview

heartbleed-lab

GitHubayushsinha322/heartbleed-lab

Self-contained Heartbleed (CVE-2014-0160) lab: builds vulnerable OpenSSL 1.0.1f in Docker and includes a Python memory-leak PoC for authorised…

cryptographyeducationexploitation+5
13 days ago
CVE-2026-3844-Breeze-Cache-WordPress-Plugin-Remote-Code-Execution preview

CVE-2026-3844-Breeze-Cache-WordPress-Plugin-Remote-Code-Execution

GitHubdhananjayasj/cve-2026-3844-breeze-cache-wordpress-plugin-remote-code-execution

Docker lab and manual exploitation guide for CVE-2026-3844, a critical unauthenticated arbitrary file upload vulnerability in the Breeze Cache…
educationexploitationlabs-practice+3
3 months ago
CVE-2026-59550 preview

CVE-2026-59550

GitHubflx-0x00/cve-2026-59550

Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
educationexploitationlabs-practice+5
14 days ago
CVE-2026-66750-Insufficient-Access-Controls-Allow-for-Unauthorized-File-Downloads-Let-s-Chat- preview

CVE-2026-66750-Insufficient-Access-Controls-Allow-for-Unauthorized-File-Downloads-Let-s-Chat-

GitHubtheopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-

Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
authentication-authorizationeducationmisconfiguration+2
2 months ago
janusec preview

janusec

GitHubjanusec/janusec

Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

api-securityauthenticationcloud-security+8
1.2k2 months ago
CVE-2026-18322 preview

CVE-2026-18322

GitHubi3it/cve-2026-18322

Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
exploitationlabs-practicepapers-research+7
1 month ago
React2Shell preview

React2Shell

GitHubsho-luv/react2shell

CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
ctfeducationexploit-frameworks+7
109 months ago
bento preview

bento

GitHubhimazawa/bento

Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
container-securityctfexploitation+4
765 years ago
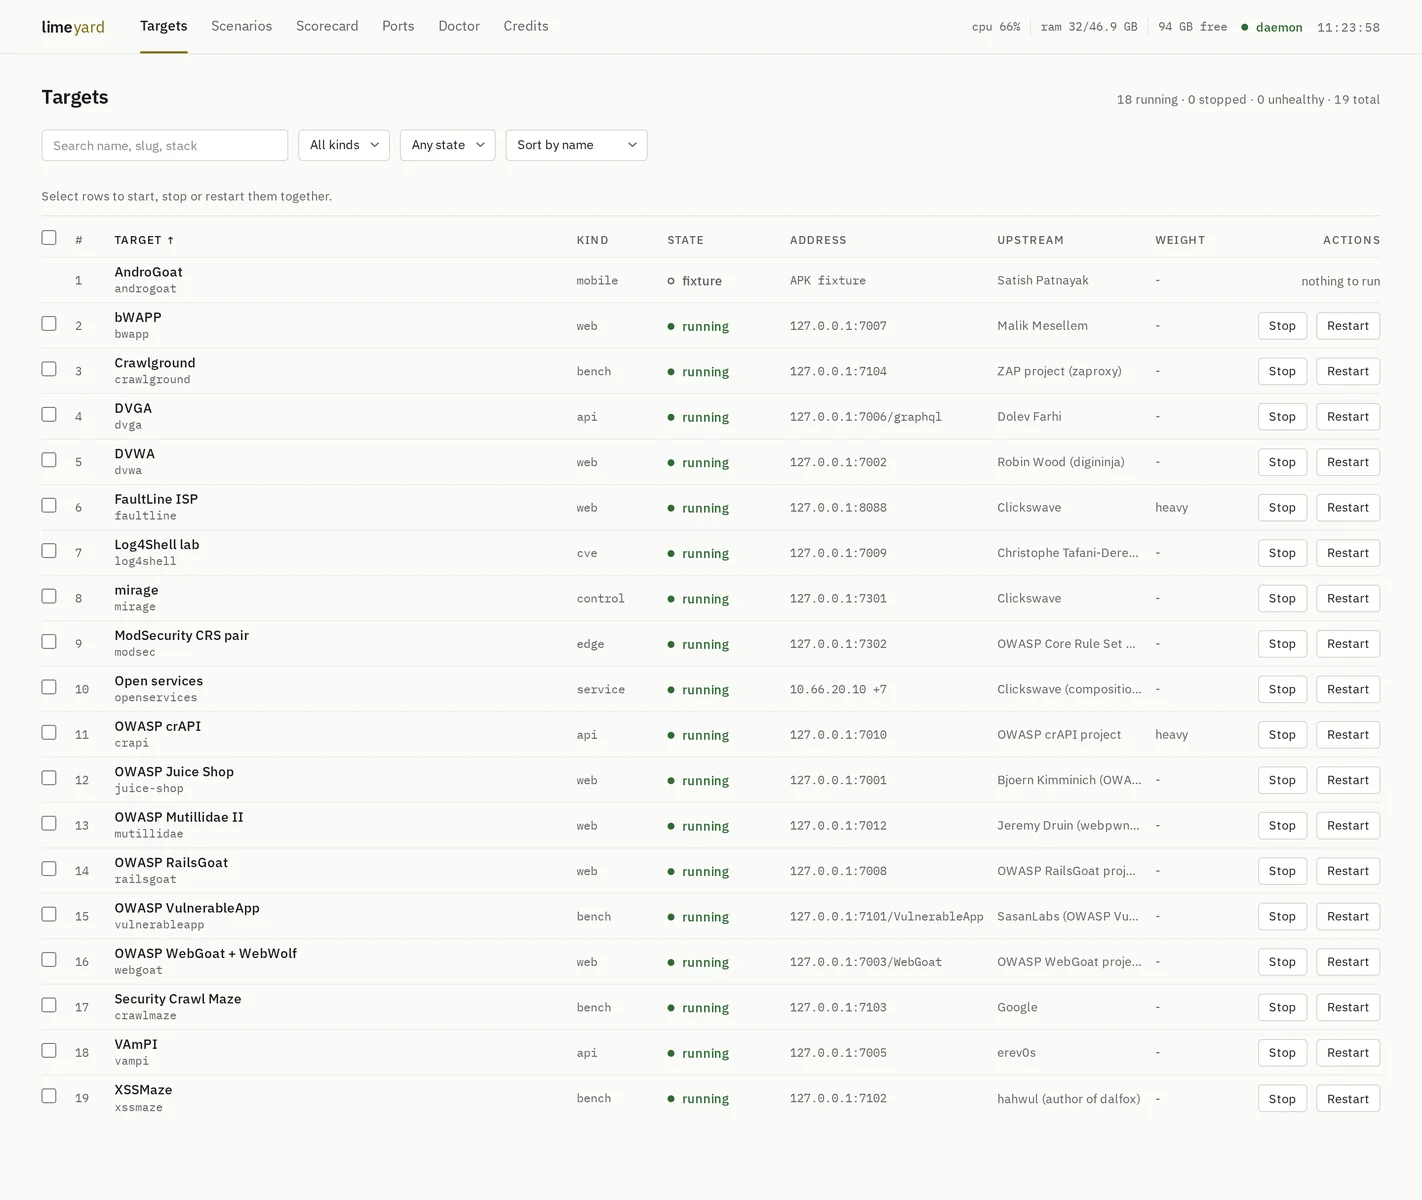
limeyard preview

limeyard

GitHubclickswave/limeyard

Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…

container-securitydevsecopsdns-subdomain-enumeration+8
117 days ago
iron-proxy preview

iron-proxy

GitHubparadigmxyz/iron-proxy

An egress firewall for untrusted workloads.
cloud-securitycontainer-securitydatabase-security+5
6825 days ago
offensive-docker preview

offensive-docker

GitHubaaaguirrep/offensive-docker

Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
container-securityexploit-frameworkspassword-cracking+5
7704 years ago
react2shell-scanner preview

react2shell-scanner

GitHubgensecaihq/react2shell-scanner

Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
code-analysiscontainer-securitydevsecops+4
589 months ago
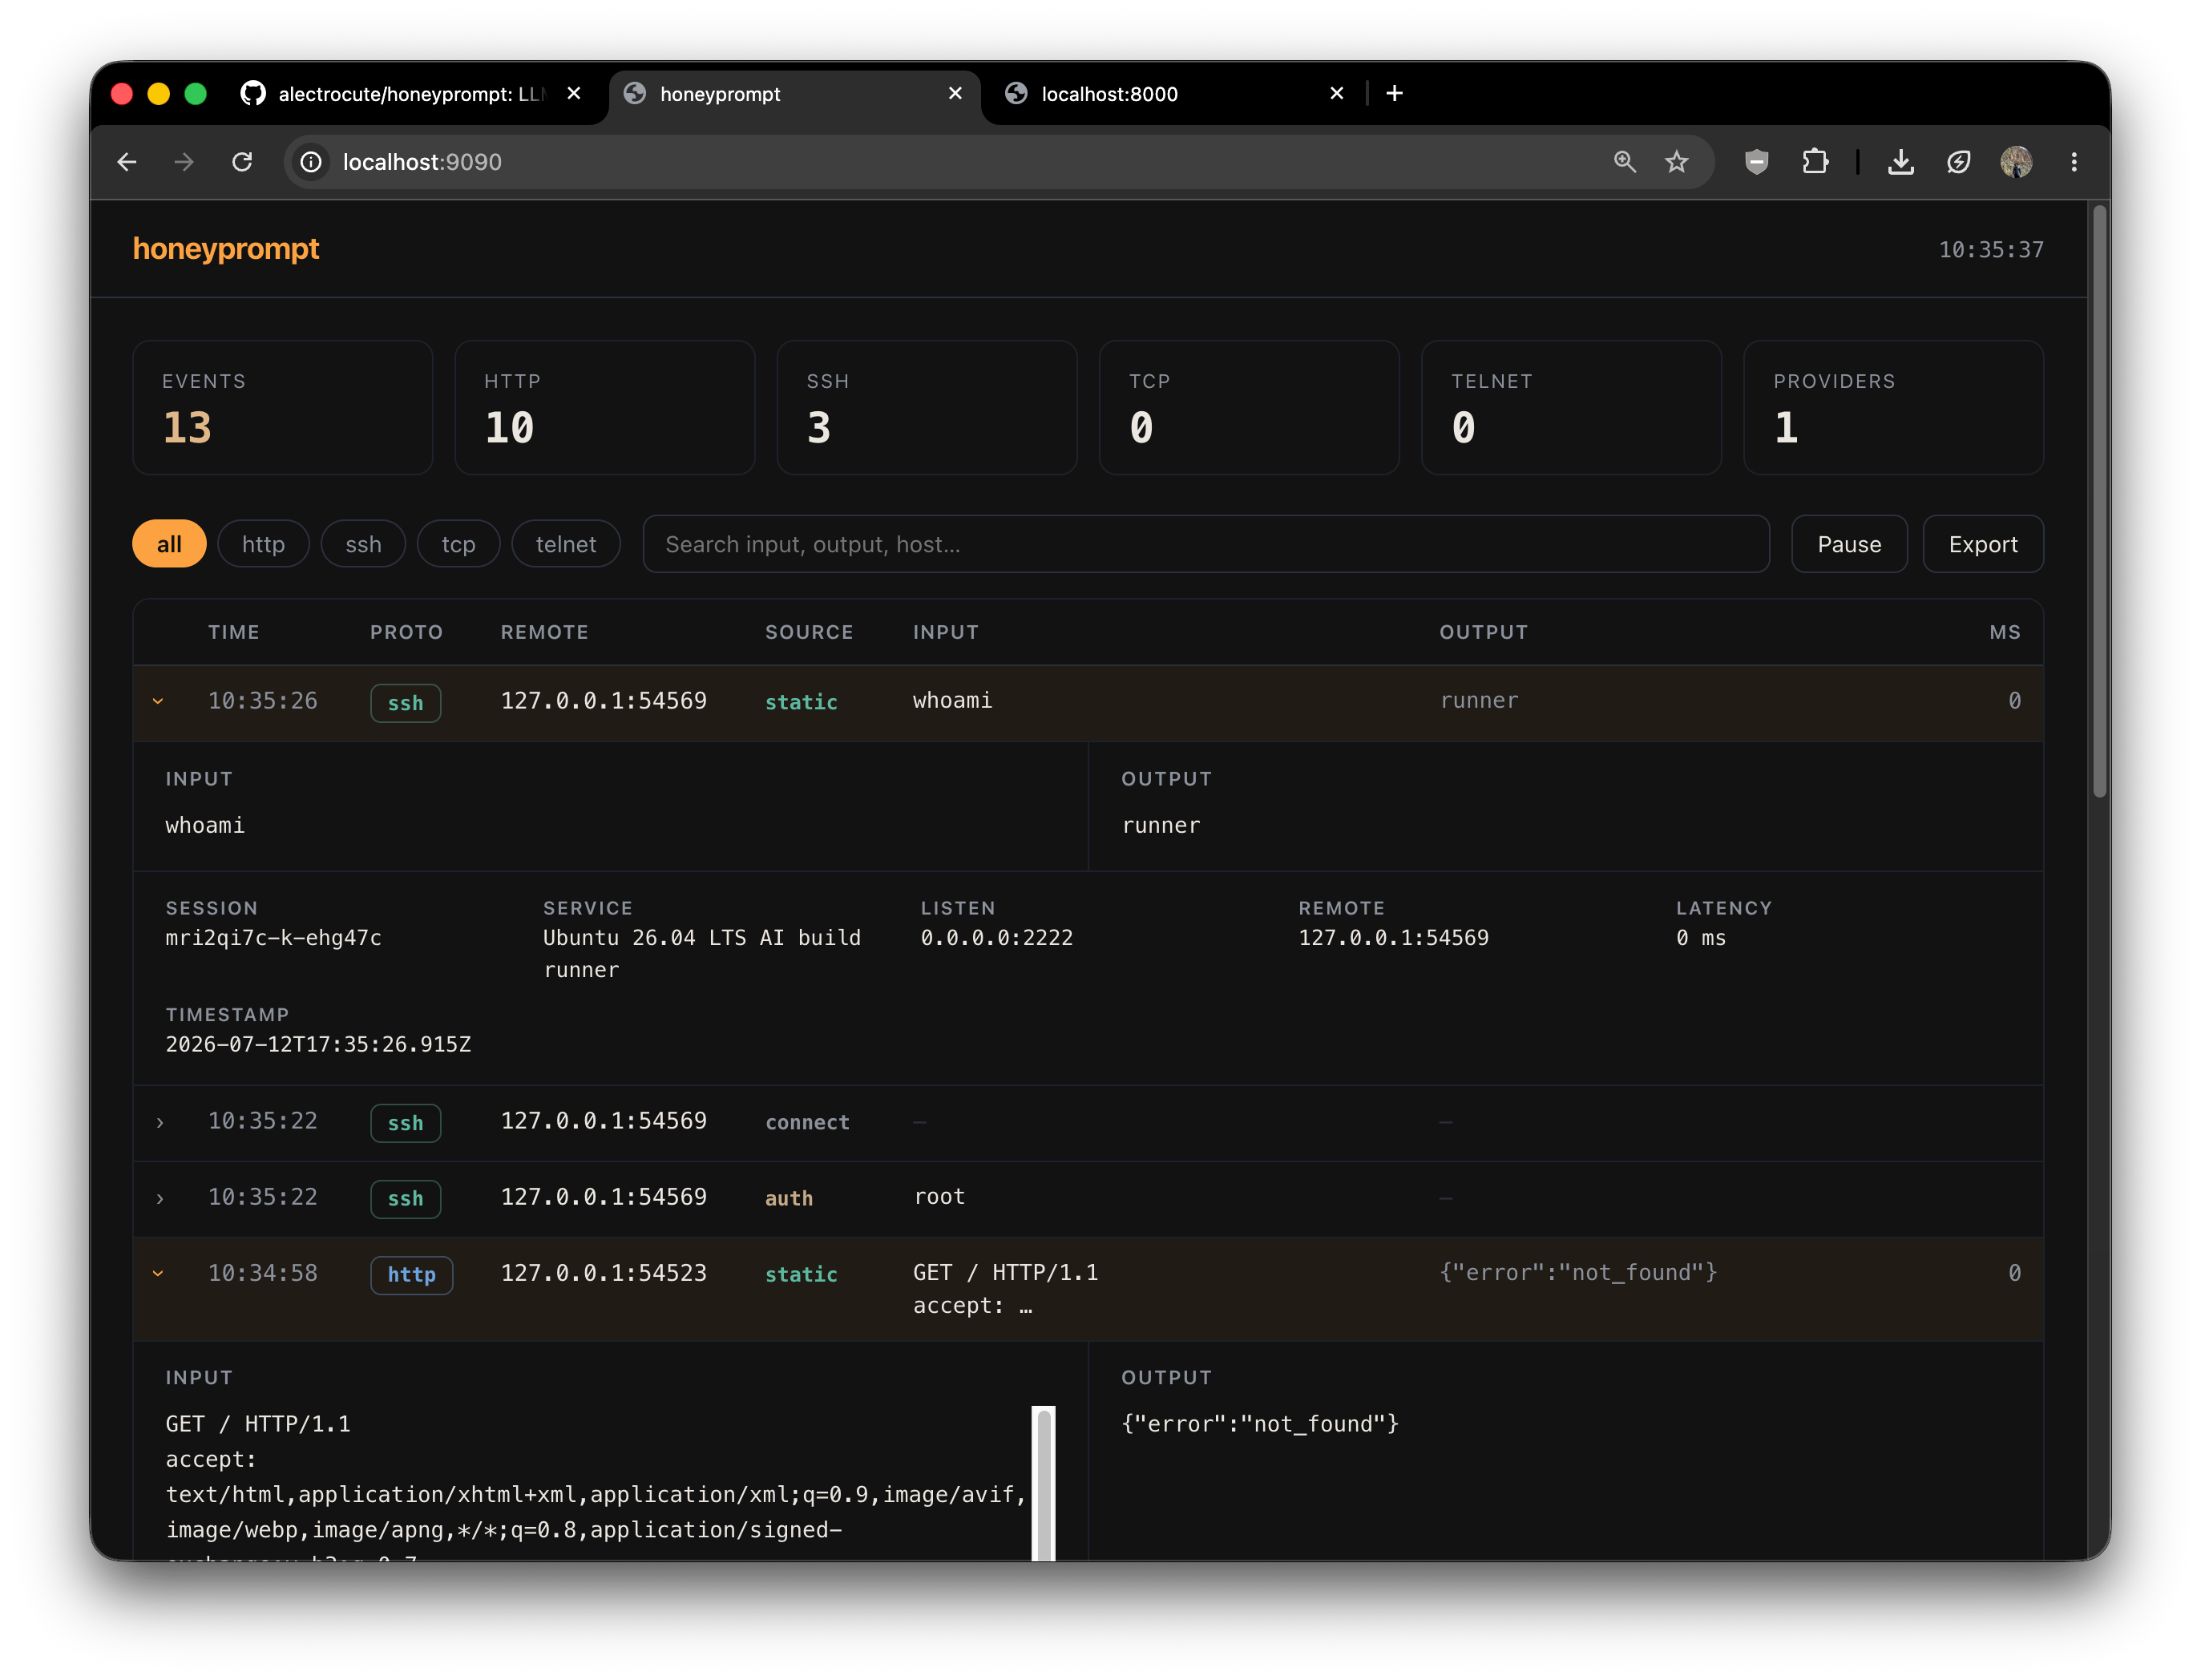
honeyprompt preview

honeyprompt

GitHubalectrocute/honeyprompt

LLM-first deception framework: "The honeypot that talks back!™"

ai-securitycontainer-securityincident-response+5
202 months ago
log4shell-poc-lab preview

log4shell-poc-lab

GitHubobscuritylabs/log4shell-poc-lab

A lab demonstration of the log4shell vulnerability: CVE-2021-44228

container-securityeducationexploitation+3
94 years ago
Previous1…567…22Next