

cve-2021-23369
 dinhvaren/cve-2021-23369
Proof-of-concept exploit for CVE-2021-23369, demonstrating a specific vulnerability in a JavaScript-based application.
exploitationvulnerability-analysisweb-security
dinhvaren/cve-2021-23369Proof-of-concept exploit for CVE-2021-23369, demonstrating a specific vulnerability in a JavaScript-based application.
 vulnerable-apps/log4shell-honeypot
Java application vulnerable to the CVE-2021-44228 (a.k.a log4shell) vulnerability
 cagataycali/hstp
Application-layer protocol framework for trust-based, end-to-end encrypted communication across heterogeneous networks, enabling uniform service…
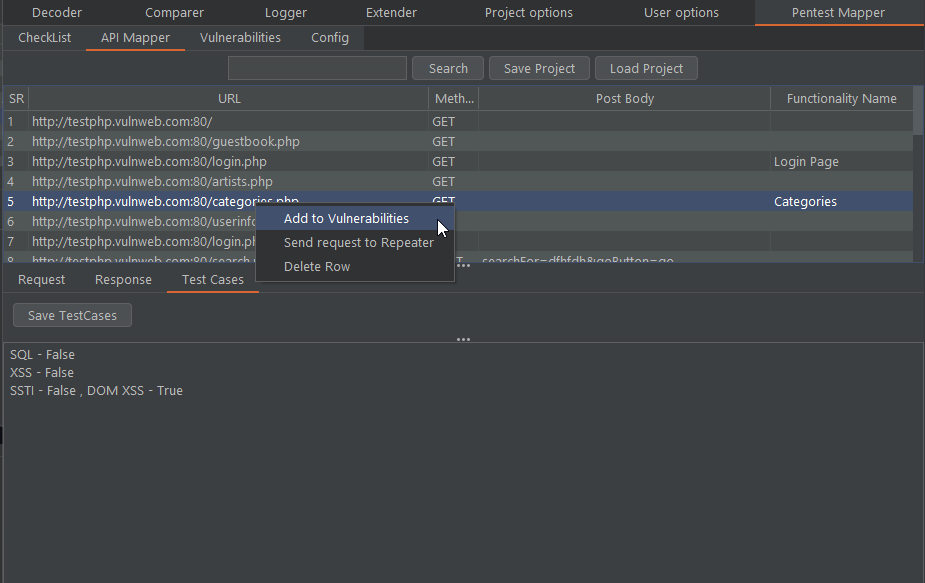 anof-cyber/pentest-mapper
A Burp Suite Extension for pentester and bug bounty hunters an to maintain checklist, map flows, write test cases and track vulnerabilities
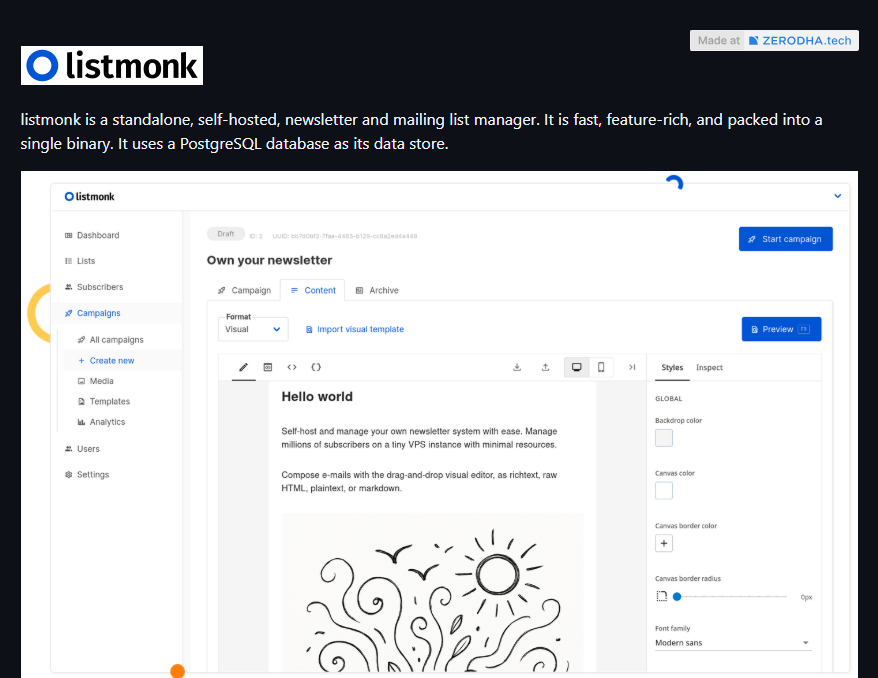 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
 jet-pentest/cve-2021-3130
Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 pwn0sec/pwnxss
PwnXSS: Vulnerability (XSS) scanner exploit
 gbrindisi/xsssniper
An automatic XSS discovery tool
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
 s3c-krd/s3cxsser
This extension will help you to detect GET/POST based XSS vulnerability in any website easily
 jenderal92/wordpress-default-password
python 2.7
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 paragonie/awesome-appsec
A curated list of resources for learning about application security
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 six2dez/wahh_extras
The Web Application Hacker's Handbook - Extra Content
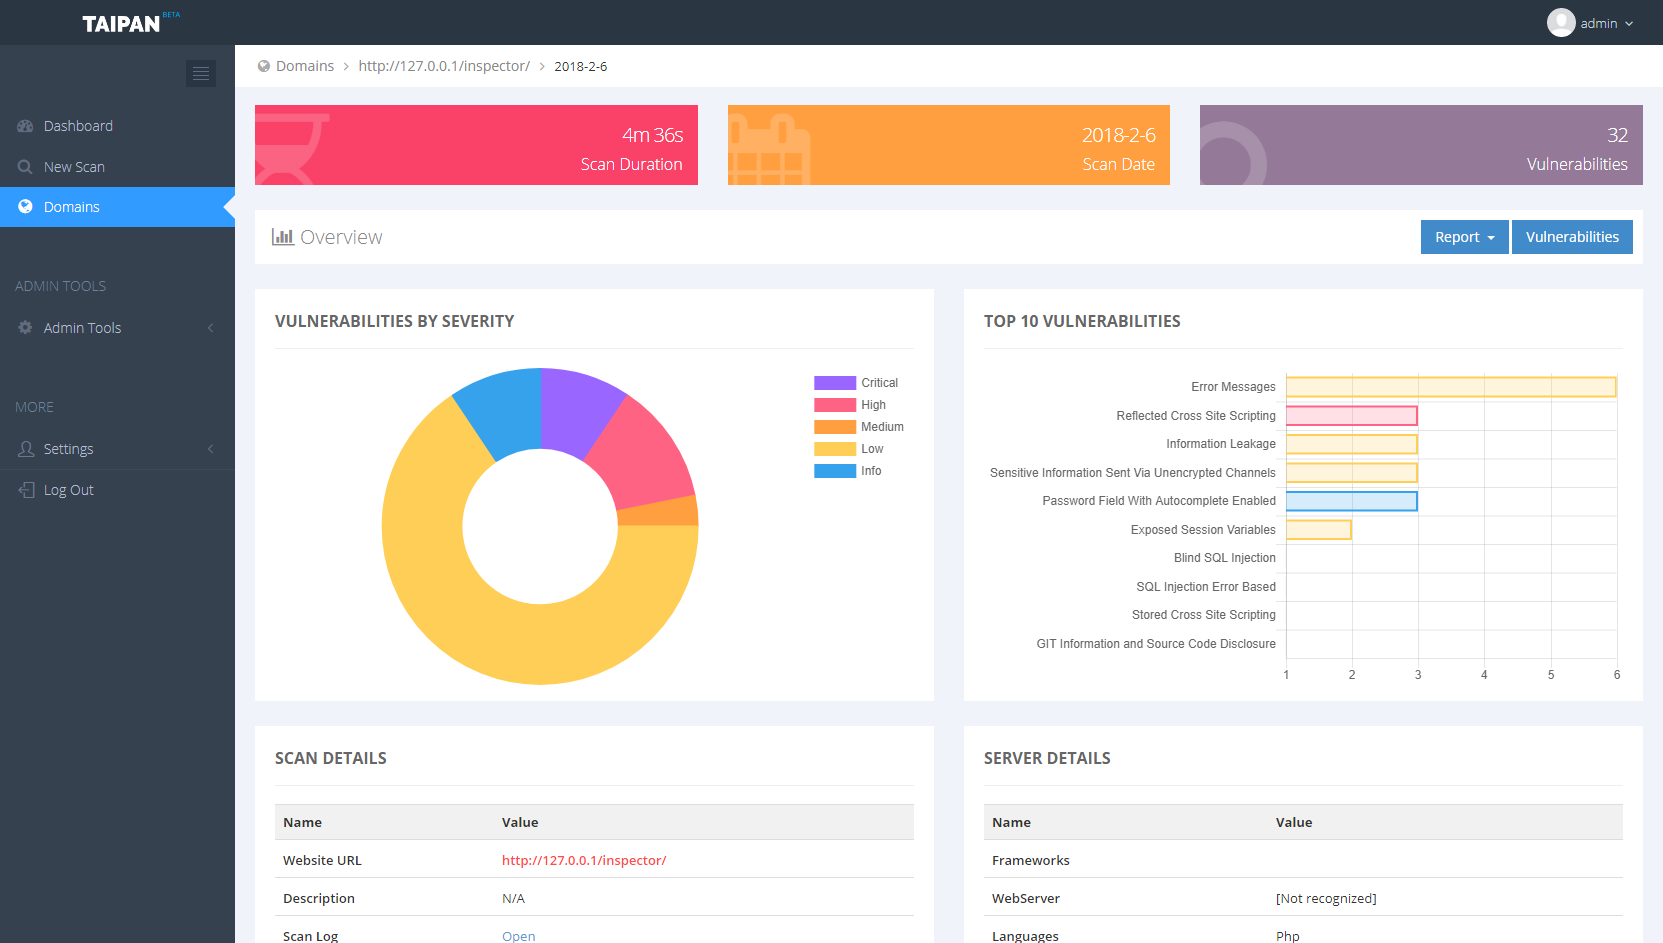 enkomio/taipan
Web application vulnerability scanner