
CVE-2026-0740
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
exploitationpayload-generationpenetration-testing+3
3
xshadow-here/cve-2026-0740Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 andsnw/sockjs-dos-py
CVE-2020-7693: SockJS 0.3.19 Denial of Service POC
 anomalousvectors/cve-2024-4367-poc
POC for PDF JS' CVE-2024-4367 vuln
 siunam321/cve-2024-8743-poc
Proof-of-Concept script for WordPress plugin Bit File Manager version <= 6.5.7 Authenticated (Subscriber+) Limited JavaScript File Upload…
 puvipavan/cve-2024-2667
This is POC for CVE-2024-2667 (InstaWP Connect – 1-click WP Staging & Migration <= 0.1.0.22 - Unauthenticated Arbitrary File Upload)
 nxploited/cve-2025-23922
WordPress iSpring Embedder plugin <= 1.0 - CSRF to Arbitrary File Upload vulnerability
 nxploited/cve-2024-6132
Pexels: Free Stock Photos <= 1.2.2 - Authenticated (Contributor+) Arbitrary File Upload
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
 netvanguard-cmd/cve-2026-27597
Exploit for CVE-2026-27597, a critical RCE in Agentfront Enclave before 2.11.1, allowing sandbox escape and remote code execution.
 xxconi/cve-2026-6960
Proof-of-concept exploit for CVE-2026-6960: unauthenticated arbitrary file upload in BookingPress Pro ≤ 5.6. Automates a 3-step chain to upload a PHP…
 ericardiansa/cve-2025-7847-poc
Wordpress Plugin AI Engine 2.9.3 - 2.9.4 Proof Of Concept
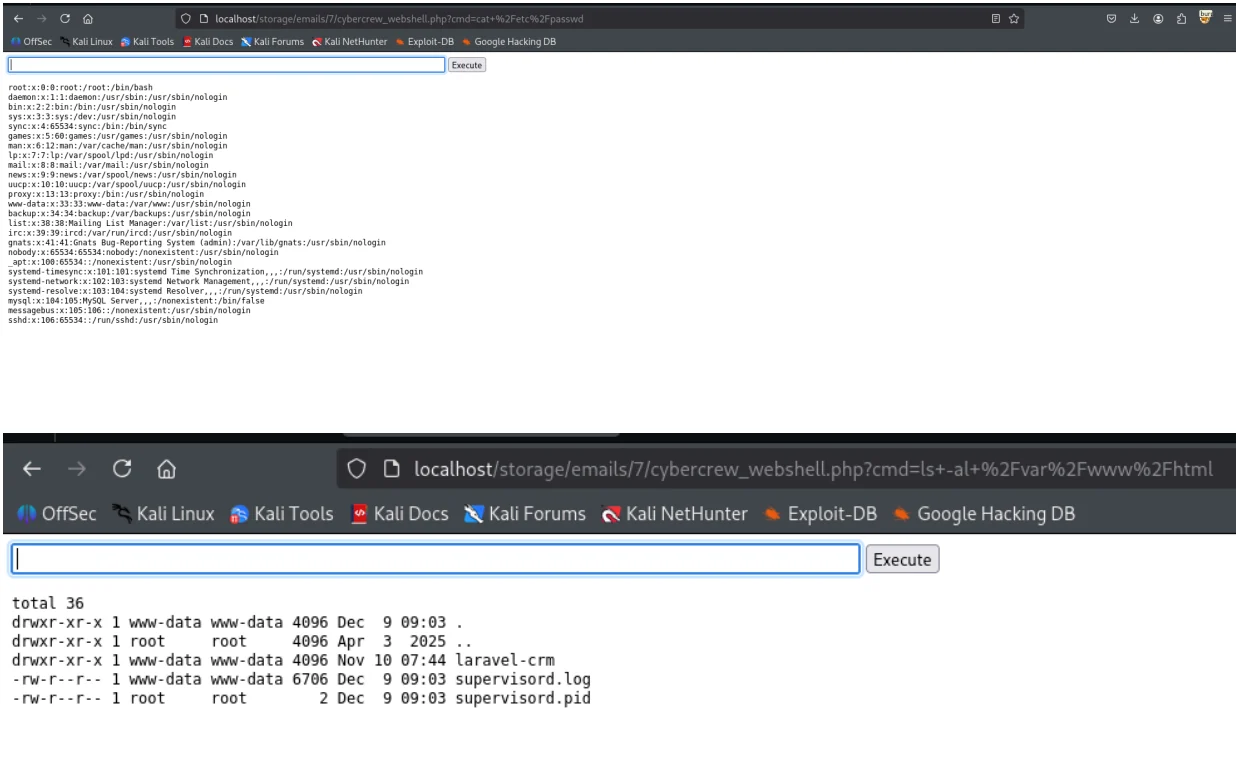 cybercrewinc/cve-2026-36340
Remote Code Execution (RCE) Vulnerability in Krayin CRM v2.1.5
 nxploited/cve-2024-56249
WordPress WPMasterToolKit plugin <= 1.13.1 - Arbitrary File Upload vulnerability
 xshadow-here/cve-2026-4882
User Registration Advanced Fields <= 1.6.20 - Unauthenticated Arbitrary File Upload
 0xabcd01/cve-2026-48866
CVE-2026-48866 — Gravity Forms <= 2.10.0.1 Arbitrary File Deletion via Path Traversal (CVSS 9.6)
 moften/cve-2019-20372
Nginx CVE-2019-20372 PoC, Unauthenticated File Upload Exploit
 professor6t9/cve-2025-3515
CVE‑2025‑3515 — Drag and Drop Multiple File Upload for Contact Form 7
 aljoharasubaie/cve-2025-57460
File upload vulnerability in machsol machpanel 8 allows attacker gain a webshell.