WordPress--CVE-2022-21661

Proof-of-concept exploit for CVE-2022-21661, a SQL injection vulnerability in WordPress Core WP_Query, demonstrating the attack and providing…

Proof-of-concept exploit for CVE-2022-21661, a SQL injection vulnerability in WordPress Core WP_Query, demonstrating the attack and providing…

Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager, enabling SSH key injection…

CVE-2022-24227 [Updated]: BoltWire v8.00 vulnerable to "Stored Cross-site Scripting (XSS)"

A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.

Python script to detect unauthenticated blind SSRF (CVE-2022-3590) in WordPress pingback feature. Supports single URL and batch scanning with…

CVE-2022-37208

POC firewall with rules designed to detect and block Spring4Shell vulnerability (CVE-2022-22965) exploit

CVE-2022-3689

Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…

Nmap scripts to detect exchange 0-day (CVE-2022-41082) vulnerability

Grow by Tradedoubler < 2.0.22 - Unauthenticated LFI

A PoC for the CVE-2022-44268 - ImageMagick arbitrary file read

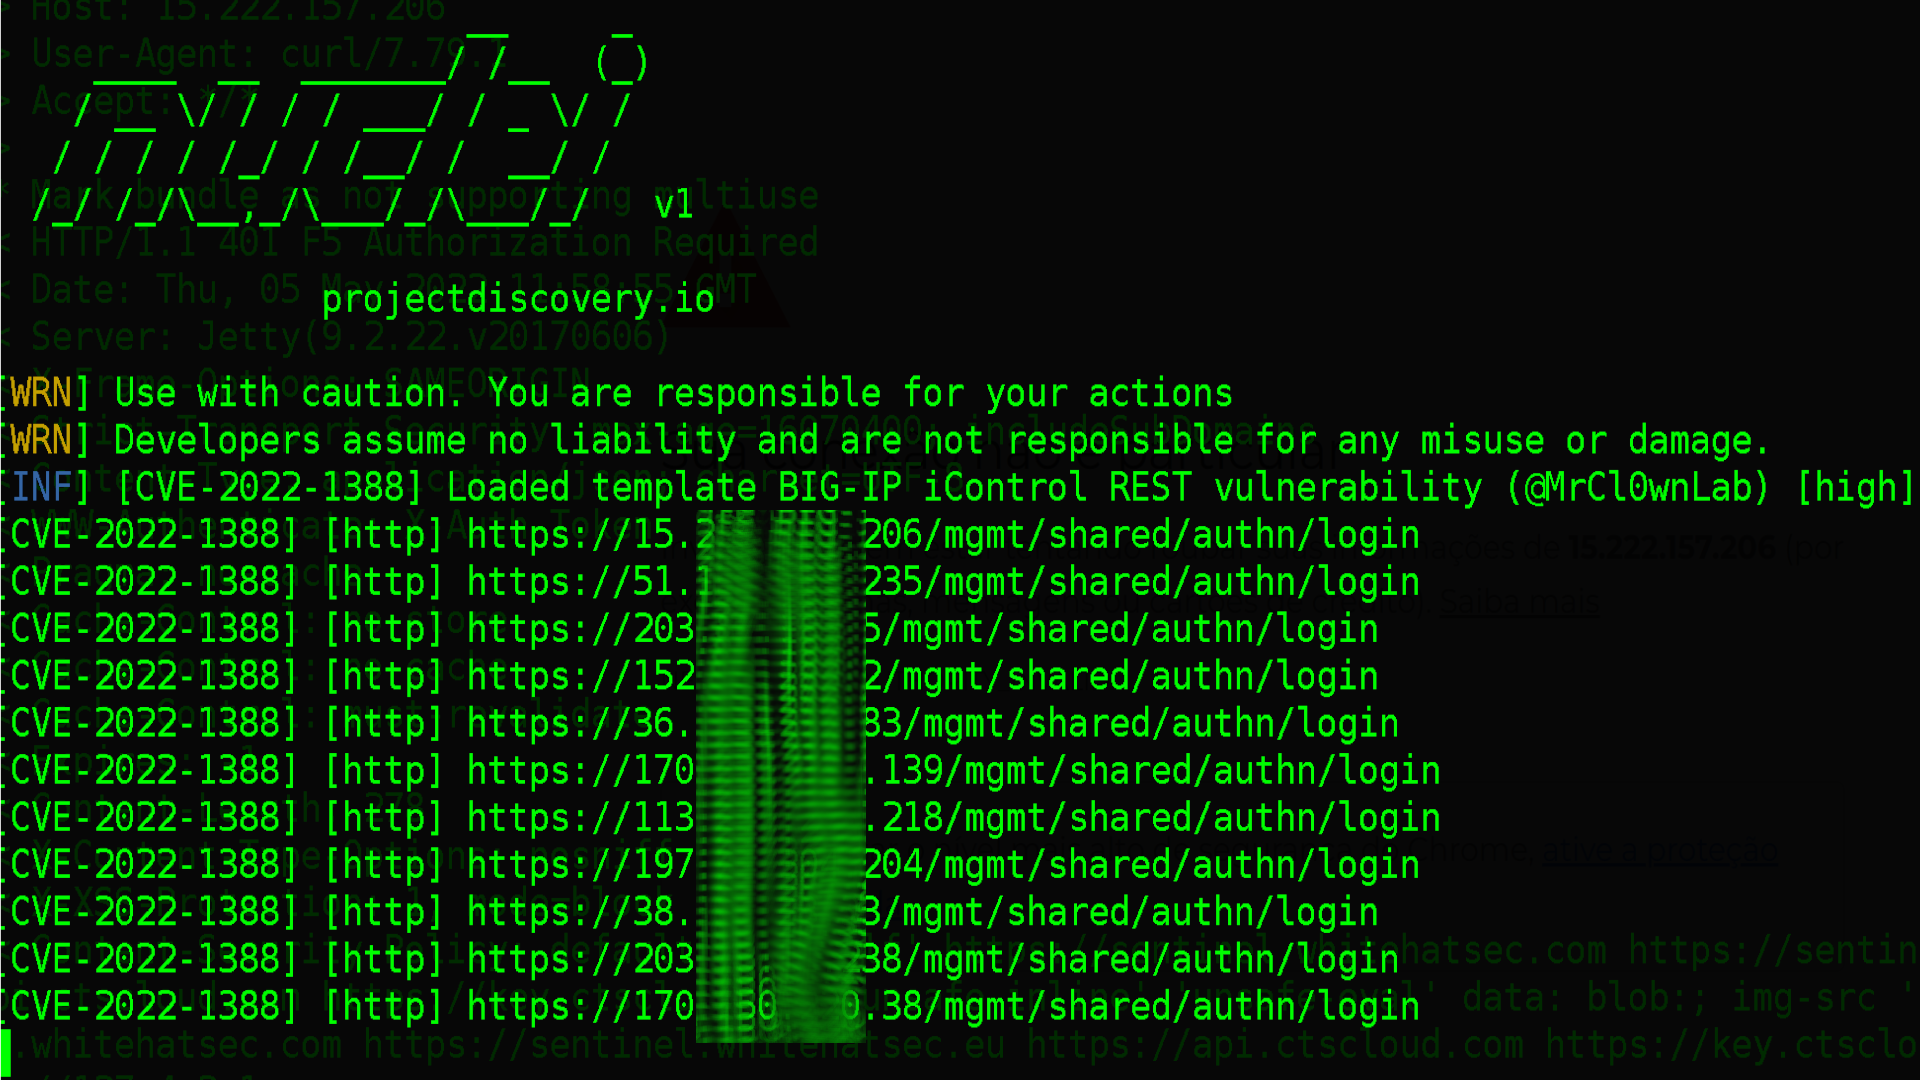
This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…

Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.

仅仅是poc,并不是exp

CVE-2022-40348: Intern Record System - 'name' and 'email' Cross-site Scripting (Unauthenticated)


The RRS v500 application is vulnerable to a reflected Cross-Site Scripting (XSS) vulnerability.