
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
248 results
rengine preview

rengine

GitHubyogeshojha/rengine

reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
crawlerdns-subdomain-enumerationinformation-gathering+9
8.8k
11 months ago
JWTweak preview

JWTweak

GitHubrishuranjanofficial/jwtweak

Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.
authenticationcryptographypayload-generation+3
1034 months ago
CVE-2026-8347 preview

CVE-2026-8347

GitHubaj2108/cve-2026-8347

CVE-2026-8347 is an Insecure Direct Object Reference (IDOR) combined with a wrong authorization level vulnerability in Concrete CMS versions 9.5.0…

authentication-authorizationvulnerability-analysisweb-application-exploitation+1
3 months ago
CVE-2025-44148 preview

CVE-2025-44148

GitHubbarisbaydur/cve-2025-44148

A reflected cross-site scripting (XSS) vulnerability exists in MailEnable Webmail due to improper user input sanitization in the failure.aspx. This…

exploitationpenetration-testingvulnerability-analysis+2
31 year ago
CVE-2025-54321 preview

CVE-2025-54321

GitHubsaykino/cve-2025-54321

Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…

curated-resourceseducationmisconfiguration+2
11 months ago
CVE-2025-22963 preview

CVE-2025-22963

GitHubsamplev45/cve-2025-22963

Detailed disclosure of CVE-2025-22963, a CSRF vulnerability in Teedy <= v1.11 enabling account takeover via forced user information changes.

educationpapers-researchvulnerability-analysis+2
1 year ago
scenester preview

scenester

GitHubnccgroup/scenester

A tool to visually snapshot a website by supplying multiple user-agent. Designed to aid in discovery of different entry points into an application.
information-gatheringosintpenetration-testing+2
3110 years ago
CVE-2026-25050 preview

CVE-2026-25050

GitHubchristbowel/cve-2026-25050

Proof-of-concept exploit for CVE-2026-25050, a timing attack enabling user enumeration via GraphQL authentication. Measures response times to…
authenticationexploitationinformation-gathering+2
29 months ago
resiprocate preview

resiprocate

GitHubresiprocate/resiprocate

C++ implementation of SIP, ICE, TURN and related protocols.
cloud-securityencryption-decryption-toolsiot-security+3
79121h 7m ago
ReconNote preview

ReconNote

GitHub0xdekster/reconnote

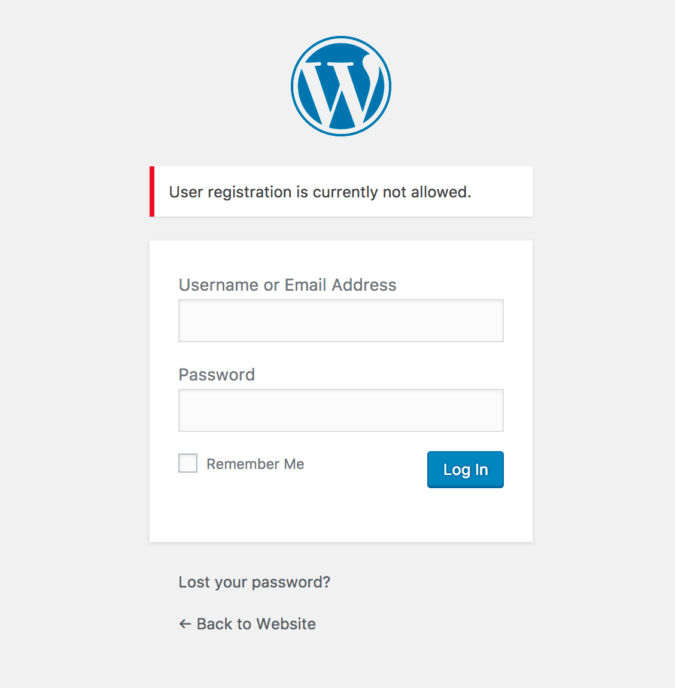
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
information-gatheringpenetration-testingreconnaissance+3
4115 years ago
setup-wordpress-with-security-best-practice preview

setup-wordpress-with-security-best-practice

GitHubpassword123456/setup-wordpress-with-security-best-practice

Comprehensive guide for hardening WordPress installations: covers admin user changes, HTTPS enforcement, plugin security, file permissions, and…
configuration-auditingeducationweb-security
292 years ago
php2shell-check preview

php2shell-check

GitHubbrentmartinmiller/php2shell-check

Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
configuration-auditingdefensive-toolsdigital-forensics+6
68 days ago
CVE-2026-13355 preview

CVE-2026-13355

GitHubmurrez/cve-2026-13355

Python PoC scanner and exploit for CVE-2026-13355, an unauthenticated admin privilege escalation in Meta Box AIO WordPress plugins, with FOFA mass…
exploitationinformation-gatheringpenetration-testing+6
1 month ago
CVE-2021-29447-PoC preview

CVE-2021-29447-PoC

GitHub0xrar/cve-2021-29447-poc

A proof of concept exploit for a wordpress 5.6 media library vulnerability
exploitationpenetration-testingvulnerability-analysis+2
63 years ago
CVE-2021-24750 preview

CVE-2021-24750

GitHubfimtow/cve-2021-24750

Demonstration of the WP Visitor Statistics plugin exploit
exploitationpenetration-testingvulnerability-analysis+2
14 years ago
CVE-2025-45805 preview

CVE-2025-45805

GitHubmohammed-alsaqqaf/cve-2025-45805

PoC of CVE-2025-45805

exploitationpenetration-testingvulnerability-analysis+2
10 months ago
CVE-2025-9816 preview

CVE-2025-9816

GitHubmonzaviman/cve-2025-9816

Proof of Concept for Stored-XSS on Vulnerable WP-Statistics Plugin known as CVE-2025-9816
exploitationpayload-generationpenetration-testing+3
11 months ago
nahsra__antisamy_CVE-2016-10006_1-5-3 preview

nahsra__antisamy_CVE-2016-10006_1-5-3

GitHubshoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3

Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…

api-securitycode-analysisdefensive-tools+2
1 year ago
Previous1…345…14Next