
CTFTiny
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
ai-securitybinary-exploitationcryptography+8
nyu-llm-ctf/ctftinyOfficial repository for CTFTiny
 star-sg/challenges
Christmas-themed CTF Advent Calendar with 12 structured challenges across binary exploitation, cryptography, reverse engineering, forensics, OSINT,…
 rkx1209/cve-2014-1303
CVE-2014-1303 (WebKit Heap based BOF) proof of concept for Linux
 ntfargo/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 r3dxpl0it/rtspserver-code-execution-vulnerability
RTSPServer Code Execution Vulnerability CVE-2018-4013
 losfuzzys/glacierctf2023_writeups
Curated CTF writeup collection for GlacierCTF 2023 covering pwn, rev, web, crypto, and smart contract challenges with solutions and educational…
 muhammednihalmp/google-chrome-zero-day
CVE-2025-6554
 fatmo666/cve-2023-38545-libcurl-socks5-heap-buffer-overflow
Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 crihexe/v8-poc-cve-2026-5865
Minimal JavaScript proof-of-concept for V8 engine vulnerability CVE-2026-5865, with scripts to patch and calibrate the exploit for d8.
 krispybyte/cve-2025-55763
Heap overflow PoC for CivetWeb CVE-2025-55763
 zha0gongz1/cve-2021-31166
PoC for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely. Although it was defined as remote command execution, it can only cause…
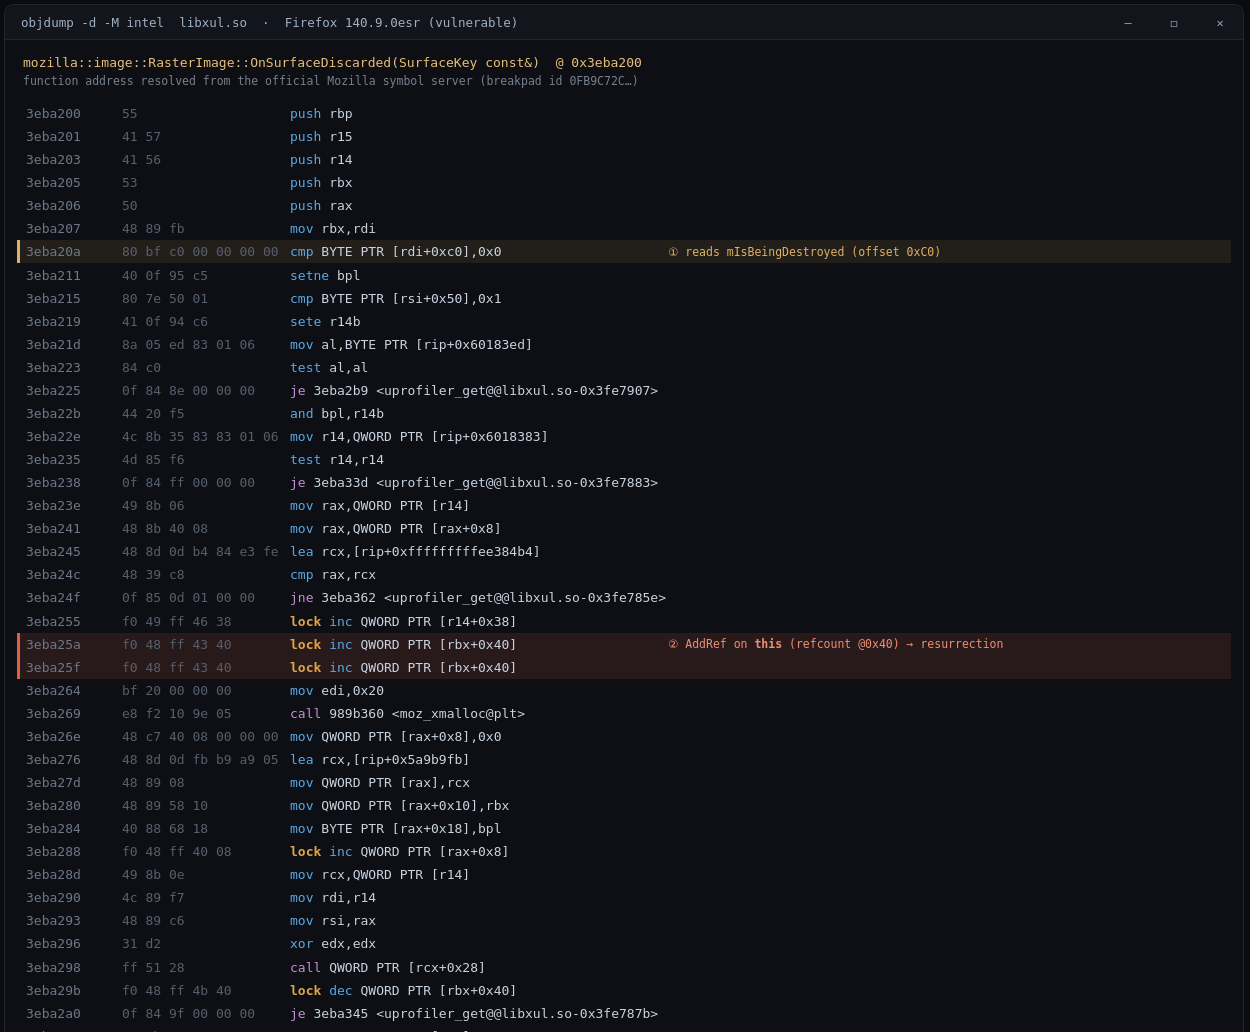 defineid/revenant
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
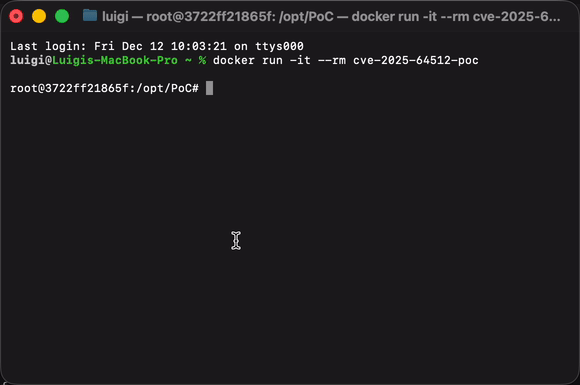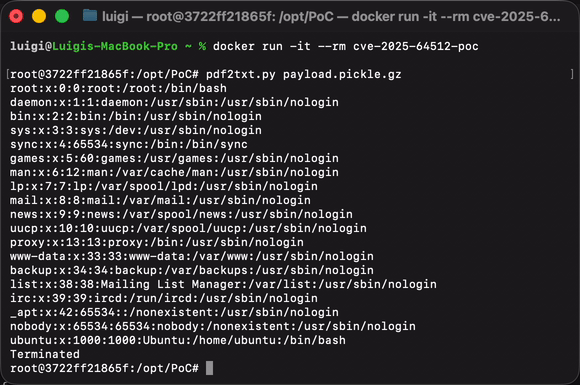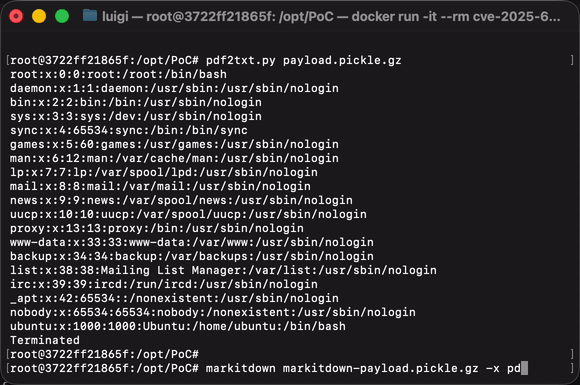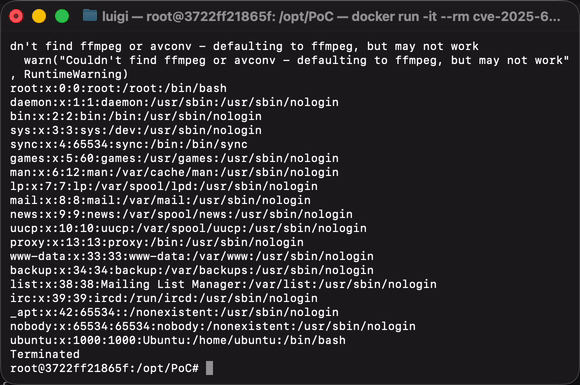 luigigubello/cve-2025-64512-polyglot-poc
A Proof-of-Concept for CVE-2025-64512 using a polyglot file.
 the-maxu/cve-2025-24201-webkit-vulnerability-detector-poc-
CVE-2025-24201 WebKit Vulnerability Detector (PoC)
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 brahmstaedt/libxml2-exploit
An example exploit for CVE-2017-7376
 w0lfzhang/sonicwall-cve-2019-7482
Exploit for SonicWall CVE-2019-7482 stack-based buffer overflow vulnerability, enabling remote code execution on affected firewall appliances.