
CVE-2020-0601_PoC
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
code-analysiscryptographyexploitation+3
joelbts/cve-2020-0601_pocDemonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 sahar042/cve-2024-1207
The WP Booking Calendar plugin for WordPress is vulnerable to SQL Injection via the 'calendar_request_params[dates_ddmmyy_csv]' parameter in all…
 jjk96/javaclasspathenum
Java classpath enumeration, focussed on CVE-2014-0043 for Apache Wicket 6.x
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript

 ghostinexile/cve-2026-63030-wp2shell
WordPress REST API SQLi to RCE PoC (CVE-2026-63030 & CVE-2026-60137)
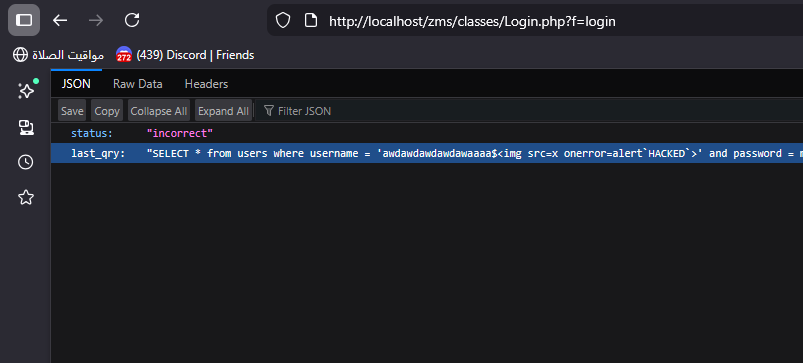 mmakingdom/cve-2025-65881
Sourcecodester Zoo Management System v1.0 is vulnerable to Cross Site Scripting (XSS) in /classes/Login.php Due to invalid Content-Type
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 feliam/cve-2014-4377
Exploit for Apple CoreGraphics heap overflow (CVE-2014-4377) enabling arbitrary code execution on iOS 7.1.x via crafted PDF used as HTML image.
 w0lfzhang/sonicwall-cve-2019-7482
Exploit for SonicWall CVE-2019-7482 stack-based buffer overflow vulnerability, enabling remote code execution on affected firewall appliances.
 xxconi/cve-2026-6960
Proof-of-concept exploit for CVE-2026-6960: unauthenticated arbitrary file upload in BookingPress Pro ≤ 5.6. Automates a 3-step chain to upload a PHP…
 andres101c/shellshock-cve-2014-6271
Exploit for CVE-2014-6271 (Shellshock) targeting Bash environment variable injection to achieve remote code execution on vulnerable systems.
 thickcoco/cve-2023-27163-poc
Poc of SSRF for Request-Baskets (CVE-2023-27163)
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.