
BruteXSS
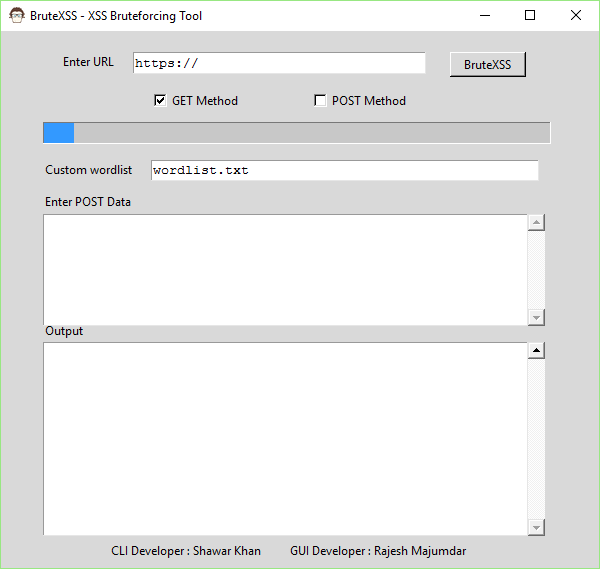
BruteXSS is a tool written in python simply to find XSS vulnerabilities in web application. This tool was originally developed by Shawar Khan in CLI.…

HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…

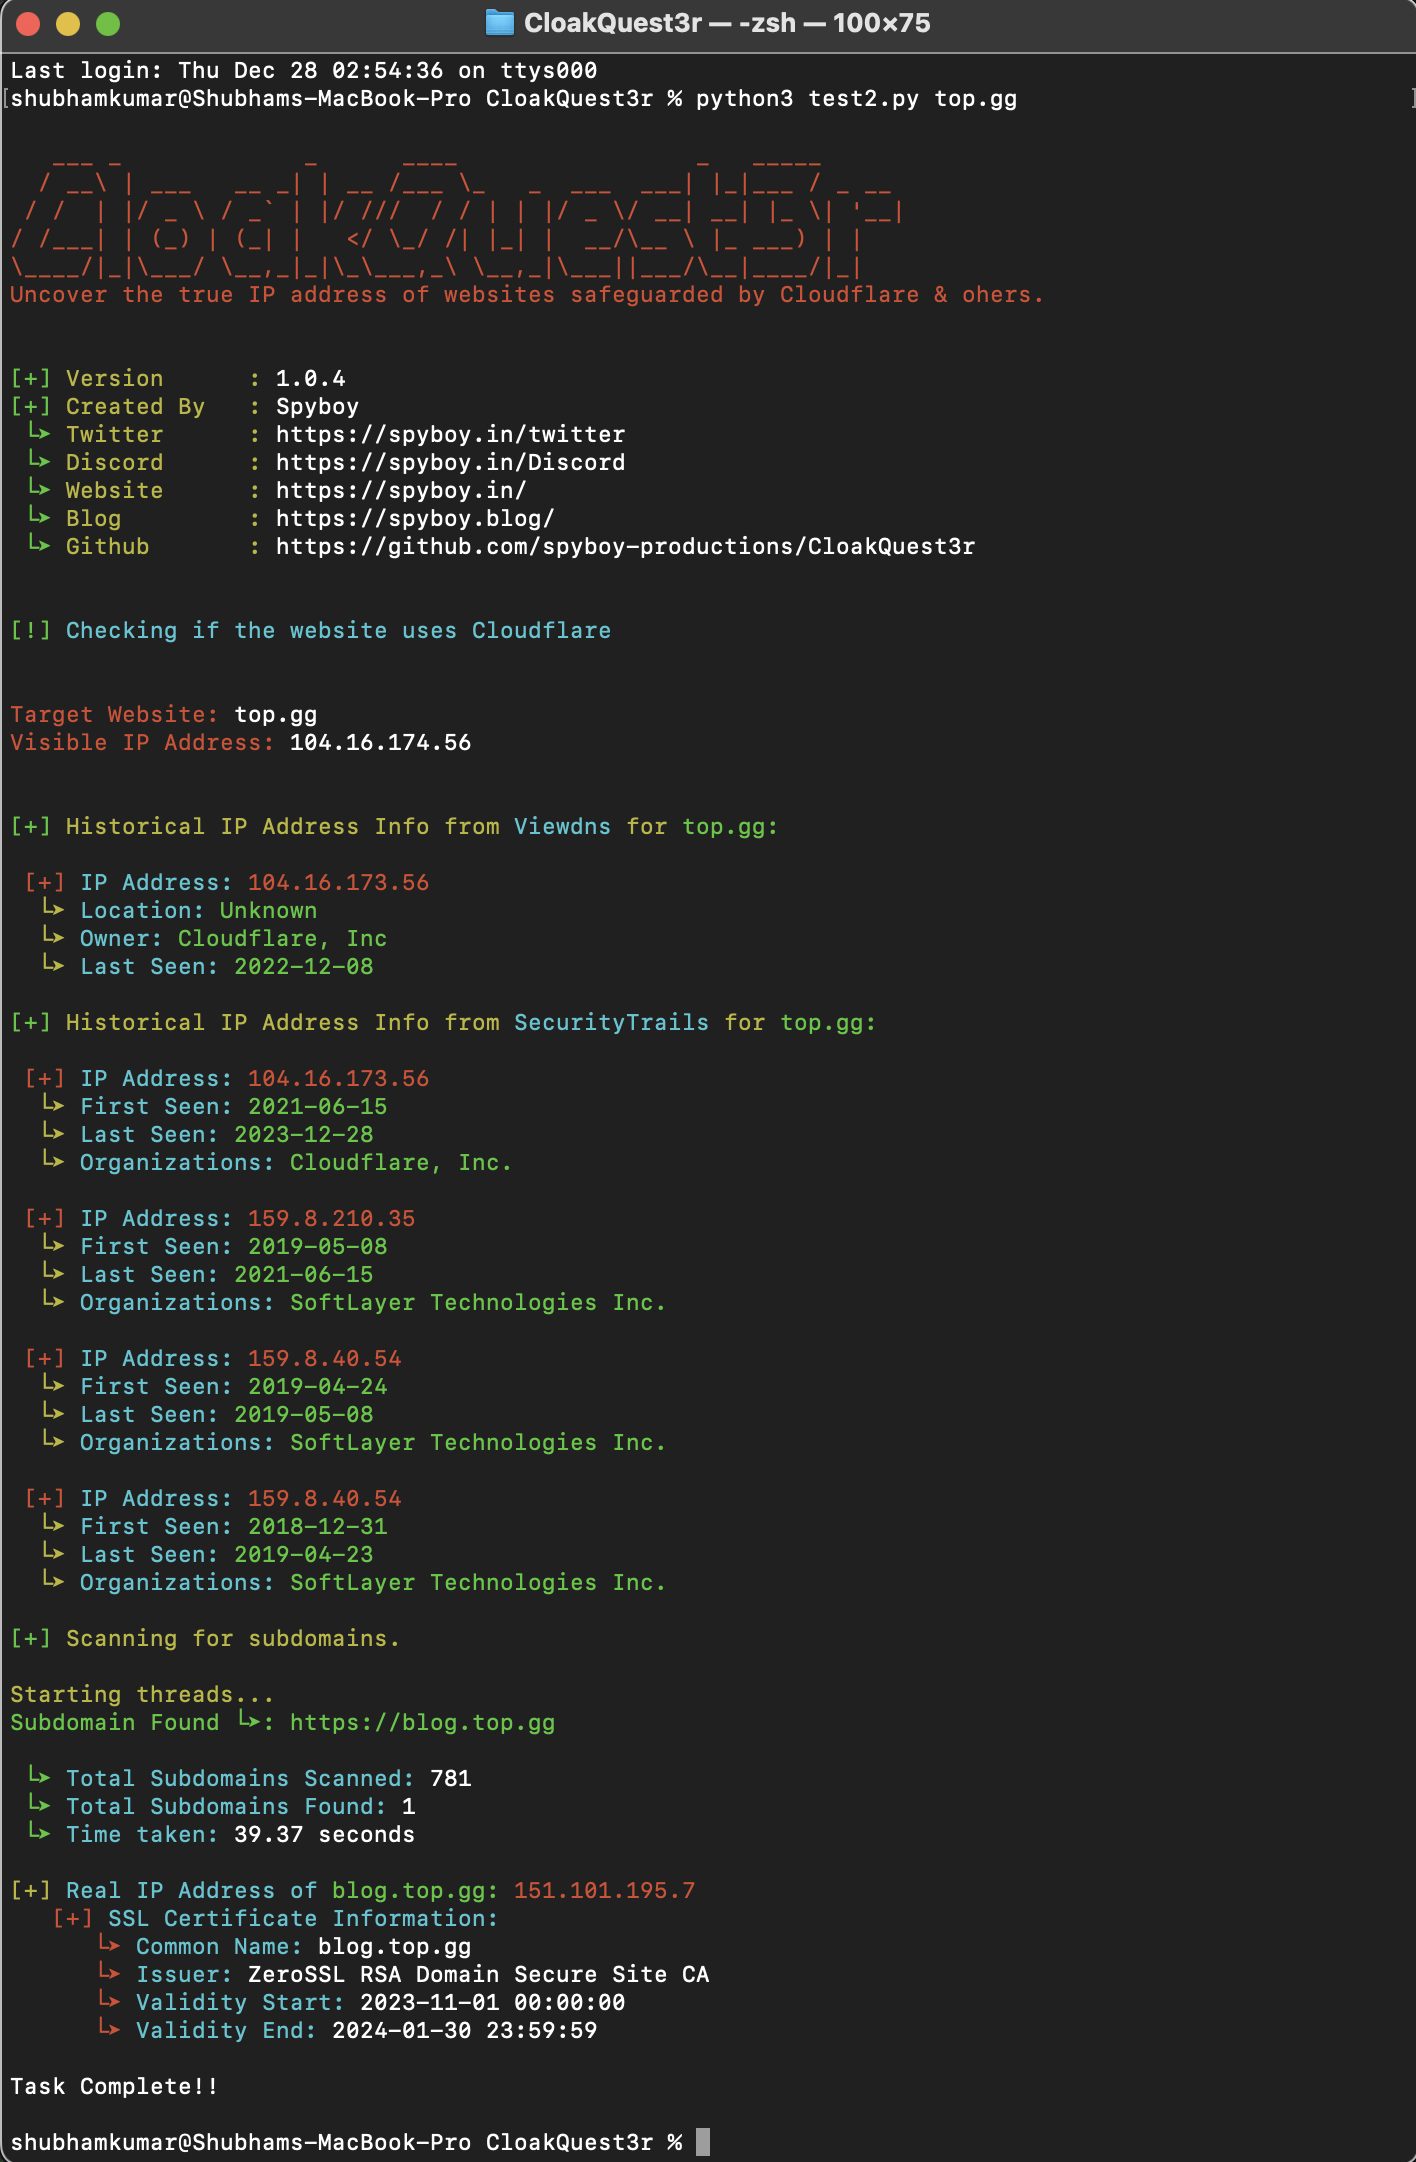
Open-source security research tool for identifying origin IP exposure of websites protected by Cloudflare and similar reverse proxy services.

An advanced multithreaded admin panel finder written in python.

A python tool used to discover endpoints, potential parameters, a target specific wordlist for a given target and secrets

Automatically Launch Google Hacking Queries Against A Target Domain

Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…

OSINT Tool For Scraping Dark Websites

Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.

A simple CORS misconfiguration scanner

Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…

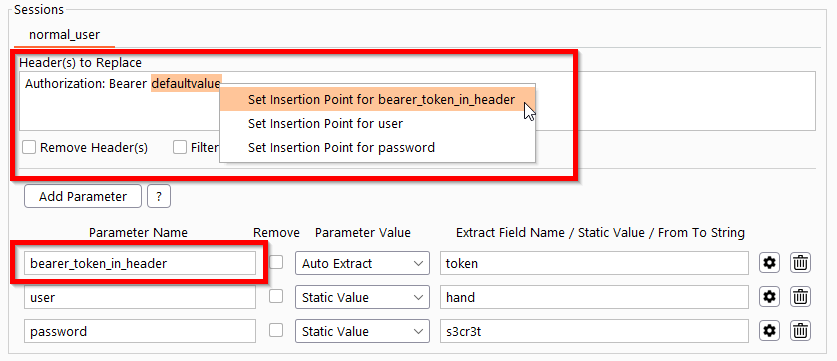
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.

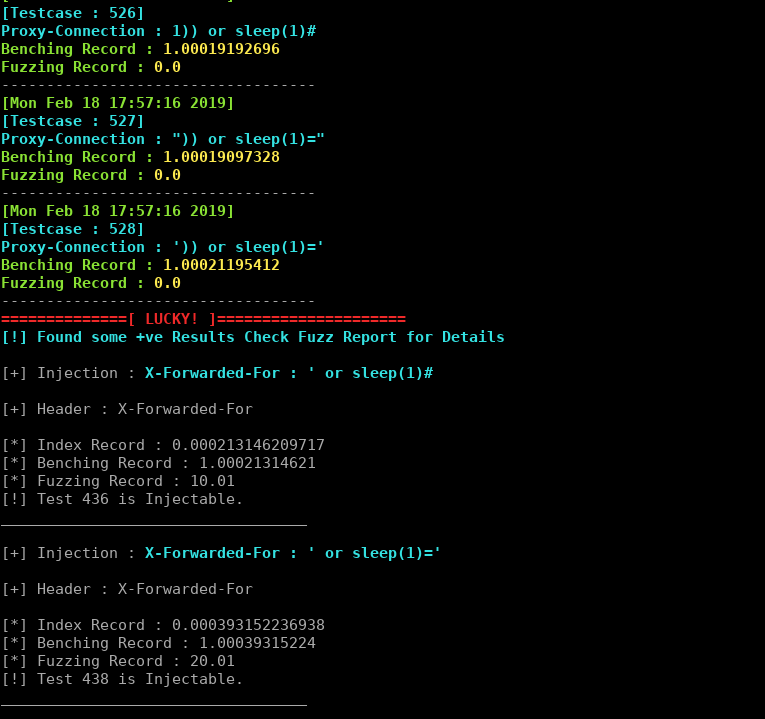
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).

Python script to discover admin panel URLs of websites, aiding in security reconnaissance and penetration testing.

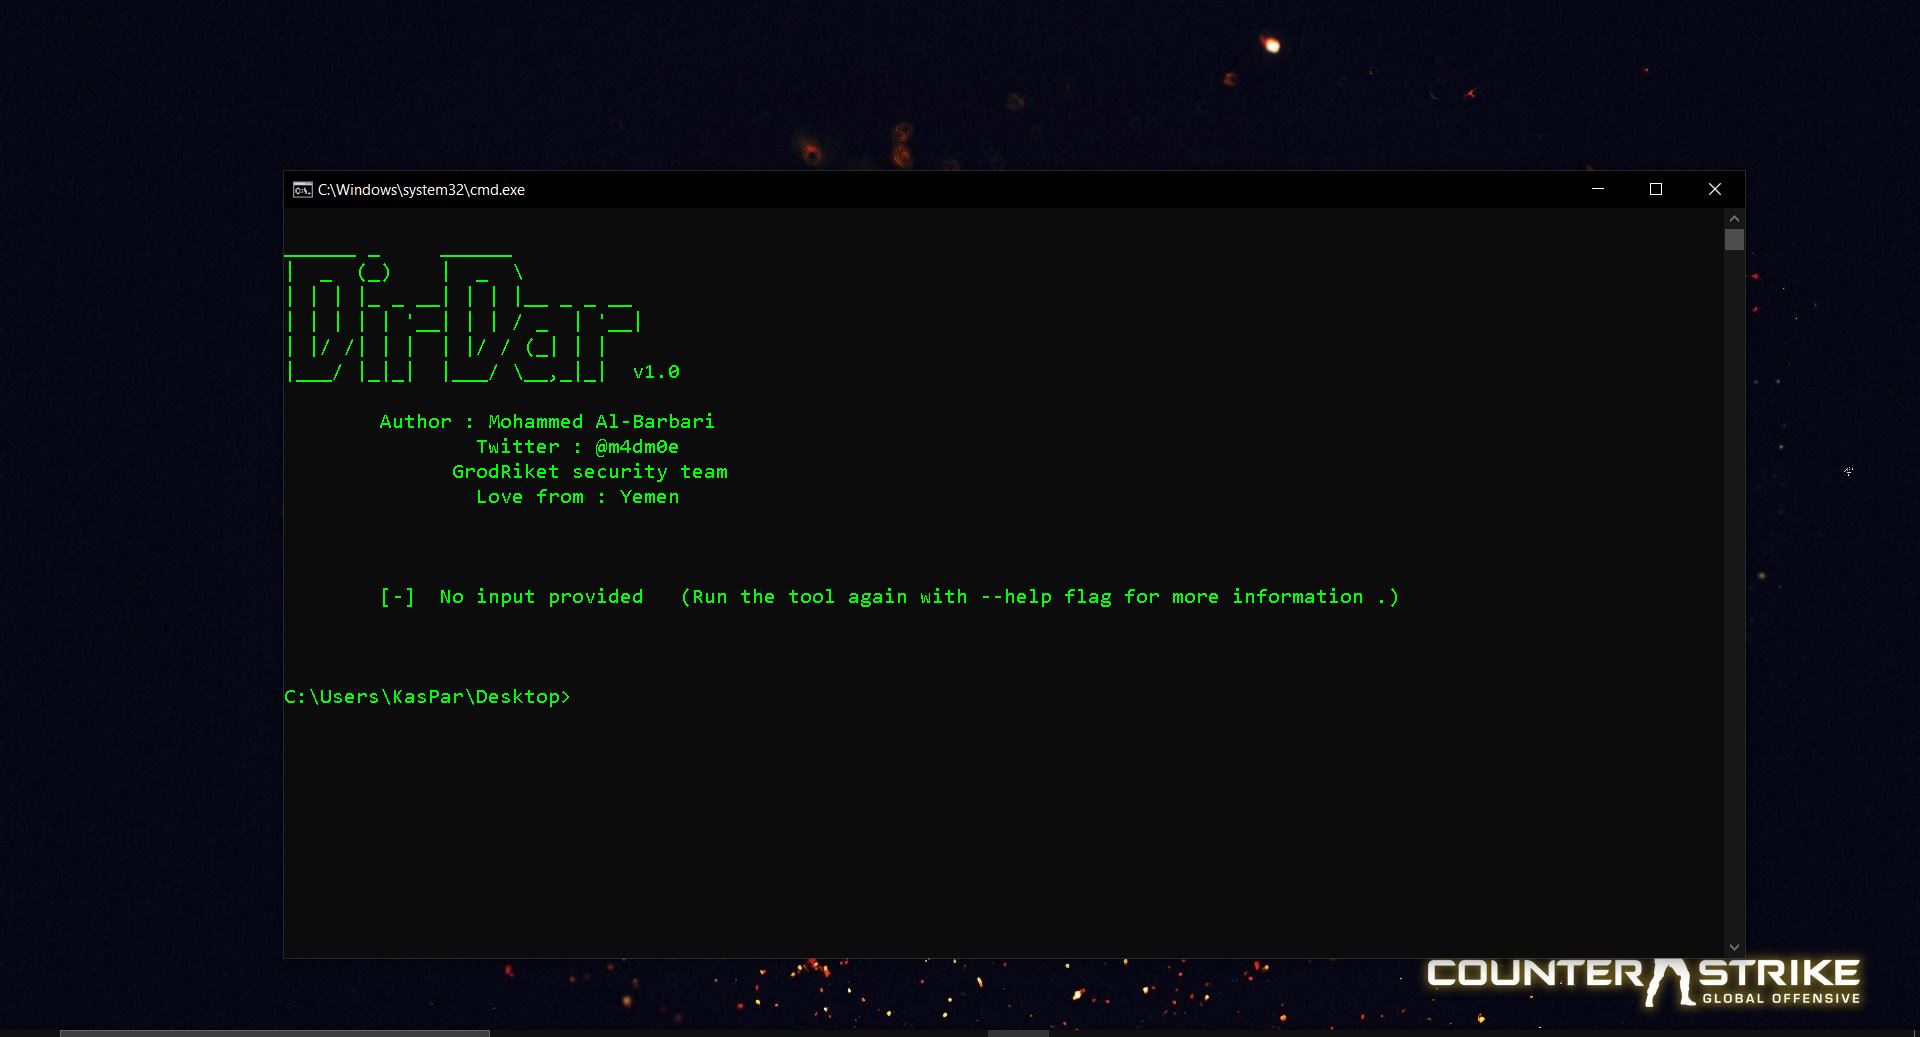
DirDar is a tool that searches for (403-Forbidden) directories to break it and get dir listing on it

You can read the writeup on this script here

Tool designed for fetching, validating, and storing working proxies.

Web Application Vulnerability Scanner