
wstg
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
educationlearning-paths-coursespenetration-testing+2
9.8k
owasp/wstgThe Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 digininja/dvwa
Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…
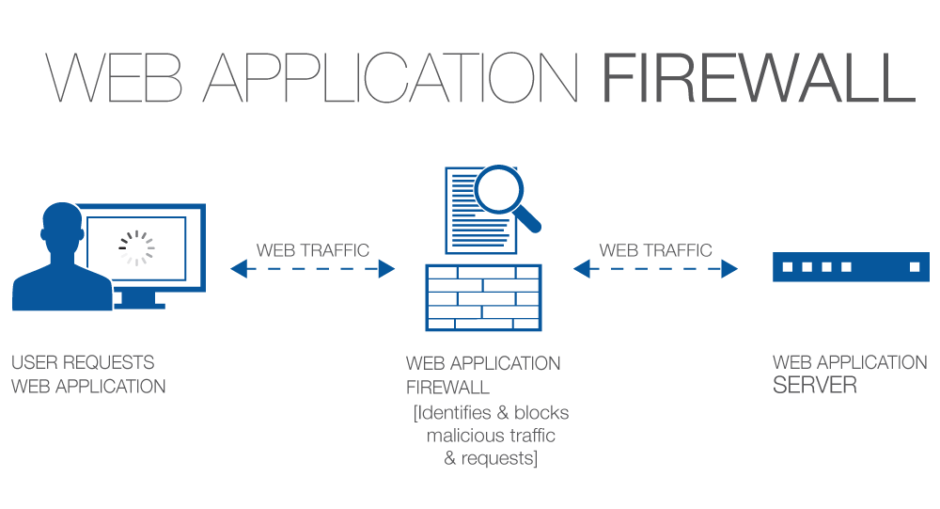 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥

 mbrandner-group/webgoat.net
Deliberately vulnerable .NET web application for learning common web security flaws through hands-on exercises covering XSS, SQL injection, and other…
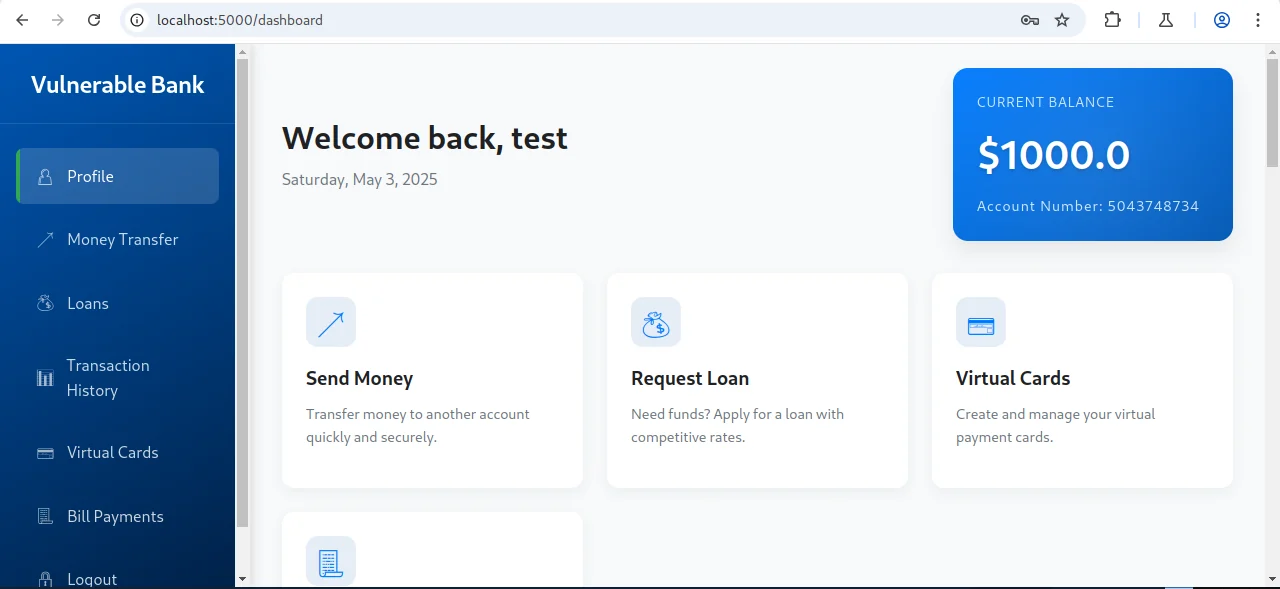 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 z3n70/cve-2023-23752
simple program for joomla CVE-2023-23752 scanner for pentesting and educational purpose
 iamarit/cve-2024-10858
Proof-of-concept exploit for CVE-2024-10858 targeting a vulnerable WordPress Jetpack plugin. Demonstrates exploitation of a security flaw in a…
 mr-n0b3dy/cve-2023-42362
Proof-of-concept exploit for CVE-2023-42362: unrestricted file upload leading to stored XSS and admin account takeover in NCR Teller web app 4.4.0.
 ramadhanamizudin/lazyweb
LazyWeb is a demonstration web application designed to showcase common server-side application vulnerabilities. Each vulnerability is categorized…
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
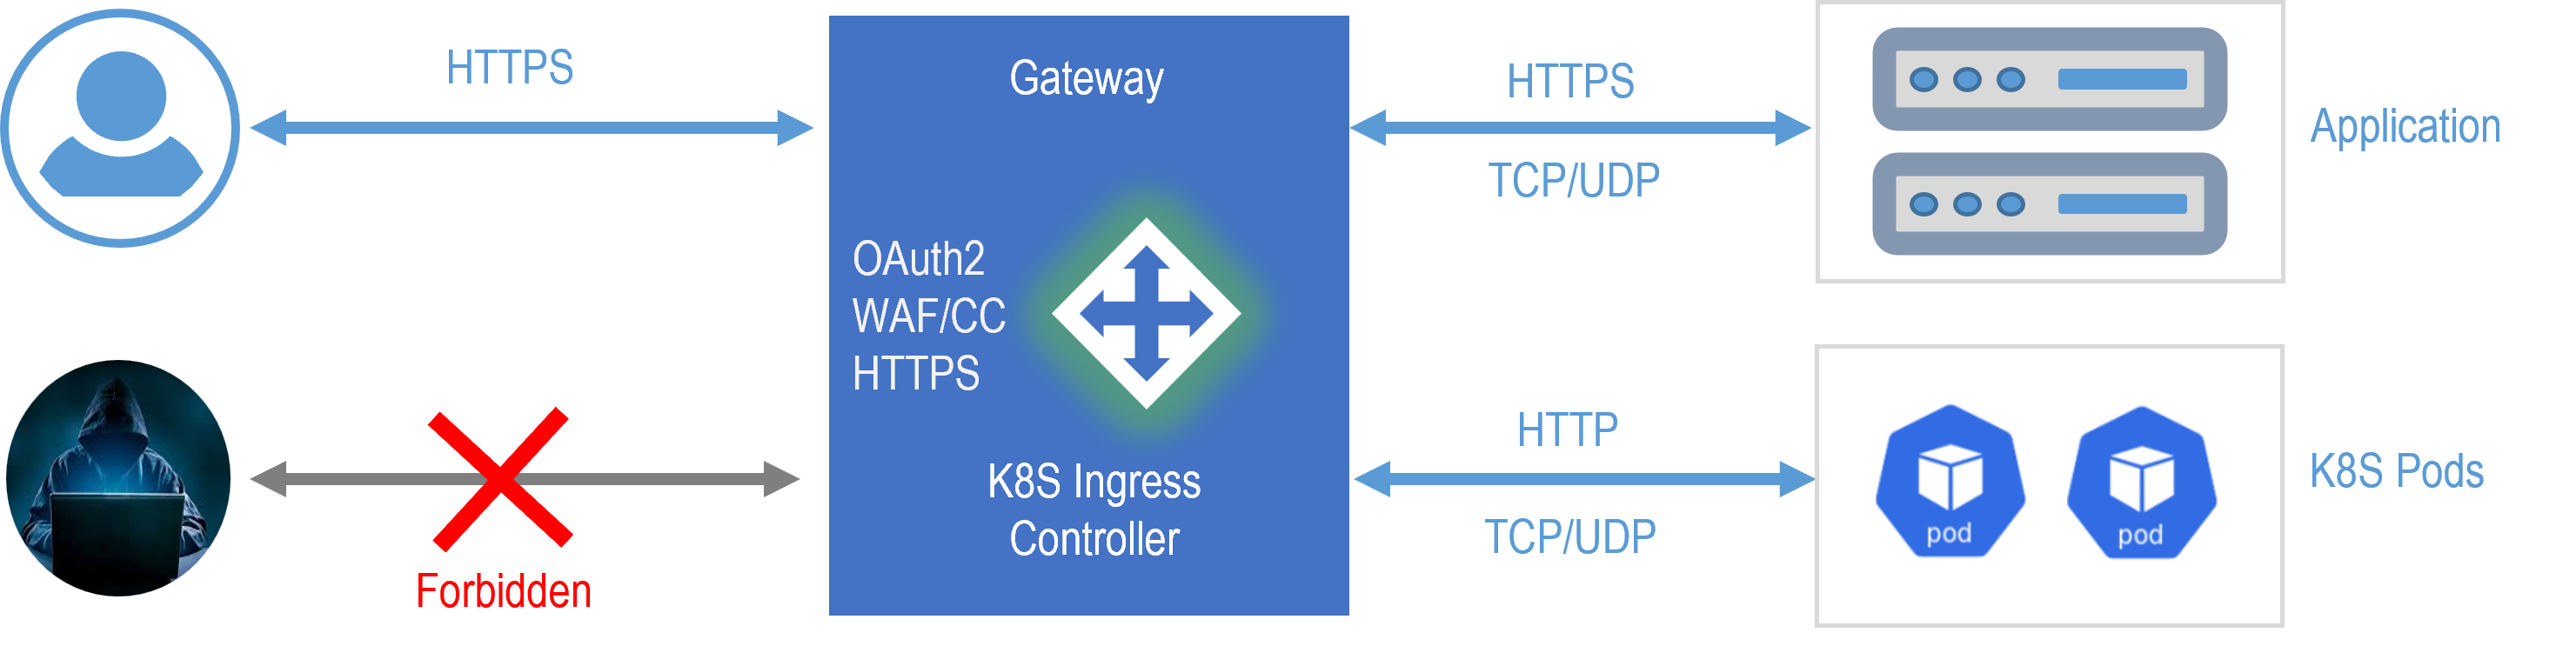 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 asang17/cve-2021-40223
XSS Vulnerability in Rittal
 kazisabu/cve-2025-70849-podinfo
PoC and Advisory for CVE-2025-70849: Unauthenticated Stored XSS in Podinfo /store endpoint.
 deaprojects/cve-2025-70849
CVE-2025-70849: Stored XSS in Podinfo
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 yavuzlar/vulnlab
Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…