
CVE-2020-13937
 kailing0220/cve-2020-13937
Apache Kylin有一个restful api会在没有任何认证的情况下暴露配置信息
exploitationmisconfigurationpenetration-testing+3
14 years ago
kailing0220/cve-2020-13937Apache Kylin有一个restful api会在没有任何认证的情况下暴露配置信息
 im-hanzou/fc3er
Automatic Mass Tool for checking vulnerability in CVE-2022-0591 - Formcraft3 < 3.8.28 - Unauthenticated SSRF
 l3ragio/cve-2022-29361_werkzeug_client-side-desync-to-xss
Proof-of-concept exploit for CVE-2022-29361, demonstrating client-side desync to XSS in Werkzeug. Tested on Chromium.
 cameron-coding-projects/joomla-cve-detector-cve-2022-27913-
Detect Joomla instances vulnerable to CVE-2022-27913 with a lightweight Python scanner for rapid identification and reporting.
 nibin-m/cve-2022-43097
All details about CVE-2022-43097
 ccordeiro/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 cappricio-securities/cve-2022-0165
WordPress Page Builder KingComposer <=2.9.6 - Open Redirect
 rishi-kaul/cve-2022-23779
CVE-2022-23779 is a security vulnerability in Zoho ManageEngine Desktop Central ,Testing for CVE-2022-23779 using curl
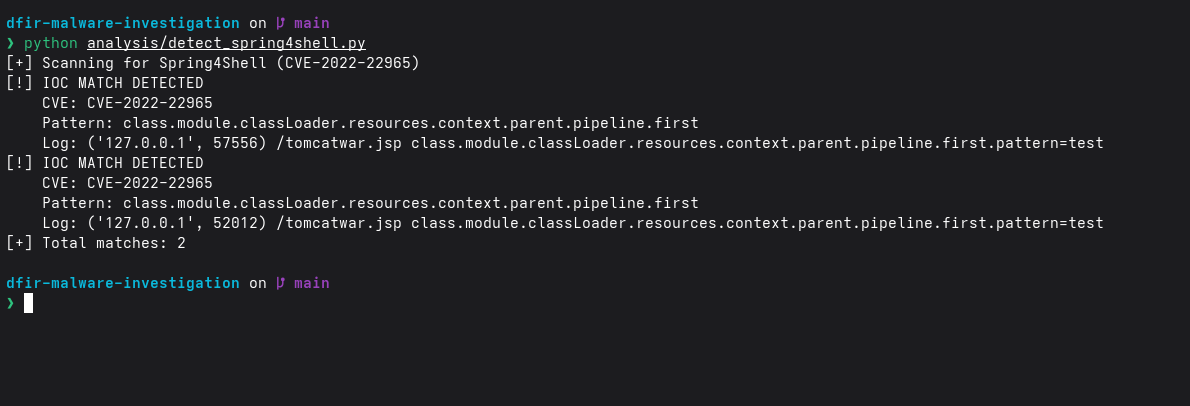 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 abrewer251/cve-2022-22536_sap_request_smuggling_scanner
Fast, socket-level scanner for detecting CVE-2022-22536 in SAP ICM or Web Dispatcher instances. Performs request smuggling tests with a crafted…
 cyberone-teamares/jquery-cve-2022-31160
jquery XSS Proof of Concept (PoC)
 randomrobbiebf/cve-2022-45354
Download Monitor <= 4.7.60 - Sensitive Information Exposure via REST API
 node011/cve-2023-27997-poc
Fortigate SSL VPN buffer overflow exploit
 drkbcn/lblfixer_cve_2022_31181
Module for PrestaShop 1.6.1.X/1.7.X to fix CVE-2022-31181 / CVE-2022-36408 vulnerability (Chain SQL Injection)
 shameem-testing/poc-for-me-saml-vulnerability
PoC for cve-2022-47966
 dkstar11q/cve-2022-40684
Authentication bypass exploit for CVE-2022-40684 targeting FortiOS, FortiProxy, and FortiSwitchManager. Checks vulnerability and overwrites admin SSH…
 7rootsec/cve-2022-21661-technical-analysis
Proof-of-concept and technical analysis for CVE-2022-21661, a WordPress SQL injection vulnerability, including root-cause breakdown, exploitation…
 g01d3nw01f/cve-2022-0739
Proof-of-concept exploit for CVE-2022-0739, an SQL injection vulnerability in the BookingPress WordPress plugin before version 1.0.11.