
ghost-cve-2026-26980
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
database-securityeducationexploitation+5
19
dinosn/ghost-cve-2026-26980CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 yogeshojha/rengine
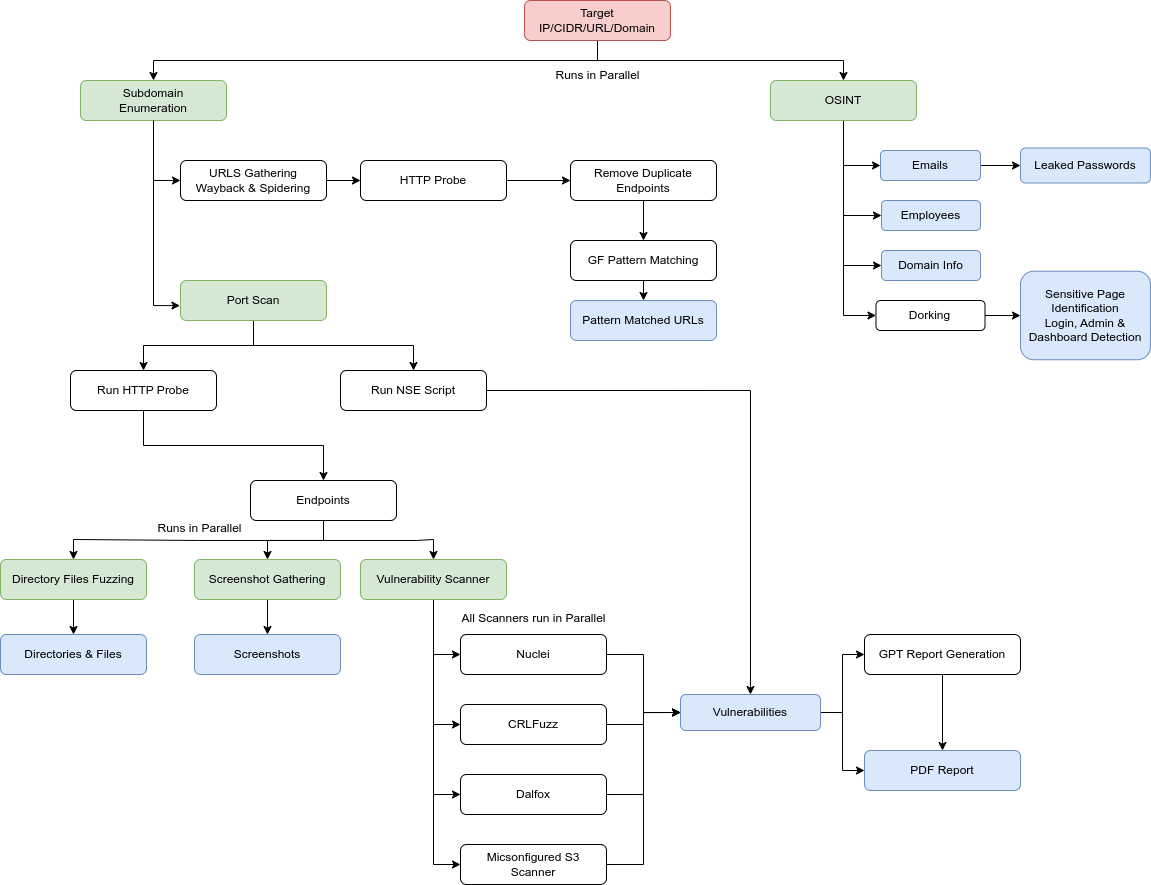
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 publicqi/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 r4x0r1337/-cve-2012-2661-activerecord-sql-injection-
Proof-of-concept exploit for CVE-2012-2661, an SQL injection vulnerability in Ruby on Rails ActiveRecord. Includes a write-up in Malay demonstrating…
 xsshk/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 charondefalt/wordpress--cve-2022-21661
Proof-of-concept exploit for CVE-2022-21661, a SQL injection vulnerability in WordPress Core WP_Query, demonstrating the attack and providing…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…
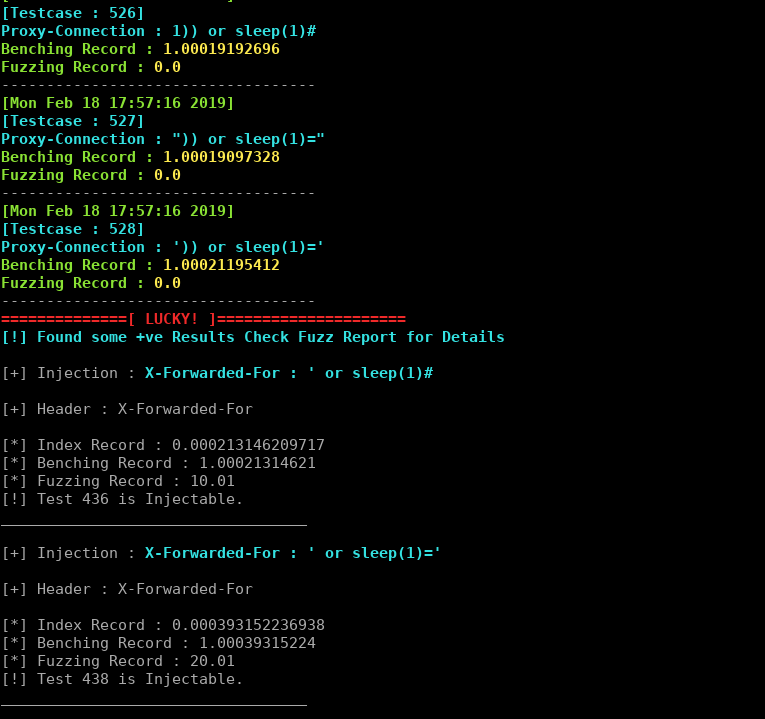 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
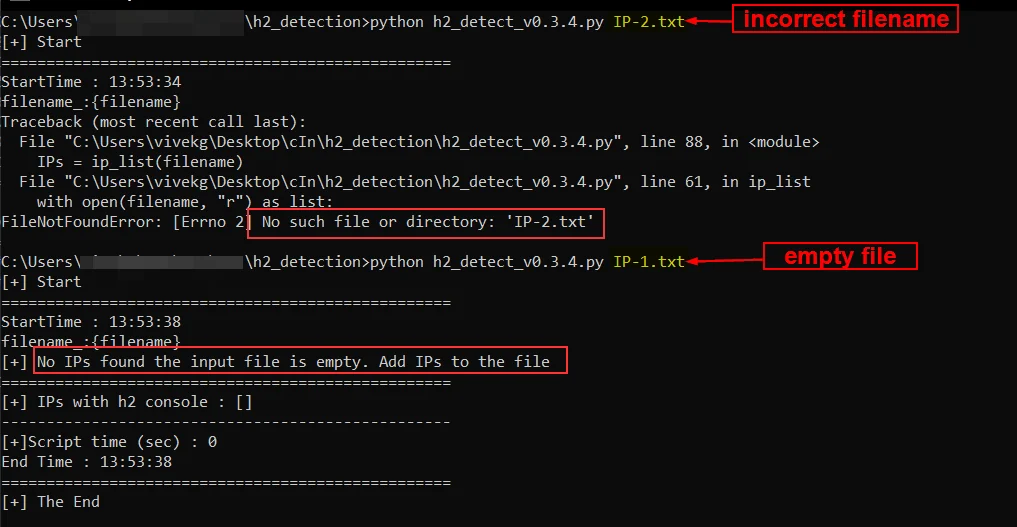 cybersecurityworks553/cve-2021-42392-detect
Scans a list of IPs to detect vulnerable H2 database consoles, identifying web pages and checking access restrictions for CVE-2021-42392.
 amitlttwo/cve-2022-31626
Proof-of-concept exploit for CVE-2022-31626, a buffer overflow in PHP's pdo_mysql with mysqlnd driver that can lead to remote code execution.
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
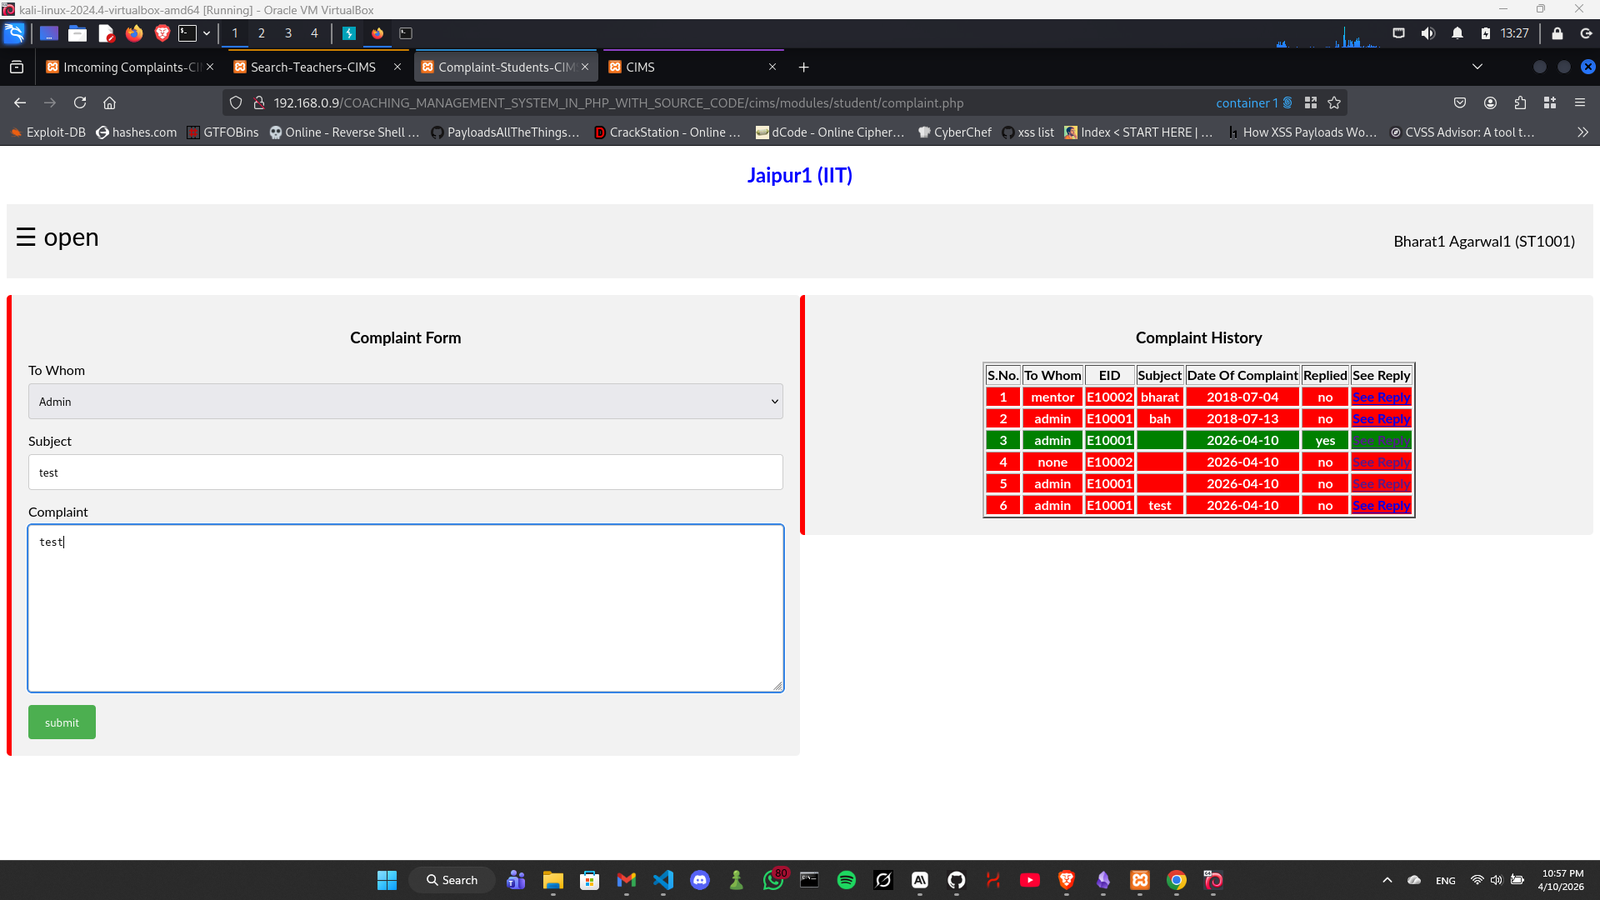 xmyronn/cve-2026-7229-sqli
Proof of concept for authenticated SQL injection in Coaching Management System, demonstrating database dump via unsanitized complaintreply parameter.
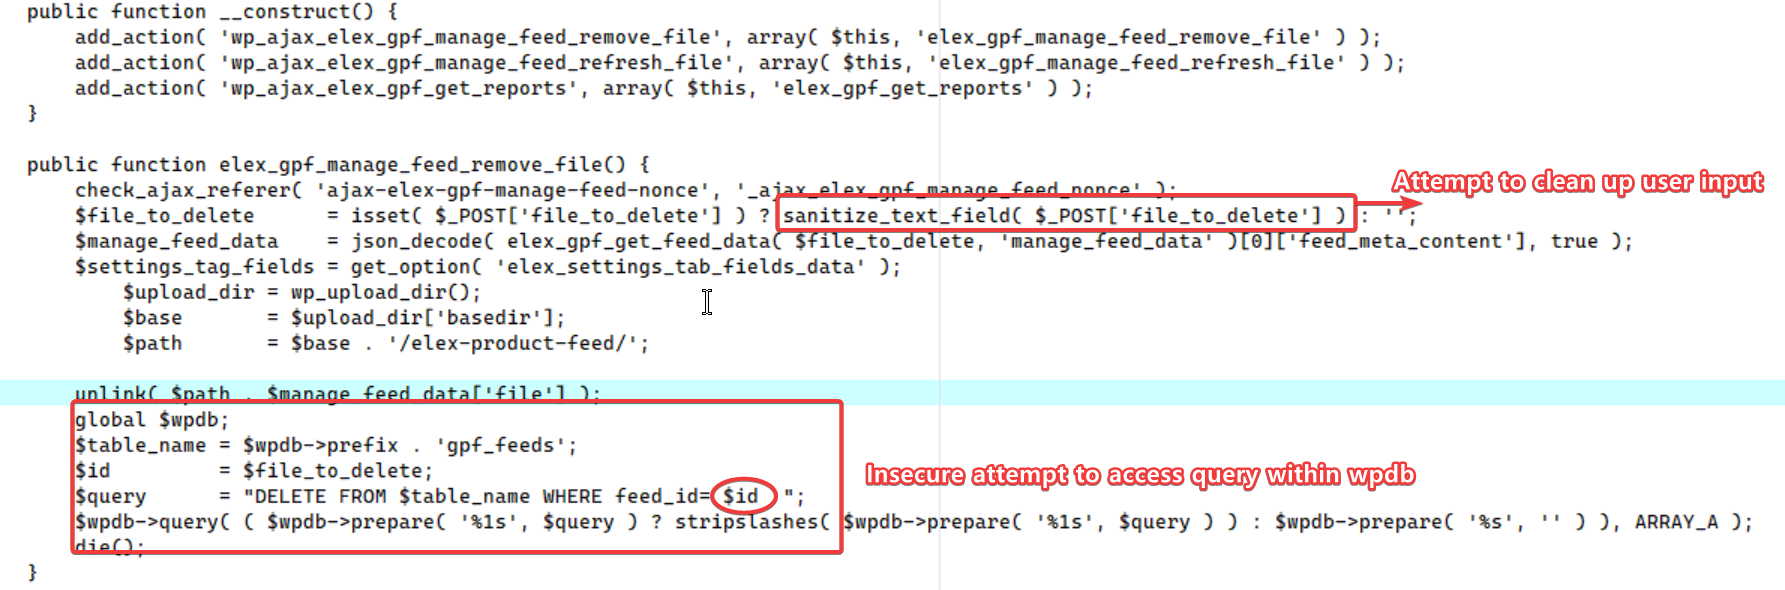 bytereaper77/cve-2025-10046
exploit SQL injection ELEX WooCommerce Google Shopping
 zierax/grafana-final-scanner
Grafana scanner with all public CVEs that I collected in one script to make grafana testing easier